
CrystalSliver
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
command-and-controlexploit-frameworksids-ips-evasion+9
1084 months ago
licitrasimone/crystalsliverCrystal Palace Evasion kit for Sliver
 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.

 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
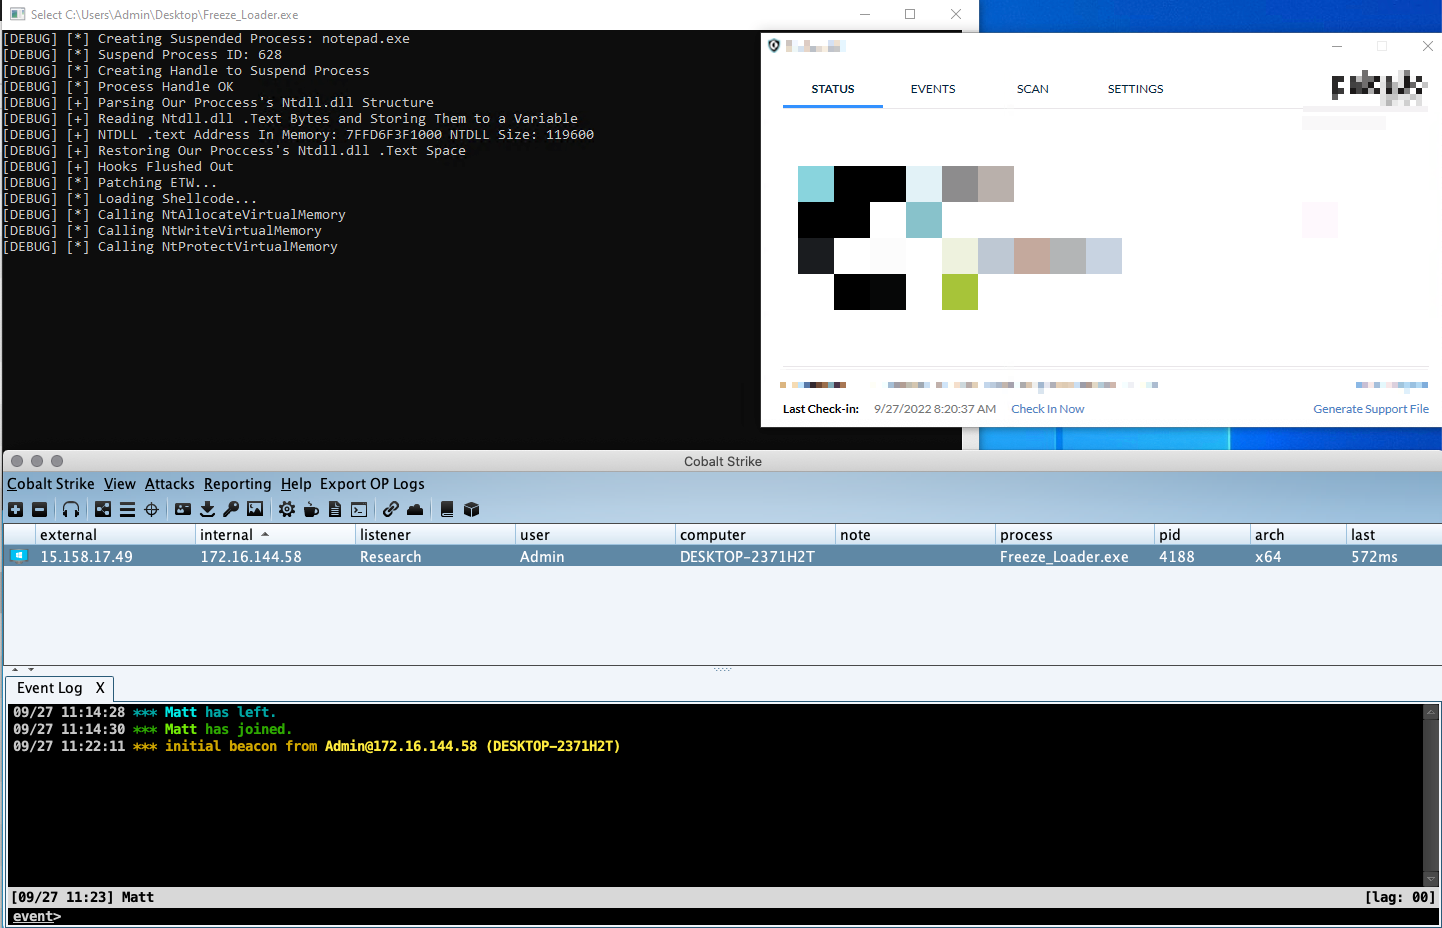 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
 gallopsled/pwntools
CTF framework and exploit development library
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
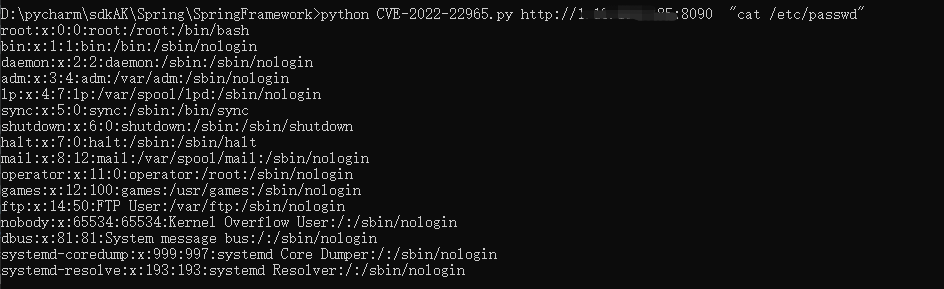 xsxtw/springframework_cve-2022-22965_rce
Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.
 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
 adenkiewicz/cve-2003-0264
Exploit for CVE-2003-0264 based on pwntools and metasploit's windows/reverse_tcp
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
 bw3ll/rop_rocket
ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…