
SysWhispers
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
exploitationids-ips-evasionpayload-development+3
2.0k
jthuraisamy/syswhispersAV/EDR evasion via direct system calls.
 nccgroup/winpayloads
Undetectable Windows Payload Generation
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
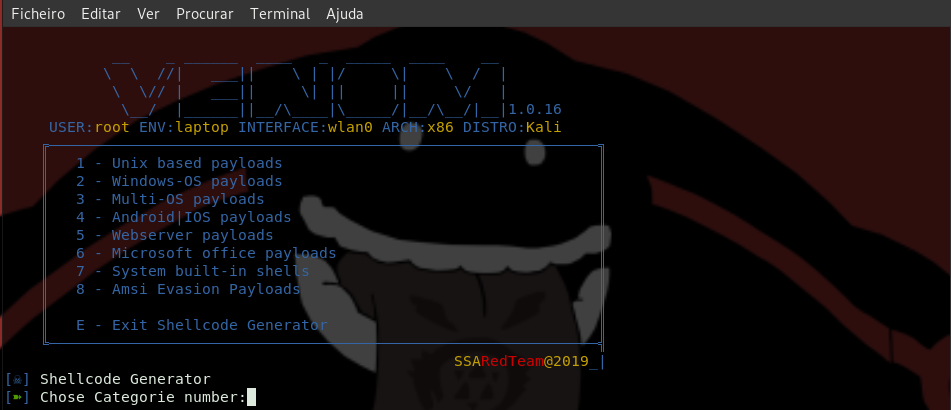 r00t-3xp10it/venom
venom - C2 shellcode generator/compiler/handler
 sensepost/ruler
A tool to abuse Exchange services
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
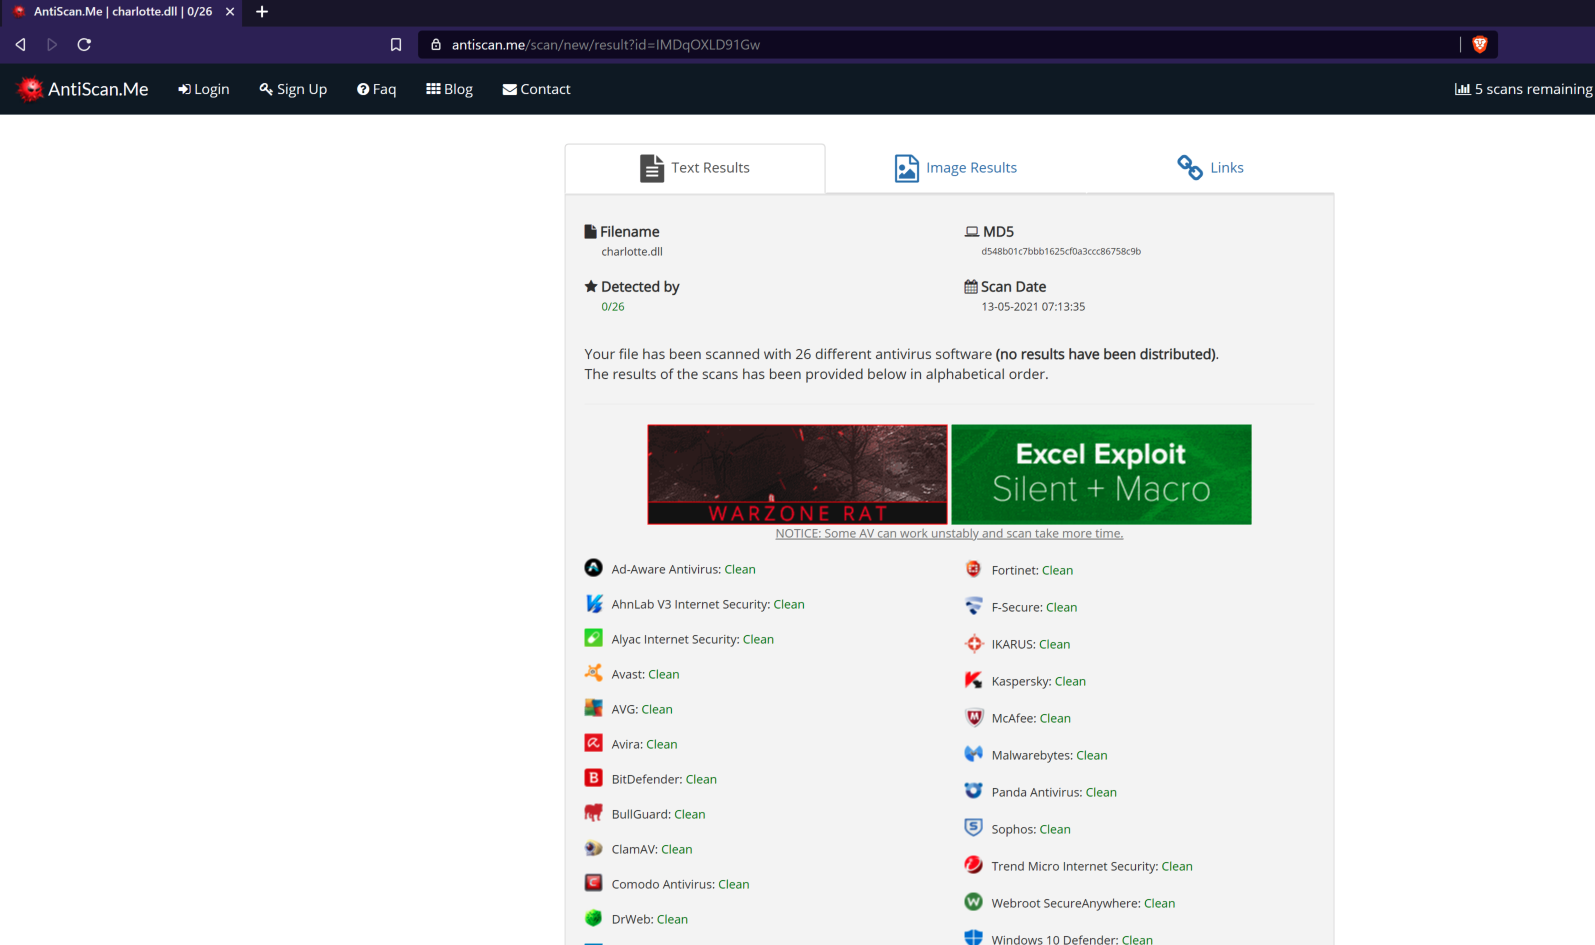 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
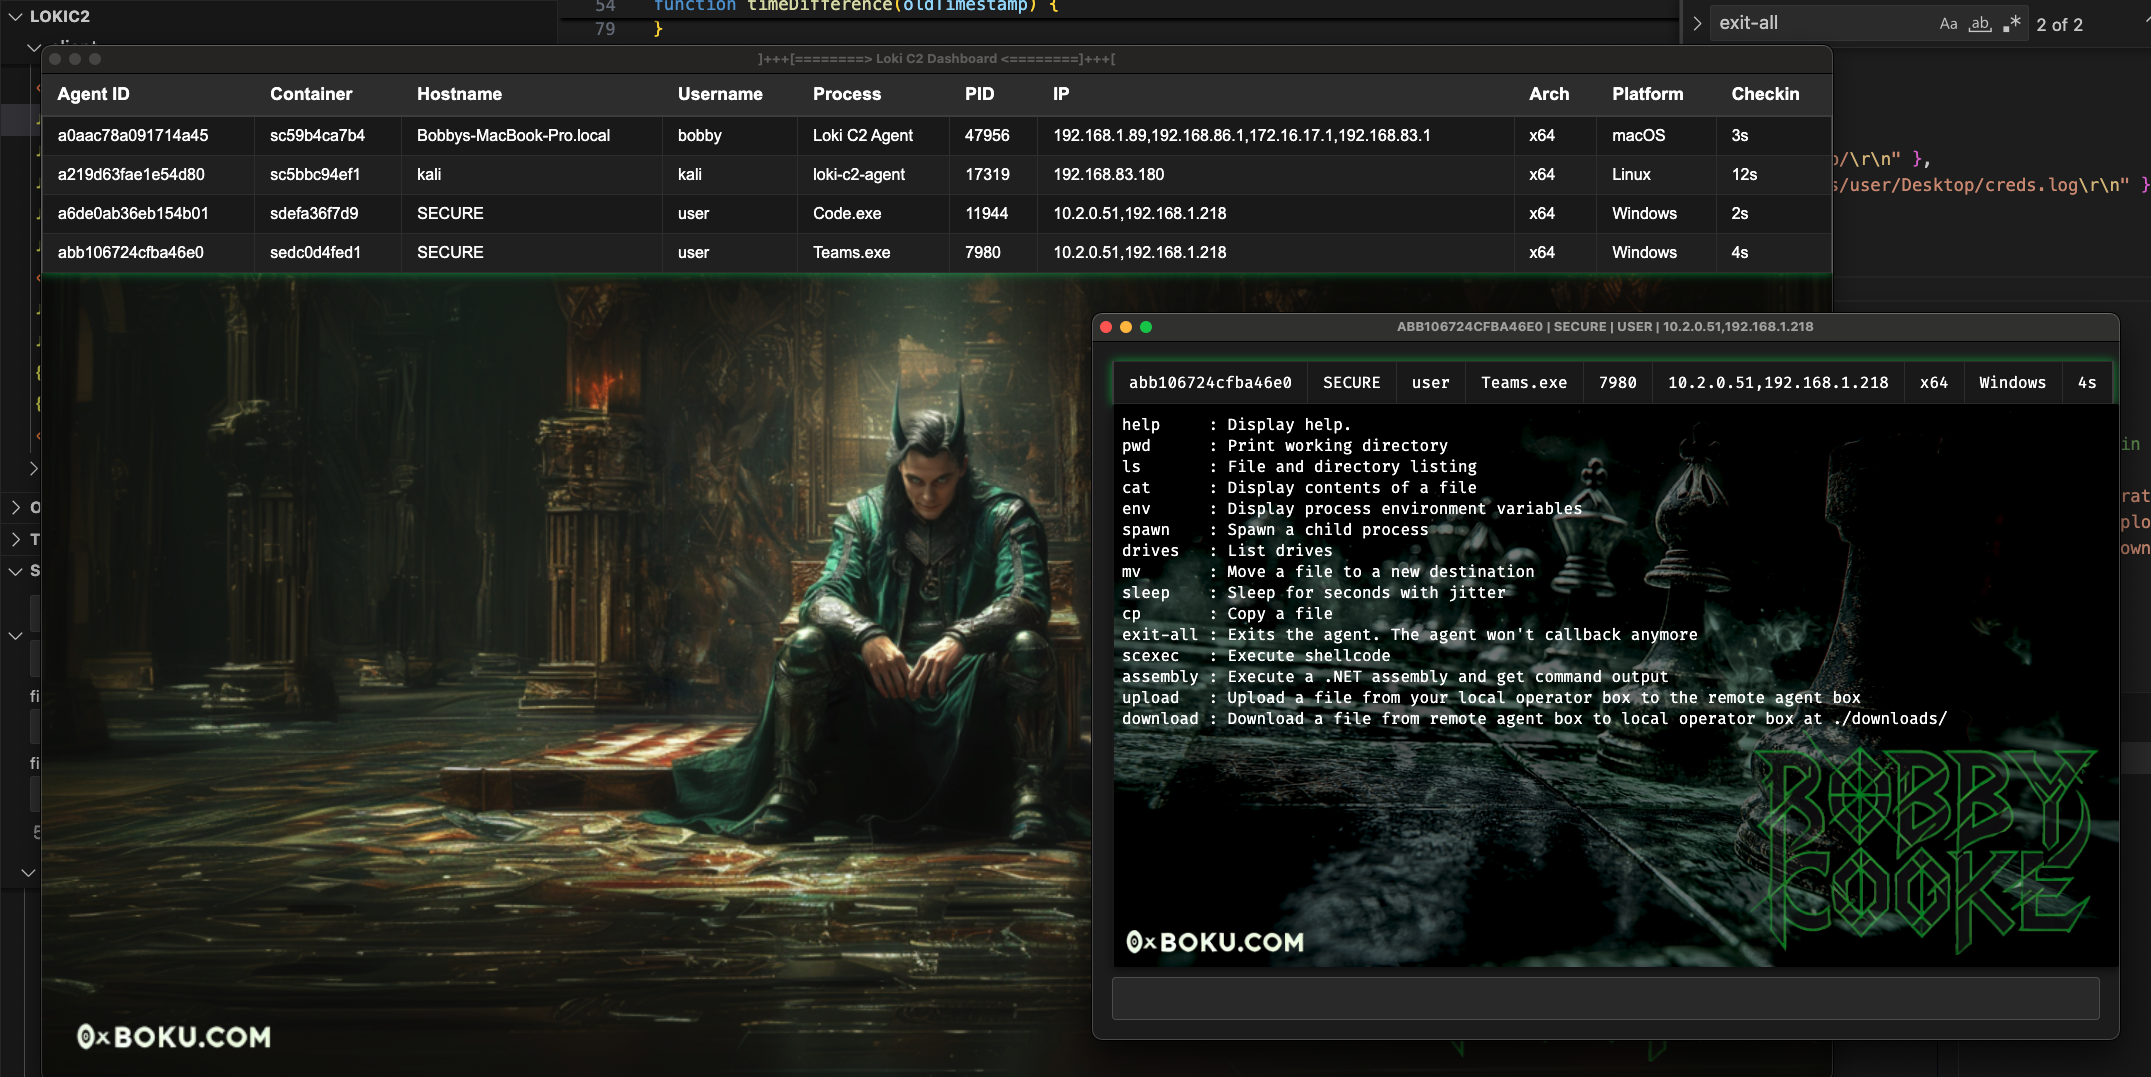 boku7/loki
🧙♂️ Node.js Command & Control for Script-Jacking Vulnerable Electron Applications

 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.
 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 egebalci/amber
Reflective PE packer.
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim