
wshlient
 gildasio/wshlient
A simple tool to interact with web shells and command injection vulnerabilities
command-and-controlpenetration-testingshellcode+1
gildasio/wshlientA simple tool to interact with web shells and command injection vulnerabilities
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
 hakkuri01/r2rs
Interactive Ruby shell for authorized CVE-2025-55182 (react2shell) testing
 passwa11/cve-2023-3519
Python exploit for CVE-2023-3519 targeting Citrix ADC with custom NASM shellcode, PHP backdoor deployment, and SUID privilege escalation.
 aadi0258/exploit-cve-2024-23897
Exploit for CVE-2024-23897 in Jenkins, enabling file read and remote code execution via crafted requests. Includes Docker setup and Groovy scripts…
 khaidtraivch/cve-2021-41773-apache-2.4.49-
Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.
 oddcod3/phantom-evasion
Python antivirus evasion tool
 mr-un1k0d3r/dkmc
DKMC - Dont kill my cat - Malicious payload evasion tool
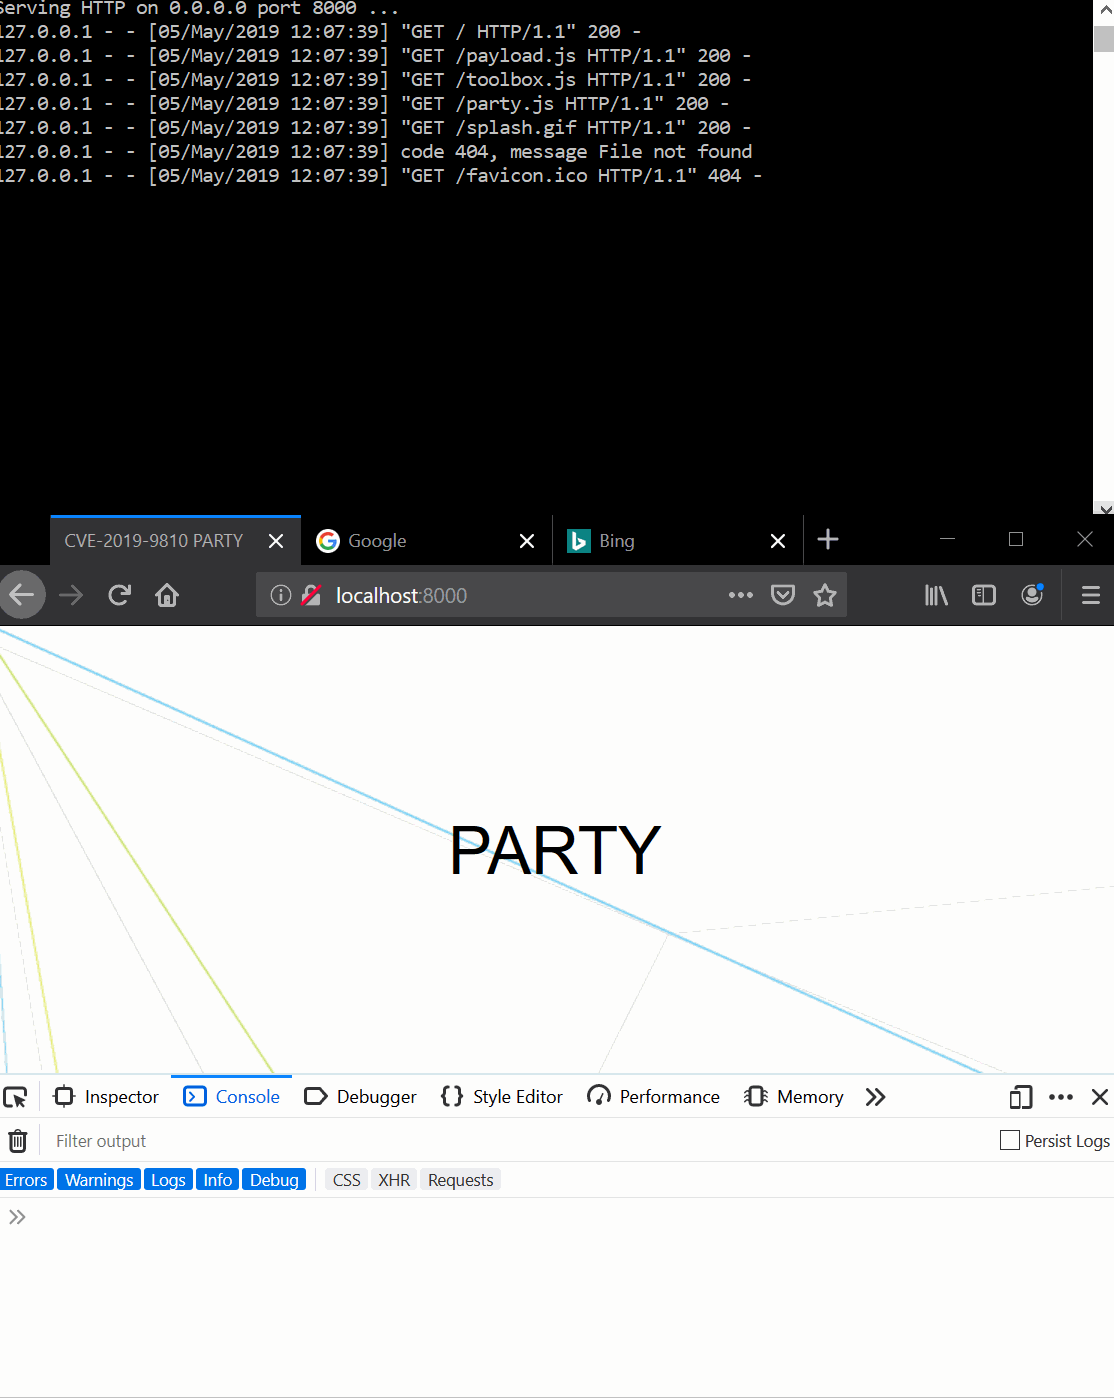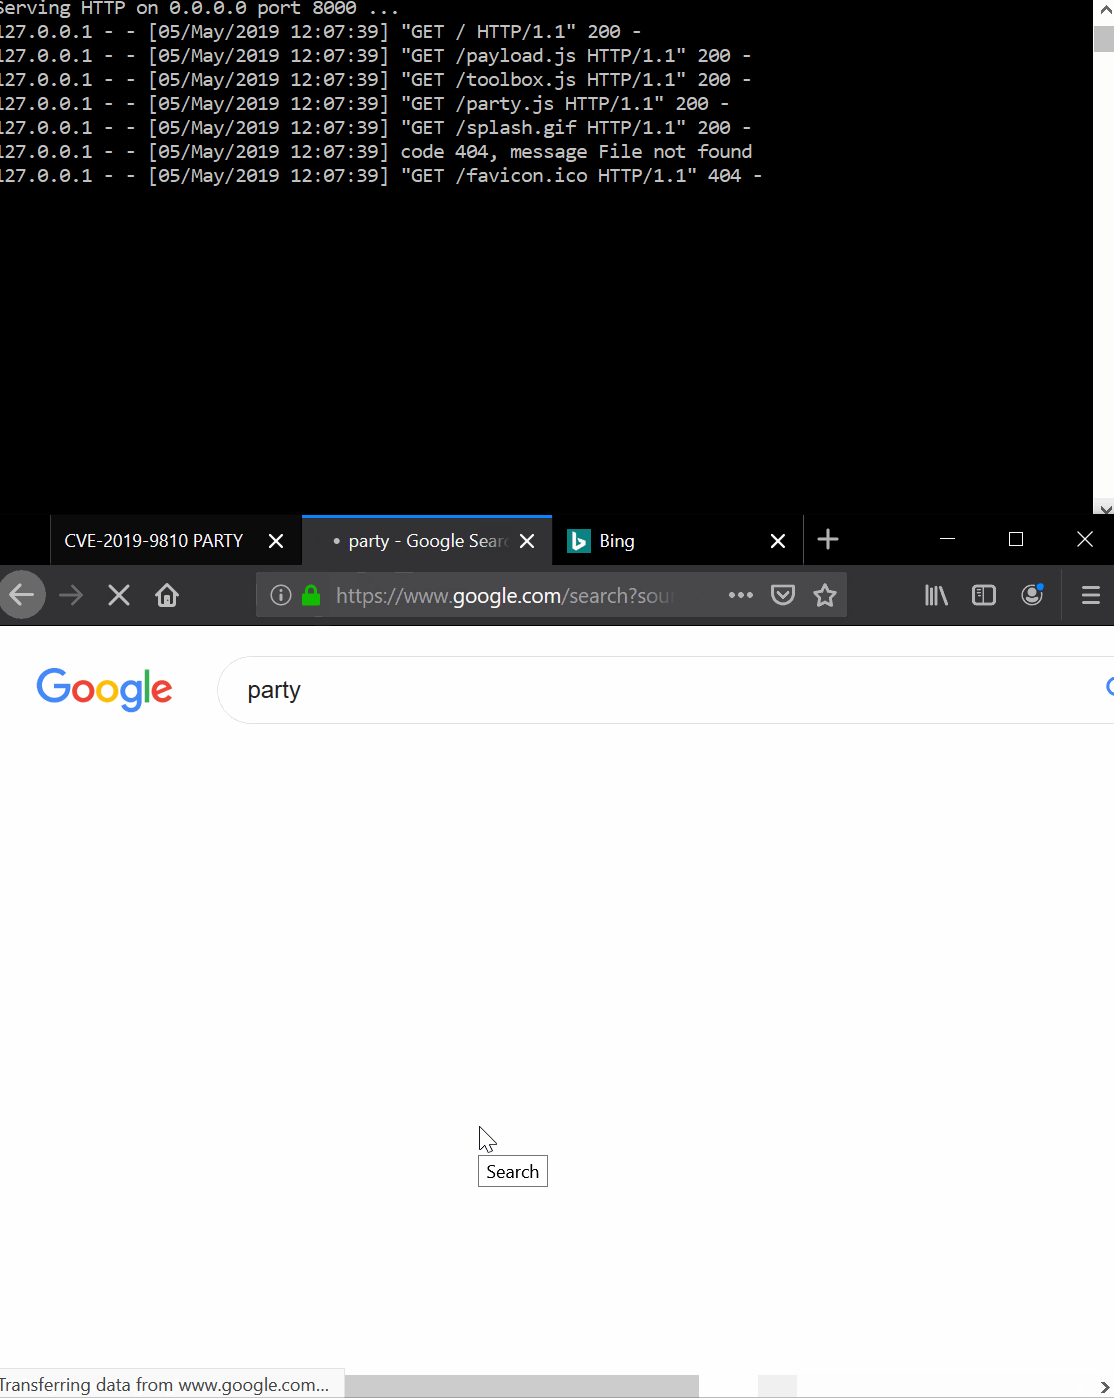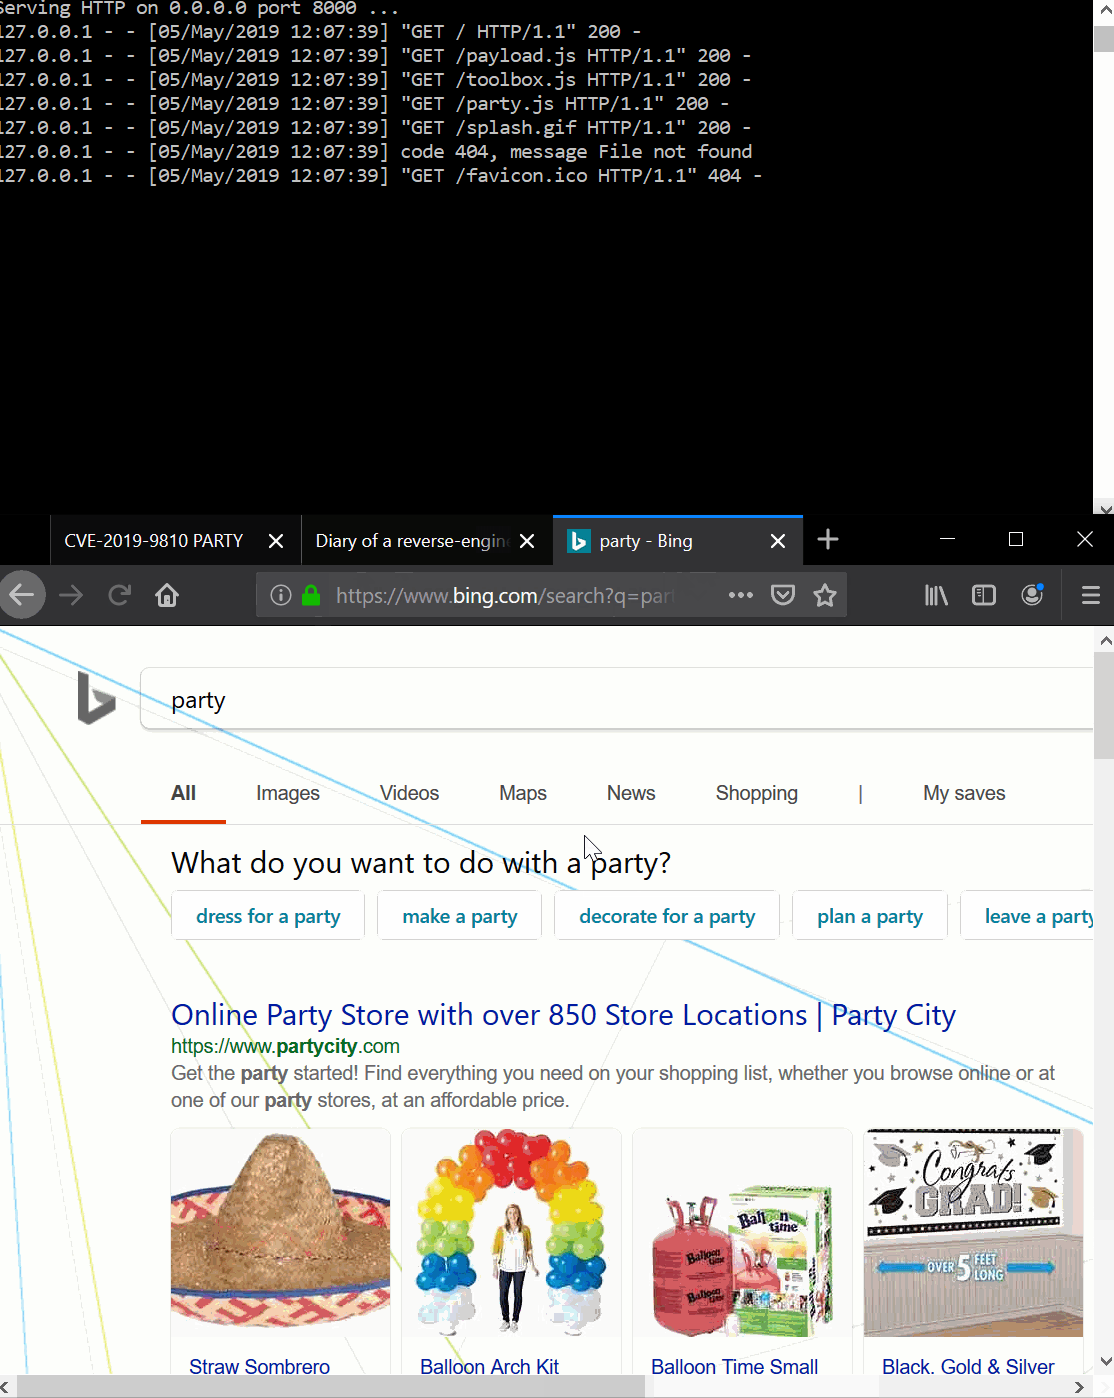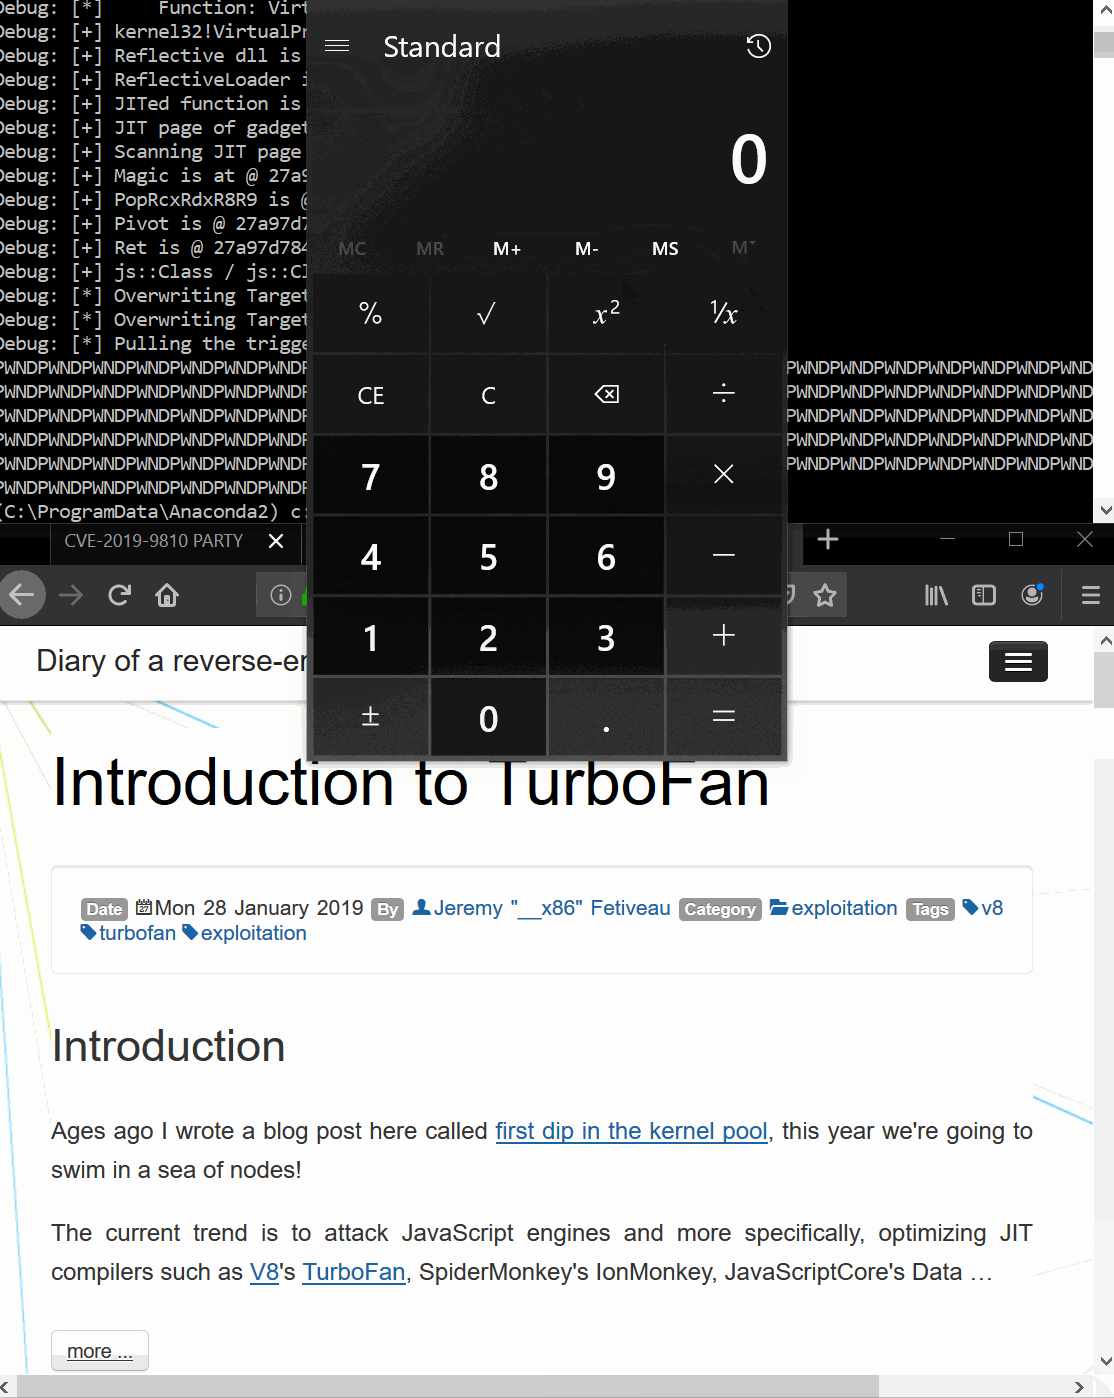 0vercl0k/cve-2019-9810
Exploit for CVE-2019-9810 Firefox on Windows 64-bit.
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 tamirido30/cve-2024-10914-exploit
CVE-2024-10914 Shell Exploit
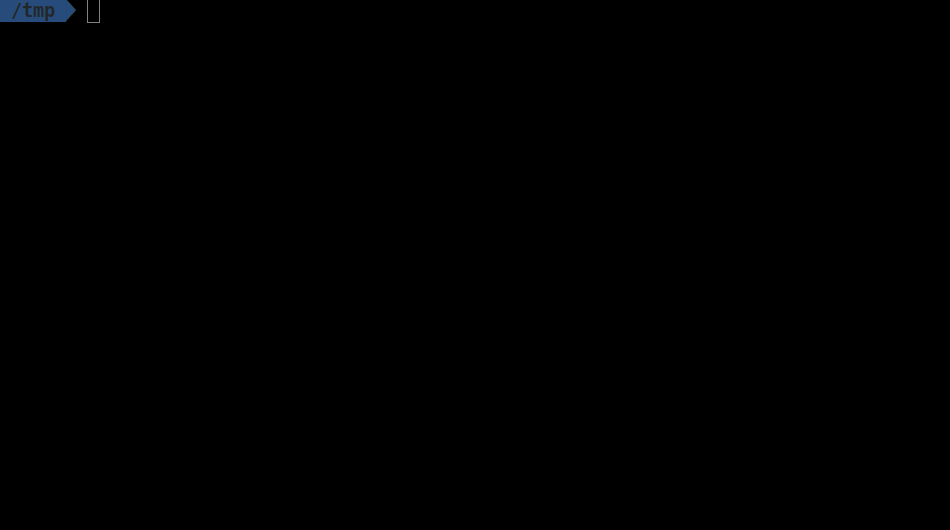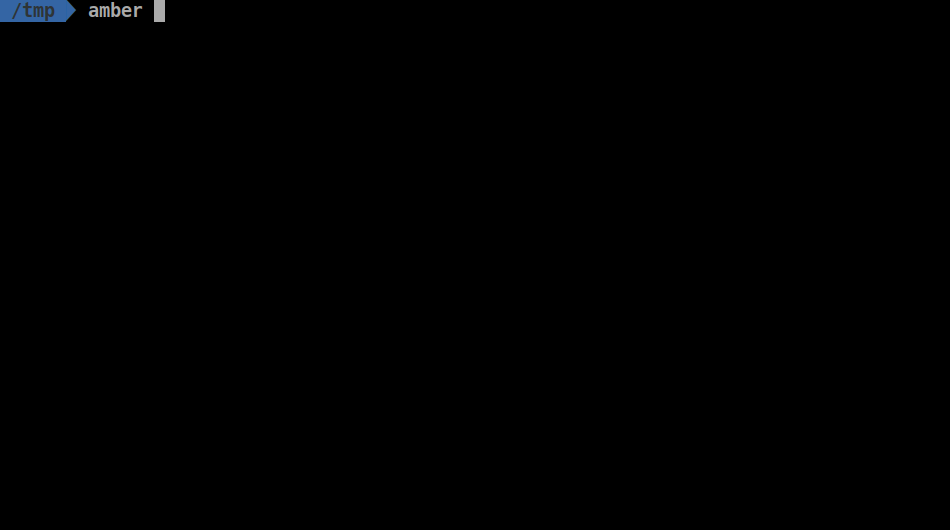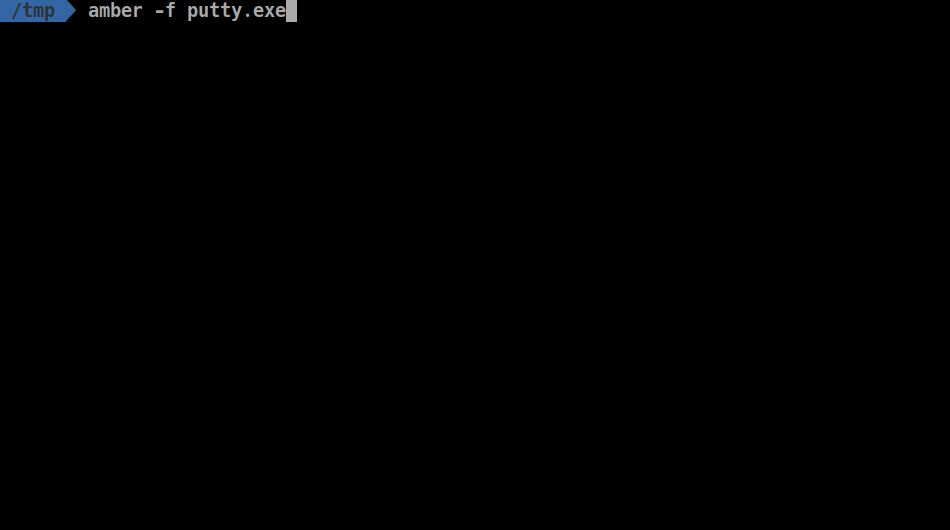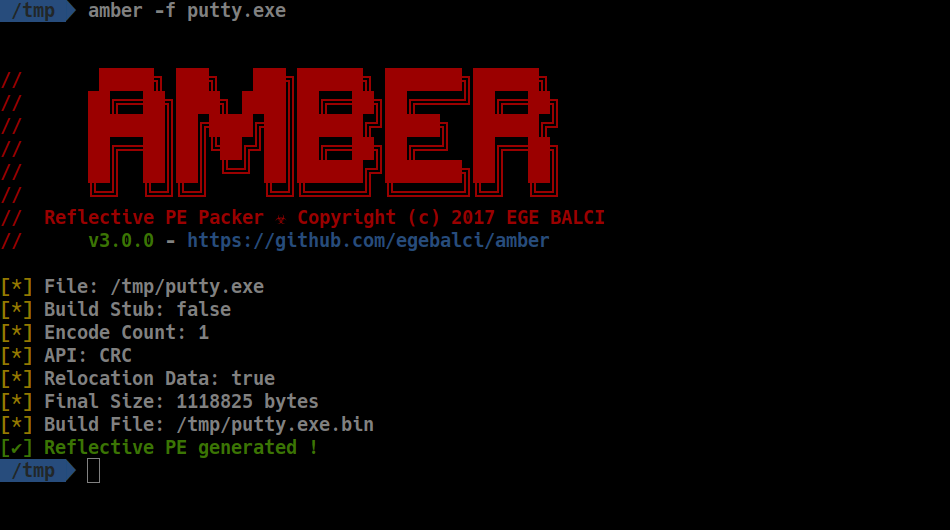 egebalci/amber
Reflective PE packer.
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 jayngng/bludit-cve-2019-17240
Bypass bludit mitigation login form and upload malicious to call a rev shell
 h3x0v3rl0rd/cve-2022-41544
Python exploit script for CVE-2022-41544 in GetSimple CMS. Automates API key leakage, CSRF token extraction, PHP shell upload, and reverse shell…
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…