
ShellGhost
 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
binary-analysisencryption-decryption-toolsexploitation+4
1.2k
lem0nsec/shellghostA memory-based evasion technique which makes shellcode invisible from process start to end.
 0x00-0x00/shellpop
Pop shells like a master.
 egebalci/amber
Reflective PE packer.
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 rcstep/cssg
Cobalt Strike aggressor script for generating, formatting, and encrypting beacon shellcode with support for multiple exit methods, syscalls, and…
 lesnuages/hershell
Multiplatform reverse shell generator
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)
 enkomio/alanframework
A C2 post-exploitation framework
 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
 aniqfakhrul/sharperner
Simple executable generator with encrypted shellcode.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
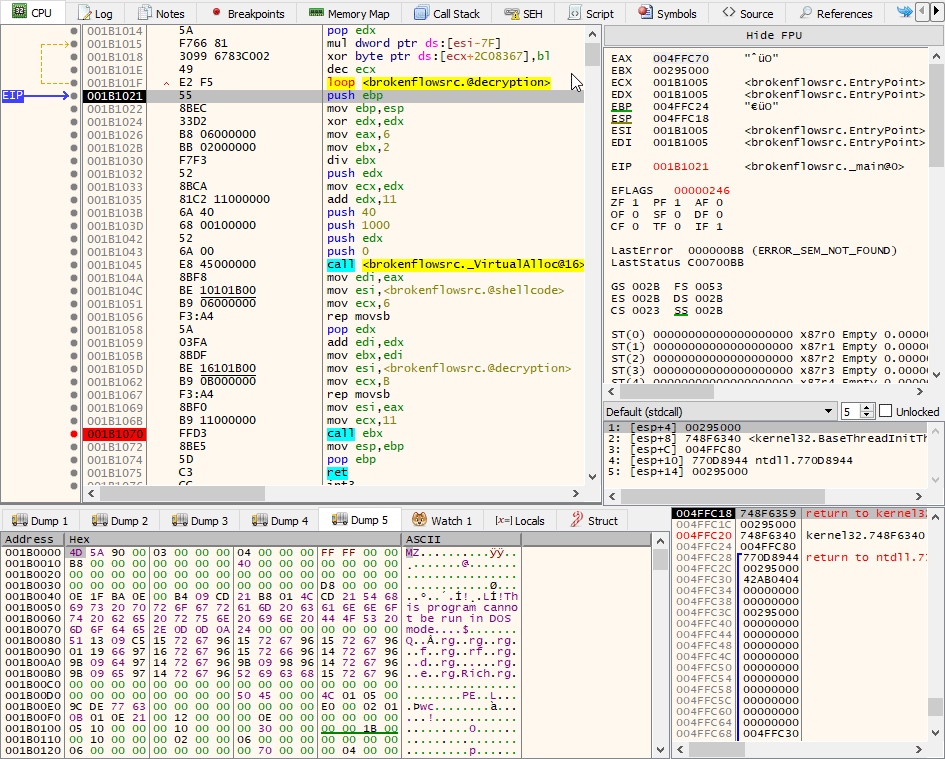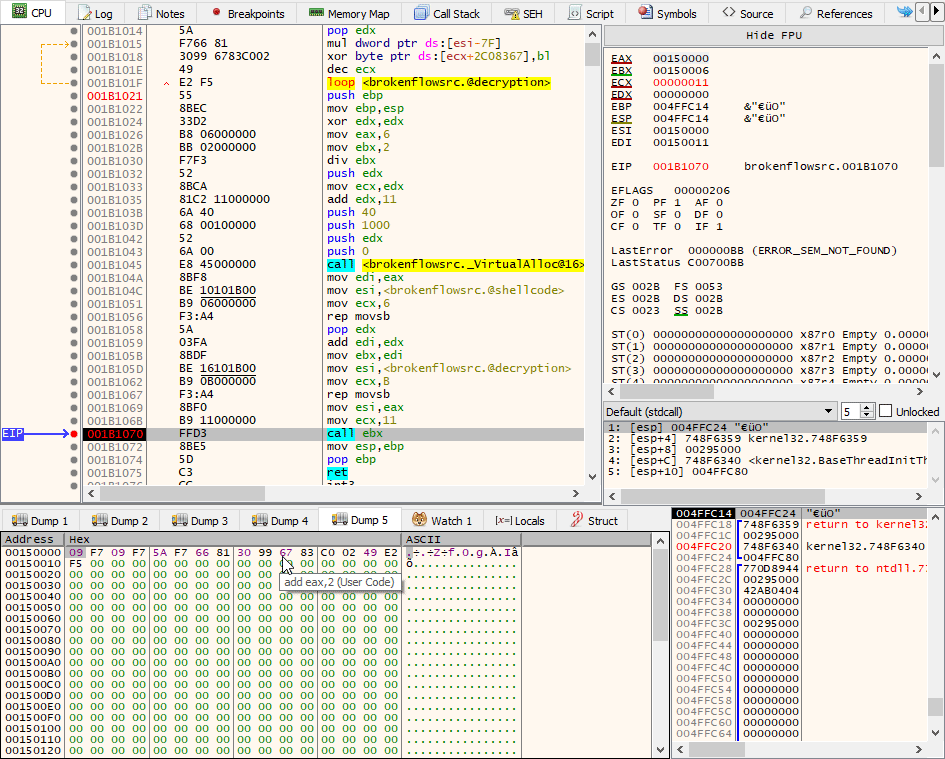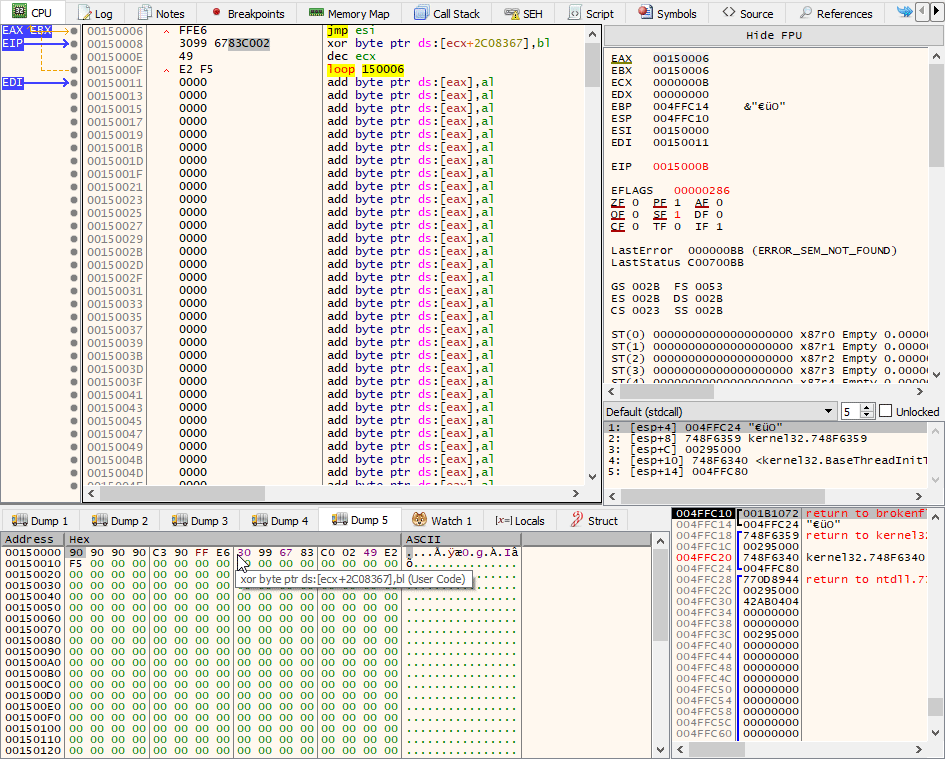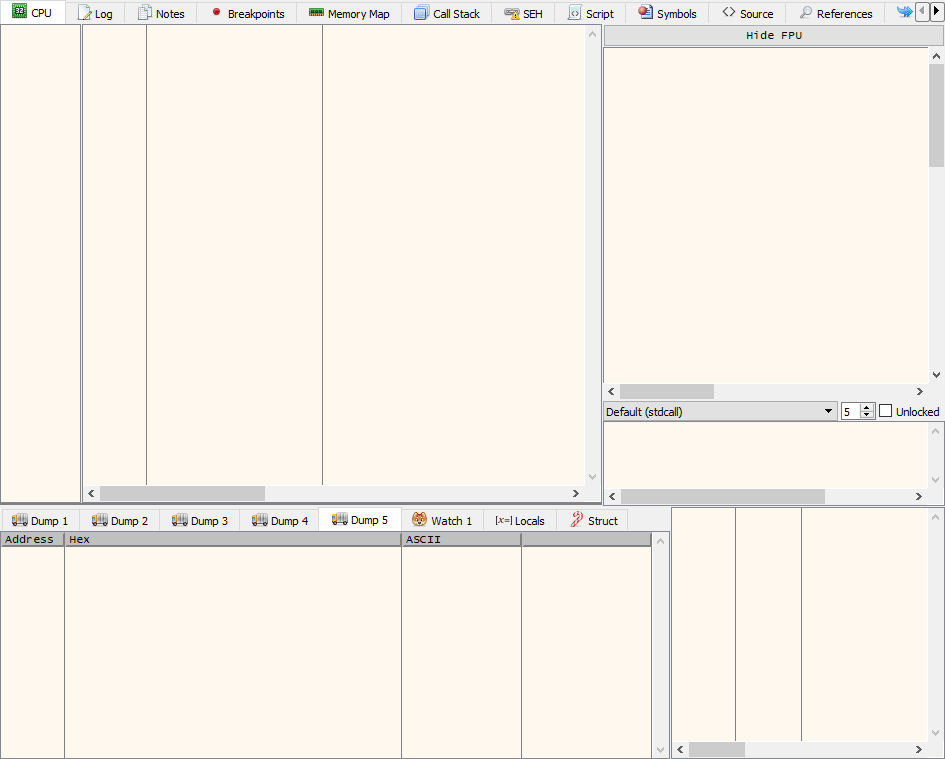 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call