cve-2023-4911-exploit-optimized

Pure C exploit for CVE-2023-4911 (Looney Tunables) — x86_64 & aarch64 implementations. Multi-processing brute-forcing, dynamic calibration,…

Pure C exploit for CVE-2023-4911 (Looney Tunables) — x86_64 & aarch64 implementations. Multi-processing brute-forcing, dynamic calibration,…

Adversary Emulation Framework

Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…


IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…

This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…

C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.

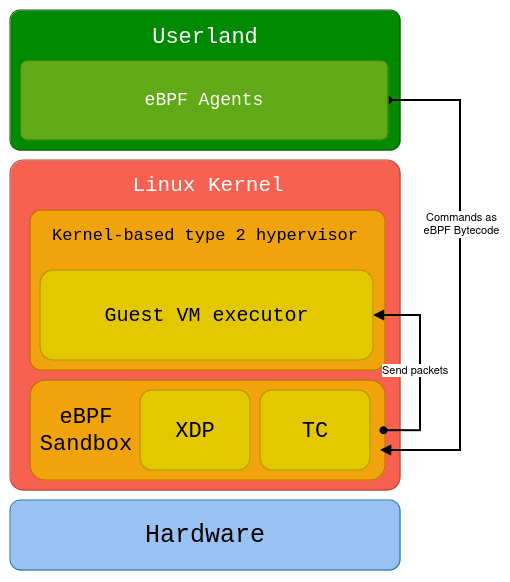
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

Dynamically invoke arbitrary unmanaged code

Dynamic shellcode loader with sophisticated evasion capabilities

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

AV/EDR evasion via direct system calls.

Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…

Convert shellcode into :sparkles: different :sparkles: formats!

PoC demonstrating a multi process injection chain aimed at remotely executing shellcode

Apply a divide and conquer approach to bypass EDRs

Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level