
BrokenFlow
 enkomio/brokenflow
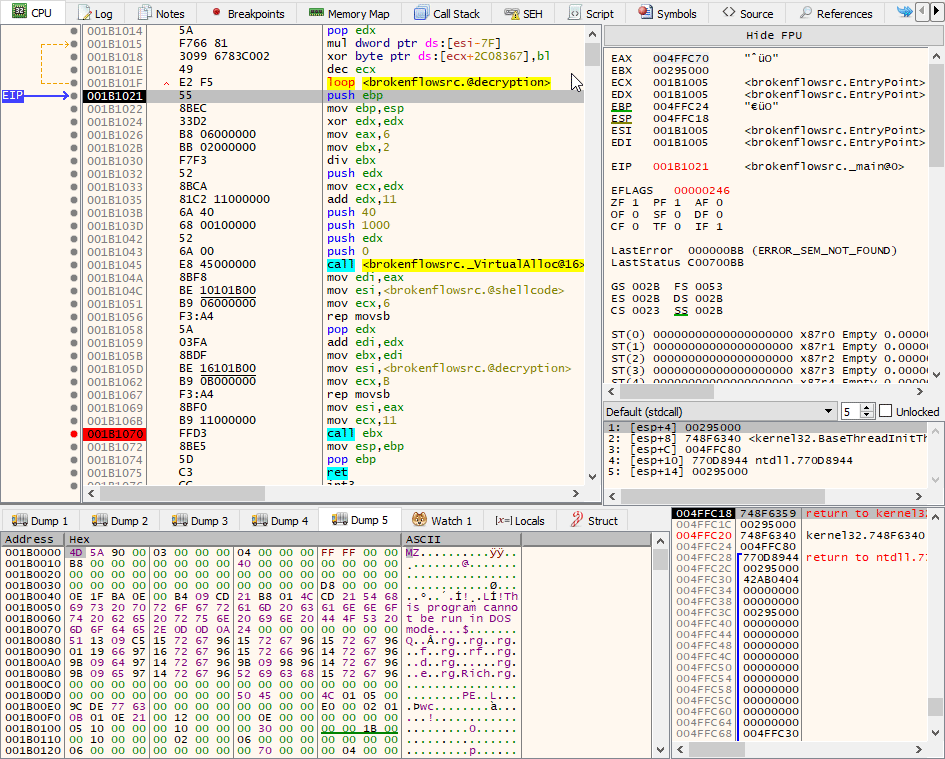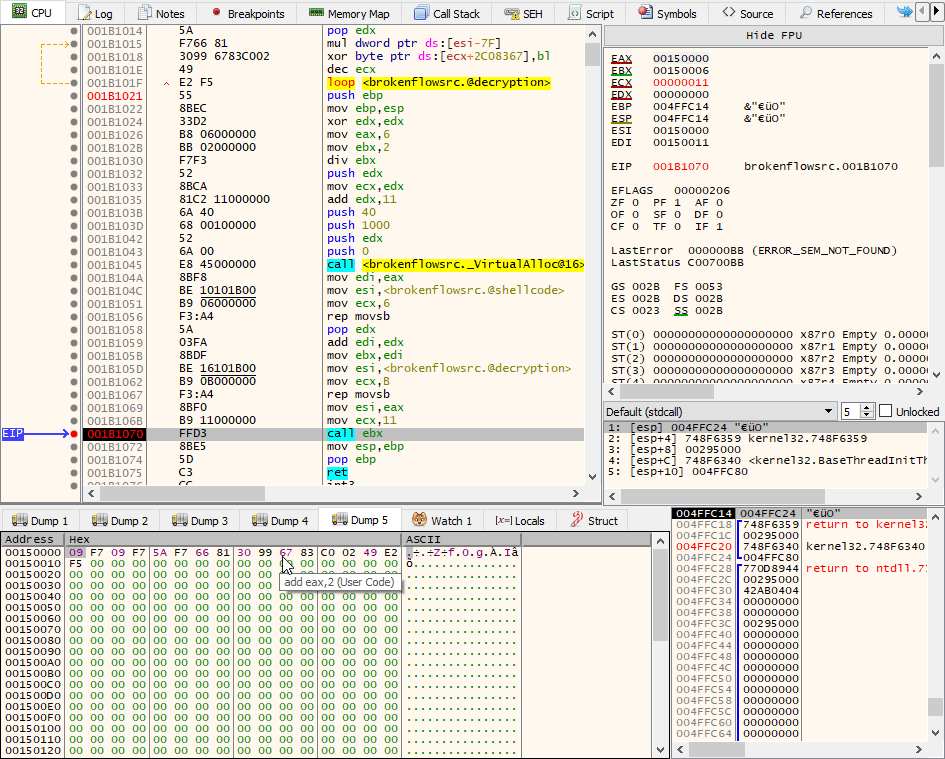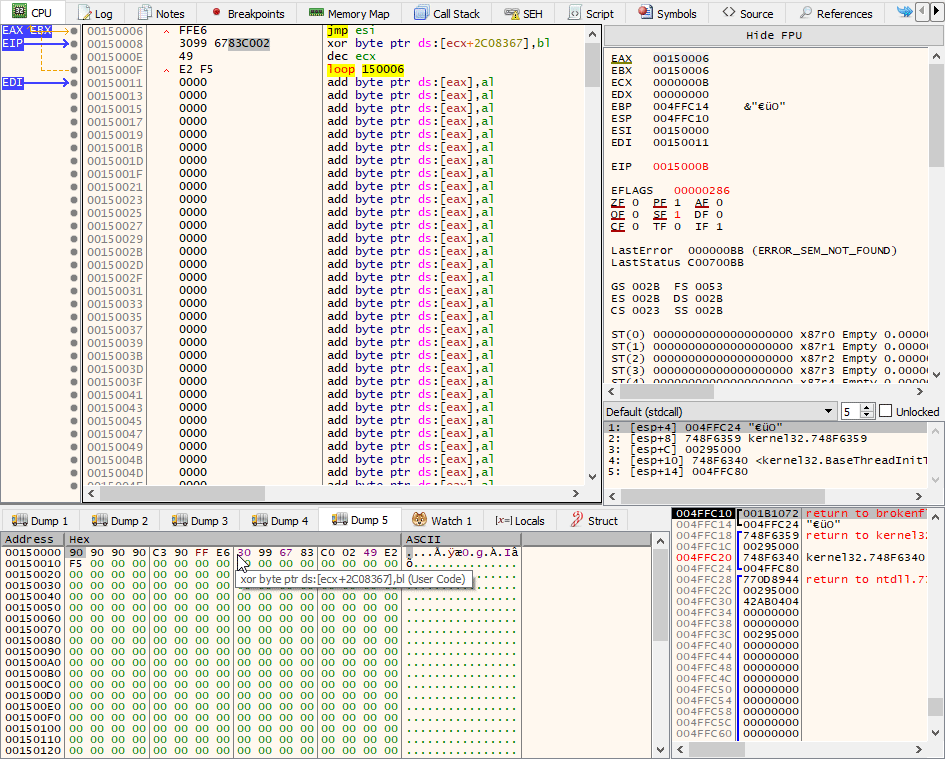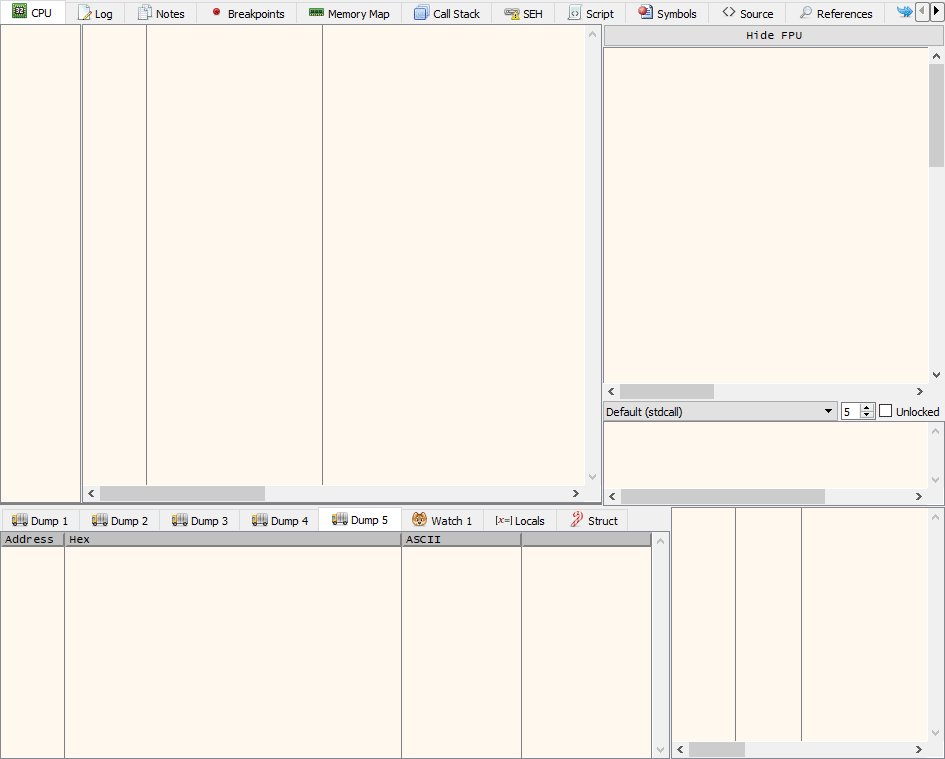
A simple PoC to invoke an encrypted shellcode by using an hidden call
binary-exploitationencryption-decryption-toolsexploitation+4
1153 years ago
enkomio/brokenflowA simple PoC to invoke an encrypted shellcode by using an hidden call
 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 bitstream93/shellcode-test-harness
A lightweight test harness designed to speed up shellcode development by providing an execution environment with integrated crash diagnostics and…
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 gmh5225/anti_suspend
Protect process by shellcode
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 infinit3i/cve-2025-24893
PoC exploits CVE-2025-24893 , a remote code execution (RCE) vulnerability in XWiki caused by improper sandboxing in Groovy macros rendered…
 trungnguyen1909/cve-2019-8781-macos
Exploit POC for the bug CVE-2019-8781, found by @LinusHenze
 xooxo/cve-2019-14745
weaponized radare2 vulnerability found by @CaptnBanana and blenk92
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
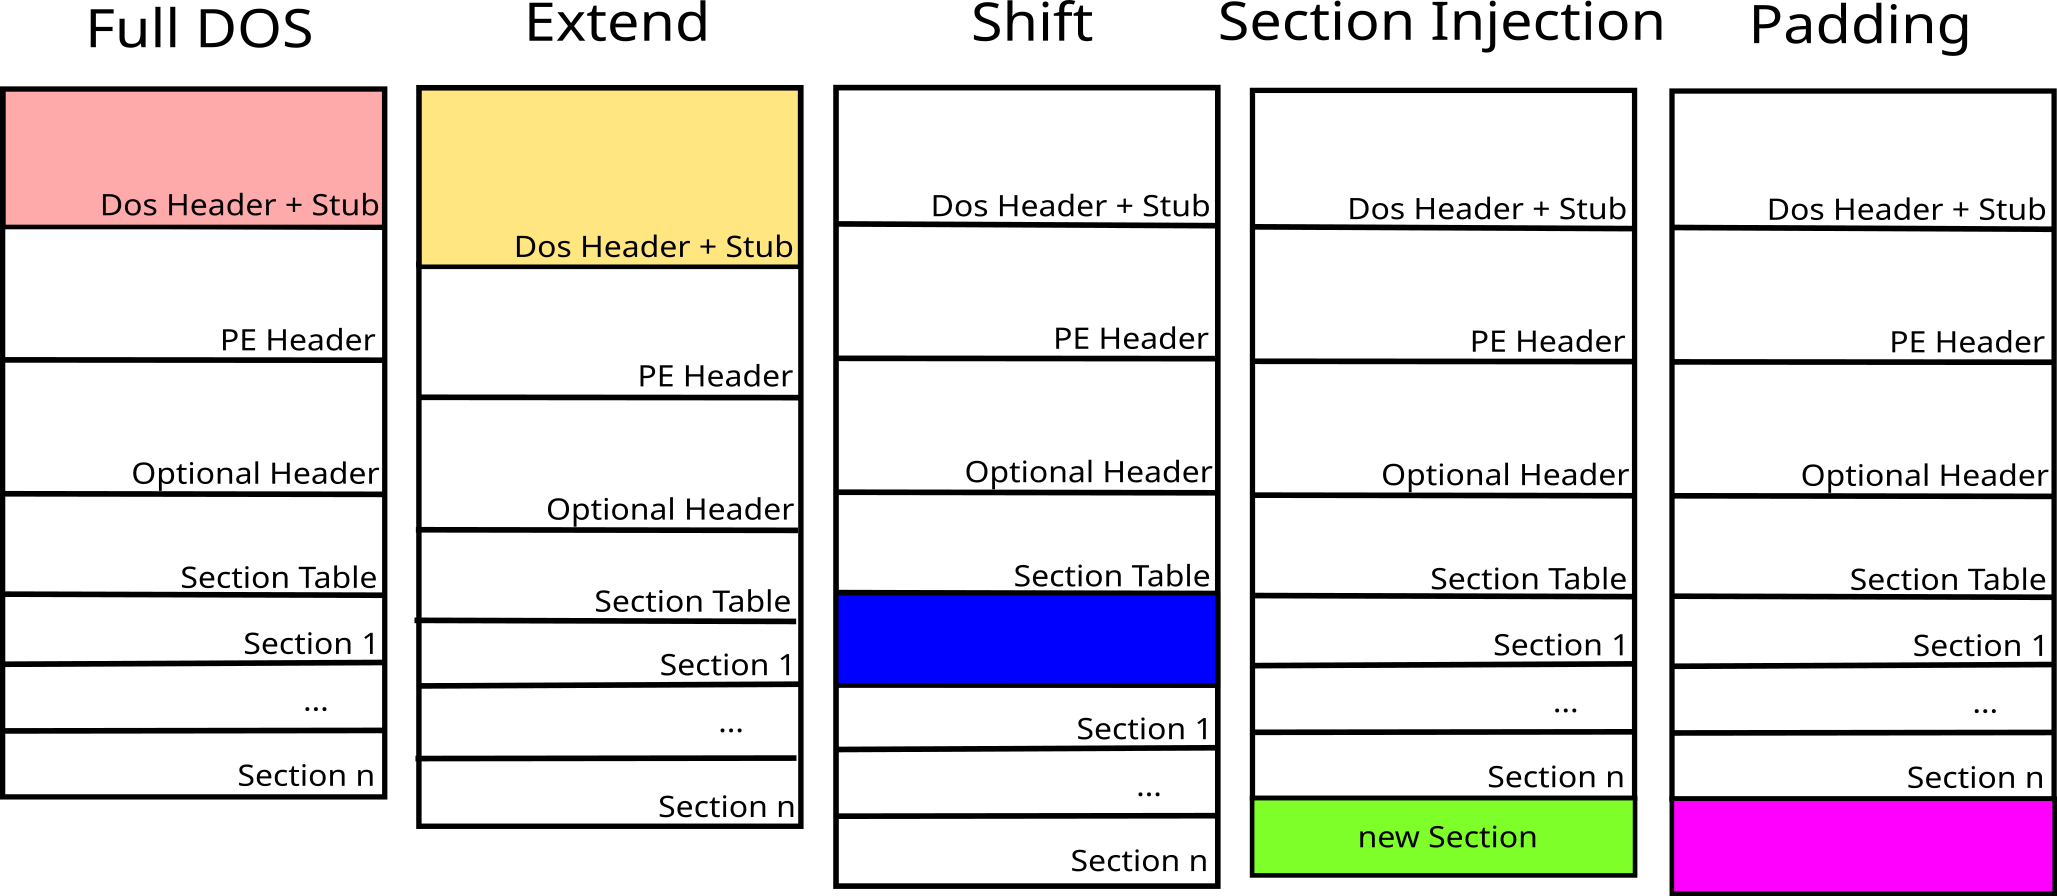
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 chvancooten/maldev-for-dummies
A workshop about Malware Development
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
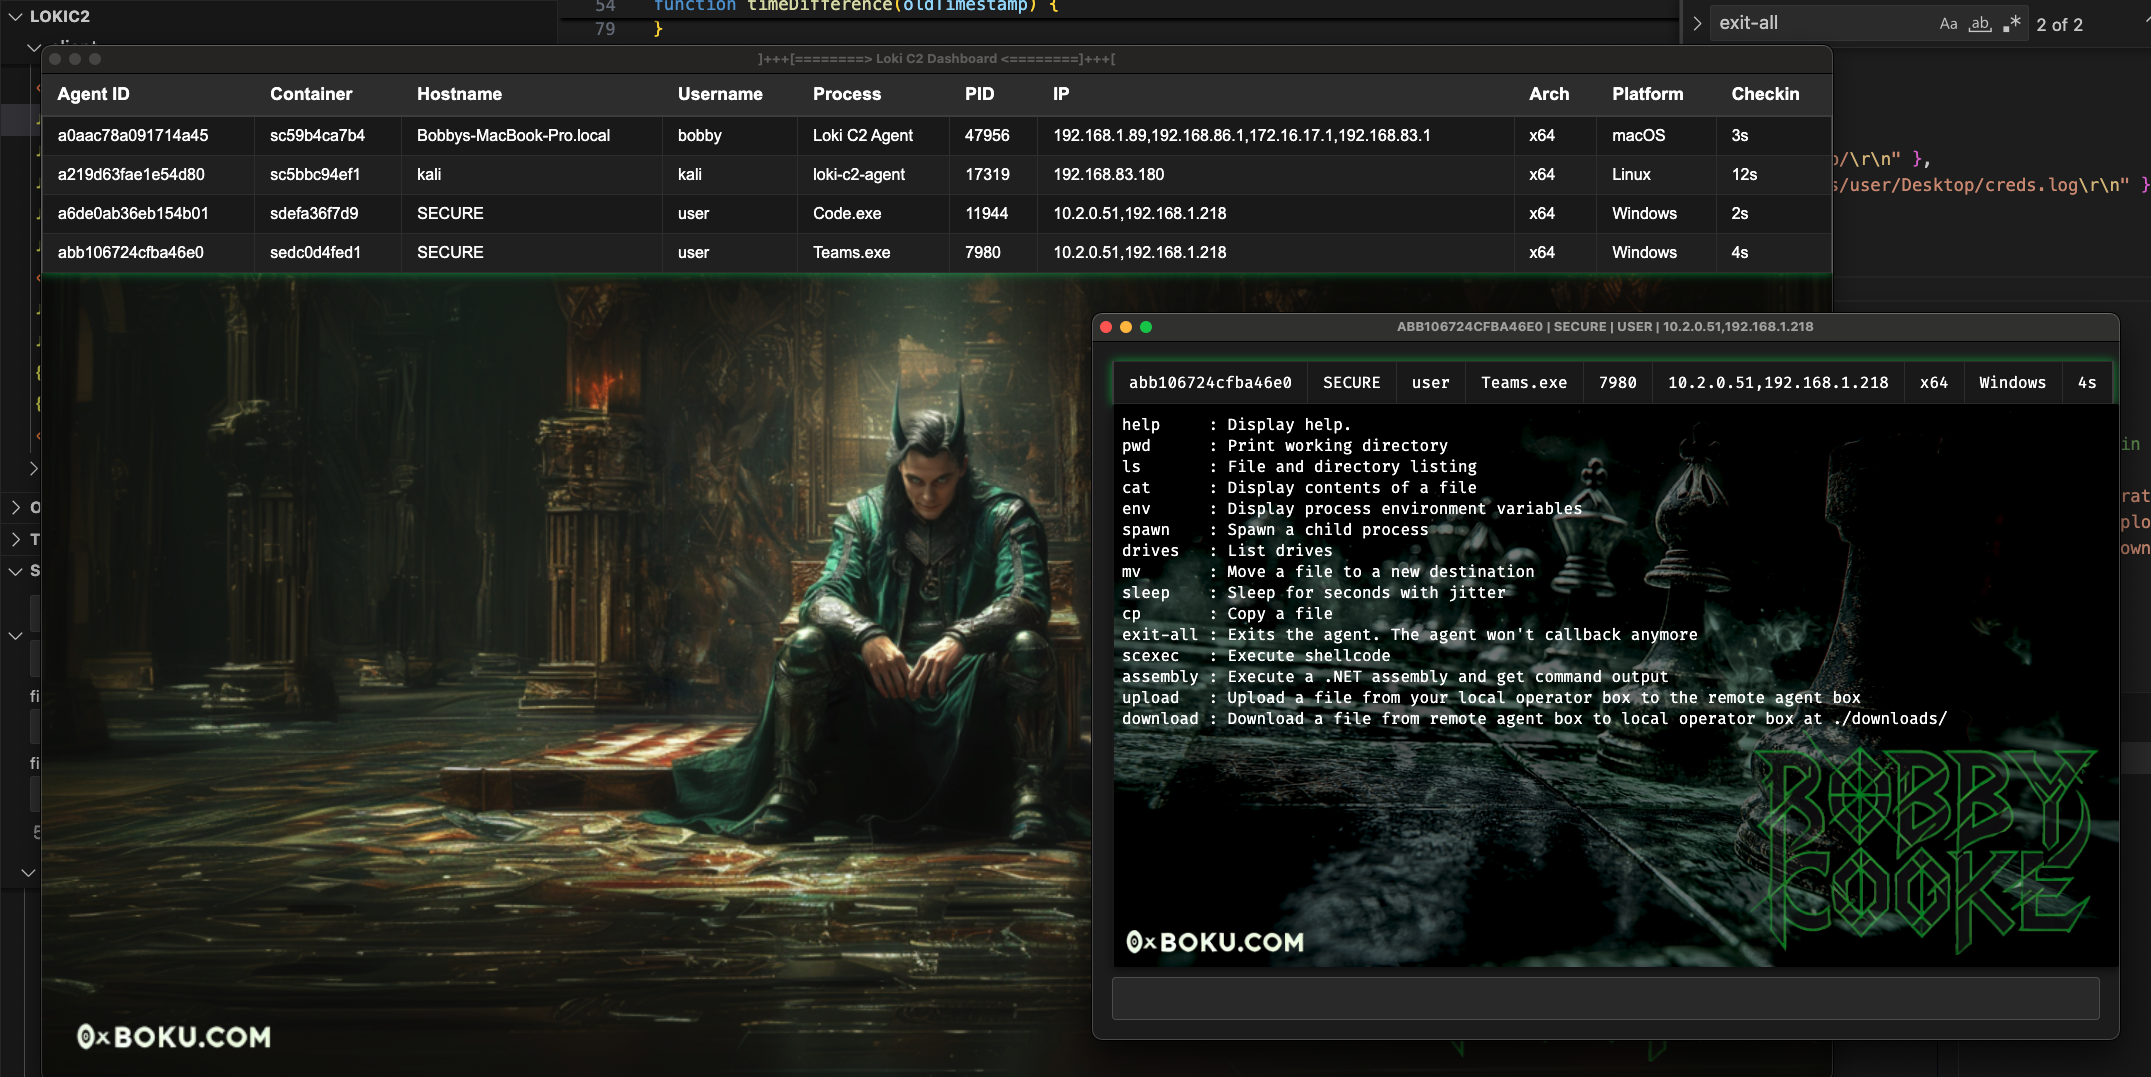 boku7/loki
🧙♂️ Node.js Command & Control for Script-Jacking Vulnerable Electron Applications