copyFail-CVE-2026-31431-workaround-bash

Provides a bash workaround script to mitigate CVE-2026-31431, preventing remote code execution via copy.fail exploit. Includes usage instructions for…

Provides a bash workaround script to mitigate CVE-2026-31431, preventing remote code execution via copy.fail exploit. Includes usage instructions for…

On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.

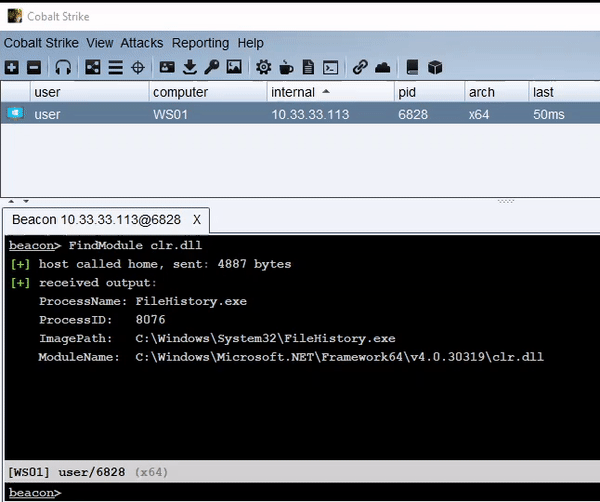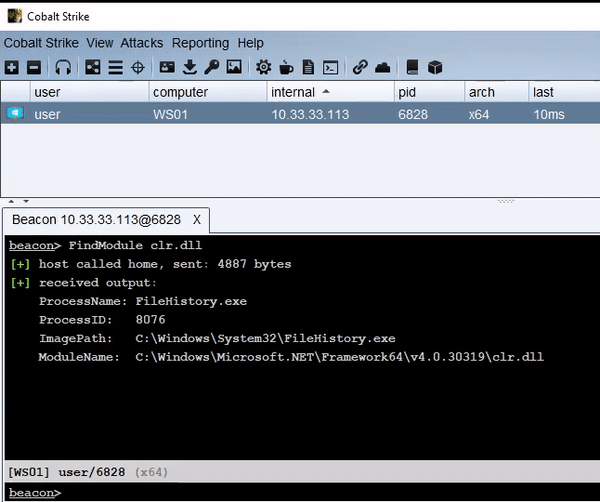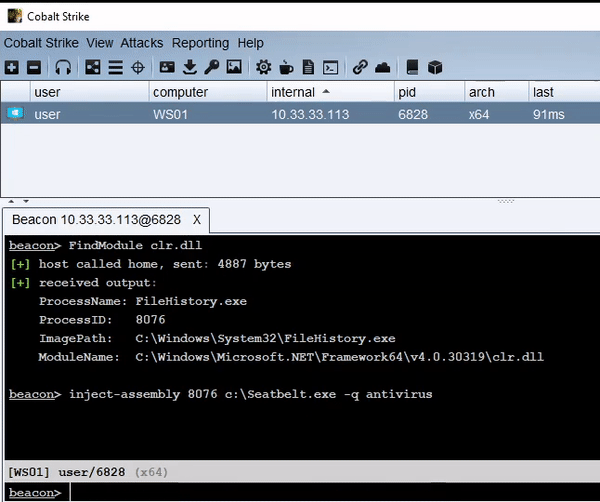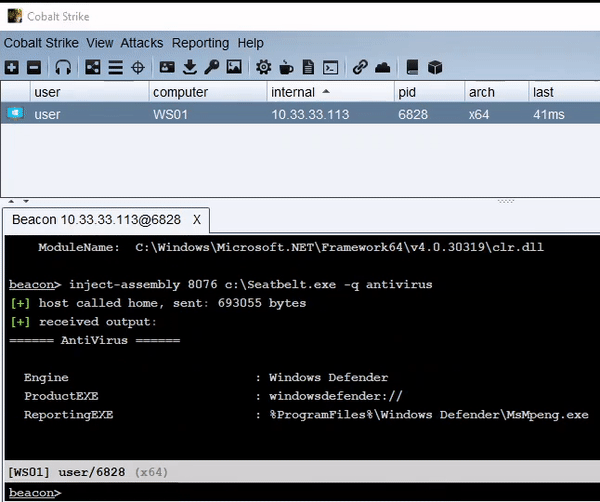
Inject .NET assemblies into an existing process

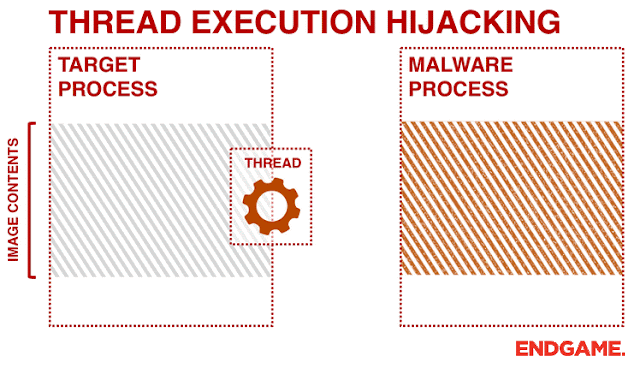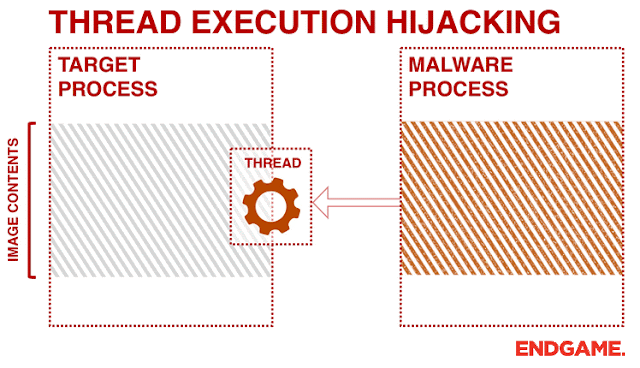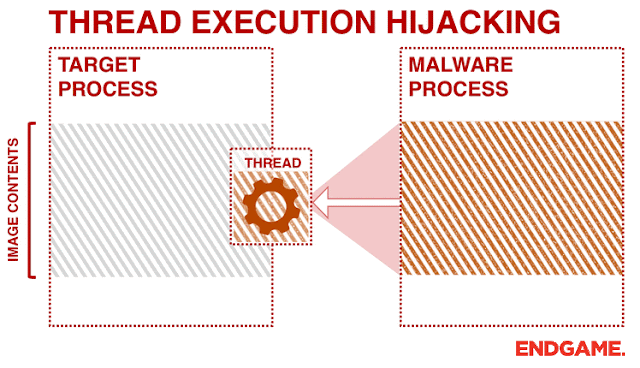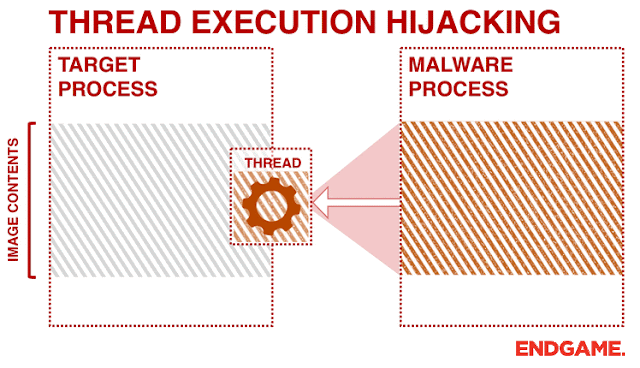
PoC Thread Execution Hijacking for Win32 Code Injection

Windows User-Mode Shellcode Development Framework (WUMSDF)

Proof of concept for CVE-2022-31814

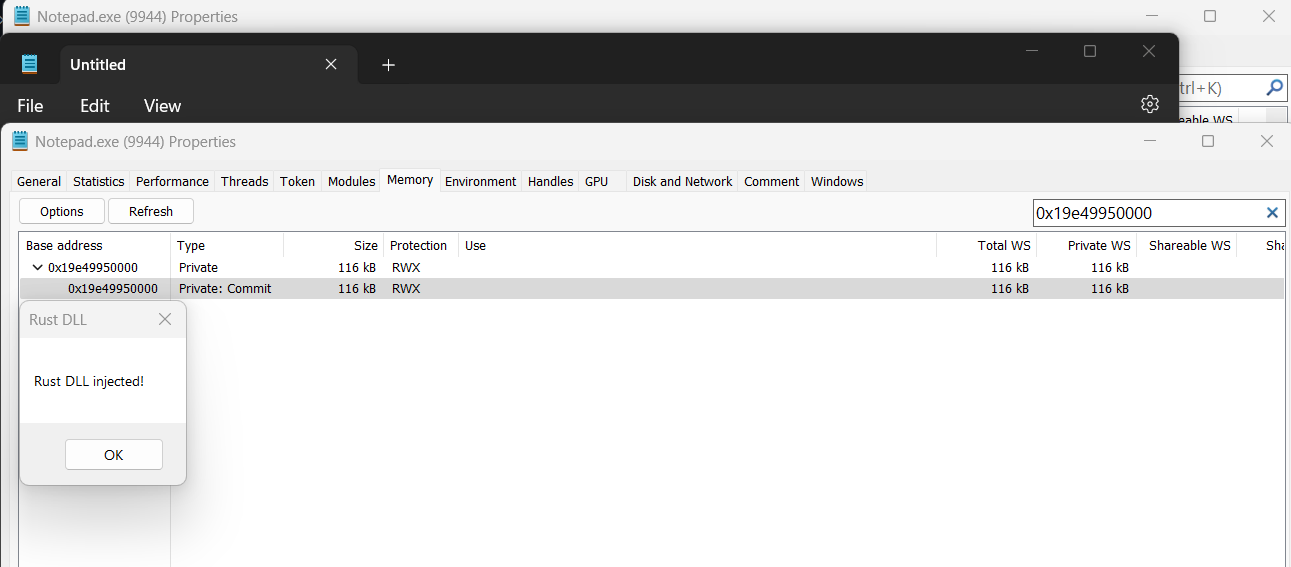
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)

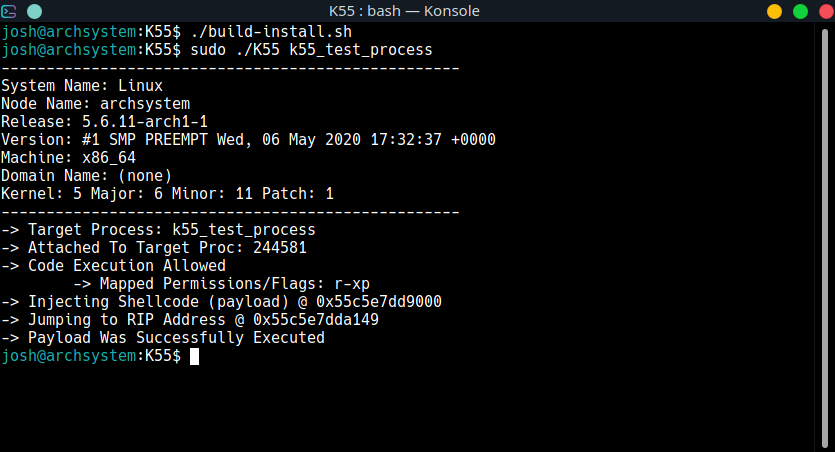
Inject a shared library (i.e. arbitrary code) into a live linux process, without ptrace

C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…

A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…

CVE-2023-22527 内存马注入工具

Full-chain exploit for CVE-2025-2783 (Ipcz Sandbox Escape & RCE).

Exploit for CVE-2022-42475, a pre-auth RCE in FortiOS SSL VPN. Supports validation, benign verification, and full exploitation with connect-back…

Rust Weaponization for Red Team Engagements.

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).