
CVE-2018-2628
 herantong/cve-2018-2628
Python-based exploit for CVE-2018-2628 targeting Oracle WebLogic Server, providing vulnerability detection and remote shell access via JSP payload…
exploitationpayload-generationpenetration-testing+3
1
herantong/cve-2018-2628Python-based exploit for CVE-2018-2628 targeting Oracle WebLogic Server, providing vulnerability detection and remote shell access via JSP payload…
 kmahyyg/cve-2022-22947
Exploit for CVE-2022-22947 in Spring Cloud Gateway, enabling remote code execution via maliciously crafted requests with integrated Godzilla memshell…
 moisestapia/cve-2022-3218
Python exploit for CVE-2022-3218 that generates a reverse TCP payload via msfvenom and delivers it over HTTP to a target Windows host.
 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
 dadosneurais/cve-2023-3824
Proof-of-concept exploit for CVE-2023-3824 (PHP phar deserialization) enabling remote code execution via crafted phar archive and reverse shell…
 rnnsz/cve-2008-4654
PoC exploit generator for CVE-2008-4654, a stack-based buffer overflow in VLC Media Player via crafted .ty+ files. Generates malicious payload file…
 rnnsz/cve-2017-8367
Python-based proof-of-concept exploit for CVE-2017-8367, a stack-based buffer overflow in Easy Mov Converter. Generates a payload file for local…
 b1gn0se/tomcat-cve-2025-24813
Proof-of-concept exploit for Apache Tomcat CVE-2025-24813, demonstrating remote code execution via partial PUT and deserialization. Includes Docker…
 caioprince/cve-2019-11395
Python exploit for CVE-2019-11395, a buffer overflow in MailCarrier 2.51 POP3 service. Generates a reverse shell payload via msfvenom and achieves…
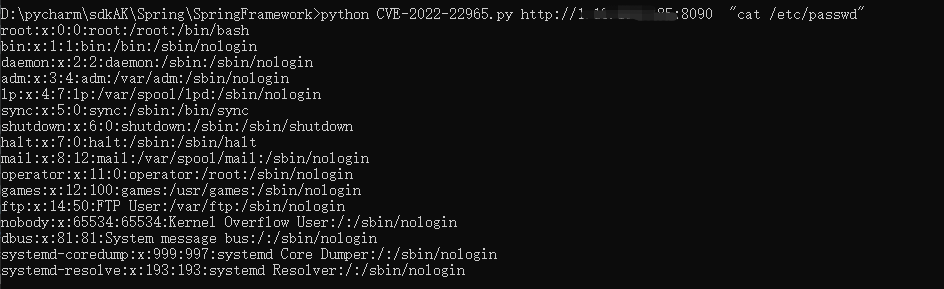 xsxtw/springframework_cve-2022-22965_rce
Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.
 f01965/cve-2019-8014
PoC and exploit for CVE-2019-8014 with shellcode payload (calc/CMD) triggered via crafted BMP image. Includes binary exploitation analysis.
 oddcod3/phantom-evasion
Python antivirus evasion tool
 mr-un1k0d3r/dkmc
DKMC - Dont kill my cat - Malicious payload evasion tool
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
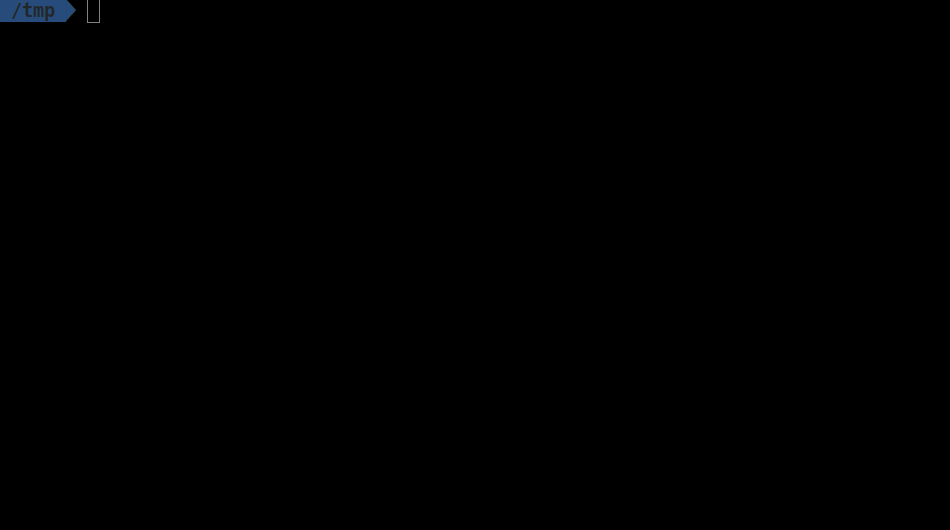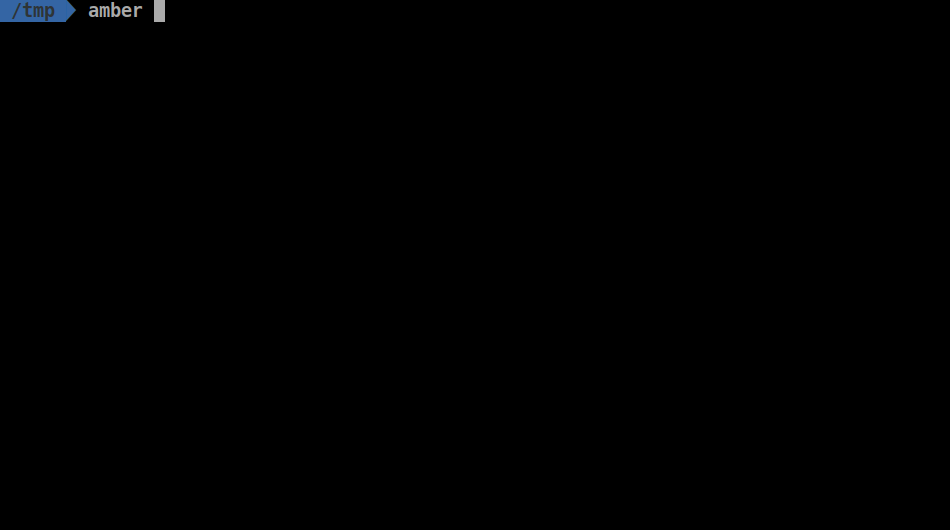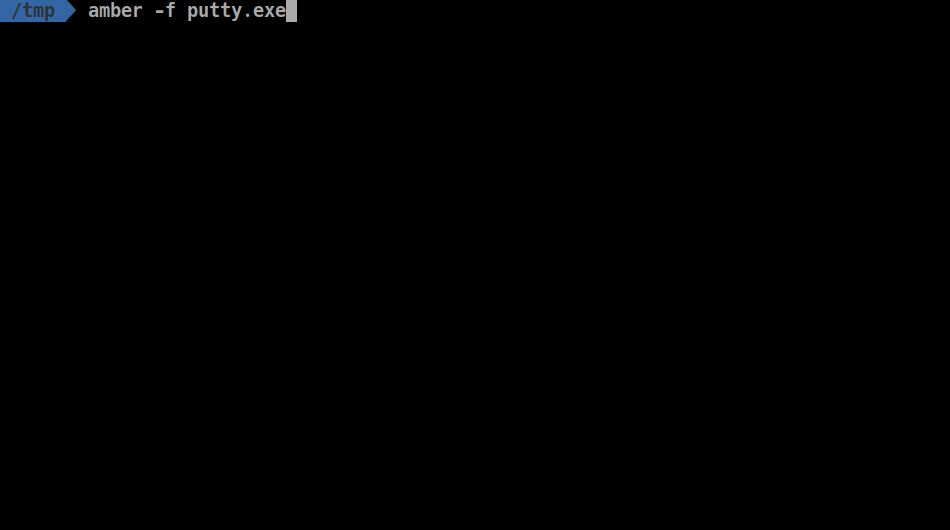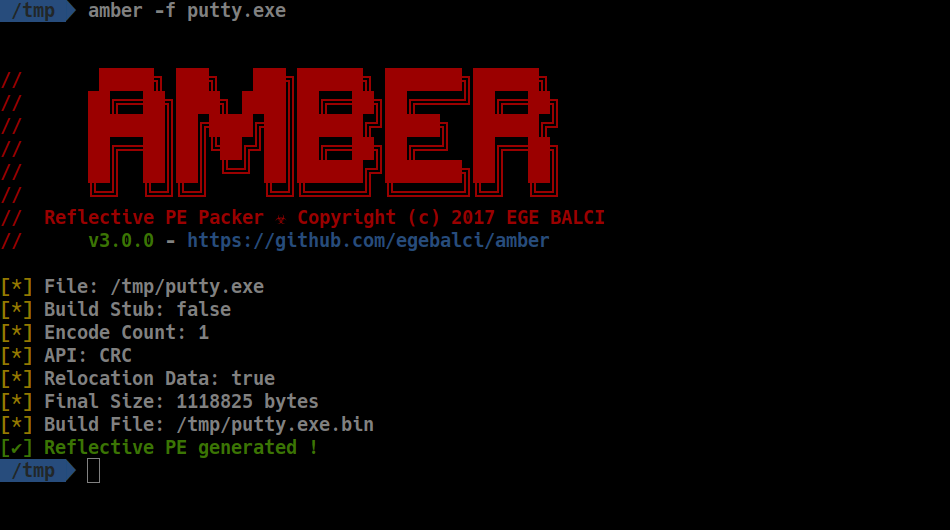 egebalci/amber
Reflective PE packer.
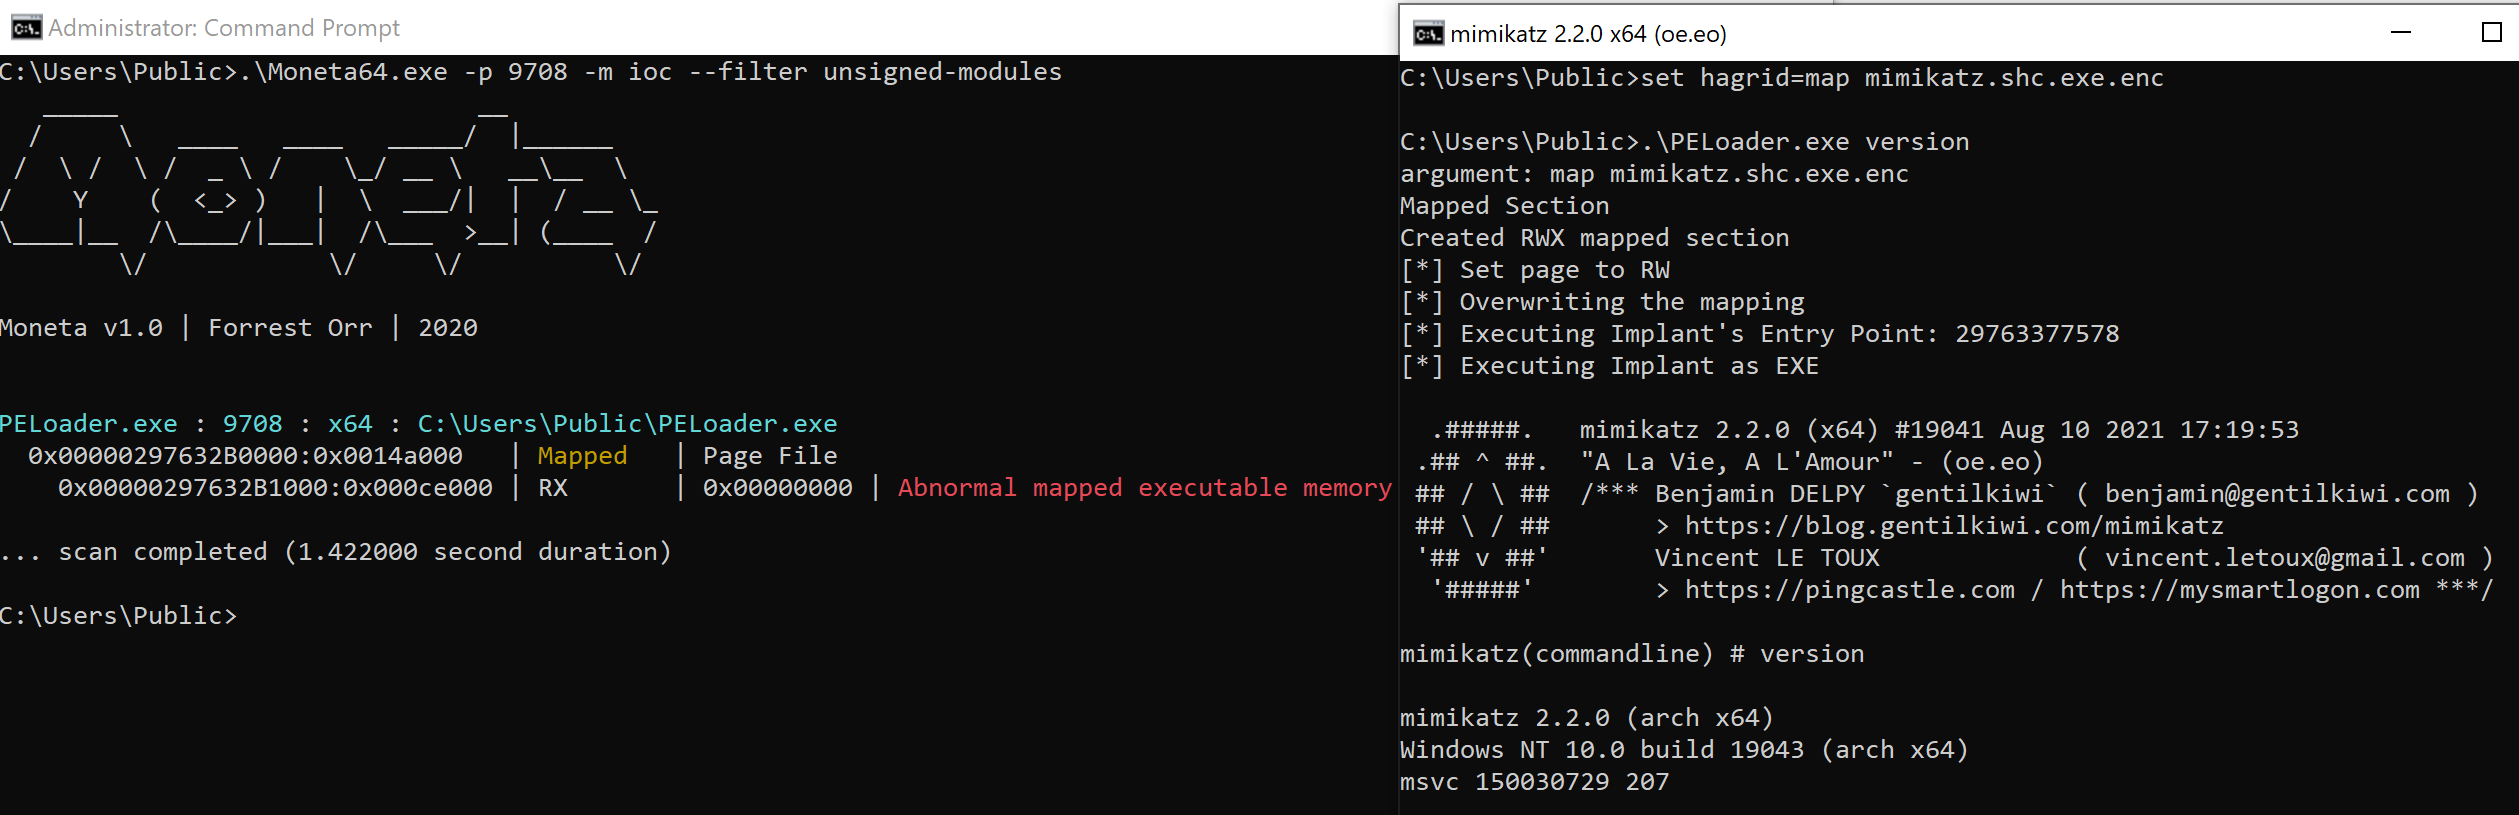 hagrid29/peloader
PE loader with various shellcode injection techniques
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 jfmaes/sharpziprunner
Executes position independent shellcode from an encrypted zip