ICMP-Ghost-A-Fileless-x64-Assembly-C2-Agent

Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

A shellcode function to encrypt a running process image when sleeping.

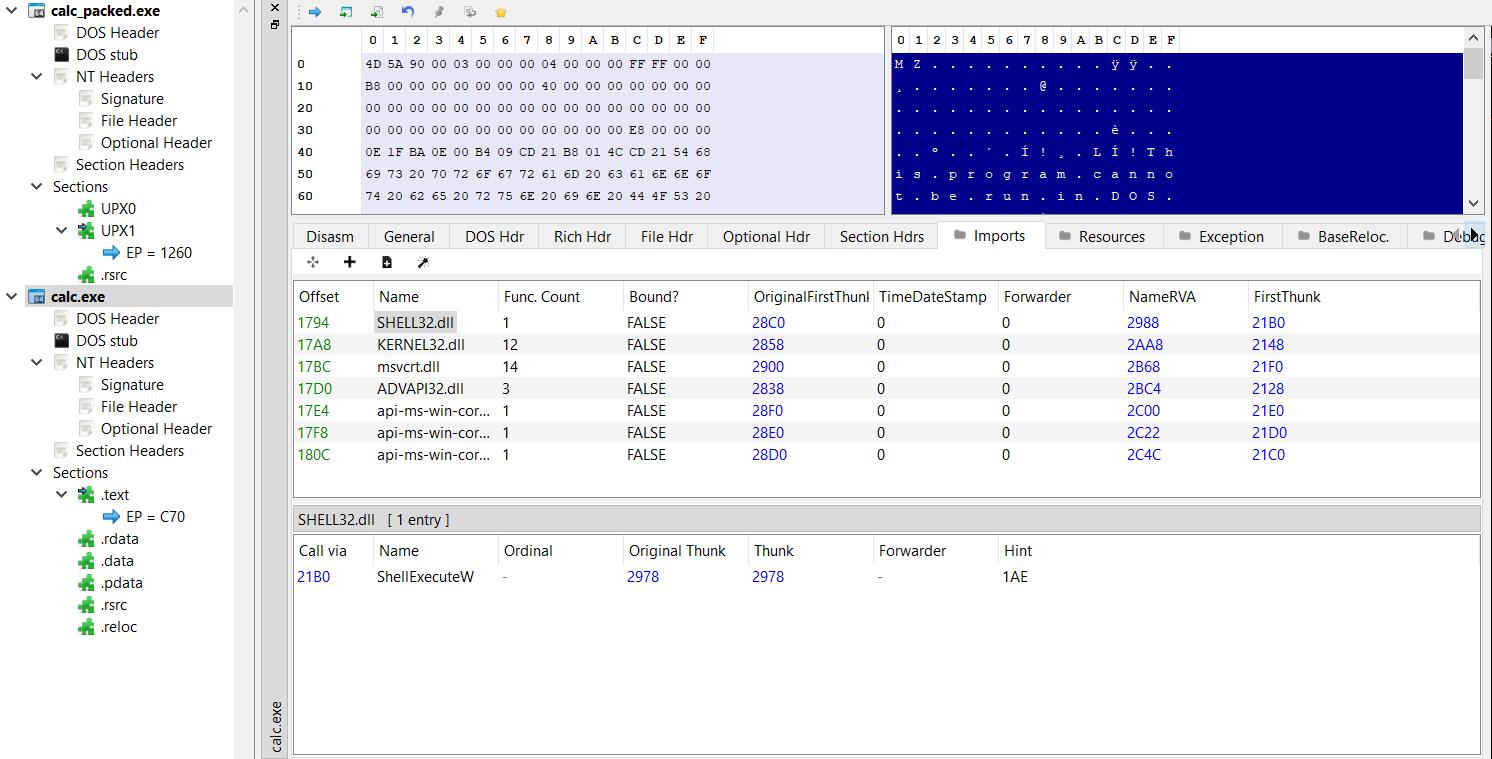
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.

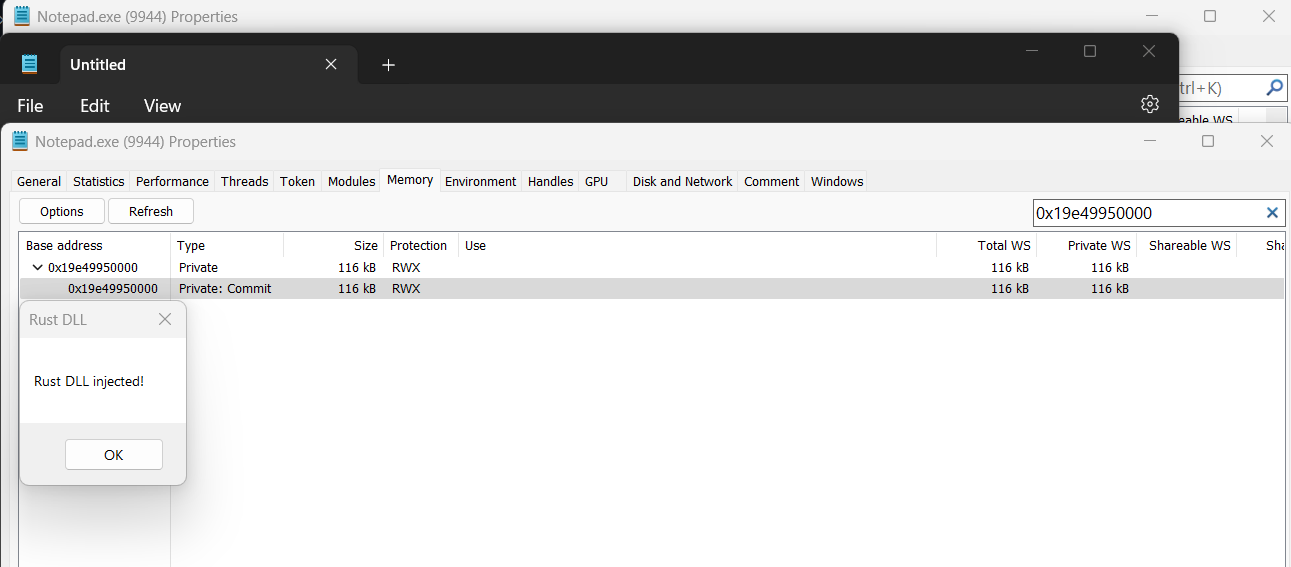
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)

Windows x64 handcrafted token stealing kernel-mode shellcode

Script to exploit CVE-2023-38035

Remote root exploit for the SAMBA CVE-2017-7494 vulnerability

Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…

Python-based exploit for CVE-2021-21086 in Adobe Acrobat Reader DC, generating malicious PDFs with shellcode execution via crafted font charstrings.

A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.

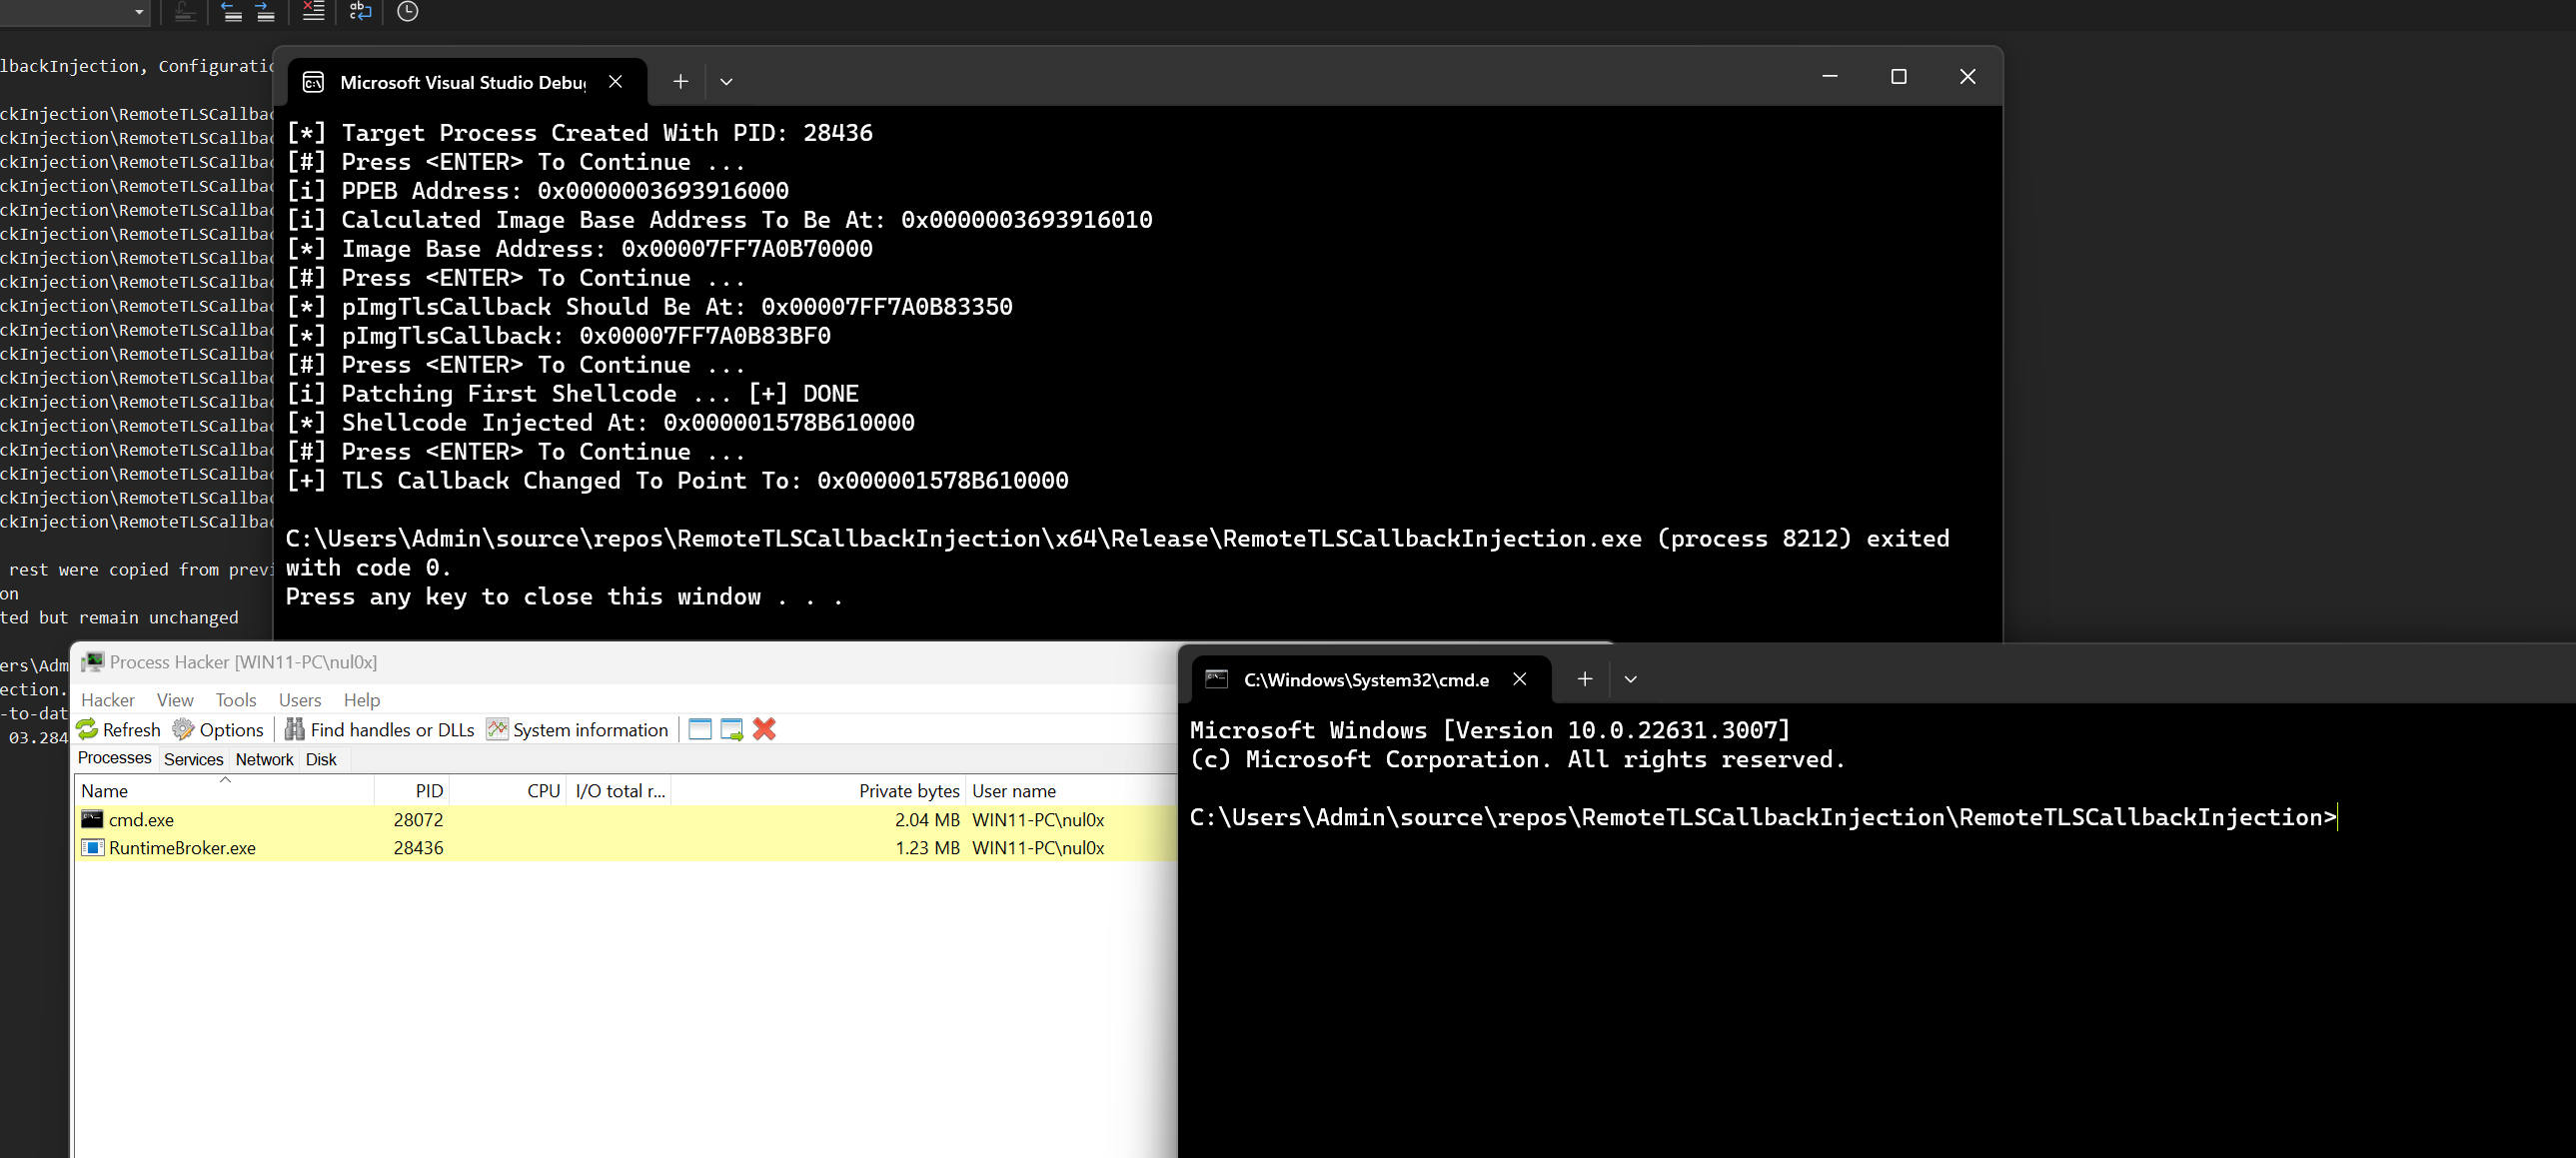
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process

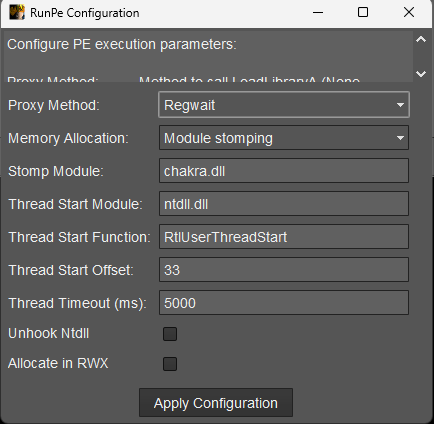
BOF to run PE in Cobalt Strike Beacon without console creation

Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…

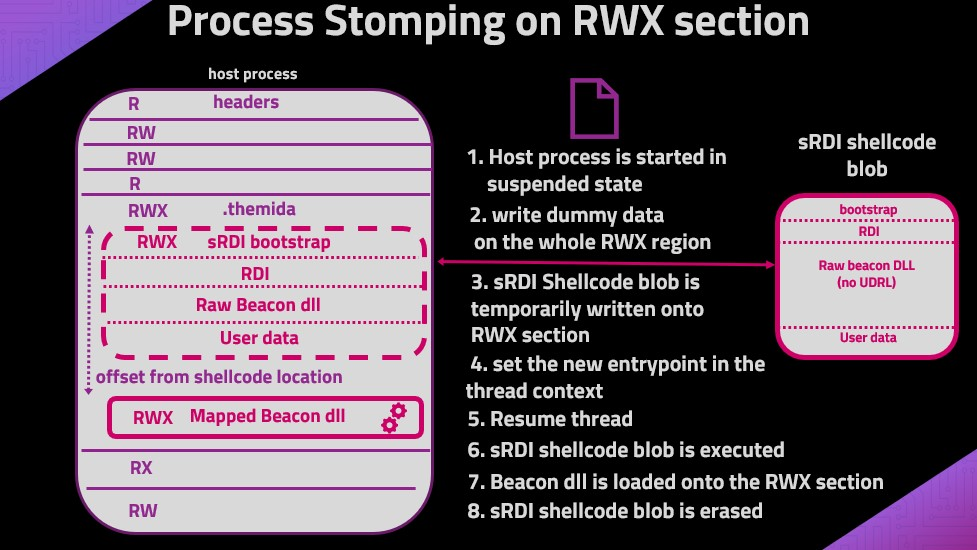
A variation of ProcessOverwriting to execute shellcode on an executable's section

NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection

Inject a shared library (i.e. arbitrary code) into a live linux process, without ptrace

A set of fully-undetectable process injection techniques abusing Windows Thread Pools

Threadless Process Injection using remote function hooking.