

gef
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
ai-assisted-reversingbinary-analysisbinary-exploitation+10
8.4k
hugsy/gefGEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 keelanbrady1011/cve-2024-36401
CVE-2024-36401 exploit with webshell-like functionality for limited environments, supporting self-signed TLS sessions and remote command execution…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
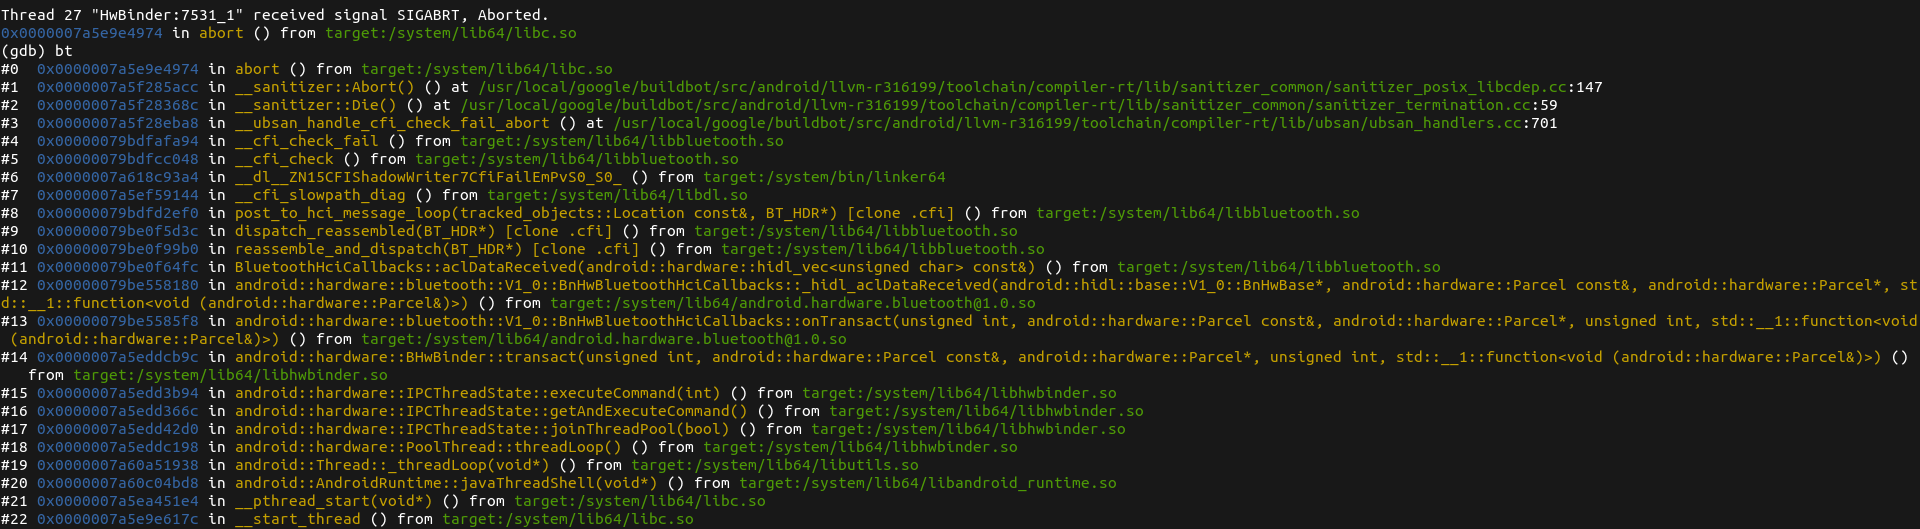 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 bytereaper77/dirty-pipe
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 jasperla/cve-2017-9101
Authenticated remote code execution exploit for PlaySMS 1.4 via CSV phonebook upload. Provides single-command and interactive shell modes for…
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 voidsec/exploit-development
Exploit Development - Weaponized Exploit and Proof of Concepts (PoC)
 marcingadz/spring-rce-poc
Testing CVE-2022-22968
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 redcode-labs/gosh
Golang reverse/bind shell generator
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 gh0x0st/invoke-psobfuscation
An in-depth approach to obfuscating the individual components of a PowerShell payload whether you're on Windows or Kali Linux.
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!