

CVE-2017-16994
 jedai47/cve-2017-16994
Linux kernel local privilege escalation exploit for CVE-2017-16994, leveraging null pointer dereference and mmap_min_addr bypass to achieve root…
binary-exploitationexploitationmemory-forensics+2
jedai47/cve-2017-16994Linux kernel local privilege escalation exploit for CVE-2017-16994, leveraging null pointer dereference and mmap_min_addr bypass to achieve root…
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
 d0n601/cve-2025-13390
WP Directory Kit <= 1.4.4 - Authentication Bypass to Privilege Escalation via Account Takeover
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
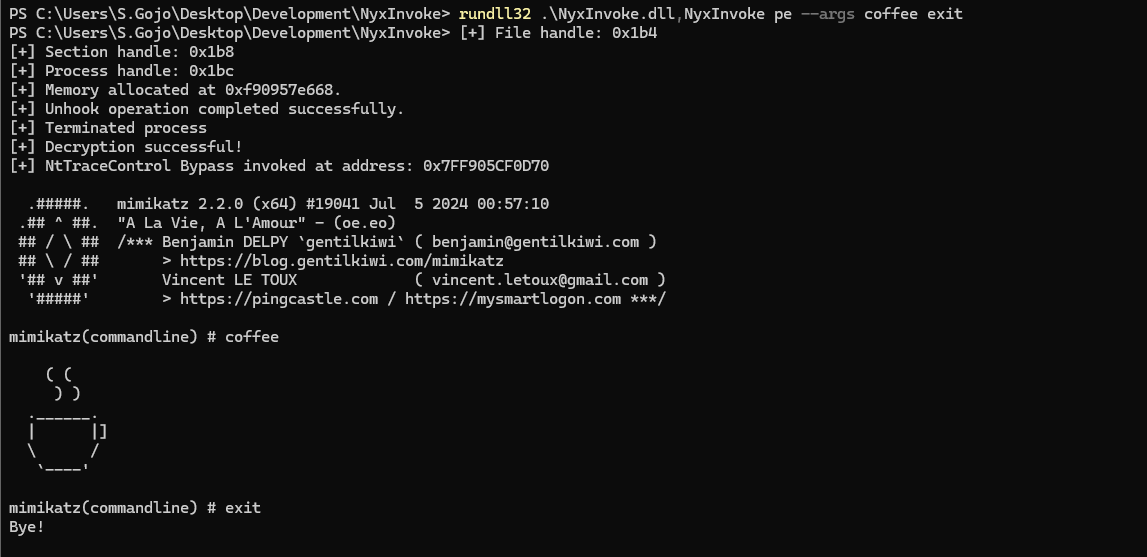 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
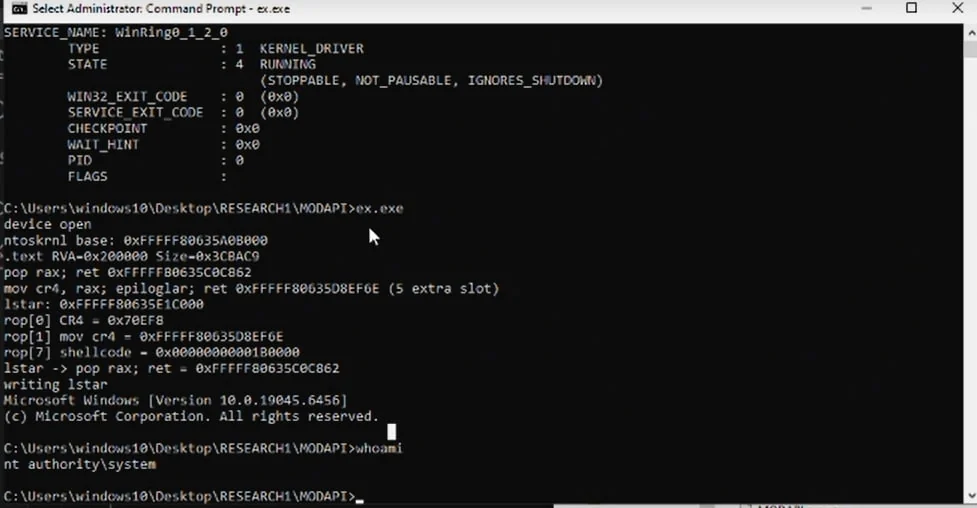 mein-0/lolmodapi
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.
 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 luke0x90/cve-2021-21551
Proof-of-concept exploit for CVE-2021-21551: Windows local privilege escalation via Dell dbutil_2_3.sys driver. Implements read/write primitives,…
 damariion/cve-2015-8522.rce
Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 0neb1n/cve-2020-1349
Exploit for Outlook 2019 zero-click vulnerability CVE-2020-1349, using MIME header parsing bugs to achieve heap overflow and EIP control via vftable…
 manojcode/foxit-reader-rce-with-virualalloc-and-shellcode-for-cve-2018-9948-and-cve-2018-9958
Foxit Reader version 9.0.1.1049 Use After Free with ASLR and DEP bypass on heap
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 maorbuskila/windows-x64-rat
Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…
 nccgroup/winpayloads
Undetectable Windows Payload Generation
