
CVE-2025-34096
 themalwareguardian/cve-2025-34096
SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.
binary-exploitationeducationexploitation+6
themalwareguardian/cve-2025-34096SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.
 rai2en/cve-2023-50564_pluck-v4.7.18_poc
A Proof of Concept for CVE-2023-50564 vulnerability in Pluck CMS version 4.7.18
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 aadi0258/exploit-cve-2024-23897
Exploit for CVE-2024-23897 in Jenkins, enabling file read and remote code execution via crafted requests. Includes Docker setup and Groovy scripts…
 kai-one001/wordpress-ht-contact-cve-2025-7340-rce
Python exploit for CVE-2025-7340, an unauthenticated file upload vulnerability in the WordPress HT Contact Form widget, enabling remote code…
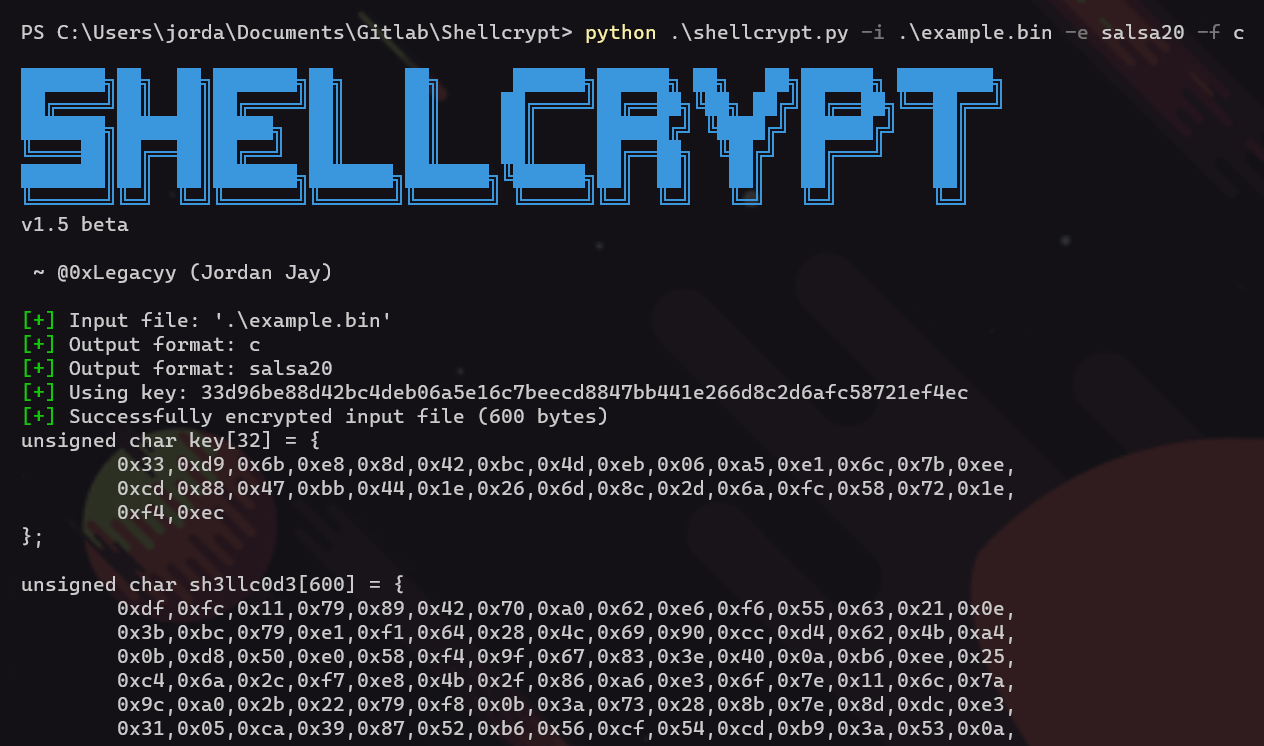 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 nxploited/cve-2025-32206
WordPress Processing Projects Plugin <= 1.0.2 is vulnerable to Arbitrary File Upload
 ktn1990/cve-2024-51793
(CVE-2024-51793) Wordpress Plugin: Computer Repair Shop <= 3.8115 - Unauthenticated Arbitrary File Upload
 rashidkhanpathan/cve-2022-40471
RCE Exploit and Research
 yukinime/cve-2025-34085
Automated scanner and exploit for CVE-2025-34085, an unauthenticated RCE in the WordPress Simple File List plugin. Supports multi-target scanning,…
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 ill-deed/cve-2025-34085-multi-target
Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…
 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
 im-hanzou/jbwper
Automatic Mass Tool for check and exploiting vulnerability in CVE-2022-4061 - JobBoardWP < 1.2.2 - Unauthenticated Arbitrary File Upload
 nu11secur1ty/shellupload
PHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.
 riftsandroses/cve-2024-50986
An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)
 rnnsz/cve-2017-8367
Python-based proof-of-concept exploit for CVE-2017-8367, a stack-based buffer overflow in Easy Mov Converter. Generates a payload file for local…