

HandleKatz
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
defensive-toolsmemory-forensicspayload-generation+3
596
codewhitesec/handlekatzPIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
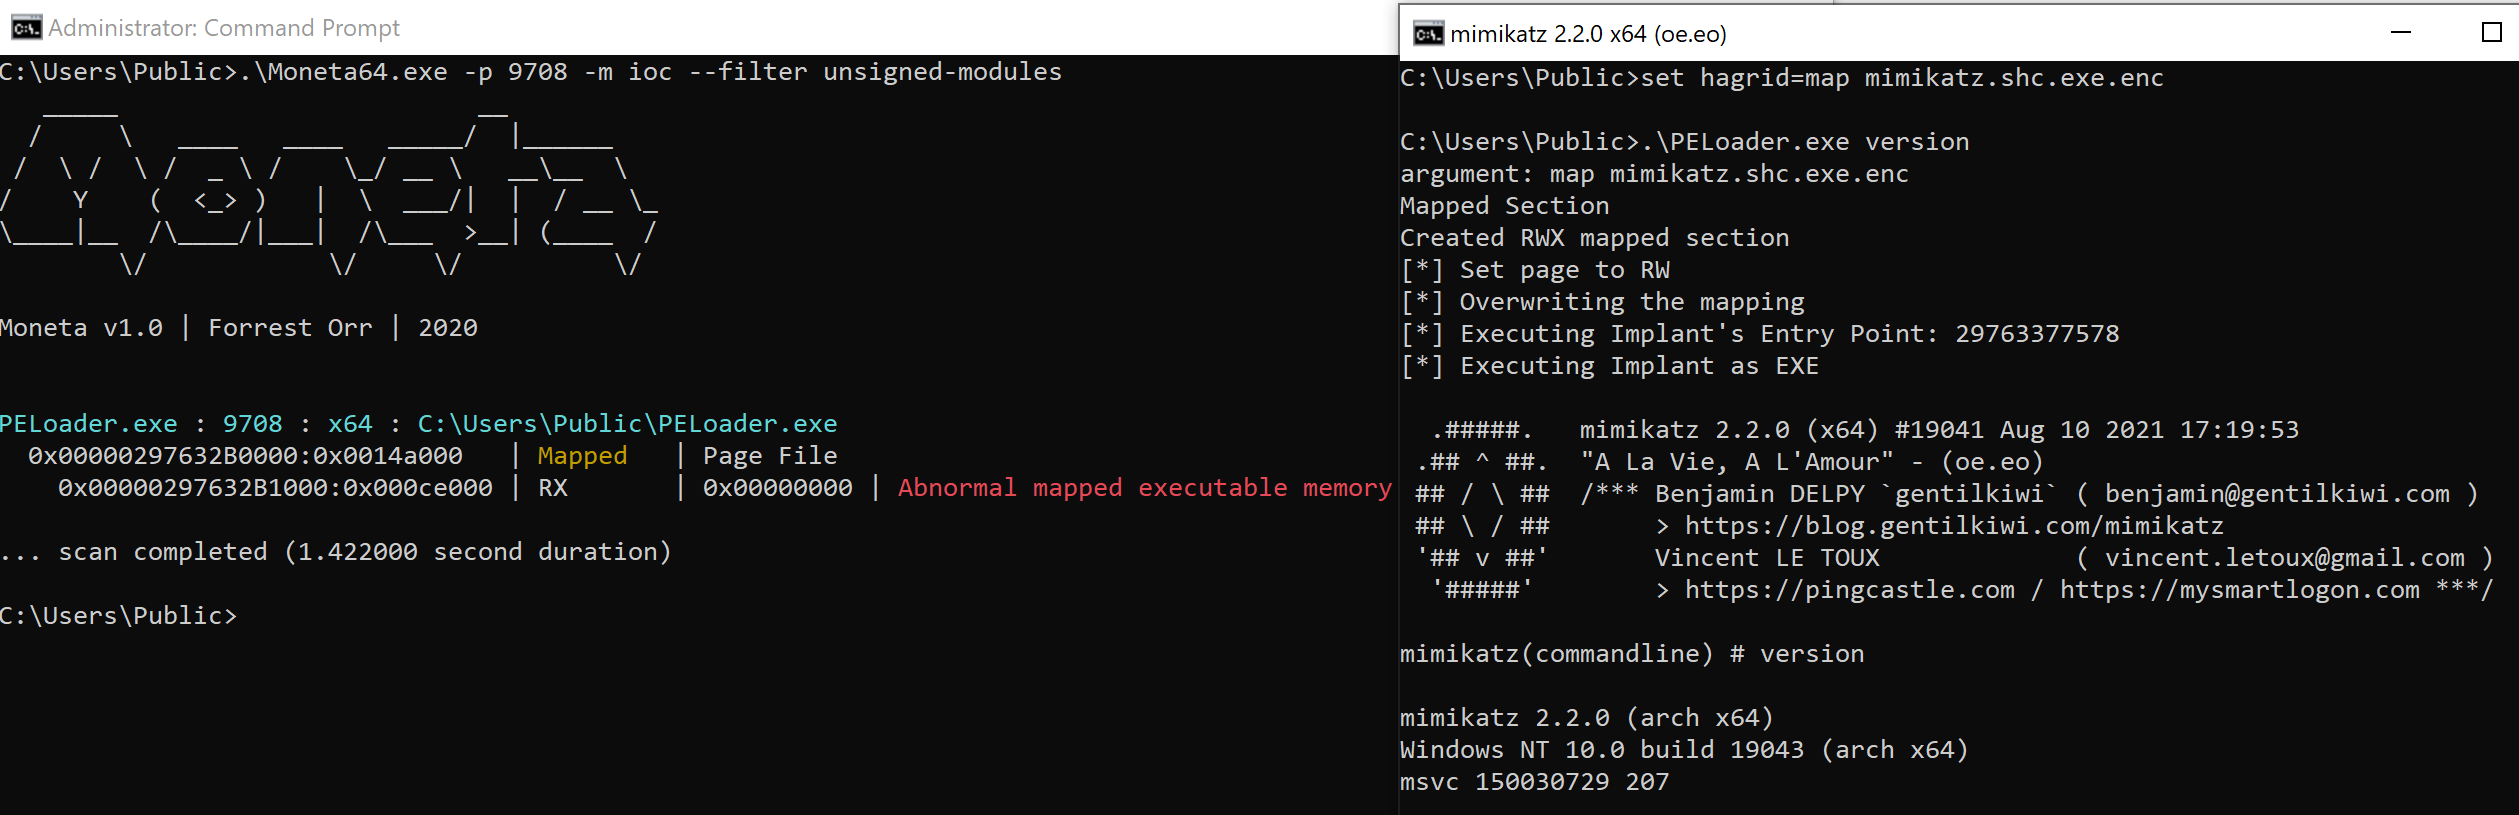 hagrid29/peloader
PE loader with various shellcode injection techniques
 sslab-gatech/pwn2own2020
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
 stong/cve-2020-15368
CVE-2020-15368, aka "How to exploit a vulnerable driver"
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities

 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
 bishopfox/cve-2023-3519
RCE exploit for CVE-2023-3519