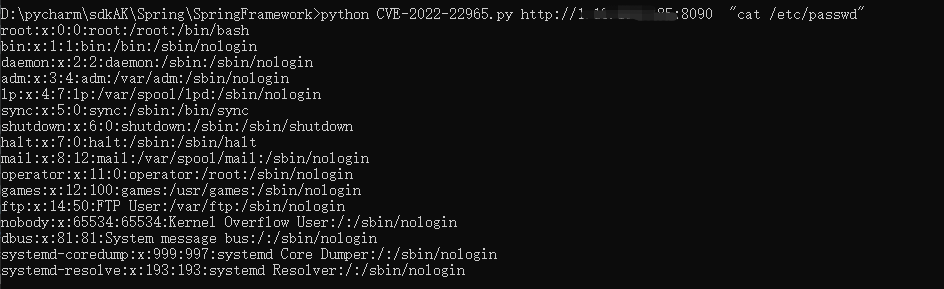
SpringFramework_CVE-2022-22965_RCE

Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.

Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.

cve-2018-6574

https://www.exploit-db.com/exploits/49757

Automated exploit for CVE-2024-23740 targeting Kap on macOS. Injects code via RunAsNode and enableNodeClilnspectArguments to spawn a remote shell.

CVE-2023-41425 Refurbish

Exploit for Easy File Sharing FTP Server 3.5 on Win7 32


CVE-2024-39069

Exploit script for CVE-2020-24186 in WordPress that uploads a camouflaged PHP webshell and provides interactive or reverse shell access with optional…

A python implementation of CVE-2004-2271 targeting MiniShare 1.4.1.

Automated exploit for CVE-2024-23741 targeting Hyper on macOS. Validates vulnerability and injects code to spawn a remote shell via RunAsNode and…

Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.

Go-based exploit for CVE-2025-32433

C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode in…

PoC and exploit for CVE-2019-8014 with shellcode payload (calc/CMD) triggered via crafted BMP image. Includes binary exploitation analysis.

Python exploit for CVE-2019-11447 that uploads a PHP reverse shell to CuteNews 2.1.2, enabling remote command execution on vulnerable web…

Python exploit for CVE-2019-11395, a buffer overflow in MailCarrier 2.51 POP3 service. Generates a reverse shell payload via msfvenom and achieves…

This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220