

baron-samedit
 czeti/baron-samedit
This repository contains a Proof-of-Concept (PoC) exploit for the Baron Samedit vulnerability (CVE-2021-3156). The exploit demonstrates privilege…
binary-exploitationexploitationpayload-development+4
czeti/baron-sameditThis repository contains a Proof-of-Concept (PoC) exploit for the Baron Samedit vulnerability (CVE-2021-3156). The exploit demonstrates privilege…
 yaoxiaoangry3/flangvik
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode in…
 1342486672/flangvik
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode in…
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.
 maldevel/gdog
A fully featured Windows backdoor that uses Gmail as a C&C server
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
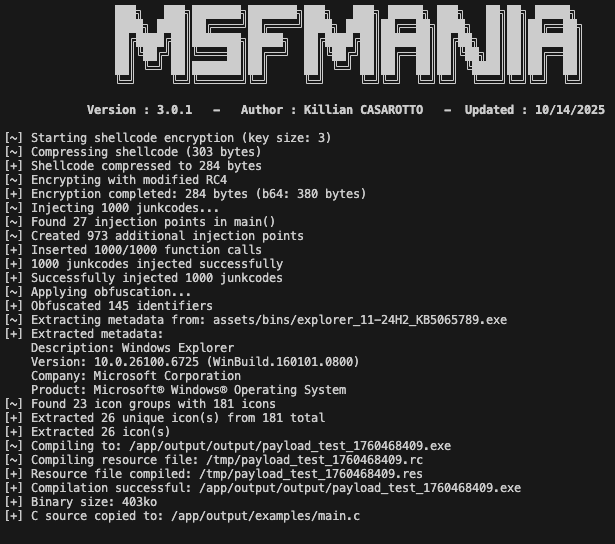 lepotekil/msfmania
Python AV Evasion Tools
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
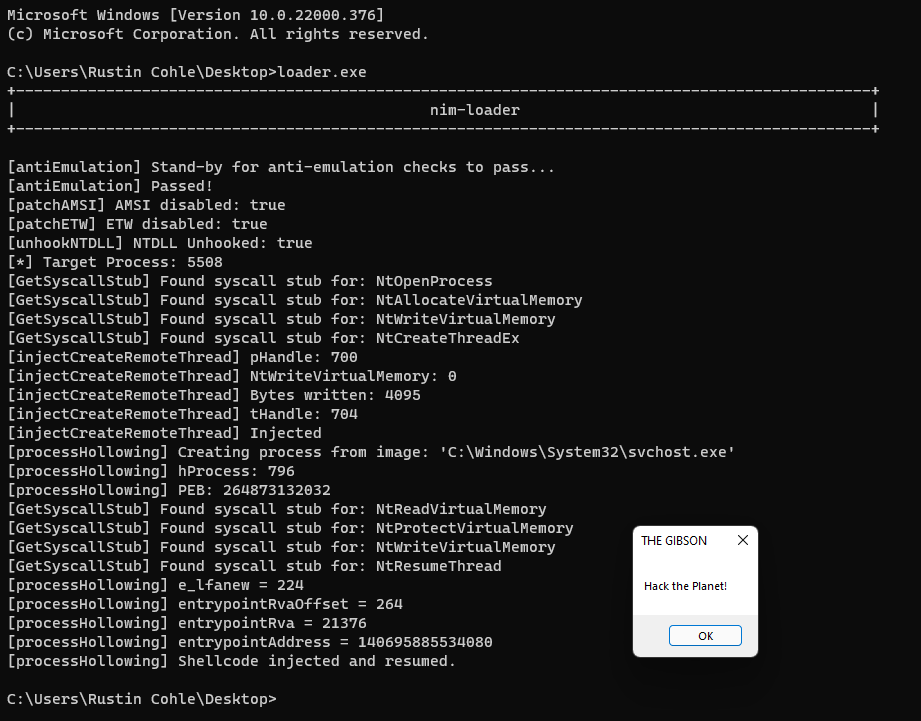 adamsvoboda/nim-loader
WIP shellcode loader in nim with EDR evasion techniques
 buffer/pylibemu
A Libemu Cython wrapper
 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 zx0cf1/shredder-rs
A high-fidelity x86_64 polymorphic mutation engine focused on instruction-level fragmentation and context preservation.
 rsmudge/cve-2020-0796-bof
Cobalt Strike Beacon Object File implementing CVE-2020-0796 SMBGhost local privilege escalation with dual weaponization paths for token theft and…
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).