
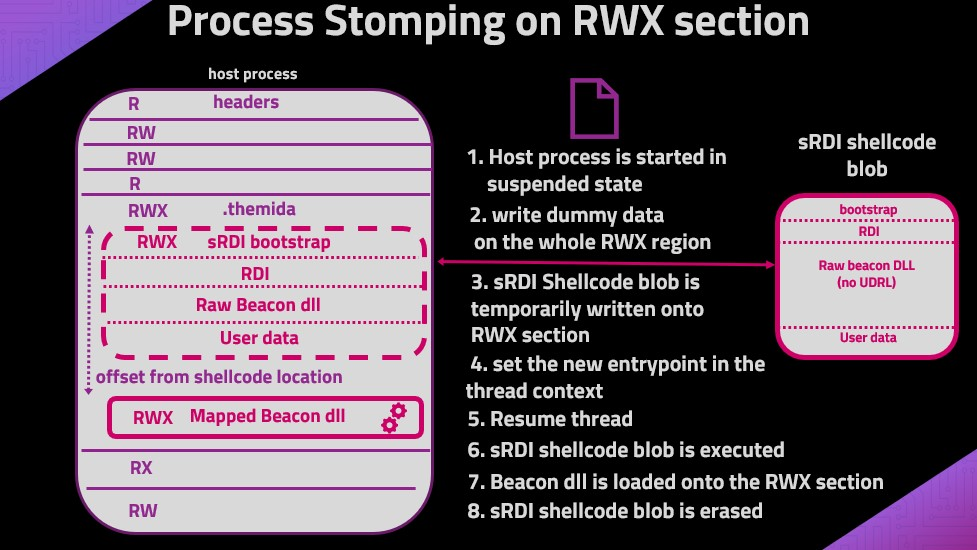
ProcessStomping
 naksyn/processstomping
A variation of ProcessOverwriting to execute shellcode on an executable's section
binary-exploitationeducationpayload-development+3
147
naksyn/processstompingA variation of ProcessOverwriting to execute shellcode on an executable's section
 yo-yo-yo-jbo/msf_shellcode_analysis
Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.