
CVE-2024-35106-POC
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…

Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…

Python exploit for CVE-2022-29464 targeting WSO2 web servers with automated webshell upload and command execution capabilities.

Proof-of-concept remote code execution exploit targeting Safari 11.0.3 on macOS 10.13.3 via a WebAssembly section vulnerability (CVE-2018-4121).…

Linux kernel local privilege escalation exploit for CVE-2017-16994, leveraging null pointer dereference and mmap_min_addr bypass to achieve root…

Exploit for CVE-2003-0264 based on pwntools and metasploit's windows/reverse_tcp

Exploit script for CVE-2020-24186 in WordPress that uploads a camouflaged PHP webshell and provides interactive or reverse shell access with optional…

This repository contains a Proof-of-Concept (PoC) exploit for the Baron Samedit vulnerability (CVE-2021-3156). The exploit demonstrates privilege…

Proof-of-concept exploit for Apache Tomcat CVE-2025-24813, demonstrating remote code execution via partial PUT and deserialization. Includes Docker…

Proof-of-concept remote code execution exploit for Safari 11.0.3 on macOS 10.13.3, leveraging a WebAssembly section vulnerability with heap spray and…

Automated exploit for CVE-2024-23741 targeting Hyper on macOS. Validates vulnerability and injects code to spawn a remote shell via RunAsNode and…

Python exploit for CVE-2019-11395, a buffer overflow in MailCarrier 2.51 POP3 service. Generates a reverse shell payload via msfvenom and achieves…

Proof-of-concept exploit for CVE-2021-21551: Windows local privilege escalation via Dell dbutil_2_3.sys driver. Implements read/write primitives,…

Exploit for CVE-2018-20250 (WinRAR ACE path traversal) with automated payload generation and Metasploit reverse shell integration for penetration…

Tools for get offsets and adding patch for support i386

Automated exploit tool targeting CVE-2024-52010 for penetration testing and vulnerability validation.

Patched GNU Bash 3.2 with a fix for CVE-2014-6271 (Shellshock). Provides a standard POSIX shell with command-line editing, job control, and history…

Patched GNU Bash 4.3 with fix for Shellshock (CVE-2014-6271). Provides a secure Bourne Again SHell with command-line editing, job control, and…

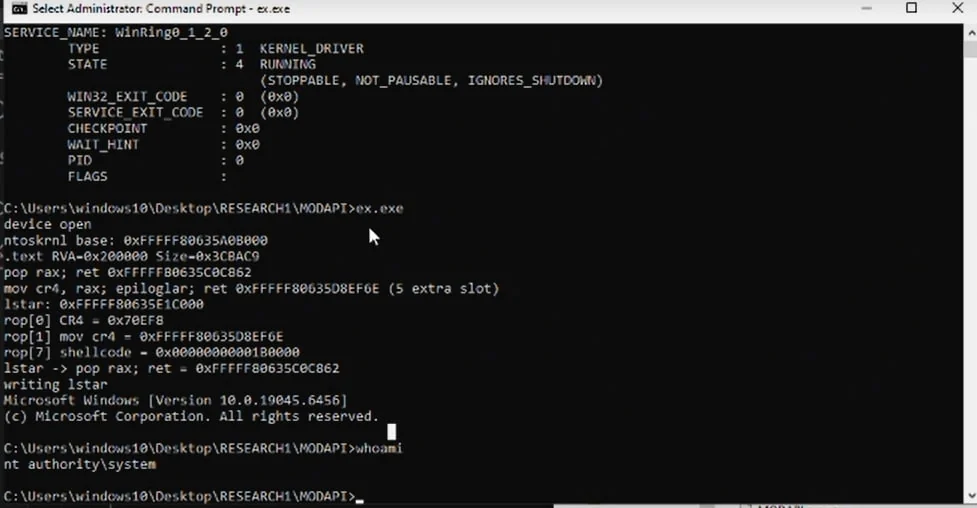
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.