

r77-rootkit
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k
bytecode77/r77-rootkitFileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
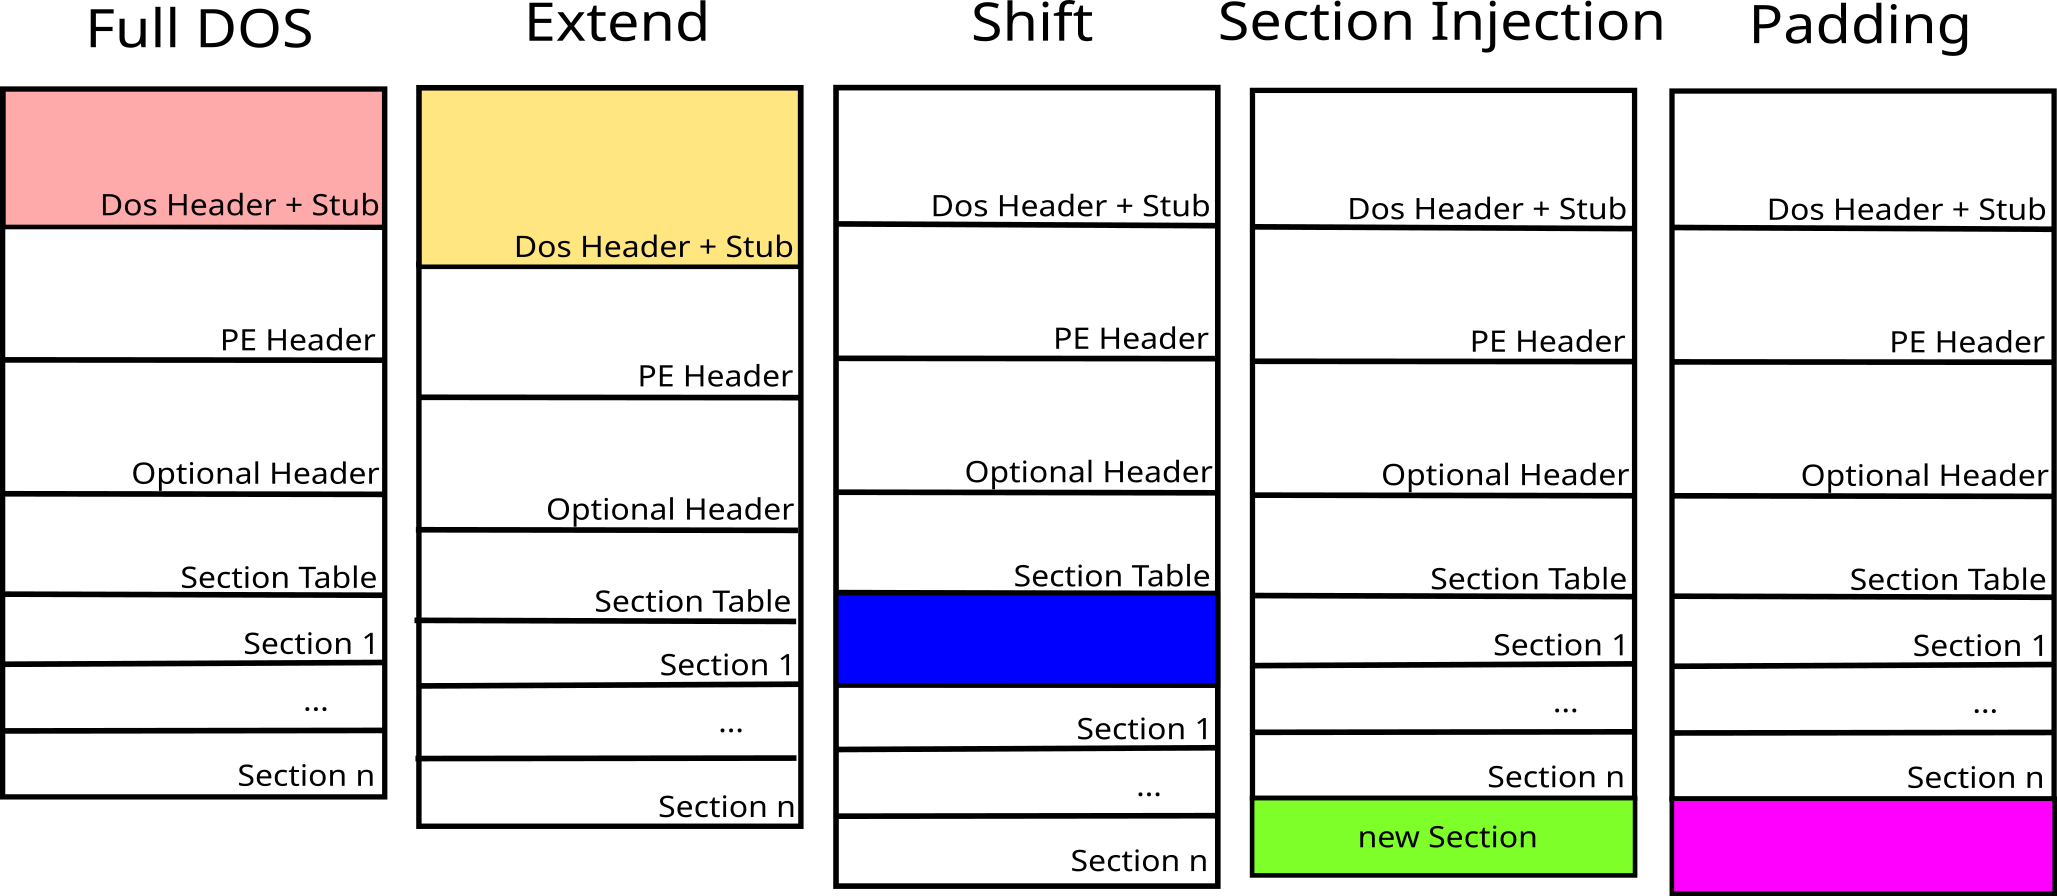
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
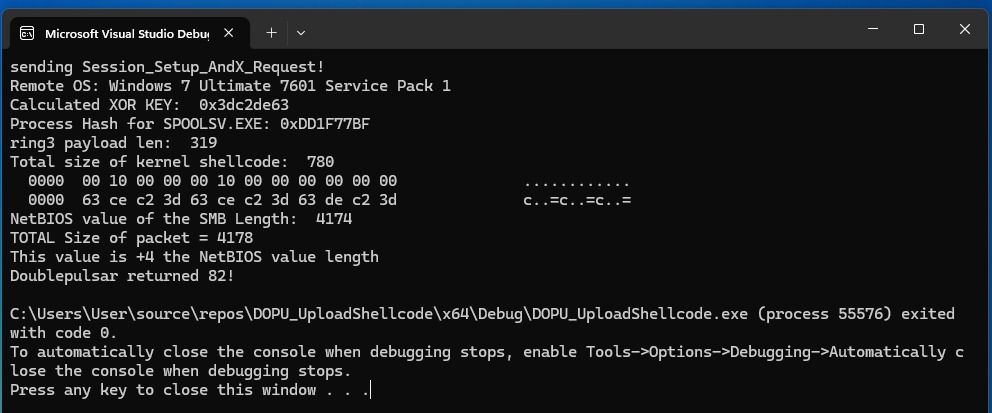 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 boku7/loki
🧙♂️ Node.js Command & Control for Script-Jacking Vulnerable Electron Applications
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 davidbuchanan314/dlinject
Inject a shared library (i.e. arbitrary code) into a live linux process, without ptrace
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
 wra7h/flavortown
Various ways to execute shellcode
 yzddmr6/java-shellcode-loader
基于Java实现的Shellcode加载器
 abedalqaderswedan1/aswcrypter
An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…