
quasibot
 smaash/quasibot
complex webshell manager, quasi-http botnet.
command-and-controlexploitationinformation-gathering+6
smaash/quasibotcomplex webshell manager, quasi-http botnet.
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 preemptdev/bluffy
Convert shellcode into :sparkles: different :sparkles: formats!
 enkomio/alanframework
A C2 post-exploitation framework
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
 nettitude/runpe
C# Reflective loader for unmanaged binaries.

 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 aniqfakhrul/sharperner
Simple executable generator with encrypted shellcode.
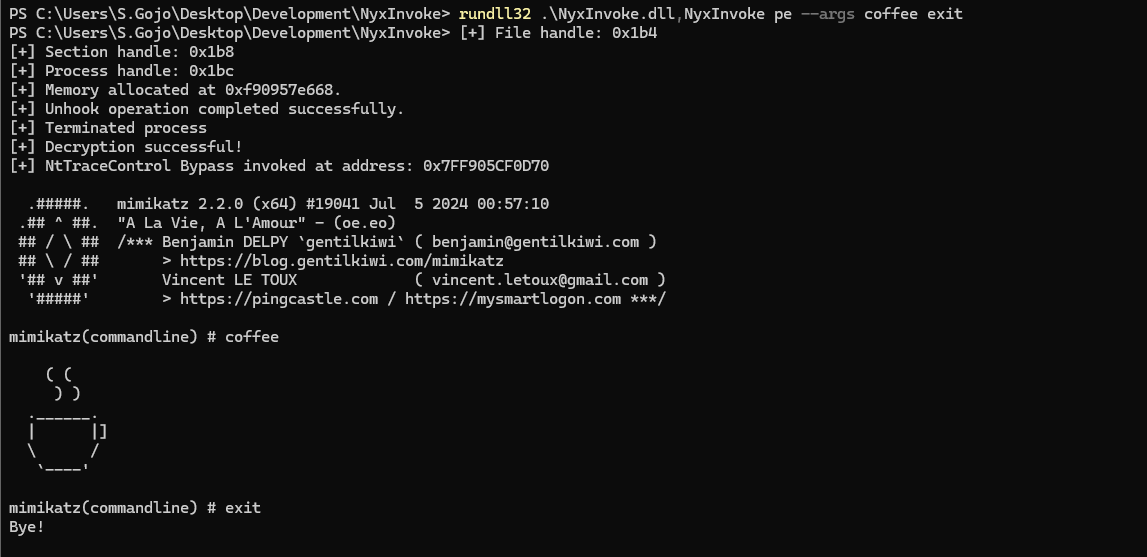 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
 saelo/cve-2018-4233
Exploit for CVE-2018-4233, a WebKit JIT optimization bug used during Pwn2Own 2018
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132