
Archived
blackpill
 shard77/blackpill
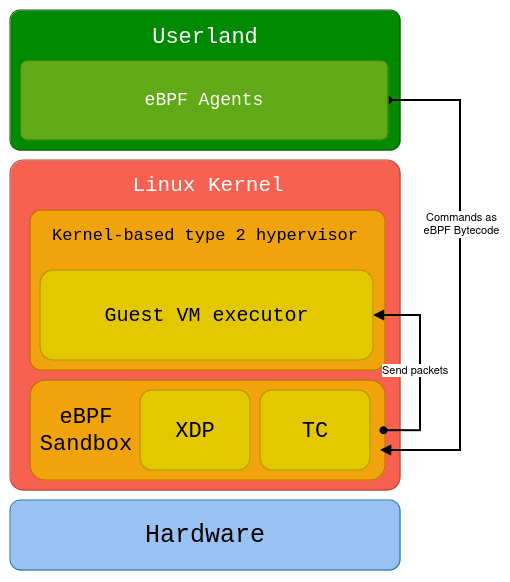
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
privilege-escalationpersistence-mechanismsids-ips-evasion+7
340
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 optiv/dent
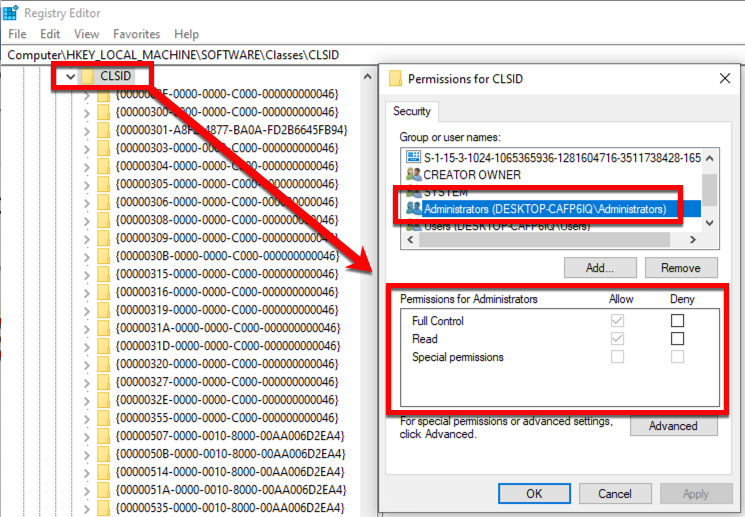
A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.
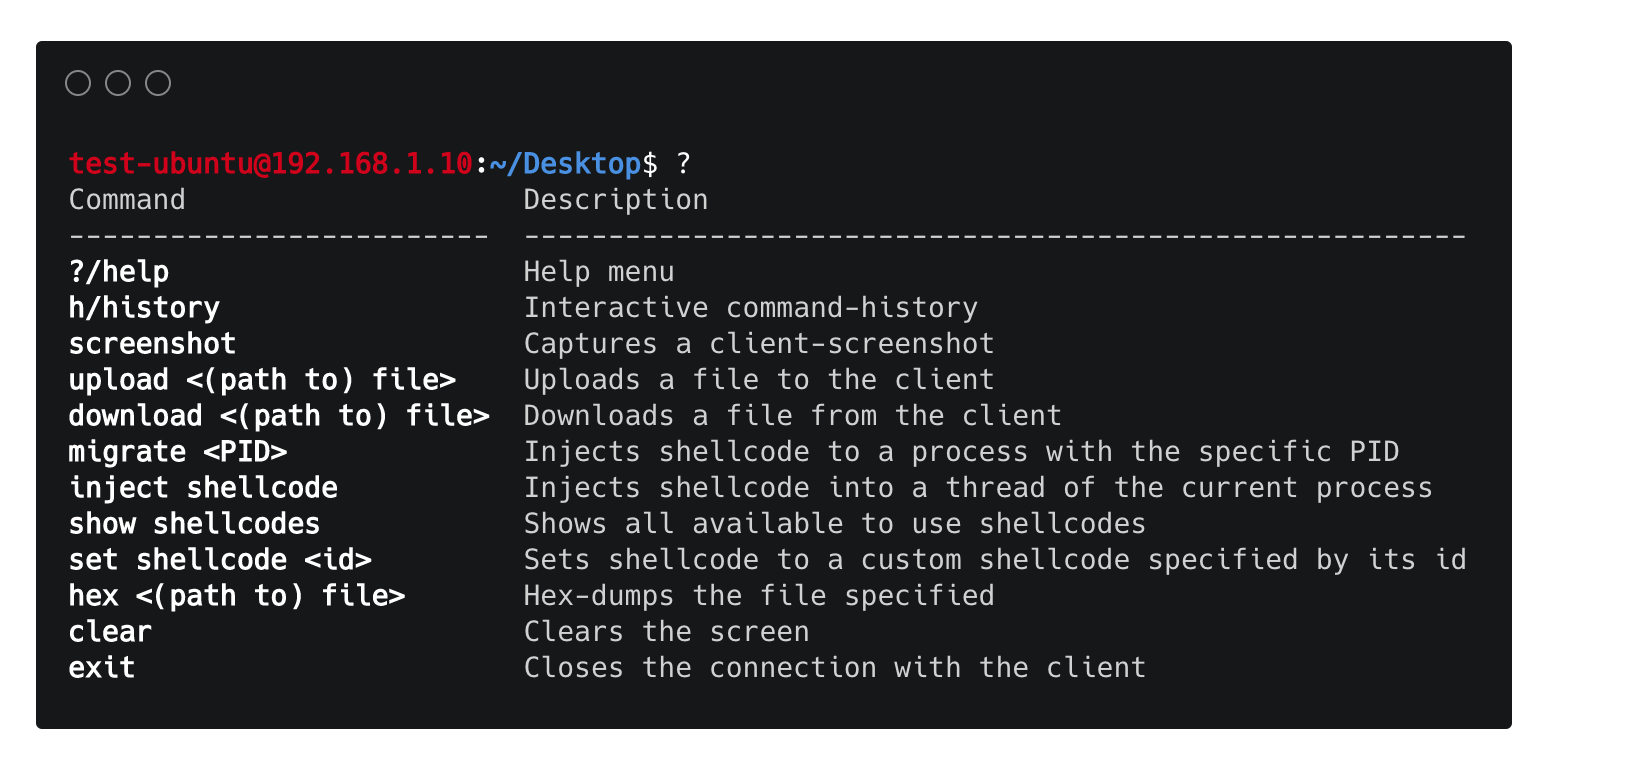 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
 zerx0r/dvenom
🐍 Double Venom (DVenom) is a tool that provides an encryption wrapper and loader for your shellcode.
 e3prom/bst
Binary String Toolkit (BST). Quickly and easily convert binary strings for all your exploit development needs. 😎
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…