actual-php2shell
 cookiengineer/actual-php2shell
🤖 NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
binary-exploitationcontainer-securityexploitation+5
17
cookiengineer/actual-php2shell🤖 NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
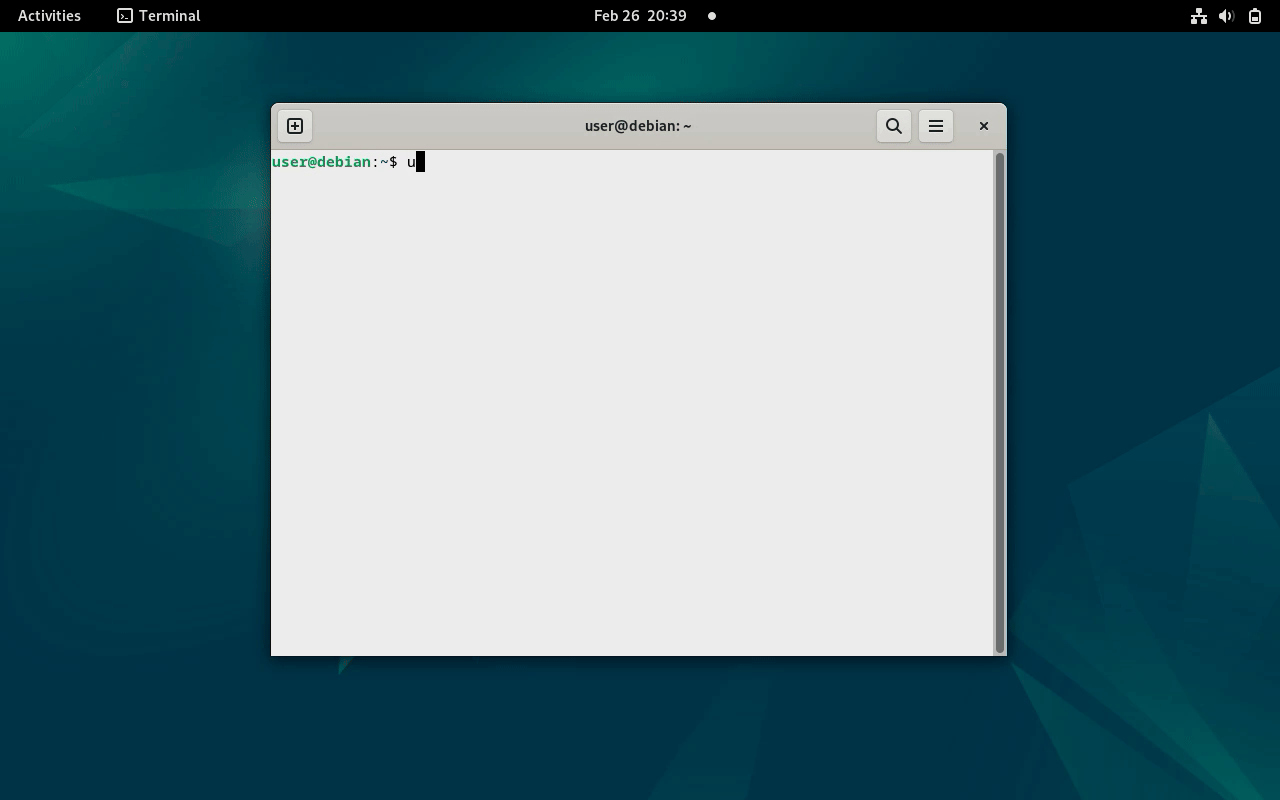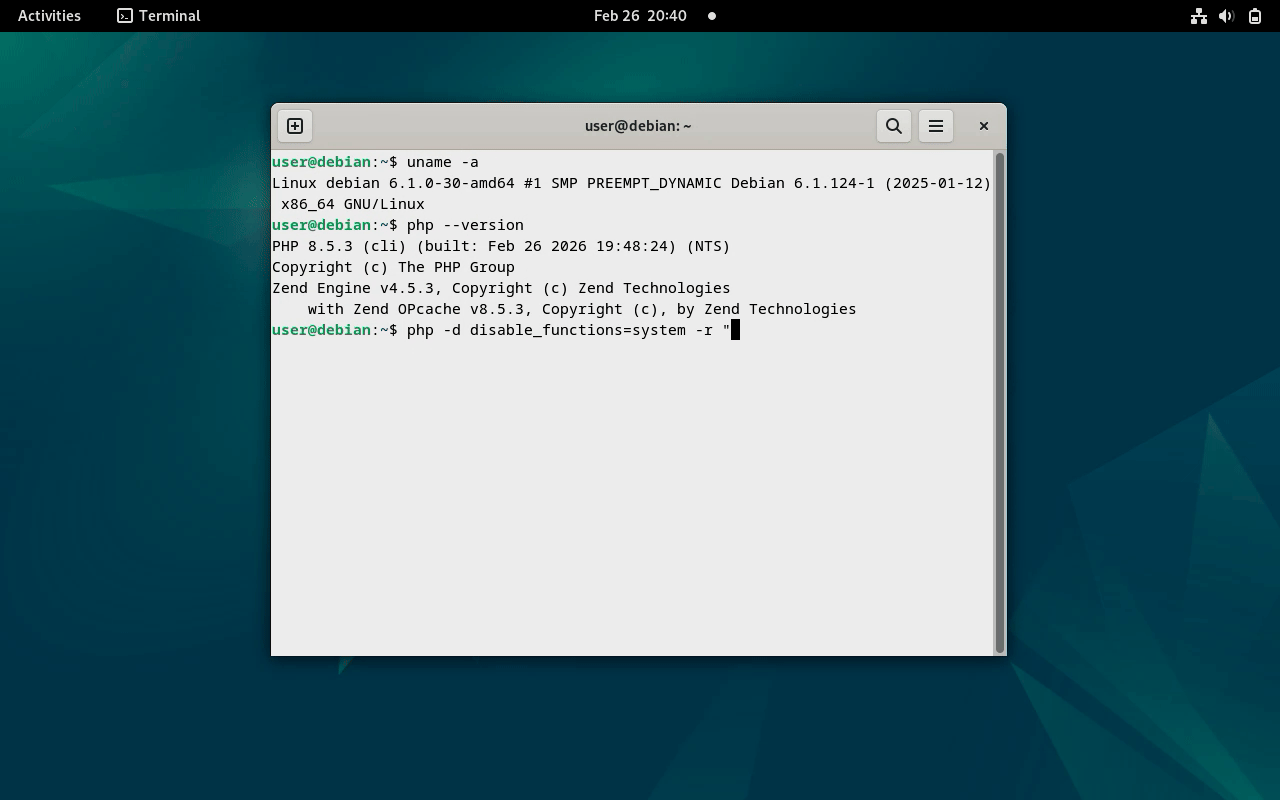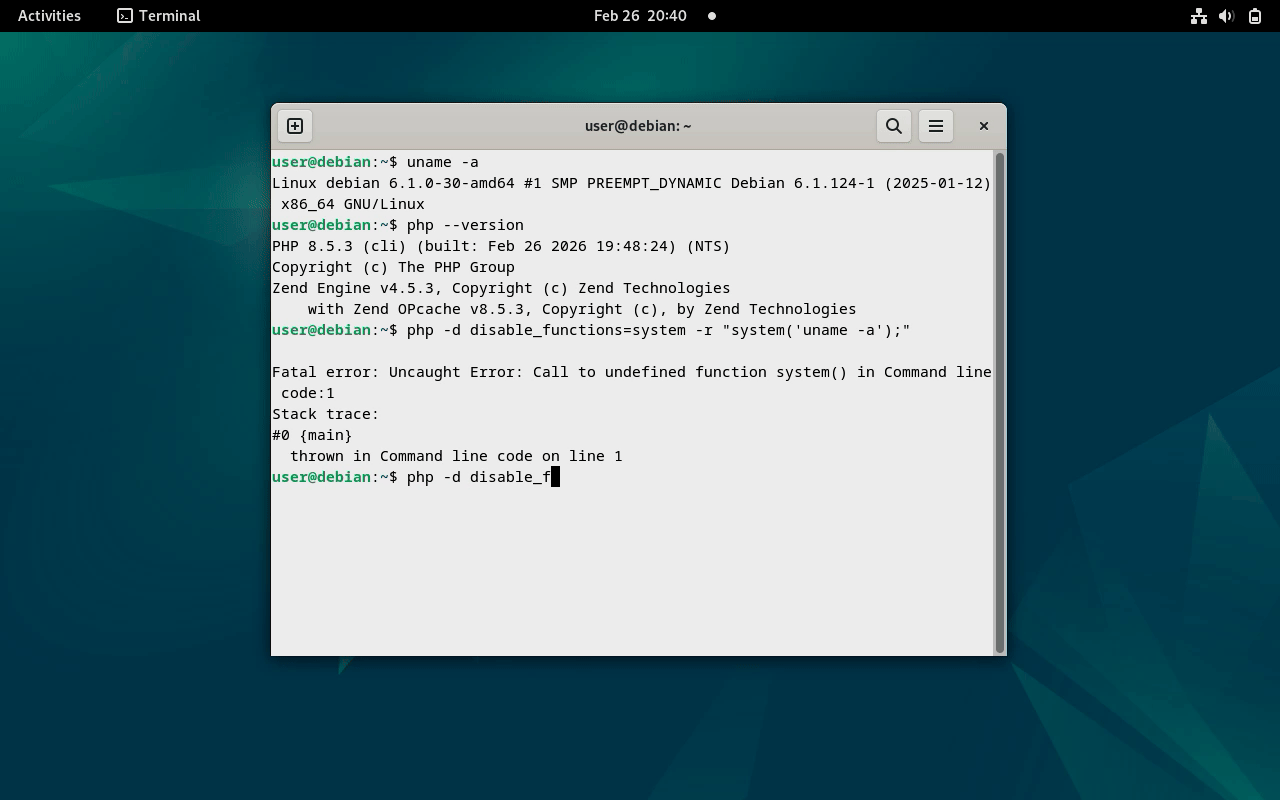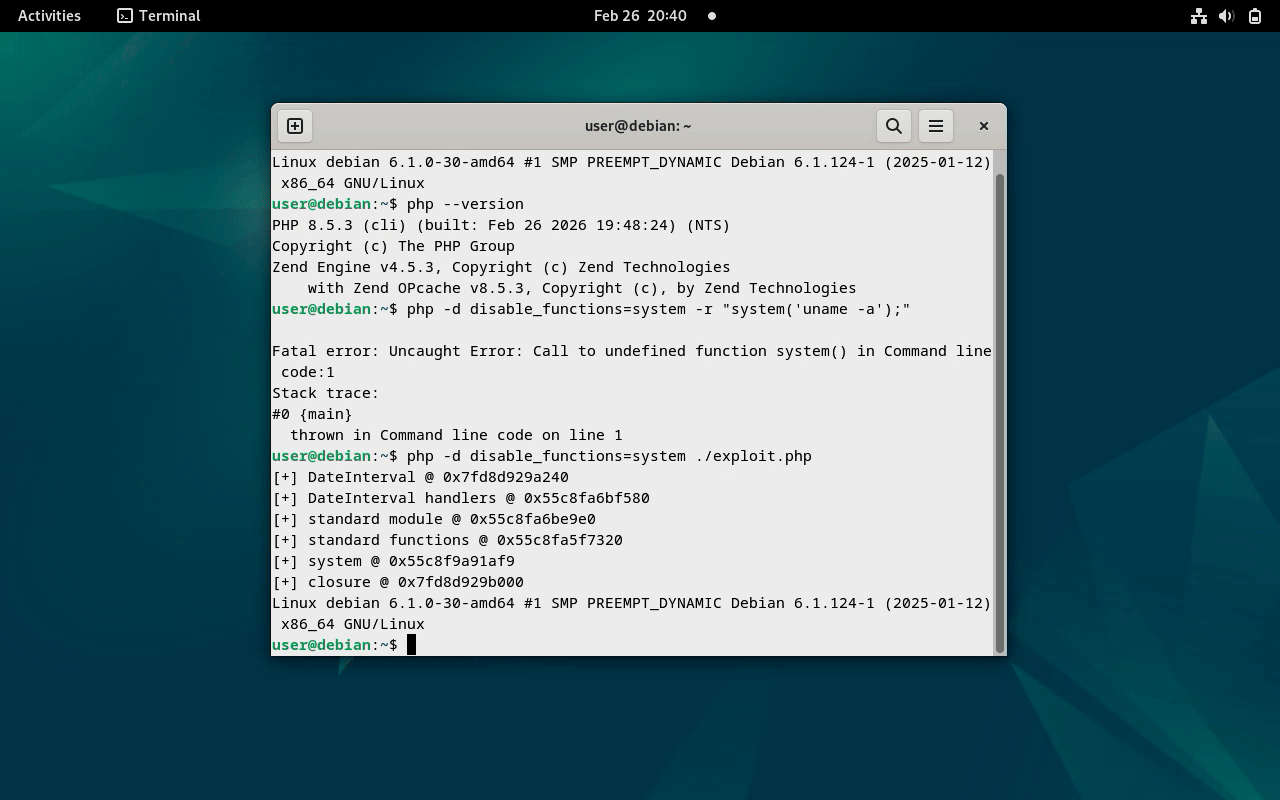 m0x41nos/timeafterfree
Proof-of-concept PHP 8 sandbox escape exploiting a use-after-free bug to bypass disable_functions and execute system commands on Unix-like systems.
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…
 5kr1pt/roundcube_cve-2025-49113
Explicação + Lab no THM