CVE-2026-31431-simple-test

Educational proof-of-concept demonstrating CVE-2026-31431 with a vulnerable target application, demonstration payload, and shellcode extraction…

Educational proof-of-concept demonstrating CVE-2026-31431 with a vulnerable target application, demonstration payload, and shellcode extraction…

Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…

Stack-based buffer overflow exploit for FreeFloat FTP Server, demonstrating reverse engineering, EIP control, and shellcode execution for educational…

An application to test windows and linux shellcodes

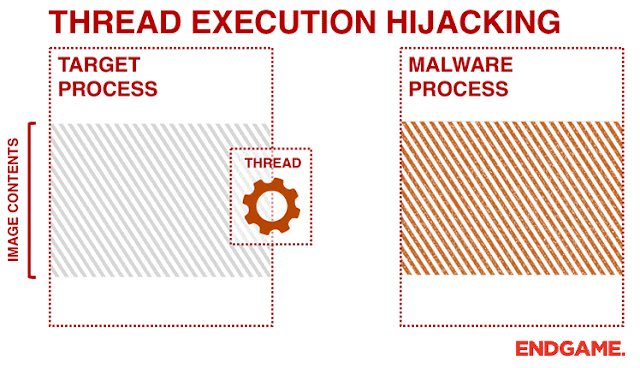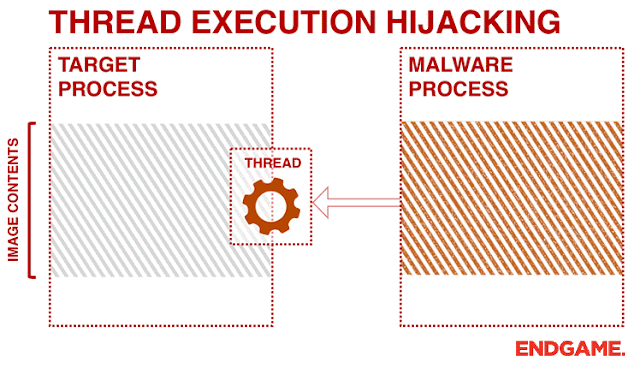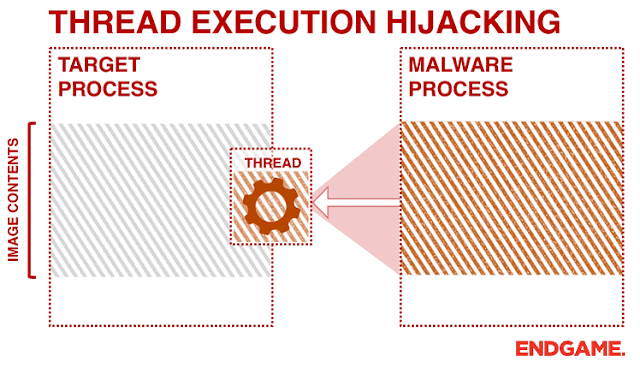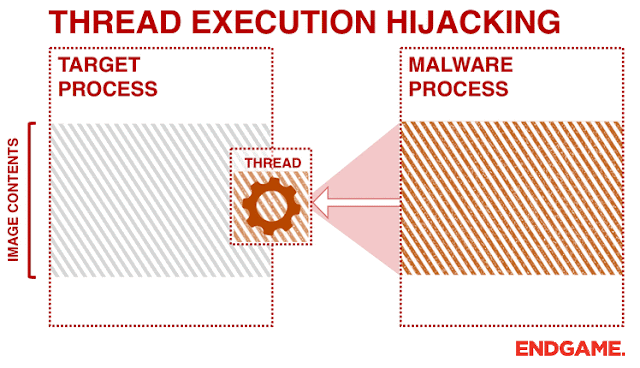
PoC Thread Execution Hijacking for Win32 Code Injection

CVE-2024-39069

ScareCrow - Payload creation framework designed around EDR bypass.

Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3

Toolbox containing research notes & PoC code for weaponizing .NET's DLR

Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…

Automated Application Generation for Stack Overflow Types on Wireless Routers