
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
252 results
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.

binary-exploitationdefensive-toolseducation+7
47
21 days ago
MSRKit preview

MSRKit

GitHubrurixis/msrkit

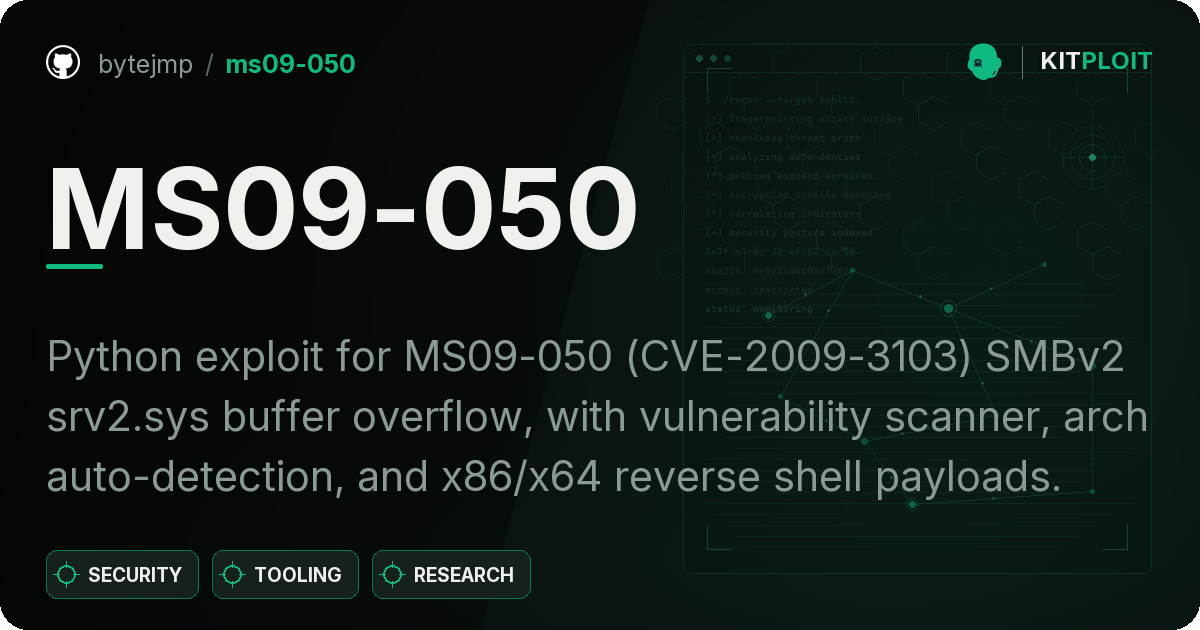
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
binary-exploitationexploitationpayload-development+5
6514 days ago
MS09-050 preview

MS09-050

GitHubbytejmp/ms09-050

Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
exploitationinformation-gatheringnetwork-security+7
17 days ago
MSRMapper preview

MSRMapper

GitHubull0a/msrmapper

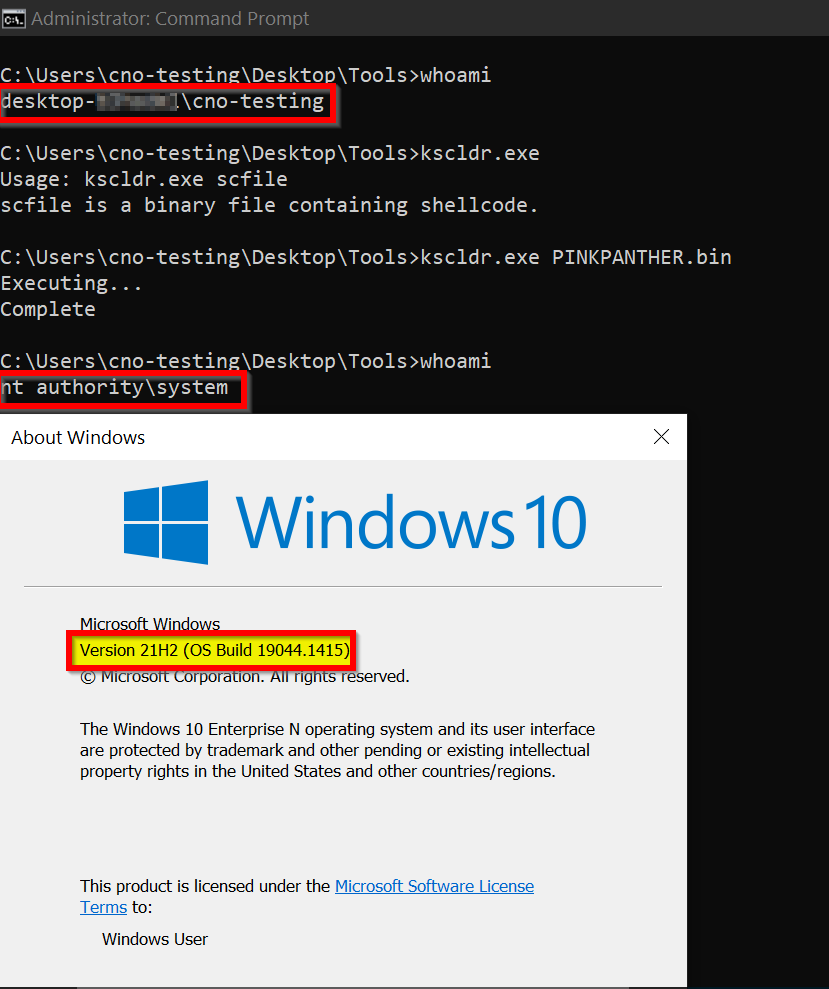
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
binary-exploitationexploitationmemory-forensics+6
118 days ago
PINKPANTHER preview

PINKPANTHER

GitHubwinterknife/pinkpanther

Windows x64 handcrafted token stealing kernel-mode shellcode

binary-exploitationpayload-developmentpost-exploitation+2
5152 years ago
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques

adversarial-attackdebuggersids-ips-evasion+6
9588 months ago
Dirty-Vanity preview

Dirty-Vanity

GitHubdeepinstinct/dirty-vanity

A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
adversarial-attackexploitationpayload-development+4
6743 years ago
Split preview

Split

GitHubkudaes/split

Apply a divide and conquer approach to bypass EDRs

adversarial-attackids-ips-evasionpayload-development+3
2882 years ago
Shinigami preview

Shinigami

GitHubbuzzer-re/shinigami

A dynamic unpacking tool

binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
1533 years ago
yara-ttd preview

yara-ttd

GitHubairbus-cert/yara-ttd

Use YARA rules on Time Travel Debugging traces
binary-analysisdynamic-analysis-sandboxingmalware-analysis+3
993 years ago
msf_shellcode_analysis preview

msf_shellcode_analysis

GitHubyo-yo-yo-jbo/msf_shellcode_analysis

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…

binary-analysiseducationmalware-analysis+3
282 months ago
DEFCON-31-Syscalls-Workshop preview

DEFCON-31-Syscalls-Workshop

GitHubvirtualalllocex/defcon-31-syscalls-workshop

Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".
educationlabs-practicepayload-development+2
7841 year ago
Kernel_VADInjector preview

Kernel_VADInjector

GitHublleon1435/kernel_vadinjector

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
adversarial-attackids-ips-evasionpayload-development+3
542 years ago
DInvoke_rs preview

DInvoke_rs

GitHubkudaes/dinvoke_rs

Dynamically invoke arbitrary unmanaged code

binary-analysisids-ips-evasionpayload-development+3
3663 months ago
DataInject-BOF preview

DataInject-BOF

GitHubiilegacyyii/datainject-bof

Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
binary-exploitationexploitationpayload-development+3
1541 year ago
PMD preview

PMD

GitHubrad9800/pmd

Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.

binary-analysiseducationlabs-practice+6
1581 year ago
BloodfangC2 preview

BloodfangC2

GitHubzarkones/bloodfangc2

Modern PIC implant for Windows (64 & 32 bit)
adversarial-attackcommand-and-controlpayload-development+4
1031 year ago
Bypass_AV preview

Bypass_AV

GitHubhkl1x/bypass_av

Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…

ids-ips-evasionpayload-developmentpayload-generation+2
10811 months ago
Previous12…14Next